Configuring Device Access Policies
In response to the ever-growing numbers of
personally owned mobile devices, such as smart phones and tablets, being brought
into the
network, IT departments are requiring more sophisticated control over how devices
connect,
what types of devices can connect, and what they are allowed to do once connected.
The RUCKUS Unleashed system can identify the type of client attempting to connect, and perform control actions such as permit and deny and rate limiting based on the device type.
Once a device access policy has been created, you can apply the policy to any WLANs for which you want to control access by device type. You could, for example, allow only Apple iOS devices on one WLAN and only Linux devices on another.
Complete the following steps to create a device access policy.
-
Reuse content for UnleashedFrom the main menu, select .
- In the Wireless Access Control page, click .
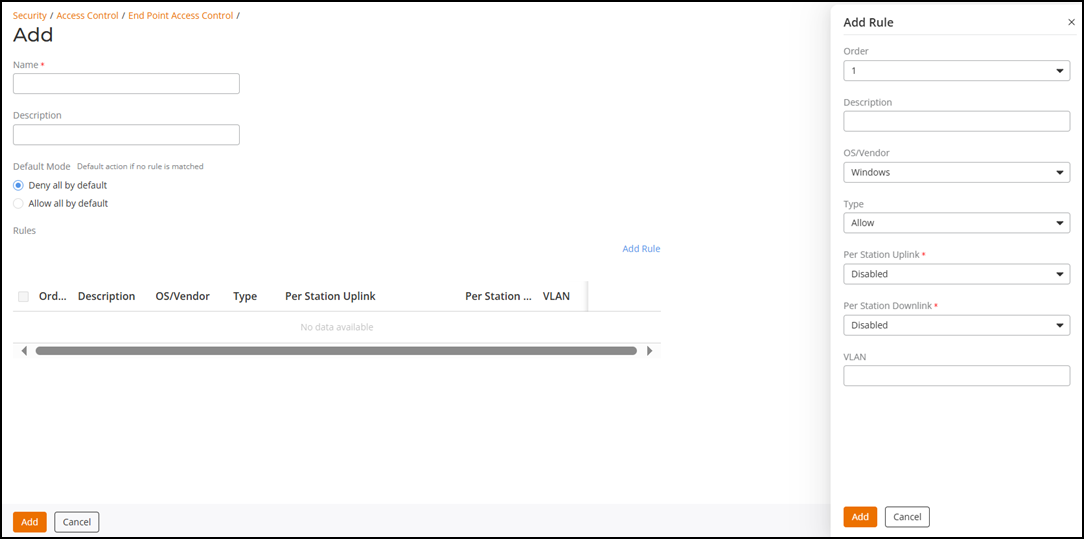
- Enter a name for the access policy, and (optionally) enter a description.
- Under Default Mode, select Deny all by default or Allow all by default to set the default access privilege that you want to grant all users by default.
- Under Rules, click Add Rule to create multiple OS-specific rules for each access policy.
- Define each access policy by configuring a combination of the following
attributes:
- Order: Select a number from the drop-down list to prioritize a rule.
- Description: Description of the rule.
- OS/Vendor: Select from any of the supported client types.
- Type: Select a rule type (allow or deny).
- Per Station Uplink and Per Station Downlink: Set rate limiting for this client type.
- VLAN: Enter a VLAN ID.
Note: The VLAN range varies from 1 through 4094.
- Click Add to add the rule you created. You can create up to nine rules per access policy (one for each client type).
- To change the order in which rules are implemented, click the Move Up or Move Down arrow in the Action column. You can also edit or clone rules in the Action column. To delete a rule, select the checkbox of the rule and click Delete.
- Click Add to add the
access policy.Note: You can create up to 32 access policies (one access policy per WLAN).