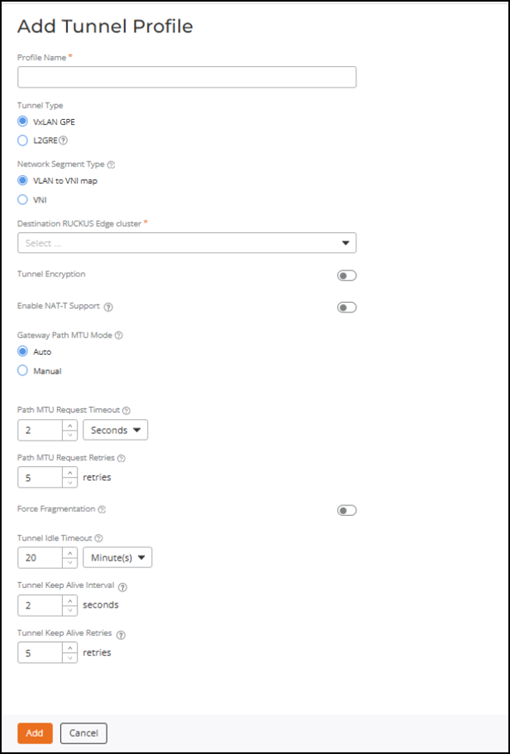
Adding a Tunnel Profile for AP-DC Edge VxLAN-GPE Tunnels
Complete the following steps to create a Tunnel Profile:
- From the navigation bar, select
.The Service Catalog page is displayed.
- Click Add in the Tunnel Profile tile.
- Complete the following
fields:
- Profile Name: Enter the name for the tunnel profile.
- Tunnel
Type: Select VxLAN GPE.Establishes tunnels between RUCKUS Access Points and RUCKUS Edge devices. It supports multiple encapsulated protocols for SD-LAN deployments needing flexibility and scalability.Note: IPv6 data packets will be tunneled through existing IPv4 VxLAN-GPE tunnels between APs and RUCKUS Edge. This support is applicable only for the SD-LAN service.
- Network Segmentation Type: This option needs to be selected for the SD-LAN. SD-LAN service maps the VLAN ID to the VNI for tunneling. The VLAN to VNI map option is selected by default as well.
- Destination RUCKUS Edge cluster: Select a Destination Edge cluster name. The APs will use the Edge nodes in this cluster as VxLAN-GPE tunnel remote end-points.
- Tunnel Encryption: Enable IPSec/IKE-based
encryption for VxLAN-GPE tunnels between APs and Edge devices. If
enabled, the tunnel traffic between the AP and Edge device is secured
using IKEv2 and IPSec protocols, ensuring data confidentiality and
integrity across public or untrusted networks. Once enabled, additional
configuration fields appear for selecting or adding an IPSec
profile.Note: Tunnel encryption is supported only for VxLAN-GPE tunnels. Enabling or disabling tunnel encryption is a disruptive operation as the existing tunnels are deleted and re-established during the change. It is recommended to perform this action during maintenance windows to avoid service interruptions.
- IPSec
Profile: Specifies the IPSec profile that defines the
encryption and authentication parameters used for the tunnel. Select a
preconfigured IPSec profile from the drop-down list. The selected
profile’s details such as Pre-Shared Key, IKE proposal, and ESP proposal
are automatically displayed for reference. If an IPsec profile is not
available, click Add to open the Add
IPSec Profile sidebar, where you can create and add a
new IPSec profile. For more information, refer to Creating an IPsec Profile.
- Note:
- Only one IPSec profile can be associated per tunnel profile. Multiple IPSec profiles per tunnel are not supported.
-
When tunnel encryption is enabled, NAT Traversal (NAT-T) is automatically activated for the VxLAN-GPE tunnel. If encryption is disabled on a tunnel profile, NAT-T remains enabled. Disabling encryption does not deactivate NAT-T.
- Enable NAT-T Support: This setting ensures the AP-Edge tunnel establishes and maintains device connections even if the AP and Data Center (DC) are separated by a NAT server, which masks the private IP of the AP. VxLAN still facilitates support between the AP and the Edge device. This option is disabled by default. Toggle the switch to enable.
- Gateway Path MTU Mode: Controls how the gateway handles the Path
Maximum Transmission Unit Discovery (PMTUD). When configuring a
VxLAN-GPE tunnel profile between an Access Point and a Data Center Edge
device, the Gateway Path MTU mode can be configured as Auto or Manual.
Select one of following options:
-
Auto: The system will attempt to automatically discover the optimal Maximum Transmission Unit (MTU) for the tunnel path.
- Manual: Enter the value in bytes (allowed
values are 1280 through 1450). The value must be less than the
Ethernet MTU on the AP.
- Note:
- When configuring a VxLAN-GPE tunnel profile between a Data Center Edge device and a DMZ Edge device, the Gateway Path MTU mode should be configured as Manual because automatic PMTUD is not supported between two Edge devices.
- Check the Ethernet MTU on the AP; Tunnel MTU gets applied only if it is less than the Ethernet MTU.
-
- Path MTU Request Timeout: The maximum wait time for a response to a path MTU request. Range: 10 milliseconds through 10 seconds; default is 2 seconds.
- Path MTU Request Retries: The maximum number of Path MTU requests sent to test one MTU value. Range: 3 through 64; default is 5 retries.
- Force Fragmentation: When enabled, the AP or Edge device will automatically fragment packets, ignoring the Don't Fragment (DF) bit in the IP header of the packets. Forced packet fragmentation can reduce congestion and improve network throughout, but it may lead to fragment loss, packet reassembly issues, and memory exhaustion. This option is disabled by default. Toggle the switch to enable.
- Tunnel Idle Timeout: This is the amount of time a VxLAN-GPE tunnel takes to age out on RUCKUS Edge, in the event after AP stops sending keepalive request packets. Select Minutes, Days, or Week from the drop-down list and then enter the duration or use the up/down arrows to set the value. Range: 5 through 10080 minutes, 1 through 7 days, or 1 week; default is 20 minutes.
- Tunnel Keep Alive Interval: Defines the interval between two consecutive keepalive request messages. Range: 1 through 5 seconds, with a default value of 2 seconds.
- Tunnel Keep
Alive Retries: Defines the maximum number of consecutive
keepalive requests that can fail before the AP determines the Edge
device is unreachable. Range: 3 through 10 retries, with a default value
of 5.Note: If the Edge does not respond to keepalive requests from the AP, the AP brings down the tunnel after the Keepalive Lifetime expires. Keepalive Lifetime = Tunnel Keep Alive Retries × Tunnel Keep Alive Interval. The AP sends one keepalive per interval, up to the configured number of retries. If the Edge does not respond to any of these keepalives, the AP brings down the active tunnel and fails over to the backup Edge. Example: Interval = 2 seconds and Retries = 5 means the AP sends 5 keepalives (one every 2 seconds). If none are answered, failover occurs after 2 × 5 = 10 seconds.
- Click Add. The Tunnel Profile is created and is displayed on the Tunnel Profile page.