Viewing the WLAN Configuration List
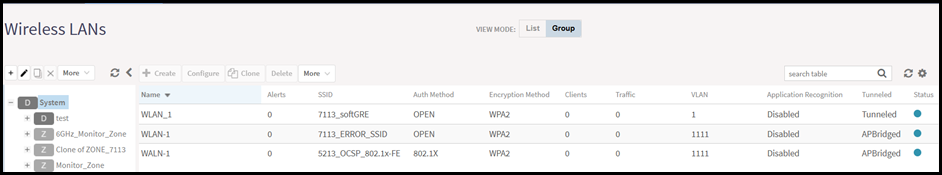
Displays a list of all configured WLANs,
including their names, SSIDs, status, and key settings. Enables quick review and
access to
individual WLAN configurations.
To view the WLAN configuration list, from the main menu, navigate to .
The left pane displays the WLANs available in FIPS mode.
Certificate Validation Failure
Indicates a failure in establishing a trusted connection due to certificate
validation issues, such as invalid, expired, or untrusted certificates.
In the event that a trusted channel cannot be established due to a certificate validation failure, perform the following -
- Consult the system audit logs to identify the specific reason for the certificate validation failure (for example, expiration, untrusted issuer, revocation, or Subject Alternative Name mismatch).
- Verify that the local system clock is accurately synchronized with a trusted time source to eliminate time-related validation errors.
- If the failure indicates an untrusted issuer, verify the configured trust anchors. Securely import any missing Root or Intermediate CA certificates into the device’s trust store, if required.
- If the failure is due to revocation, expiration, or identity mismatch, coordinate with the remote peer’s owner to obtain a newly issued, valid certificate that meets the configured security requirements.
- Attempt to re-establish the trusted channel after resolving the identified issue.