Creating an L2 Access Control Service
Another method to control access to the network is by defining Layer 2 MAC address
access control lists (ACLs), which can then be applied to one or more WLANs or WLAN
groups. L2 ACLs are either allow-only or deny-only; that is, an ACL can be set up
to allow only specified clients based on the MAC addresses that are configured. Further,
L2 ACLs can also be used to allow-only or deny-only clients based on the ether types
of the packet where EtherTypes is a field present in the ethernet header of a packet.
Note: If a tagged packet with Tag Protocol Identifier (TPID) value of 0x8100, 0x9100, or
0x88A8 is received, then instead of the TPID, the actual Ether-Type of the packet
will be used for making the allow or block decision against the configured
Ether-Types. If the mentioned TPID values need to be treated as Ether-Type to
make
the allow or block decision, configure the required TPID values in the custom
Ether-Type list.
- Select .
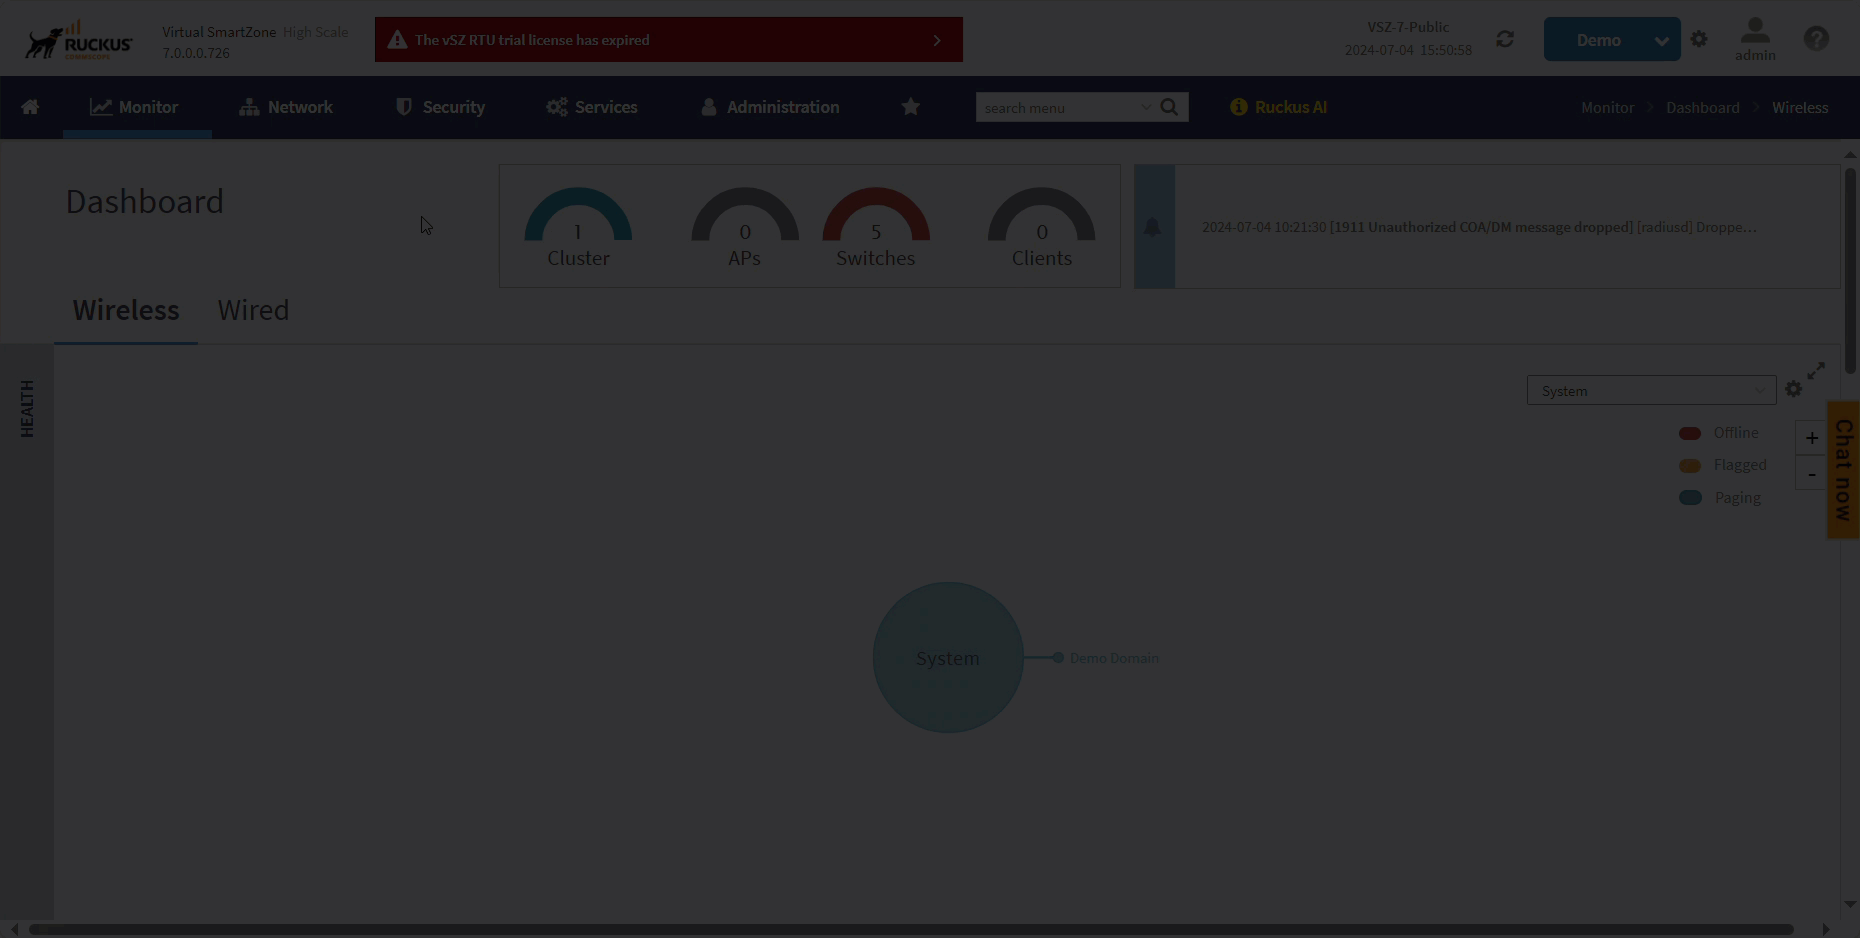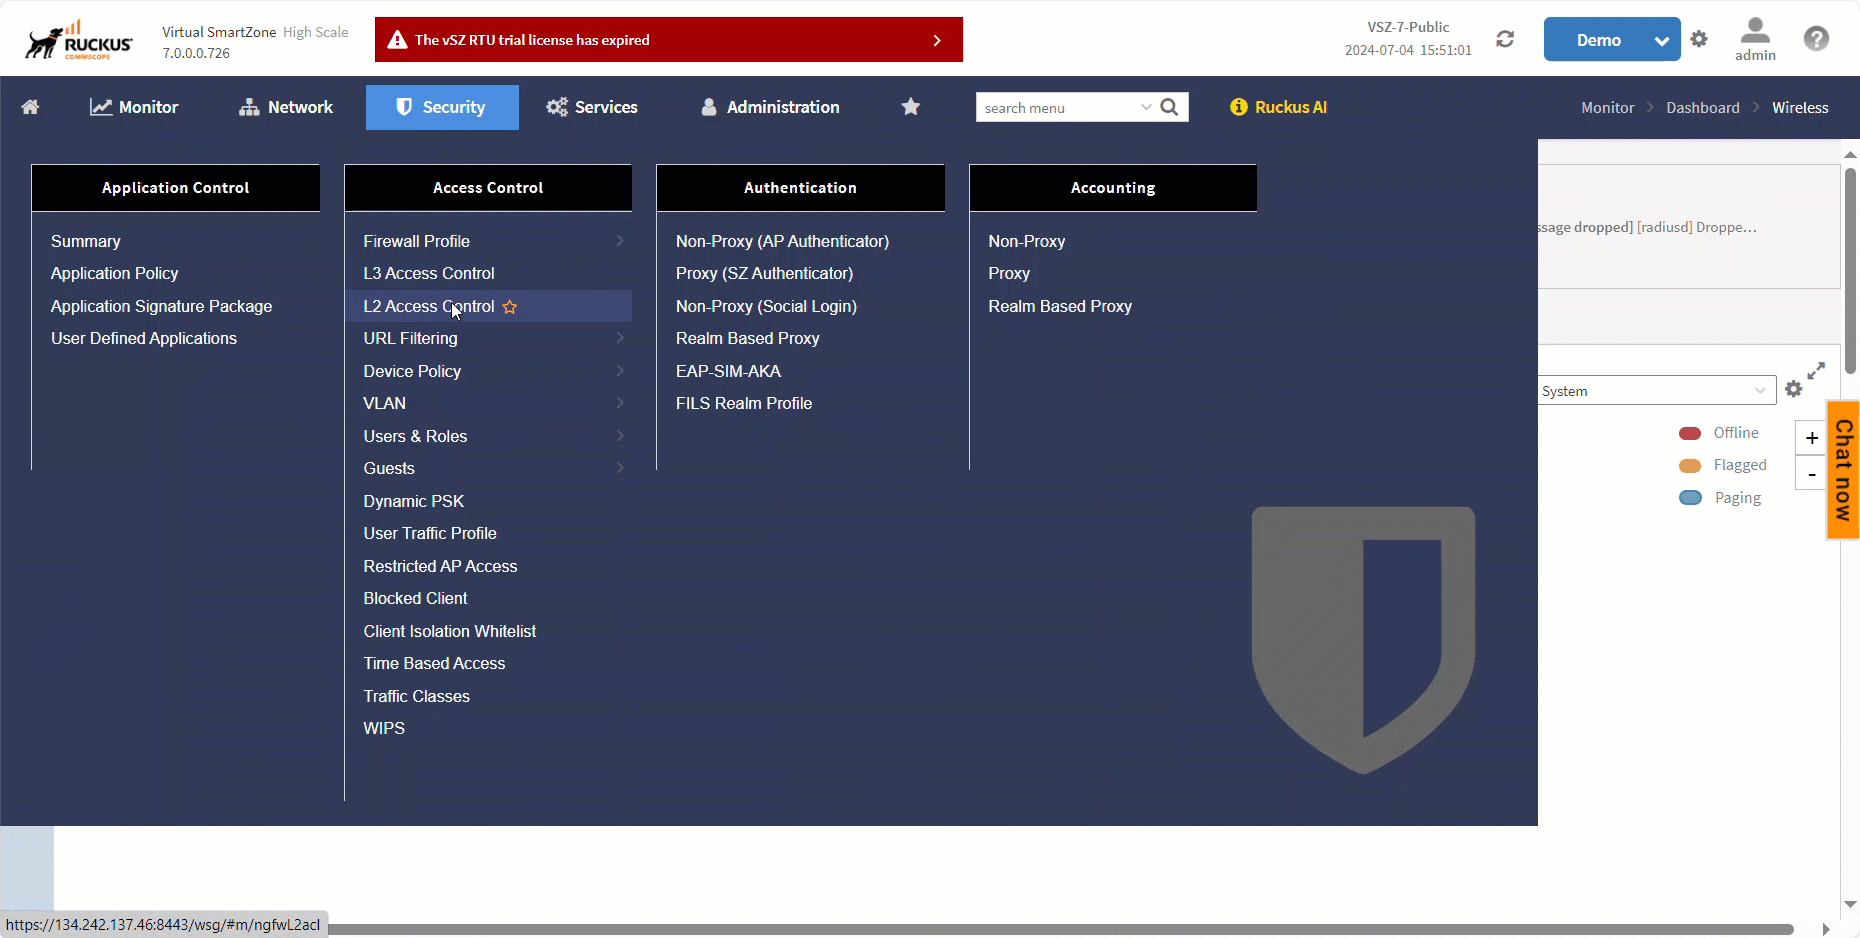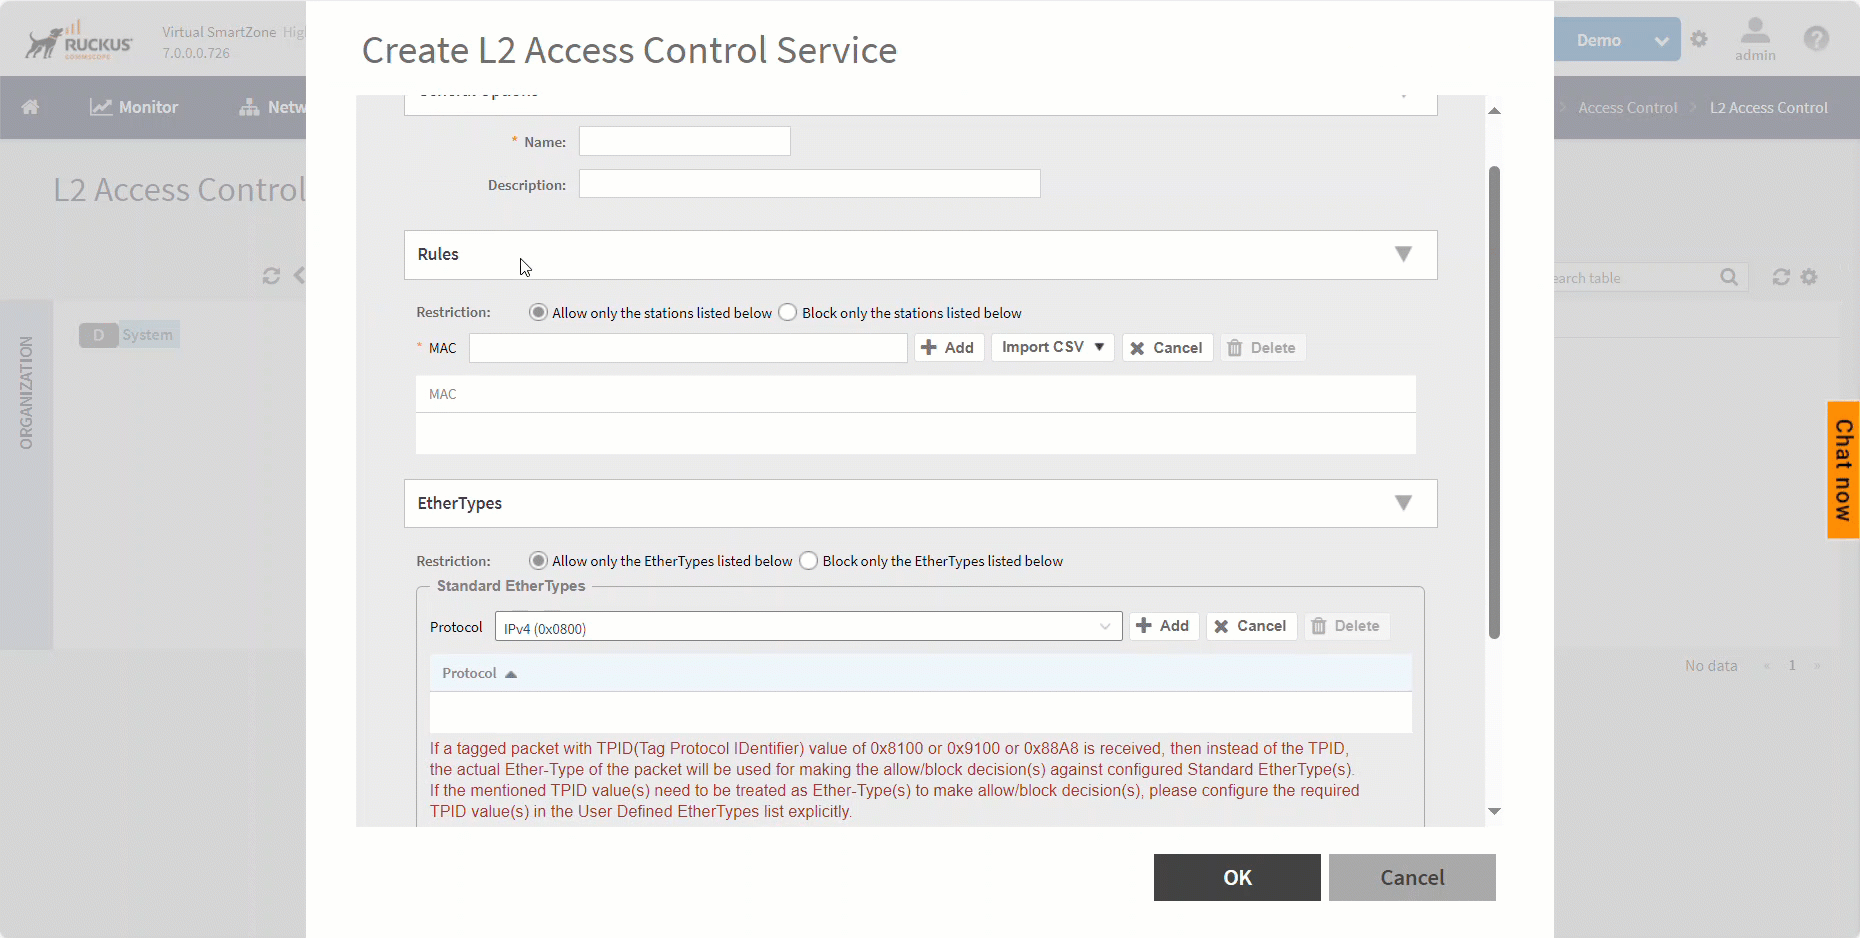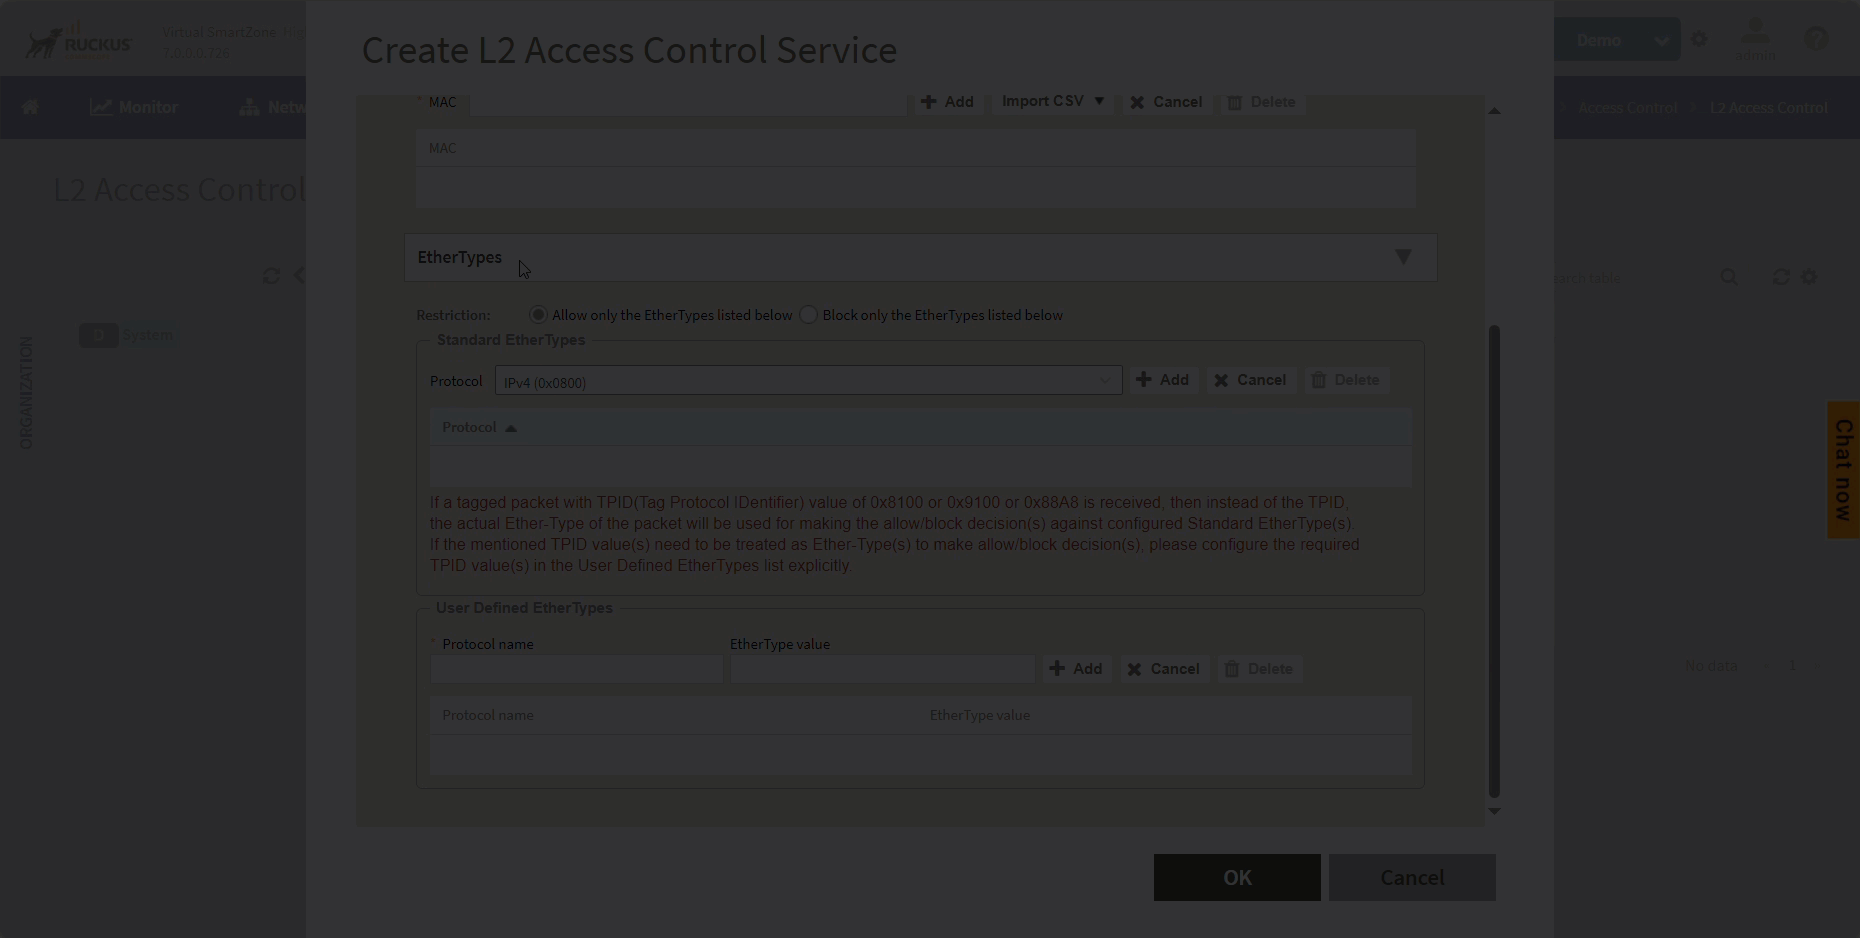
- Click Create.
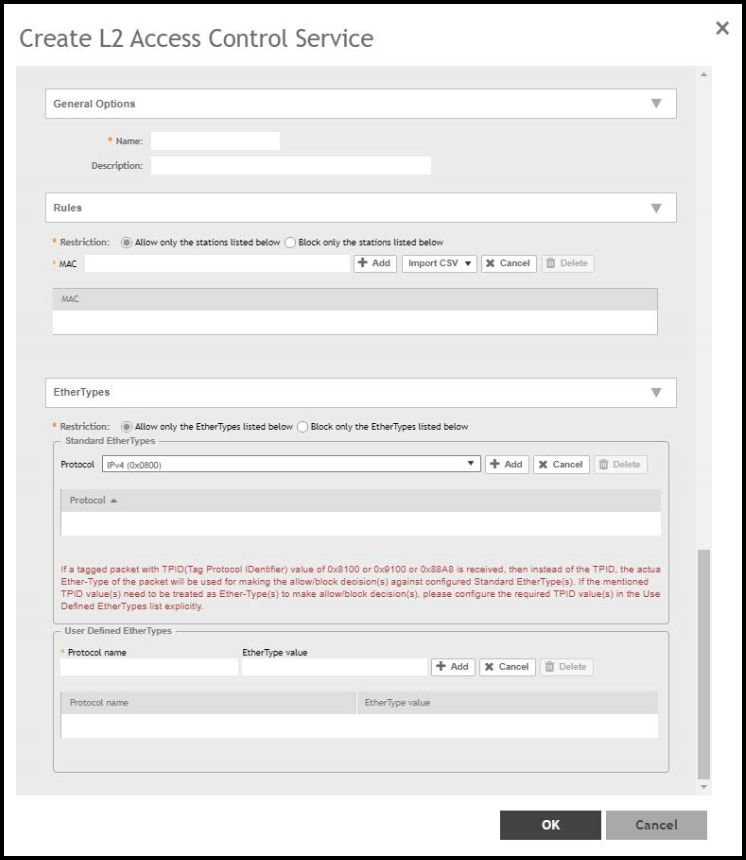
- Configure the following options:
- General Options
- Rules
- Restriction: Select the default action that the controller will take if no rules are matched. Available options include Allow only the stations listed below or Block only the stations listed below.
- MAC Address: Enter the MAC address to which this L2 access policy applies and click Add or click Import CSV to import the MAC address.
- EtherTypes
- Restriction: The EtherType in the L2 ACL profile allows or blocks the specified EtherType traffic from the clients toward the network. Available options include Allow only the EtherTypes listed below or Block only the EtherTypes listed below.
- Standard Ether Types: Select a protocol from the Protocol list to which this L2 access policy applies and click Add.
-
5.2.1 updateUser Defined Ether Types: Enter a protocol name and EtherType value in hexadecimal format and click Add. A maximum of ten custom EtherTypes can be configured to be allowed or blocked.
- Click OK.