Creating an Application Control Policy
An application control policy is created
to limit and classify traffic into priority queues using QoS traffic shaping rules,
or to
completely block access to an application.
- From the main menu, go to .
- Click Create.
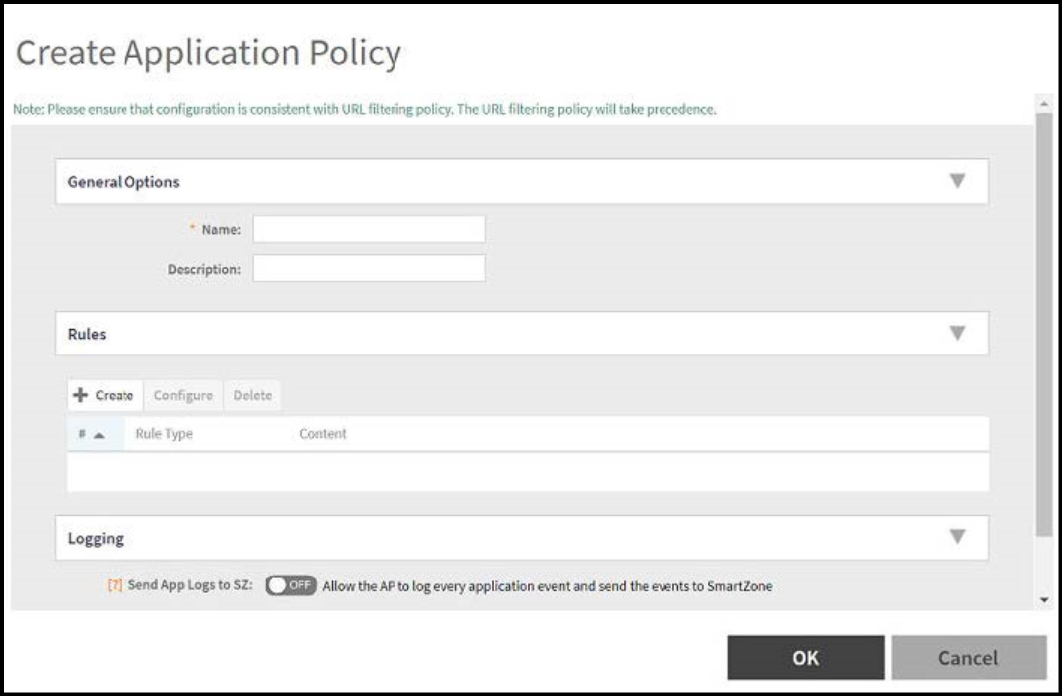
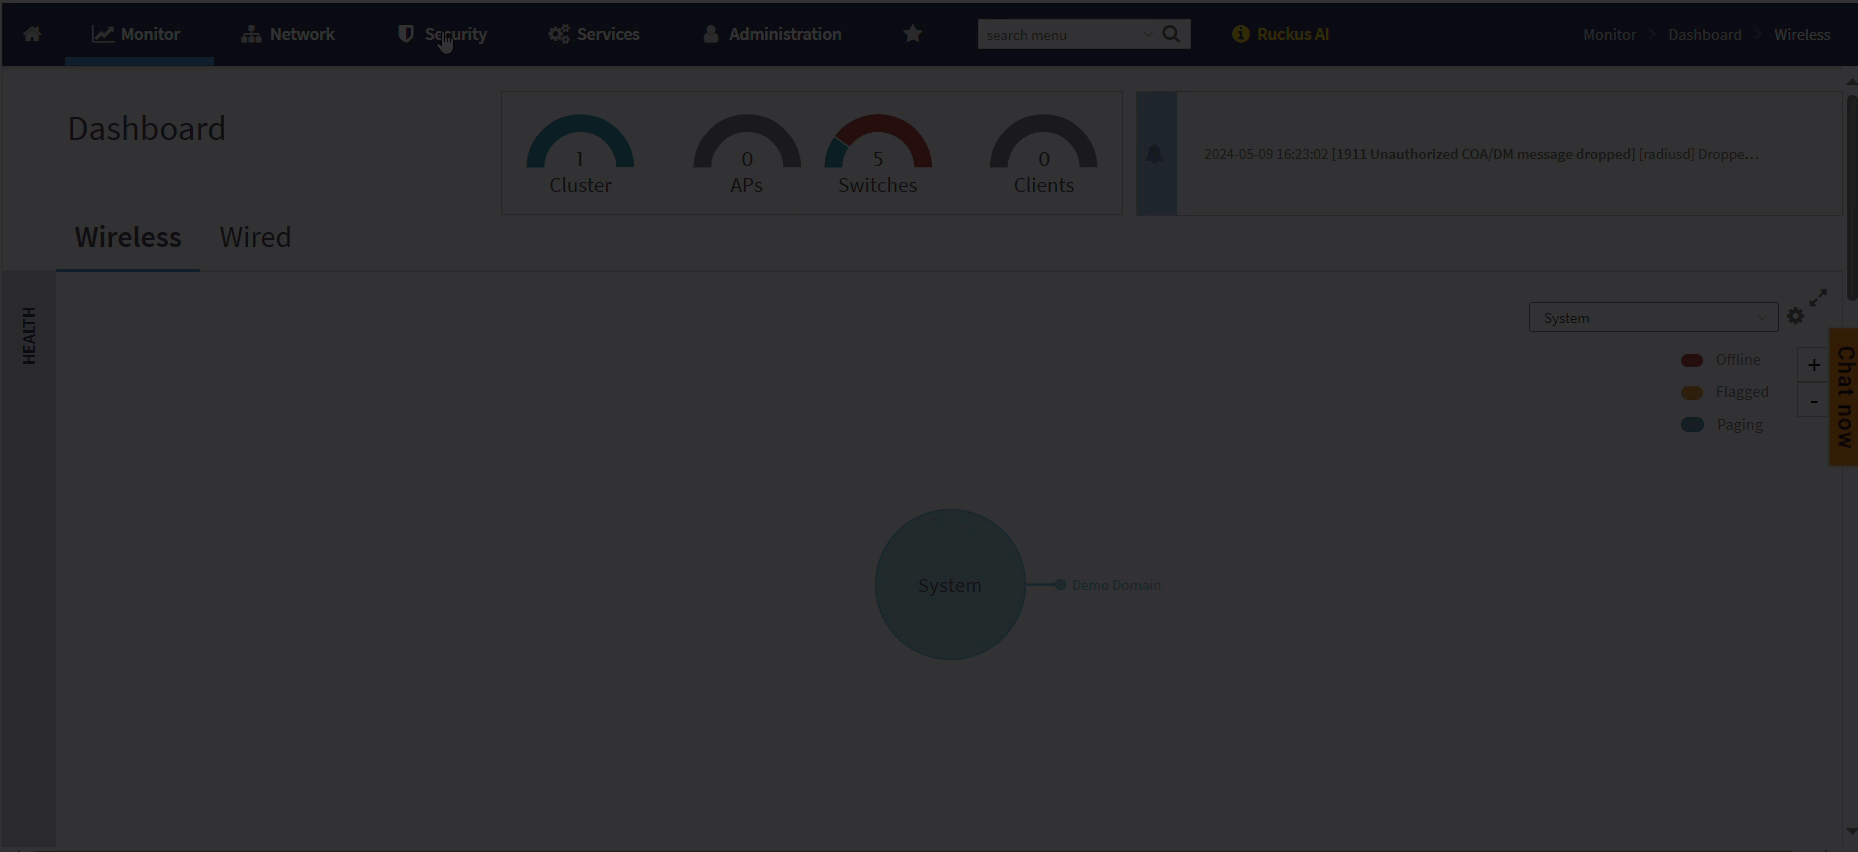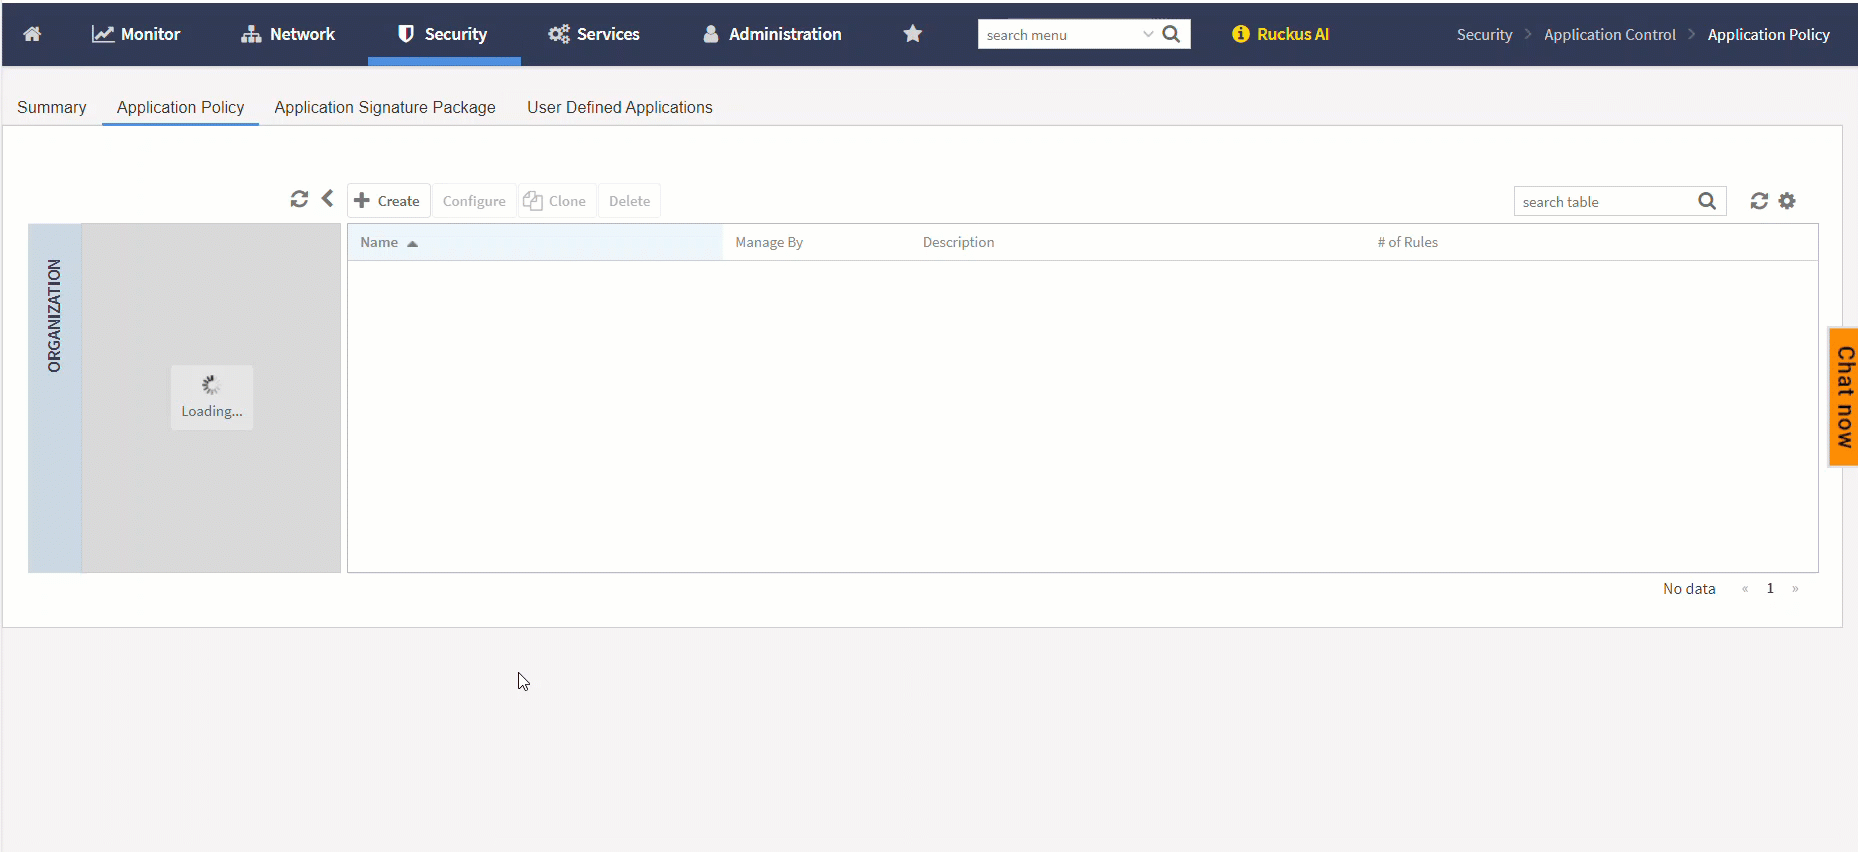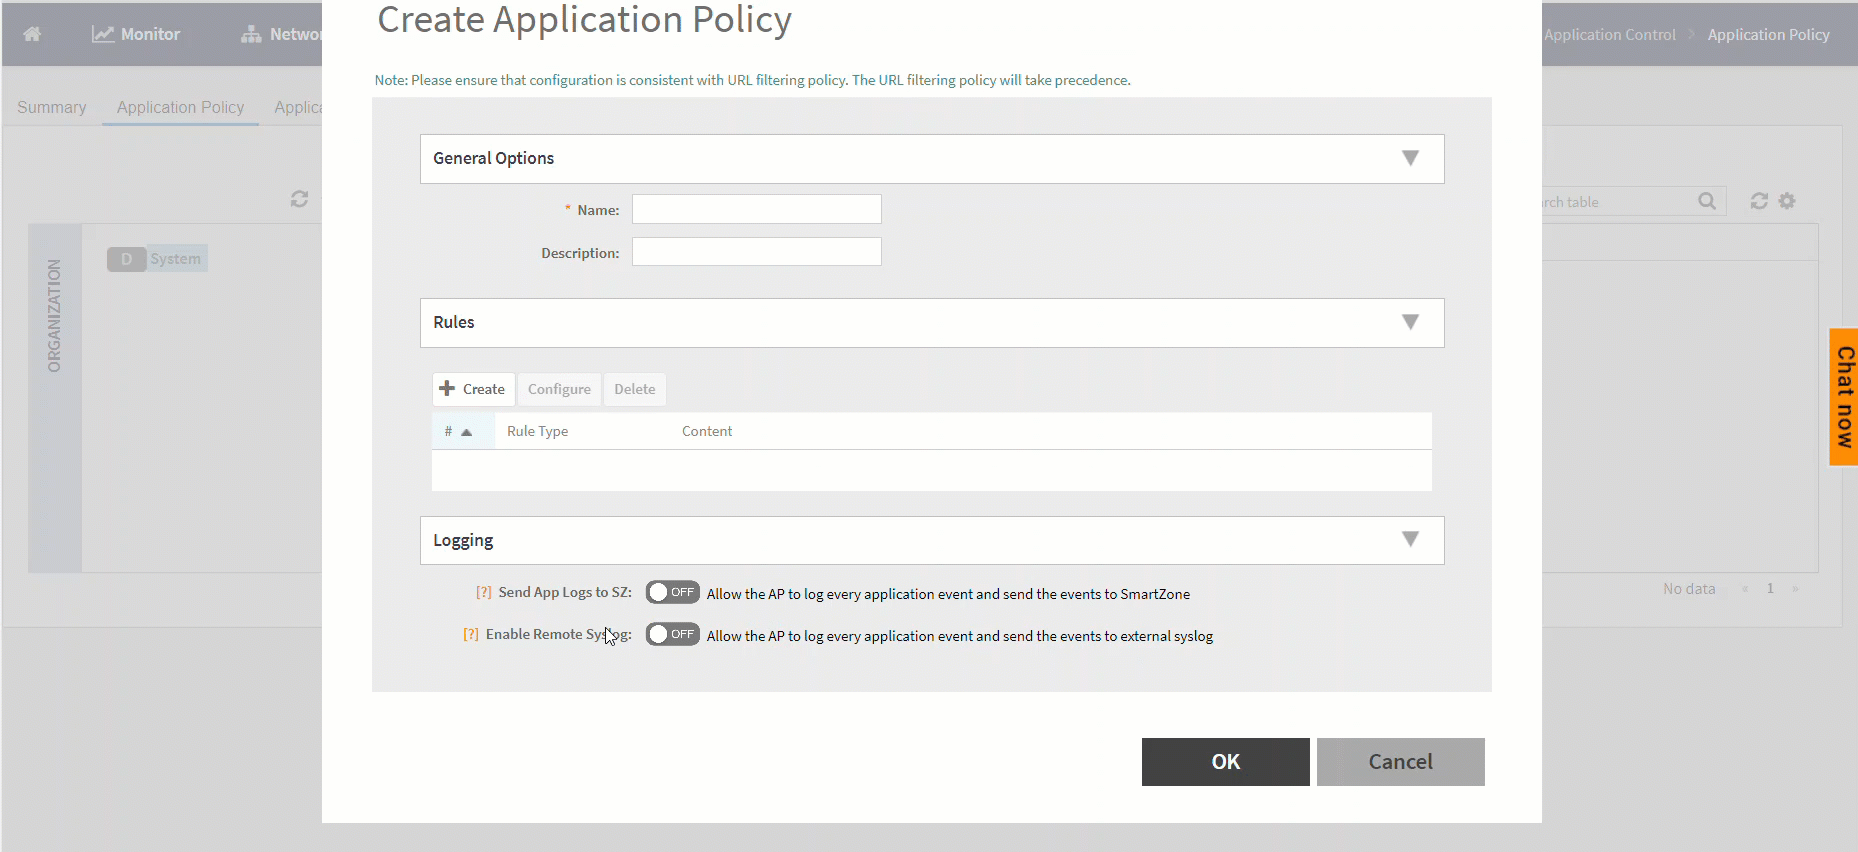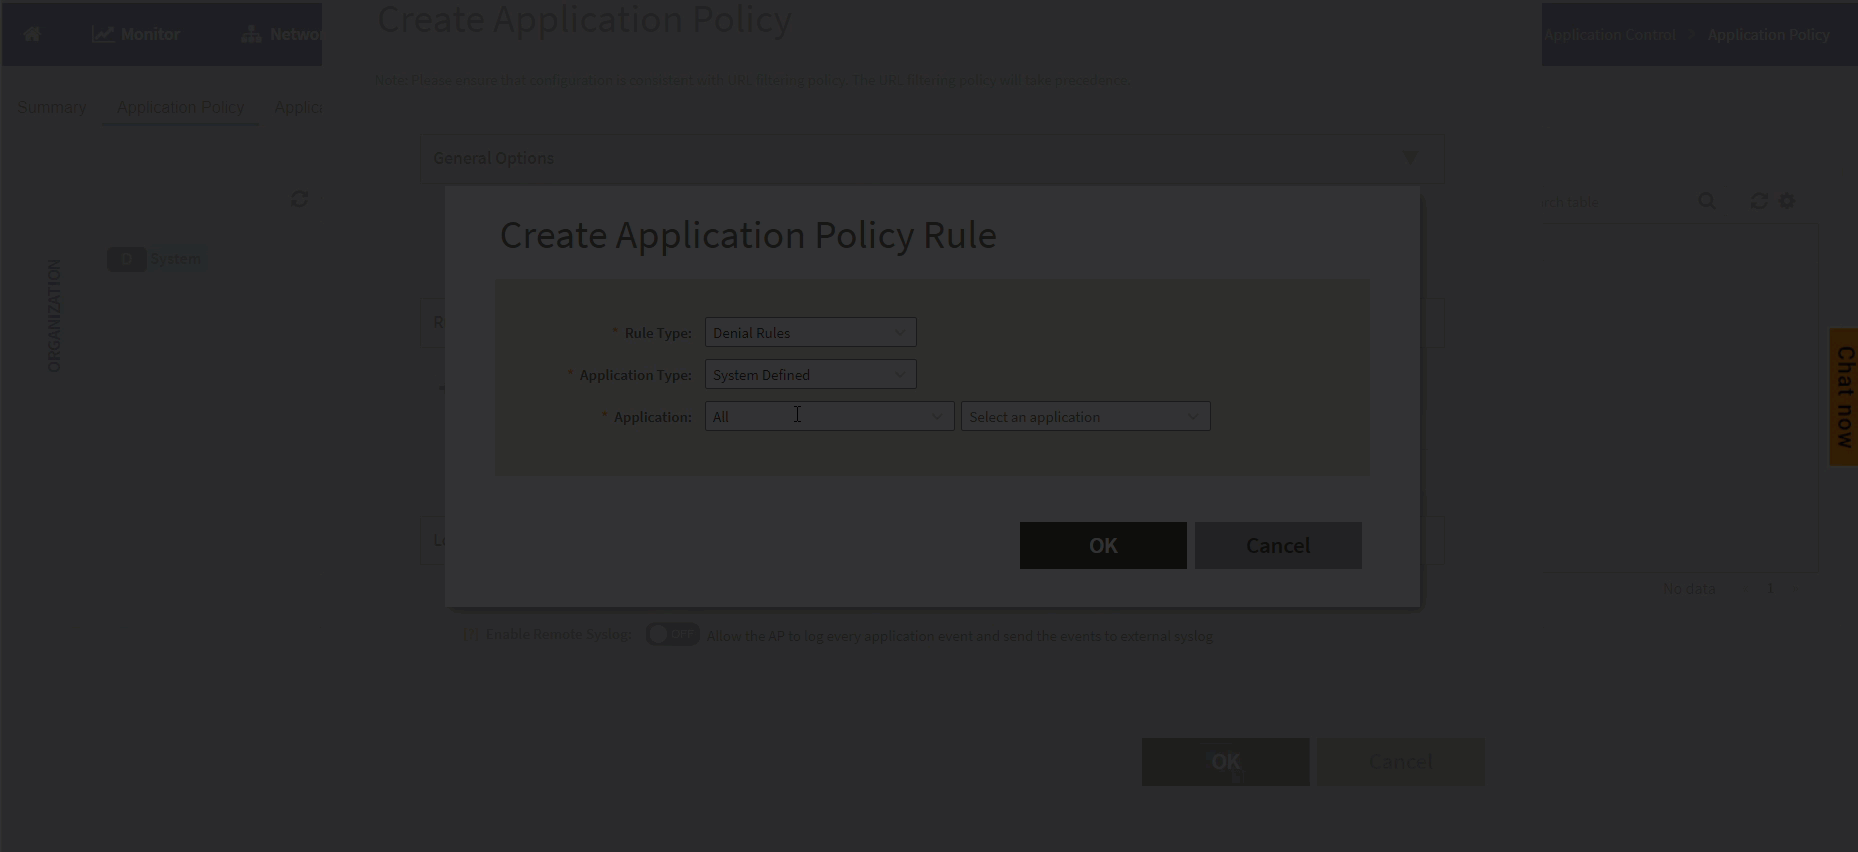
- Under General Options, enter the policy name and description.
- Under
Rules, click
Create to create a new rule.
Note: Each application policy can contain up to 128 rules.
- From the Rule Type list, select one of the following options:
- From the Application Type list, select an application type.
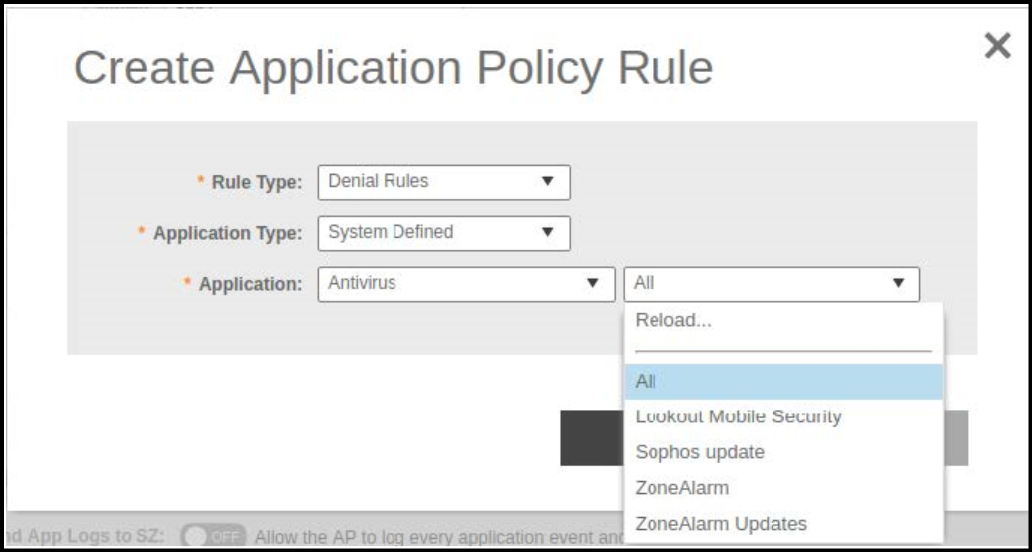
- From the Application
field, select the application for which you want to create a policy rule. For example, if you select All in the Anitvirus application category and save the application rule, the application rule list reflects all antivirus applications and is selected as a single entry in the rule list. A full category is counted as one rule in the allotment of 128 Layer 7 rules in a Layer 7 policy.
- Click OK to save the rule.
- Under Logging, select the appropriate option for the APs to log events:
- Click OK to save the application control policy.