Creating a WLAN Configuration
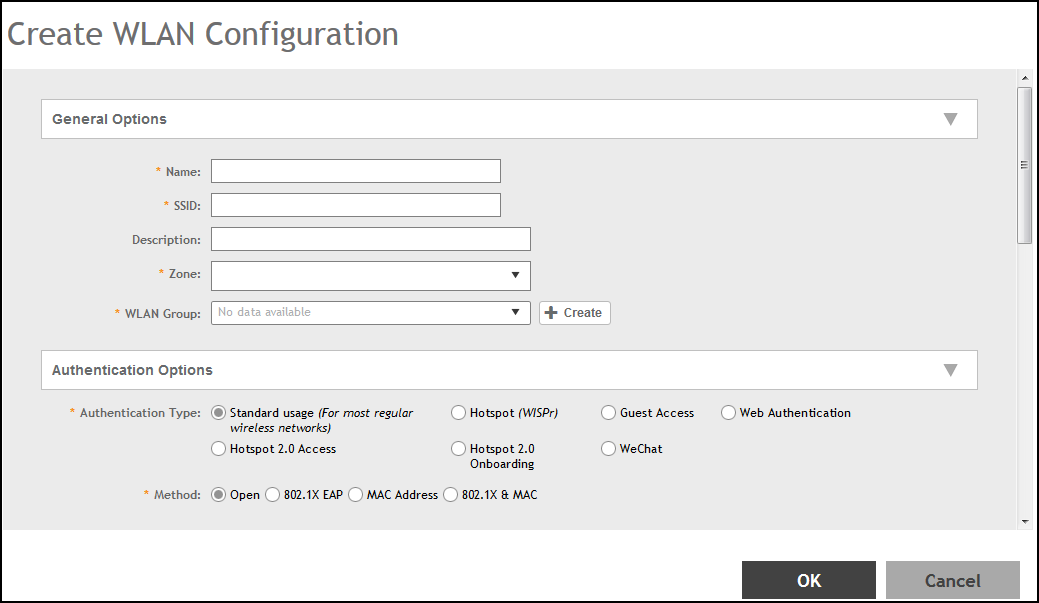
Complete the following steps to create a WLAN configuration for an AP zone.
- Go to page, from the System tree hierarchy, select the Zone to create a WLAN.
- Click Create. The Create WLAN Configuration page is displayed.
- Set the required configurations as detailed in
the following table.
WLAN Configuration for SZ100 and vSZ-E
Field Description Your Action General Options Name Indicates the user-friendly administrative name for the WLAN. Enter a name. SSID Indicates the SSID for the WLAN. Enter the SSID. Description Indicates a user-friendly description of the WLAN settings or function. Enter a short description. Zone Indicates the zone to which the WLAN belongs. Select the zone to which the WLAN settings apply. WLAN Group Indicates the WLAN groups to which the WLAN applies. Select the WLAN groups. Authentication Options Authentication Type Defines the type of authentication flow for the WLAN. Note: Authentication types such as Web Authentication, and Guest Access except WeChat are supported by APs in IPv6 mode.Select the required option: - Standard Usage—This is a standard WLAN approriate for most wireless networks.
- Hotspot (WISPr)— Select this option to use a
hotspot service (suitable for external captive
portal workflows) or WISPr.
Note: Hotspot (WISPr) applies to WLAN traffic that is tunneled and not tunneled.
- Guest Access — Select this option, for guest
users to use a WLAN. After creating a WLAN for guest
access, you can start generating guest passes.
For more information about Hotspot 2.0 online signup, refer to the Hotspot 2.0 Reference Guide for this release.
- Web Authentication — Select this option to require all WLAN users to complete a web-based login every time they attempt to connect to the network.
- Hotspot 2.0 Access — Select this option to apply a previously created Hotspot 2.0 operator profile to this WLAN. Refer to the Hotspot 2.0 Reference Guide for this release.
- Hotspot 2.0 Onboarding — Click this option if
you want to use this WLAN for Hotspot 2.0
onboarding. For more information, refer to the
Hotspot 2.0 Reference Guide. Hotspot 2.0 onboarding
allows Open and 802.1x EAP authentication methods.
Note: This authentication type cannot be reconfigured to use a different authentication type due to differences in how Authentication and Accounting profiles are stored and subsequently mapped to WLAN configurations.
- WeChat — Select this option if you want the WLAN usage through WeChat.
Method Specifies the authentication mechanism. Select the following option: - Open (Default)—No authentication mechanism is
applied to connections. If WPA or WPA2 encryption is
used, this implies WPA-PSK authentication.
Under Authentication Type, if Web Authentication is selected, the Open is the only available authentication option, even though PSK-based encryption is supported.
- 802.1X EAP—A very secure
authentication/encryption method that requires a
back-end authentication server, such as a RADIUS
server. Your choice mostly depends on the types of
authentication the client devices support and your
local network authentication environment. If you
select Enable RFC Location Delivery Support for Authentication & Accounting Server, enter
the Operator Realm.
Selecting the authentication method as Hotspot (WISPr) also allows you to select 802.1x EAP as an authentication option. This enables a two-step authentication method when shared and pre-authenticated devices are used, or when user equipment is shared among multiple users. The device access is successful when both authentication processes are completed successfully: 802.1x EAP authentication first, followed by Hotspot (WISPr) authentication.
- MAC Address—Authenticates clients by MAC address.
- 802.1X EAP & MAC—Selecting this option
indicates that the 802.1x EAP and MAC address
authentication methods must both pass for a user to
successfully authenticate. First, MAC address
authentication is verified; if that passes, 802.1x
EAP authentication is processed. After the two
authentication methods succeed, the user equipment
gains access to the WLAN. Authentication is handled
by a back-end RADIUS server.
When this authentication method is selected, the MAC Authentication and MAC Address Format fields will be shown within the Authentication Options section.
Reserve SSID The Reserve SSID is broadcasted in case the AP loses its SSH Control connection to the controller, or Dataplane if it is tunneling traffic. The Reserve SSID will typically become operational within 3 minutes, depending upon when the lost heartbeat is detected.
This allows Open, WPA2/WPA3, WPA2/WPA3 mixed or WPA-mixed mode to be used as back up SSID. Reserve SSID is limited to only one WLAN per Zone.
By default it is disabled.
Encryption Options 7.0.0 Patch 4 updateMethod Encryption options is a list of security protocols used to protect wireless networks. Select the appropriate encryption option by clicking the corresponding radio button.
Select the option: - WPA2—Enhanced WPA encryption using
AES/AUTO algorithm. Choose
the following:
- AES/AUTO:
- PassPhrase - Enter passphrase. A passphrase is a sequence of words or long string of characters used to secure access to a network, system or a service.
- Enable 802.11r Fast Roaming - Click the 802.11r Fast Roaming radio button and enter the Mobility Domain ID.
- 802.11w MFP - Select the approriate option.
- Dynamic PSK -
- AES/AUTO:
- WPA3—Enhanced WPA3 encryption using
AES algorithm.
Important: Enable this option for 6G radio.
- AES:
- SAE Passphrase : Enter the SAE (Simultaneous Authentication of Equals) passphrase. It is a component of the WPA3 security protocol. You can use the Eye icon to toggle the visibility of the passphrase.
- Enable 802.11r Fast Roaming - Click the 802.11r Fast Roaming radio button and enter the Mobility Domain ID.
- 802.11w MFP - By default this option is selected as Required. This is an IEE 802.11 standard that enhances the security of the wireless network
- Transistion Disable Indication - Is disabled by default. If enabled, it directs the Wi-Fi clients to use the most secure algorithm they support when connecting to the Access Point. It is only available when WPA3 or OWE (Enhanced Open) is enabled.
- AES:
- WPA2/WPA3-Mixed - This configuration allows
both WPA2 and WPA3 devices to connect to the same
network. By default the algorithm is AES.
- Passphrase - Enter the network passphrase.
- SAE
Passphrase Enter the Simultaneous
Authentication of Equals (SAE) passphrase.
You can use the Eye icon to toggle the visibility of the passphrase.
- DPSK3- Enables DPSK for both WPA2 and WPA3 clients. When set to On, there is no need to configure Passphrase and SAE passphrase. The external DPSK server will manage password assignment. This feature is only supported with RUCKUS Cloudpath as the external DPSK server.
- Transition Disable Indication - This option is set to On when DPSK3 is enabled and cannot be modified. When enabled, it directs Wi-Fi clients to use the most secure algorithm they support when connecting to the Access Point. This option is only available when WPA3 or OWE (Enhanced Open) is enabled.
- WPA-Mixed — Allows networks to support both WPA and WPA2 compliant devices. Use this setting if your network includes a mix of older clients that only support WPA and TKIP, and newer clients that support WPA2 and AES. Choose the algorithm AES/AUTO algorithm.
Reserve SSID Is a limited to only one WLAN per Zone. The Reserve SSID option is displayed only when standard + open + (WPA2/ WPA3 or WPA2/WPA3-Mixed or WPA mixed is enabled.
By default it is disabled. Data Plane Options Access Network Defines the data plane tunneling behavior. Enable Tunnel WLAN traffic through Ruckus GRE.
Configure the following options as appropriate:- GRE Tunnel Profile: Manages AP traffic. Select the profile from the list.
- Split Tunnel Profile: Enables split
tunneling to manage user traffic between corporate
and local traffic. Enable the profile from the list.
Click Create to create a new
profile or click
 to edit a profile. By
default, the option is disabled.
Note: RuckusGRE or SoftGRE must be enabled on the WLAN before mapping it to a Split Tunnel Profile.vSZ-D DHCP/NAT Enables tunneling option for DHCP/NAT. Select the required check boxes: RADIUS based DHCP/NAT Enables RADIUS-based DHCP/NAT settings. DHCP server authorizes remote clients and allocates addresses based on replies from a RADIUS server. Select the required check boxes: Authentication & Accounting Server (for WLAN Authentication Type: Standard ) Authentication Server Specifies the server used for authentication on this network. By enabling proxy, authentication requests will flow through the controller. In a non-proxy mode, the AP will communicate directly with the authentication server without going through the controller. Accounting Server Specifies the server used for accounting messages. By enabling proxy, accounting messages are sent by the controller. In a non-proxy mode, the AP will communicate accounting messages directly. Hotspot Portal (for WLAN Authentication Type: Hotspot (WISPr)) Hotspot (WISPr) Portal Defines hotspot behavior, such as redirects, session timers, and location information, among others. Select the hotspot portal profile that you want this WLAN to use. Bypass CNA Bypasses the Apple CNA feature on iOS and OS X devices that connect to this WLAN. Select the Enable check box. Authentication Server Indicates the authentication server that you want to use for this WLAN. Choose the option. Options include Local DB, Always Accept, and any AAA servers that you previously added. Additionally, if you want the controller to proxy authentication messages to the AAA server, select the Use Controller as Proxy check box. When the SSH tunnel between the AP and the controller is down, you can enable Backup Authentication Service to back up the AP's authentication services to a secondary device.
Note: For WISPr survivability, the customer portal must use the AP WISPr ZD-Style API/Backup AAA authentication to continue the WISPr service.Accounting Server Indicates the RADIUS Accounting server that you want to use for this WLAN. Choose the option. You must have added a RADIUS Accounting server previously. Additionally, if you want the controller to proxy accounting messages to the AAA server, select the Use the Controller as Proxy check box. When the SSH tunnel between the AP and the controller is down, you can enable Backup Accounting Service to back up the AP's accounting services to a secondary device.
Note: For WISPr survivability, the customer portal must use the AP WISPr ZD-Style API/Backup AAA authentication to continue the WISPr service.Guest Access Portal (for WLAN Authentication Type: Guest Access) Guest Portal Service Indicates the guest access portal to be used on this WLAN. Choose the guest portal service. Bypass CNA Bypasses the Apple CNA feature on iOS and OS X devices that connect to this WLAN. Select the Enable check box. Guest Authentication Manages guest authentication. Select: Guest Accounting Indicates the RADIUS Accounting server that you want to use for this WLAN. Choose the server. You must have added a RADIUS Accounting server previously. Additionally, if you want the controller to proxy accounting messages to the AAA server, select the Use the Controller as Proxy check box. Authentication & Accounting Server (for WLAN Authentication Type: Web Authentication) Web Authentication Portal Indicates the web authentication portal to use for this WLAN. Choose the web authentication portal from the drop-down menu. Bypass CNA Bypasses the Apple CNA feature on iOS and OS X devices that connect to this WLAN. Select the Enable check box. Authentication Server Indicates the authentication server that you want to use for this WLAN. Choose the option. Options include Local DB, Always Accept, and any AAA servers that you previously added. Additionally, if you want the controller to proxy authentication messages to the AAA server, select the Use the Controller as Proxy check box. Accounting Server Indicates the RADIUS Accounting server that you want to use for this WLAN. Choose the server. You must have added a RADIUS Accounting server previously. Additionally, if you want the controller to proxy accounting messages to the AAA server, select the Use the Controller as Proxy check box. Hotspot 2.0 Profile (for WLAN Authentication Type: Hotspot 2.0 Access) Hotspot 2.0 Profile Indicates the profile, which includes operator and identify provider profiles. Choose the profile. Authentication Server RFC 5580 Supports RFC 5580 location delivery on the WLAN, which carries location information in RADIUS exchanges. Select the check box. Accounting Server Updates Indicates the frequency to send interim updates. Configure the account update interval for accounting servers defined in the Hotspot 2.0 Identity Provider profile.
Enter the duration in minutes. Range: 0 through 1440. WeChat Portal (for WLAN Authentication Type: WeChat) WeChat Portal Defines the WeChat authentication URL, DNAT destination, and other information. Select a WeChat portal service. Accounting Server Indicates the RADIUS Accounting server that you want to use for this WLAN. Choose the server. You must have added a RADIUS Accounting server previously. Additionally, if you want the controller to proxy accounting messages to the AAA server, select the Use the Controller as Proxy check box. Forwarding Profile (for WLAN Usage > Access Network) Forwarding Policy Defines special data packet handling to be taken by the data plane when the traffic is tunneled. Forwarding Profile is Factory Default. It is disabled. Wireless Client Isolation Client Isolation Prevents wireless clients from communicating with each other. By default this option is disabled. Enable Client Isolation to separate wireless client traffic from all hosts on the same VLAN/subnet.
When Client Isolation is enabled the below options are available to enable or disable as appropriate:
- Isolate unicast packets: Isolates only unicast packets between a client isolation-enabled WLAN and other clients of the AP.
- Isolate multicast/broadcast packets: By default, this option is disabled, when enabled, only multicast packets between a client isolation and other clients of the AP are separated.
- Automatic support for VRRP/HSRP: By default, this option is disabled, when enabled, allows you to have isolation without adding physical MAC addresses of VRRP/HSRP routers. Client isolation only discovers virtual IP and MAC in VRRP/HSRP.
Isolation Whitelist Isolation whitelist allows you to manually specify a list of MAC and IP Addresses that override the blocked list. Click on the Add icon corresponding to the field to manually enter the MAC and IP addresses to the isolation whitelist. Note: Specify a default gateway that splits IP address into the host and network addresses in the whitelist.RADIUS Option NAS ID Defines the ID sent to the RADIUS server, which will identify the AP. Choose the option: NAS Request Timeout Indicates the duration after which an expected RADIUS response message is considered to have failed. Enter the timeout period (in seconds). NAS Max Number of Retries Indicates the maximum number of failed connection attempts after which the controller will fail over to the backup RADIUS server. Enter the maximum number of failed connection attempts. NAS Reconnect Primary Indicates the time interval after which the controller will recheck if the primary RADIUS server is available when the controller has failed over to the backup RADIUS server.
Enter the duration in minutes. Range: 1 through 60 minutes. The default interval is 5 minutes. Called Station ID Indicates the format for the called station ID, which is sent to the RADIUS server as an attribute, and can be used in policy decisions. Select a format: Single Session ID Accounting Enabling this feature allows the APs to maintain one accounting session for a client roaming between APs. If the client roams from one AP to another, the accounting session ID and statistics will be carried while roaming from one AP to the other. If the feature is not enabled, the accounting session ID is regenerated and statistics are also reset, essentially resetting the accounting. Select the Enable check box to use this feature. NAS IP Indicates the NAS IP address. Select the option: Vendor Specific Attribute Profile Indicates the VSA profile Select from the following options: Firewall Options Firewall Profile Indicates the zone for which the firewall profile applies. Select the option. Enable WLAN specific Applies the firewall profile to the WLAN. Select the option and update the following: - In the Rate Limiting field, select the Uplink and Downlink option to specify and apply rate limit values for the device policy to control the data rate.
- Select the L3 Access Control Policy from the drop-down list or click Create to create a new policy.
- Select the L2 Access Control Policy from the drop-down list or click Create to create a new policy.
- Select the Application Policy from the drop-down list or click Create to create a new policy.
- Select the URL Filtering Profile from the drop-down list or click Create to create a new profile.
- Select the Device Policy from the drop-down list or click Create to create a new policy.
Application Recognition and Control (ARC) Enables DPI-based Layer 7 application recognition, and if enabled, an application control policy. Recognition and control are performed on the AP. Select the option. Client Virtual ID Extraction Extracts the Virtual IDs of the users who login into the social media , public email such as WeChat, WhatsApp, hotmail, and cloud disk, and send these virtual ids to the auditing system.
URL Filtering Enables URL filtering on the WLAN controller to block or allow access to specific websites or web pages. Select the option. Advanced Options 7.0 updateBSS PriorityDetermines the traffic transmit preference of one WLAN compared to another. Traffic for the high priority WLANs are always sent before the low priority WLANs in the same QoS category (background, best effort, video, voice). Choose the priority: Client Fingerprinting Enables the AP to attempt to utilize DHCP fingerprinting to identify client devices by their operating system, device type, and host name. Select the check box. Note: DHCP is not always accurate in device identification, as different operating systems or device types can share the same DHCP signature, making it difficult for the AP to distinguish them. HTTP provides more accurate identification through the User-Agent field, but many devices either do not send HTTP packets or include incomplete User-Agent data, delaying passive detection by the AP.
Access VLAN Tags the WLAN traffic with a VLAN ID from 2 through 4094. By default, all client traffic will be assigned to the native (untagged) VLAN on the AP's Ethernet port, which is represented as VLAN ID 1. Select the check box and enter the VLAN ID. Hotspot 2.0 Onboarding Allows devices to connect to a Wi-Fi network automatically, wherein the service providers engage in roaming partnerships to provide seamless access to Wi-Fi networks. The devices are authenticated using credentials or certificates. Select the check box to allow Hotspot 2.0 Onboarding for the WISPr WLAN. Hide SSID Removes the SSID from Beacon frames. By removing the SSID, in most cases, clients will not show this SSID in their scan list unless the device is already configured to connect. This can simplify the network decision for an end user. Select the check box. Client Load Balancing Disables client load balancing on this WLAN if you toggle the switch to OFF (enabled by default). Click the Client Load Balancing toggle switch to OFF to disable this feature. Proxy ARP Enables proxy ARP. When proxy ARP is enabled on a WLAN, the AP provides proxy service for stations when receiving neighbor discovery packets (for example, ARP request and ICMPv6 Neighbor Solicitation messages), and acts on behalf of the station in delivering ARP replies. When the AP receives a broadcast ARP/Neighbor Solicit request for a known host, the AP replies on behalf of the host. If the AP receives a request for an unknown host, it forwards the request. Select the check box. DGAF Disables AP from forwarding downstream group-addressed frames. This option is available only when proxy ARP is enabled. Select the option. MAX Clients Limits the number of clients that can associate with this WLAN per AP radio (default is 100). Every connection attempt after this maximum value will not be permitted to connect. Enter the number of clients allowed. 802.11d Adds additional regulatory information to AP beacons and probe responses. This compliance information provides country-specific guidance such as permitted channels and transmit power, to ensure that the devices operate within the legal boundaries of the country 802.11d is helpful for many devices that cannot independently determine their operating country. Select the check box to enable this option. 802.11k Neighbor Report Enhances roaming by providing a list of neighbor APs to the client device. APs build a neighbor AP list via background scanning, and when the client plans to roam, it will request this list from the AP. This list is then used to perform efficient scanning to find a roaming candidate. Select the check box. Anti-spoofing Prevents attacks on genuine clients from rogue clients that could lead to service disruption, data loss, and so on. This is achieved by matching the MAC address or IP address (IPv4) of the client with the address in the RUCKUS database. If the addresses do not match, the packet is dropped. These checks are also performed on ingress data packets to catch spoofed data packets early. Enable the option. By default, the following options are also enabled: - ARP request rate limit: Enter the packets to be reviewed for Address Resolution Protocol (ARP) attacks per minute. In ARP attacks, a rouge client sends messages to a genuine client to establish connection over the network.
- DHCP request rate limit: Enter the packets to be reviewed for DHCP pool exhaustion per minute. When rouge clients send a DHCP request with a spoofed address, an IP address from the DHCP pool is assigned to it. If this happens repeatedly, the IP addresses in the DHCP pool are exhausted, and genuine clients may miss out on obtaining the IP addresses.
Note: When you enable anti-spoofing, an ARP request and DHCP request rate limiter are automatically enabled with default values (in packets per minute, or ppm) that are applied per client; implying that each client connected to an interface enabled with anti-spoofing is allowed to send a maximum of "X" ARP/DHCP request ppm. The value "X" is configured on the interface to which the client is connected.Force DHCP Requires the clients to obtain a valid IP address from DHCP within the specified number of seconds. This prevents clients configured with a static IP address from connecting to the WLAN. Additionally, if a client performs Layer 3 roaming between different subnets, in some cases the client sticks to the former IP address. This mechanism optimizes the roaming experience by forcing clients to request a new IP address. Select the check box. DHCP Option 82 Enables an AP to encapsulate additional information (such as VLAN ID, AP name, SSID, and MAC address) into the DHCP request packets before forwarding them to the DHCP server. The DHCP server can then use this information to allocate an IP address to the client from a particular DHCP pool based on these parameters. Select the option. DHCP Option 82 Format Enables an AP to encapsulate additional information (such as VLAN ID, AP name, SSID, MAC address, IF name, AP model, Location, Privacy type and Area name) into the DHCP request packets before forwarding them to the DHCP server. The DHCP server can then use this information to allocate an IP address to the client from a particular DHCP pool based on these parameters.
Enable the required format: DTIM Interval Indicates the frequency at which the Delivery Traffic Indication Message (DTIM) will be included in Beacon frames.
Enter the frequency number. Range: 1 through 255.
Directed MC/BC Threshold Defines the per-radio-client count at which an AP stops converting group-addressed data traffic to unicast. However, the Directed Threshold logic is only one part of the APs' multicast handling logic, which means there may be other factors that determine whether a frame is transmitted as unicast or multicast. APs support a feature called Directed Multicast (configurable only on AP CLI, enabled by default), which adds additional logic to the multicast flow. If Directed Multicast is disabled, the AP uses the Directed Threshold as the only criteria to determine whether to transmit a multicast packet as unicast. However, when Directed Multicast is enabled, the flow is changed. Directed Multicast is a feature that checks to see if a multicast packet is well-known or not. For well-known multicast packets, for example, Bonjour, uPNP, most IPv6 link- and node-local, and Spectralink, the AP still applies the Directed Threshold logic to determine conversion to unicast. For non well-known types, the AP monitors and maintains a database of client subscriptions using IGMP and MLD. If associated clients are subscribed to the multicast stream, then the AP always converts these packets to unicast, regardless of the Directed Threshold configuration. If there are no clients subscribed to the multicast stream, the AP drops these packets. It is important to be aware of this behavior when validating multicast operation in a deployment. Enter the client count number. Range: 0 through 128.
Client Tx/Rx Statistics Stops the controller from monitoring traffic statistics for unauthorized clients. Select the check box. Inactivity Timeout Indicates the duration after which idle clients will be disconnected. Enter the duration.
Range: 60 through 86400 seconds
User Session Timeout Indicates the duration after which the client gets disconnected. Note: Before getting disconnected the client can be either in an idle state or connected to the WLAN (SSID).Enter the duration.
Range: 120 to 864000 seconds (10 days).
Default Value: 172800 seconds (2 days).
Note: The default value will remain effected only when the session timeout is not applied from the Radius server.Note: The user session timeout is displayed only for those WLANs in which 802.1X or MAC authentication is enabled.7.0 updateWiFi 6/7Controls how the Wi-6/7 AP radios operate to support clients of various capabilities on a specific WLAN.
By default, this feature enabled (ON), allowing Wi-Fi 6/7 client devices and legacy Wi-Fi 5 client devices to interoperate with the Wi-Fi 6/7 APs and utilize Wi-Fi 6/7 features (such as OFDMA, TWT, 6GHz operation, Preamble Puncturing, 320MHz bandwidth, and MLO) available on the WLAN.
When disabled (OFF), the Wi-Fi 6/7 APs are downgraded to support Wi-Fi 4/5 capabilities. This allows Wi-Fi 6/7 and legacy client devices to interoperate with the Wi-Fi 6/7 APs on the WLAN; however, the Wi-Fi 6/7 features are not available for use. Disabling this feature is recommended when client drivers are not up to date or if the client device drivers have bugs
Refer to Wi-Fi 6 or Wi-Fi 7 Support for further feature information and the Wi-Fi support matrix.Note: From releases 5.2.1 through 6.1.2, this option was labeled as Wi-Fi 6. Beginning with release 7.0.0, this option is renamed as Wi-Fi 6/7.Default setting: Enabled (toggled ON).
Click the toggle button to OFF to downgrade the Wi-Fi 6/7 AP functionality, allowing support for Wi-Fi 6/7 and legacy client devices.
7.0MLO (Multi Link Operation)Allows client devices to seamlessly associate across multiple bands and facilitates smooth switch between these links. The Multi-Link Operation (MLO) feature enhances peak throughput by efficiently sending packets from the same flow across multiple links. It also minimizes latency due to increased channel access opportunities through these multiple links. Furthermore, it enables swift and seamless traffic routing based on channel capacity for load balancing without the need for disassociation and reassociation. Default radio frequency: 2.4GHz + 5GHz
You can also select a combination of two radio frequency. For example, 2.4 GHz + 5 GHz, 2.4 GHz + 6 GHz or 5 GHz + 6 GHz.
OFDM Only Disconnects 802.11b devices from the WLAN and all devices are forced to use higher data rates for more efficient airtime usage. This setting only affects the 2.4-GHz radio. OFDM is used by 802.11a, g, n, and ac, but is not supported by 802.11b. Select the option. BSS Min Rate Forces client devices to both be closer to the AP and to use higher, more efficient rates when you increase the BSS minimum rate above the default (all rates) setting. The BSS minimum rate is the lowest data rate supported on the WLAN. When OFDM-only is enabled, it takes higher priority than BSS minimum rate settings. Select the option. Mgmt Tx Rate Sets the transmit rate for management frame types such as beacon and probes. Select the value. 6G BSS Min Rate Forces client devices to both be closer to the AP and to use higher, more efficient rates when you increase the BSS minimum rate above the default (all rates) setting. The BSS minimum rate is the lowest data rate supported on the WLAN. When OFDM-only is enabled, it takes higher priority than BSS minimum rate settings. Select one of the following option: 6G Mgmt Tx Rate Sets the transmit rate for management frame types such as beacon and probes. Select one of the following option: Service Schedule Controls when the WLAN service is active. The purpose of this setting is to automatically enable or disable a WLAN based on a predetermined schedule. By default, the service is Always On. Always Off can be checked in order to create a WLAN and apply it, but prevent it from advertising until ready. The Specific setting allows a configurable schedule based on time of day and days of the week. Note: When a service schedule is created, it is saved by the controller and AP using time zone of the browser. When it is enforced by the AP, the AP will enforce it according to the time zone of the browser when it was configured.Choose the option: Band Balancing Disables band balancing only for this WLAN, if you select the check box. Select the Disable band balancing for this WLAN service check box. Qos Map Set Reprioritizes downlink packets based on the configured mappings. When an AP receives a downlink packet, it checks the existing DSCP (Layer 3 QoS) marking, compares it to this map set and then changes the user priority (Layer 2 QoS) values for transmission by the AP.
To configure this feature, select the User Priority (UP) from the table (0-7) and configure the DSCP (0-64) range that will be mapped to this UP.
Exceptions can also be added such that the original DSCP and UP tagging are preserved and honored by the AP.
Select Enable QOS Map Set. Multicast Filter Drops the broadcast and multicast from the associated wireless clients. Click to enable this option. SSID Rate Limiting Enforces an aggregate rate limit for all users of the WLAN. The purpose of this feature is to prevent the combined throughput from all users of an SSID from exceeding this threshold. This feature is different from per-user rate limiting, which enforces the same rate limit for each individual device. Select Uplink and Downlink check boxes and enter the limiting rates in mbps respectively. Range: 1 mbps through 1000 mbps. Multicast Rate Limiting Multicast rate limit can be configured at WLAN level. The UplinkDownlink values are displayed only if the multicast rate limit is enabled.
The Downlink traffic is limited to 50% of the configured multicast rate limiting. For example, if multicast rate limiting downlink traffic is set to 6Mbps, only 50 percent of the traffic, a maximum of 3.00Mbps to 4.00Mbps traffic passes per second. This limit is only for downlink and shall not be affected by BSS Min Rate setting.
Note: SSID Rate Limit always take precedence, if, Mutlicast Rate Limit is also configured.Select the Uplink and Downlink check boxes and enter the limiting rates in Mbps, respectively. Range: 1 through 100 Mbps.
DNS Server Profile Allows the AP to inspect DHCP messages and overwrite the DNS servers with the DNS server configured in this profile. This allows for policy-based DNS application in which unique users/roles should use a different DNS server than others. Select a profile from the drop-down menu. Select Disable from the drop-down menu if you want to disable the DNS Server profile for the WLAN service. Click  to add a new profile or click
 to edit a profile.
DNS Spoofing Profile When an AP receives a DNS packet all the fields in the packet are validated. Note: Only A/AAAA DNS query packets are considered. When same domain name is present in both DNS spoofing profile and walled garden table in WISPr WLAN then AP DNS cache is updated with the IP address present in the DNS spoofing profile.If DNS spoof and URL filtering with safe search is enabled, URL filtering(safe search) takes the precedence for "goggle", "You Tube", "Bing" domain names. If safe search is not enabled, DNS-Spoof takes the precedence. If safe search is not enabled and URL filtering is enabled also DNS-Spoof takes the precedence.Select a profile from the drop-down menu. Select Disable from the drop-down menu if you want to disable the DNS Spoofing profile for the WLAN service. Click to add a new profile or click
to edit a profile. Precedence Profile Defines the relative policy assignment priority for some specific settings. For example, if a WLAN is configured to use VLAN 10, and an AAA/role policy is configured for VLAN 20, and a device OS policy is configured for VLAN 30, and a user/device connects to the WLAN matching all of these policies, which VLAN should be assigned? The precedence policy determines which setting takes priority. Select the required option. Click  to add a new profile or click
 to edit a profile.
Client Flow Data Logging Sends a log message with source MAC, destination MAC, source IP, destination IP, source port, destination port, L4 protocol, and AP MAC of each packet session to the external syslog server. This function is provided by the AP syslog client (not the controller syslog client), which must be enabled at the zone level in order to support this client flow logging. Select the check box to log the client-flow data to the external syslog server. Then enable AP syslog functionality from the Zone settings. Airtime Decongestion Mitigates airtime congestion caused by management frames in high density deployments. Select the check box. Join RSSI threshold Indicates the signal threshold that could connect to the Wi-Fi. If Airtime Decongestion is enabled, Join RSSI threshold is automatically disabled. Enter the Client RSSI threshold to allow joining. Range: -60 through -90 dBm. Transient Client Management Discourages transient clients from joining the network. Select the Enable Transient Client Management check box and set the following parameters: - Join wait time—Enter the wait time before a client can be permitted to join. Range: 1 through 60 secs.
- Join expire time—Enter the time during which a rejoin request is accepted without delay. Range: 1 through 300 secs.
- Join wait threshold—Enter the number of join attempts after which a client is permitted to join even before the join wait time expires.
Optimized Connectivity Experience (OCE) OCE enables probe response suppression and prevents devices with marginal connectivity from joining the network. Optimizes the connectivity experience for OCE-enabled APs and stations. Select Optimized Connectivity Experience (OCE) and set the following parameters: - Broadcast Probe Response Delay - Indicates the time delay to transmit probe response frames in milliseconds.
- RSSI-based Association Rejection Threshold - Indicates the minimum threshold value to connect to the network (in dBm). If the value entered is less than the minimum threshold value, then any RSSI-based association is rejected.
AP Host Name Advertisement in Beacon AP host name is included in beacon. By default this feature is disabled. Enable this option to view the AP host name. 7.0QOS MirroringThis feature allows an AP to use a client's uplink Quality of Service (QoS) classification (Voice, Video, Best Effort or Background) to classify the client device's downlink packets in the mirrored (reverse direction) stream. The AP assigns the downlink packets to the same QoS category as the uplink packets. - Disabled - QoS mirroring is disabled for all the clients.
- Enabled via Protocol - QoS mirroring is enabled only for clients that send Mirrored Stream Classification Service (MSCS) requests. Legacy clients are not supported with QoS preference. This is the default setting.
- Enabled for All - Unilateral mirroring is applied for this option and QoS mirroring is enabled for all the clients.
WLAN Configuration for SZ300 and vSZ-H
Field Description Your Action General Options Name Indicates the user-friendly administrative name for the WLAN. Enter a name. SSID Indicates the SSID for the WLAN. Enter the SSID. Description Indicates a user-friendly description of the WLAN’s settings or function. Enter a short description. Zone Indicates the zone to which the WLAN configuration applies. Select the zone to which the WLAN settings apply. WLAN Groups Indicates the WLAN groups to which the WLAN applies. Select the WLAN groups to which the WLAN configuration applies. Authentication Options Authentication Type Defines the type of authentication flow for the WLAN. Note: Authentication types such as WeChat, Web Authentication, and Guest Access are not supported by APs in IPv6 mode.Select the required option: - Standard Usage—This is a regular WLAN suitable for most wireless networks.
- Hotspot (WISPr)—Click this option if
want to use a hotspot service (use this type for
external captive portal workflows) or WISPr.
Note: Hotspot (WISPr) applies to WLAN traffic that is tunneled and not tunneled.
- Guest Access—Click this option if you
want guest users to use this WLAN. After you
complete creating this WLAN for guest access, you
can start generating guest passes.
For more information about Hotspot 2.0 online signup, see the Hotspot 2.0 Reference Guide for this release.
- Web Authentication—Click this option if you want to require all WLAN users to complete a web-based logon to this network every time they attempt to connect.
- Hotspot 2.0 Access—Click this option
if you want a Hotspot 2.0 operator profile that you
previously created to use this WLAN. See the Hotspot
2.0 Reference Guide for this release.
Note: You can select 8021.X EAP + “WPA3” or “WPA2/WPA3-Mixed” for HS2.0 access WLAN to add more security.
- Hotspot 2.0 Onboarding—Click this
option if you want to use this WLAN for Hotspot 2.0
onboarding. See the Hotspot 2.0 Reference Guide for
this release for more information. Hotspot 2.0
onboarding allows for Open and 802.1x EAP
authentication methods.
Note: This authentication type cannot be reconfigured to use a different authentication type due to differences in how Authentication and Accounting profiles are stored and subsequently mapped to WLAN configurations.
- WeChat—Click this option if you want the WLAN usage through WeChat.
Method Specifies the authentication mechanism. Select the following option: - Open (Default)—No authentication
mechanism is applied to connections. If WPA or WPA2
encryption is used, this implies WPA-PSK
authentication.
If you clicked Web Authentication in Authentication Type, Open is the only available authentication option, even though PSK-based encryption can be supported.
- 802.1X EAP—A very secure
authentication/encryption method that requires a
back-end authentication server, such as a RADIUS
server. Your choice mostly depends on the types of
authentication the client devices support and your
local network authentication environment. If you
select Enable RFC Location Delivery Support
for Authentication & Accounting
Server, enter the Operator Realm.
Selecting the authentication method as Hotspot (WISPr) allows you to select 802.1x EAP as an authentication option. This enables a two-step authentication method when shared and pre-authenticated devices are used, or when user equipment is shared among multiple users. The device access is successful when both authentication processes are completed successfully: 802.1x EAP authentication first, followed by Hotspot (WISPr) authentication.
Selecting the authentication method as Hotspot 2.0 Access with support of WPA3 allows you to select 802.1x EAP as an authentication option.
- MAC Address—Authenticate clients by MAC address.
- 802.1X EAP & MAC—Selecting this
option indicates that the 802.1x EAP and MAC address
authentication methods must both pass for a user to
successfully authenticate. First, MAC address
authentication is verified; if that passes, 802.1x
EAP authentication is processed. After the two
authentication methods succeed, the user equipment
gains access to the WLAN. Authentication is handled
by a back-end RADIUS server.
When this authentication method is selected, the MAC Authentication and MAC Address Format fields will be shown within the Authentication Options section.
Encryption Options 7.0.0 patch 4 updateMethod Specifies the encryption method. WPA and WPA2 are both encryption methods certified by the Wi-Fi Alliance; WPA2 with AES is the recommended encryption method. The Wi-Fi Alliance will be mandating the removal of WEP due to its security vulnerabilities, and RUCKUS recommends against using WEP, if possible.
Select the option: - WPA2—Enhanced WPA encryption using
AES/AUTO algorithm. Choose
the following:
- AES/AUTO:
- PassPhrase - Enter passphrase. A passphrase is a sequence of words or long string of characters used to secure access to a network, system or a service.
- Enable 802.11r Fast Roaming - Click the 802.11r Fast Roaming radio button and enter the Mobility Domain ID.
- 802.11w MFP - Select the approriate option.
- Dynamic PSK -
- AES/AUTO:
- WPA3—Enhanced WPA3 encryption using
AES algorithm.
Important: Enable this option for 6G radio.
- AES:
- SAE Passphrase : Enter the SAE (Simultaneous Authentication of Equals) passphrase. It is a component of the WPA3 security protocol. You can use the Eye icon to toggle the visibility of the passphrase.
- Enable 802.11r Fast Roaming - Click the 802.11r Fast Roaming radio button and enter the Mobility Domain ID.
- 802.11w MFP - By default this option is selected as Required. This is an IEE 802.11 standard that enhances the security of the wireless network
- Transistion Disable Indication - Is disabled by default. If enabled, it directs the Wi-Fi clients to use the most secure algorithm they support when connecting to the Access Point. It is only available when WPA3 or OWE (Enhanced Open) is enabled.
- AES:
- WPA2/WPA3-Mixed - This configuration allows
both WPA2 and WPA3 devices to connect to the same
network. By default the algorithm is
AES.
- Passphrase - Enter the network passphrase.
- SAE Passphrase Enter
the Simultaneous Authentication of Equals (SAE)
passphrase.
You can use the Eye icon to toggle the visibility of the passphrase.
- DPSK3- Enables DPSK for both WPA2 and WPA3 clients. When set to On, there is no need to configure Passphrase and SAE passphrase. The external DPSK server will manage password assignment. This feature is only supported with RUCKUS Cloudpath as the external DPSK server.
- Transition Disable Indication - This option is set to On when DPSK3 is enabled and cannot be modified. When enabled, it directs Wi-Fi clients to use the most secure algorithm they support when connecting to the Access Point. This option is only available when WPA3 or OWE (Enhanced Open) is enabled.
- WPA-Mixed — Allows networks to support both WPA and WPA2 compliant devices. Use this setting if your network includes a mix of older clients that only support WPA and TKIP, and newer clients that support WPA2 and AES. Choose the algorithm AES/AUTO algorithm.
Reserve SSID The Reserve SSID is broadcasted in case the AP loses its SSH Control connection to the controller or Dataplane if it is tunneling traffic. The Reserve SSID will typically become operational within 3 minutes, depending upon when the lost heartbeat is detected.
This allows Open, WPA2/WPA3, WPA2/WPA3 mixed or WPA-mixed mode to be used as back up SSID. Reserve SSID is limited to only one WLAN per Zone.
By default it is disabled.
Data Plane Options Access Network Defines the data plane tunneling behavior. Enable Tunnel WLAN traffic through Ruckus GRE.
Configure the following options as appropriate:- GRE Tunnel Profile: Manages AP traffic. Select the profile from the list.
- Split Tunnel Profile: Enables split
tunneling to manage user traffic between corporate
and local traffic. Enable the profile from the list.
Click Create to create a new
profile or click to edit a profile. By
default, the option is disabled.
Core Network Defines the network mode. Select the option: vSZ-D DHCP/NAT Enables tunneling option for DHCP/NAT. Select the required check boxes: RADIUS based DHCP/NAT Enables RADIUS-based DHCP/NAT settings. The DHCP server authorizes remote clients and allocates addresses based on replies from a RADIUS server. Select the required check boxes: Flexi-VPN Profile Enables forwarding of tunneled traffic to another remote DP instance through inter-DP RuckusGRE Tunnel (Flexi). Note: If there are more than 40 DPs approved, the controller limits the user to use Flexi-VPN feature.Select the profile from the list. Authentication & Accounting Server (for WLAN Authentication Type: Standard usage) Authentication Server Specifies the server used for authentication on this network. By enabling Proxy, authentication requests will flow through the controller. In a non-proxy mode, the AP will communicate directly with the authentication server without going through the controller. Accounting Server Specifies the server used for accounting messages. By enabling Proxy, accounting messages are sent by the controller. In a non-proxy mode, the AP will communicate accounting messages directly. Hotspot Portal (for WLAN Authentication Type: Hotspot (WISPr)) Hotspot (WISPr) Portal Defines hotspot behavior such as redirects, session timers, and location information among others. Select the hotspot portal profile that you want this WLAN to use. Bypass CNA Bypasses the Apple CNA feature on iOS and OS X devices that connect to this WLAN. Select the Enable check box. Authentication Service Indicates the authentication server that you want to use for this WLAN. Choose the option. Options include Local DB, Always Accept, and any AAA servers that you previously added. Select: - Use Controller as Proxy for the controller to proxy authentication messages to the AAA server
- Use Realm-based profile to list contents the realm-based profile
When the SSH tunnel between the AP and the controller is down, you can enable Backup Authentication Service to back up the AP's authentication services to a secondary device.
Note: The customer portal must use AP WISPr ZD-Style API/Backup AAA to continue to provide the WISPr service for WISPr survivability.Accounting Service Indicates the RADIUS Accounting server that you want to use for this WLAN. Choose the option. You must have added a RADIUS Accounting server previously. Additionally, if you want the controller to proxy accounting messages to the AAA server, select the Use the Controller as Proxy check box.
- Use Controller as Proxy for the controller to proxy authentication messages to the AAA server
- Use Realm-based profile to list contents the realm-based profile
When the SSH tunnel between the AP and the controller is down, you can enable Backup Accounting Service to back up the AP's accounting services to a secondary device.
Note: The customer portal must use AP WISPr ZD-Style API/Backup AAA to continue to provide the WISPr service for WISPr survivability.Guest Access Portal (for WLAN Authentication Type: Guest Access) Guest Access Service Indicates the guest access portal to be used on this WLAN. Choose the guest portal service. Bypass CNA Bypasses the Apple CNA feature on iOS and OS X devices that connect to this WLAN. Select the Enable check box. Guest Authentication Manages guest authentication. Select: Guest Accounting Indicates the RADIUS Accounting server that you want to use for this WLAN. Choose the server. You must have added a RADIUS Accounting server previously. Additionally, if you want the controller to proxy accounting messages to the AAA server, select the Use the Controller as Proxy check box. Authentication & Accounting Service (for WLAN Authentication Type: Web Authentication) Web Authentication Portal Indicates the web authentication portal to use for this WLAN. Choose the web authentication portal from the list. Bypass CNA Bypasses the Apple CNA feature on iOS and OS X devices that connect to this WLAN. Select the Enable check box. Authentication Service Indicates the authentication server that you want to use for this WLAN. Choose the option. Options include Local DB, Always Accept, and any AAA servers that you previously added. Additionally, if you want the controller to proxy authentication messages to the AAA server, select the Use the Controller as Proxy check box. Accounting Service Indicates the RADIUS Accounting server that you want to use for this WLAN. Choose the server. You must have added a RADIUS Accounting server previously. Additionally, if you want the controller to proxy accounting messages to the AAA server, select the Use the Controller as Proxy check box. Hotspot 2.0 Profile (for WLAN Authentication Type: Hotspot 2.0 Access) Hotspot 2.0 Profile Indicates the profile, which includes the operator and identifies provider profiles. Choose the profile. Accounting Service (RFC 5580) Supports RFC 5580 location delivery on the WLAN, which carries location information in RADIUS exchanges. Select the check box. Accounting Service (Updates) Indicates the frequency to send interim updates. Configures the account update interval for accounting servers defined in the Hotspot 2.0 Identity Provider profile.
Enter the duration in minutes. Range: 0 through 1440. WeChat Portal (for WLAN Authentication Type: WeChat) WeChat Portal Defines the WeChat authentication URL, DNAT destination, and other information. Select a WeChat portal service. Accounting Server Indicates the RADIUS Accounting server that you want to use for this WLAN. Choose the server. You must have added a RADIUS Accounting server previously. Additionally, if you want the controller to proxy accounting messages to the AAA server, select the Use the Controller as Proxy check box. Forwarding Profile (for WLAN Usage > Access Network) Forwarding Policy Defines special data packet handling to be taken by the data plane when the traffic is tunneled. Forwarding Profile is Factory Default. It is disabled. Wireless Client Isolation Client Isolation Prevents wireless clients from communicating with each other. Enable Client Isolation to separate wireless client traffic from all hosts on the same VLAN/subnet.
When client isolation is enabled the below options are available to enable or disable as appropriate:
- Isolate unicast packets: Isolates only unicast packets between a client isolation-enabled WLAN and other clients of the AP.
- Isolate multicast/broadcast packets: By default, this option is disabled, when enabled, only multicast packets between a client isolation and other clients of the AP are separated.
- Automatic support for VRRP/HSRP: By default, this option is disabled, when enabled, allows you to have isolation without adding physical MAC addresses of VRRP/HSRP routers. Client isolation only discovers virtual IP and MAC in VRRP/HSRP.
Isolation Whitelist Isolation whitelist allows you to manually specify a list of MAC and IP Addresses that override the blocked list. Click on the Add icon corresponding to the field to manually enter the MAC and IP addresses to the isolation whitelist. Note: Specify a default gateway that splits IP address into the host and network addresses in the whitelist.RADIUS Option NAS ID Defines the ID sent to the RADIUS server, which will identify the AP. Choose the option: NAS Request Timeout Indicates the duration after which an expected RADIUS response message is considered to have failed. Enter the timeout period (in seconds). NAS Max Number of Retries Indicates the maximum number of failed connection attempts after which the controller will fail over to the backup RADIUS server. Enter the maximum number of failed connection attempts. NAS Reconnect Primary Indicates the time interval after which the controller will recheck if the primary RADIUS server is available when the controller has failed over to the backup RADIUS server.
Enter the duration in minutes. Range: 1 through 60 minutes. The default interval is 5 minutes. Called Station ID Indicates the format for the called station ID, which is sent to the RADIUS server as an attribute, and can be used in policy decisions. Select a format: Single Session ID Accounting Allows the APs to maintain one accounting session for a client roaming between APs. If the client roams from one AP to another, the accounting session ID and statistics will be carried while roaming from one AP to the other. If the feature is not enabled, the accounting session ID is regenerated and the statistics are also reset, essentially resetting the accounting session. Select the Enable check box. NAS IP Indicates the NAS IP address. Select the option: Vendor Specific Attribute Profile Indicates the VSA profile Select from the following options: Firewall Options Firewall Profile Indicates the zone for which the firewall profile applies. Select the option. Enable WLAN specific Applies the firewall profile to the WLAN. Select the option and update the following: - In the Rate Limiting field, select the Uplink and Downlink option to specify and apply rate limit values for the device policy to control the data rate.
- Select the L3 Access Control Policy from the drop-down list or click Create to create a new policy.
- Select the L2 Access Control Policy from the drop-down list or click Create to create a new policy.
- Select the Application Policy from the drop-down list or click Create to create a new policy.
- Select the URL Filtering Profile from the drop-down list or click Create to create a new profile.
- Select the Device Policy from the drop-down list or click Create to create a new policy.
Application Recognition and Control Enables DPI-based Layer 7 application recognition, and if enabled, an application control policy. Recognition and control are performed on the AP. Select the option. Client Virtual ID Extraction Extracts the Virtual IDs of the users who login into the social media , public email such as WeChat, Whats App, hotmail, and cloud disk, and send these virtual ids to the auditing system.
URL Filtering Enables URL filtering on the WLAN controller to block or allow access to specific websites or web pages. Select the option. Advanced Options 7.0 updateBSS PriorityDetermines the traffic transmit preference of one WLAN compared to another. Traffic for the high priority WLANs are always sent before the low priority WLANs in the same QoS category (background, best effort, video, voice). Choose the priority: Client Fingerprinting Enables the AP to attempt to utilize DHCP fingerprinting to identify client devices by their operating system, device type, and host name. Select the check box. Note: DHCP is not always accurate in device identification, as different operating systems or device types can share the same DHCP signature, making it difficult for the AP to distinguish them. HTTP provides more accurate identification through the User-Agent field, but many devices either do not send HTTP packets or include incomplete User-Agent data, delaying passive detection by the AP.
Access VLAN Tags the WLAN traffic with a VLAN ID from 2 through 4094. By default, all client traffic will be assigned to the native (untagged) VLAN on the AP's Ethernet port, which is represented as VLAN ID 1. Select the check box and enter the VLAN ID. Hotspot 2.0 Onboarding Allows devices to connect to a Wi-Fi network automatically, wherein the service providers engage in roaming partnerships to provide seamless access to Wi-Fi networks. The devices are authenticated using credentials or certificates. Select the check box to allow Hotspot 2.0 Onboarding for the WISPr WLAN. Hide SSID Removes the SSID from beacon frames. By removing the SSID, in most cases, clients will not show this SSID in their scan list unless the device is already configured to connect. This can simplify the network decision for an end user. Select the check box. Client Load Balancing Disables client load balancing on this WLAN if you toggle the switch to OFF (enabled by default). Click the Client Load Balancing toggle switch to OFF to disable this feature. Proxy ARP Enables proxy ARP. When proxy ARP is enabled on a WLAN, the AP provides ARP response service for stations. When the AP receives an ARP request for a known host, it replies with an ARP response on behalf of the host. If the AP receives a request for an unknown host, it forwards the request. Select the check box. 6.0 updateDGAFDisables AP from forwarding downstream group-addressed frames. This option is available only when proxy ARP is enabled. Select the option. ND Proxy Enables Neighbor Discovery proxy. When ND proxy is enabled on a WLAN, the AP provides Neighbor Advertisement service for stations. When the AP receives a Neighbor solicitation request for a known host, it replies with a Neighbor Advertisement on behalf of the host. If the AP receives a request for an unknown host, it forwards the request. Note: This feature is available only on IPv6 and Dual zone and is enabled by default.Enable the option. Suppress NS Suppress Network Solicitation (NS) on a wireless medium when there is no Station entry available in the cache. This feature can be configured only when the ND Proxy option is enabled. Note: This feature is available only on IPv6 and Dual zone and is disabled by default.Enable the option. RA Proxy Enables Router Advertisement proxy. When RA proxy is enabled on a WLAN, the AP provides Router Advertisement service for wireless stations. When the AP receives a Router solicitation request on a WLAN, it replies with a Router Advertisement on behalf of the routers available on the network learned by the AP. If the router entries are not found in the cache, the AP forwards the request. Note: This feature is available only on IPv6 and Dual zone and is enabled by default.Enable the option. RS/RA Guard Prevents Router Solicitation (RS) from the wired side of the network to a wireless side. Also prevents Router Advertisement (RA) from a wireless side of the network to the wired side. This feature can be configured only when the RA Proxy option is enabled. Note: This feature is available only on IPv6 and Dual zone and is disabled by default.Enable the option. RA Throttling Regulates the multicast Router Advertisement (RA) from a wired medium to a wireless medium based on the configured Max Allowed RA and Interval. This feature can be configured only when RA Proxy is enabled. Note: This feature is available only on IPv6 and Dual zone and is disabled by default.MAX Clients Limits the number of clients that can associate with this WLAN per AP radio (default is 100). Every connection attempt after this maximum value will not be permitted to connect. Enter the number of clients allowed. 802.11d Adds additional regulatory information to AP beacons and probe responses. This compliance information provides country-specific guidance such as permitted channels and transmit power, to ensure that the devices operate within the legal boundaries of the country. 11d is helpful for many devices that cannot independently determine their operating country. Enable the option. 802.11k Neighbor Report Enhances roaming by providing a list of neighbor APs to the client device. APs build a neighbor AP list via background scanning, and when the client plans to roam, it will request this list from the AP. This list is then used to perform efficient scanning to find a roaming candidate. Enable the option. Anti-spoofing Prevents attacks on genuine clients from rogue clients that could lead to service disruption, data loss, and so on. This is achieved by matching the MAC address or IP address (IPv4) of the client with the address in the RUCKUS database. If the addresses do not match, the packet is dropped. These checks are also performed on ingress data packets to catch spoofed data packets early. Enable the option. By default, the following options are also enabled: - ARP request rate limit: Enter the packets to be reviewed for Address Resolution Protocol (ARP) attacks, per minute. In ARP attacks a rouge client sends messages to a genuine client to establish connection over the network.
- DHCP request rate limit: Enter the packets to be reviewed for DHCP pool exhaustion per minute. When rouge clients send a DHCP request with a spoofed address, an IP address from the DHCP pool is assigned to it. If this happens repeatedly, the IP addresses in the DHCP pool are exhausted, and genuine clients may miss out on obtaining the IP addresses.
Note: When you enable anti-spoofing, an ARP request and DHCP request rate limiter is automatically enabled with default values (in packets per minute, or ppm) which are applied per client; implying that each client connected to an interface enabled with anti-spoofing is allowed to send a maximum of "X" ARP/DHCP request ppm. The value "X" is configured on the interface that the client is connected.Note: The Force-DHCP option will be enabled by default when anti-spoofing is enabled, and it cannot be changed after anti-spoofing is enabled.Force DHCP Requires the clients to obtain a valid IP address from DHCP within the specified number of seconds. This prevents clients configured with a static IP address from connecting to the WLAN. Additionally, if a client performs Layer 3 roaming between different subnets, in some cases the client sticks to the former IP address. This mechanism optimizes the roaming experience by forcing clients to request a new IP address. Select the check box. DHCP Option 82 Enables an AP to encapsulate additional information (such as VLAN ID, AP name, SSID, and MAC address) into DHCP request packets before forwarding them to the DHCP server. The DHCP server uses this information to allocate an IP address to the client from a particular DHCP pool based on these parameters.
is enabled.DHCP Option 82 Format Enables an AP to encapsulate additional information into DHCP request packets before forwarding them to the DHCP server. The DHCP server uses this information to allocate an IP address to the client from a particular DHCP pool based on these parameters.
Enable the required format: DTIM Interval Indicates the frequency at which the Delivery Traffic Indication Message (DTIM) will be included in Beacon frames.
Enter the frequency number. Range: 1 through 255.
Directed MC/BC Threshold Defines the per-radio-client count at which an AP stops converting group-addressed data traffic to unicast. However, the Directed Threshold logic is only one part of the access points' multicast handling logic, which means there may be other factors that determine whether a frame is transmitted as unicast or multicast. APs support a feature called Directed Multicast (configurable only on AP CLI, enabled by default), which adds additional logic to the multicast flow. If Directed Multicast is disabled, the AP uses the Directed Threshold as the only criteria to determine whether to transmit a multicast packet as unicast. However, when Directed Multicast is enabled, the flow is changed. Directed Multicast is a feature that checks to see if a multicast packet is well-known or not. For well-known multicast packets, for example, Bonjour, uPNP, most IPv6 link- and node-local, and Spectralink, the AP still applies the Directed Threshold logic to determine conversion to unicast. For non well-known types, the AP monitors and maintains a database of client subscriptions using IGMP and MLD. If associated clients are subscribed to the multicast stream, then the AP always converts these packets to unicast, regardless of the Directed Threshold configuration. If there are no clients subscribed to the multicast stream, the AP drops these packets. It is important to be aware of this behavior when validating multicast operation in a deployment. Enter the client count number. Range: 0 through 128.
Client Tx/Rx Statistics Stops the controller from monitoring traffic statistics for unauthorized clients. Select the check box. User Session Timeout Indicates the duration after which idle clients will be disconnected. Note: Before getting disconnected the client can be either in an idle state or connected to the WLAN (SSID).Enter the duration. Range: 120 to 864000 seconds (10 days).
Default Value: 172800 seconds (2 days).
Note: This default value will remain effected only when the session timeout is not applied from the Radius server.Note: The user session timeout is displayed only for those WLANs in which 802.1X or MAC authentication is enabled.User Session Timeout Indicates the duration after which the client gets disconnected. Note: Before getting disconnected the client can be either in an idle state or connected to the WLAN.Enter the duration.
Range: 120 to 864000 seconds (10 days).
Default Value: 172800 seconds (2 days).
Note: This default value will remain effected only when the session timeout is not applied from the Radius server.WiFi 6/7 Controls how the Wi-6/7 AP radios operate to support clients of various capabilities on a specific WLAN.
By default, this feature enabled (ON), allowing Wi-Fi 6/7 client devices and legacy Wi-Fi 5 client devices to interoperate with the Wi-Fi 6/7 APs and utilize Wi-Fi 6/7 features (such as OFDMA, TWT, 6GHz operation, Preamble Puncturing, 320MHz bandwidth, and MLO) available on the WLAN.
When disabled (OFF), the Wi-Fi 6/7 APs are downgraded to support Wi-Fi 4/5 capabilities. This allows Wi-Fi 6/7 and legacy client devices to interoperate with the Wi-Fi 6/7 APs on the WLAN; however, the Wi-Fi 6/7 features are not available for use. Disabling this feature is recommended when client drivers are not up to date or if the client device drivers have bugs
Refer to Wi-Fi 6 or Wi-Fi 7 Support for further feature information and the Wi-Fi support matrix.Note: From releases 5.2.1 through 6.1.2, this option was labeled as Wi-Fi 6. Beginning with release 7.0.0, this option is renamed as Wi-Fi 6/7.Default setting: Enabled (toggled ON).
Click the toggle button to OFF to downgrade the Wi-Fi 6/7 AP functionality, allowing support for Wi-Fi 6/7 and legacy client devices.
7.0MLO (Multi Link Operation)Allows client devices to seamlessly associate across multiple bands and facilitates smooth switch between these links. The Multi-Link Operation (MLO) feature enhances peak throughput by efficiently sending packets from the same flow across multiple links. It also minimizes latency due to increased channel access opportunities through these multiple links. Furthermore, it enables swift and seamless traffic routing based on channel capacity for load balancing without the need for disassociation and reassociation. Default radio frequency: 2.4GHz + 5GHz
You can also select a combination of two radio frequency. For example, 2.4 GHz + 5 GHz, 2.4 GHz + 6 GHz or 5 GHz + 6 GHz.
OFDM Only Disconnects 802.11b devices from the WLAN and all devices are forced to use higher data rates for more efficient airtime usage. This setting only affects the 2.4-GHz radio. OFDM is used by 802.11a, g, n, and ac, but is not supported by 802.11b. Select the check box. BSS Min Rate Forces client devices to be both closer to the AP and to use higher, more efficient rates when you increase the BSS minimum rate above the default (all rates) setting. The BSS minimum rate is the lowest data rate supported on the WLAN. When OFDM-only is enabled, it takes higher priority than BSS minimum rate settings. Select the option. Mgmt Tx Rate Sets the transmit rate for management frame types such as beacon and probes. Select the value. 6.1 update6G BSS Min RateForces client devices to both be closer to the AP and to use higher, more efficient rates when you increase the BSS minimum rate above the default (all rates) setting. The BSS minimum rate is the lowest data rate supported on the WLAN. When OFDM-only is enabled, it takes higher priority than BSS minimum rate settings. Select one of the following option: 6.1 update6G Mgmt Tx RateSets the transmit rate for management frame types such as beacon and probes. Select one of the following option: Service Schedule Controls when the WLAN service is active. The purpose of this setting is to automatically enable or disable a WLAN based on a predetermined schedule. By default, the service is Always On. Always Off can be selected in order to create a WLAN and apply it, but prevent it from advertising until ready. The Specific setting allows a configurable schedule based on time of day and days of the week. Note: When a service schedule is created, it is saved by the controller and AP using the time zone of the browser. When it is enforced by the AP, the AP will enforce it according to the time zone of the browser when it was configured.Choose the option: Band Balancing Disables band balancing only for this WLAN, if you select the check box. Select the Disable band balancing for this WLAN service check box. Qos Map Set Reprioritizes downlink packets based on the configured mappings. When an AP receives a downlink packet, it checks the existing DSCP (Layer 3 QoS) marking, compares it to this map set, and then changes the user priority (Layer 2 QoS) values for transmission by the AP.
To configure this feature, select the User Priority (UP) from the table (0-7) and configure the DSCP (0-64) range that will be mapped to this UP.
Exceptions can also be added such that the original DSCP and UP tagging are preserved and honored by the AP.
To configure this feature, select the User Priority (UP) from the table (0-7) and configure the DSCP (0-64) range that will be mapped to this UP.
Select Enable QOS Map Set.Multicast Filter Drops the broadcast and multicast from the associated wireless clients. Click to enable this option. SSID Rate Limiting Enforces an aggregate rate limit for all users of the WLAN. The purpose of this feature is to prevent the combined throughput from all users of an SSID from exceeding this threshold. This feature is different from per-user rate limiting, which enforces the same rate limit for each individual device. Select the Uplink and Downlink check boxes and enter the limiting rates in mbps, respectively. Range: 1 through 1000 Mbps. Note: Rate limit supports maximum of 100 clients per WLAN per radio. After the threshold, the system displays client failure (203) error.Multicast Rate Limiting Multicast rate limit can be configured at WLAN level. The UplinkDownlink values are displayed only if the multicast rate limit is enabled.
The Downlink traffic is limited to 50% of the configured multicast rate limiting. For example, if multicast rate limiting downlink traffic is set to 6Mbps, only ~50%, .for example. 3.00Mbps to 4.00Mbps max per second traffic passes. This limit is only for downlink and shall not be affected by BSS Min Rate setting.
Note: SSID Rate Limit always take precedence, if, Mutlicast Rate Limit is also configured.Select the Uplink and Downlink check boxes and enter the limiting rates in Mbps, respectively. Range: 1 through 100 Mbps.
DNS Server Profile Allows the AP to inspect DHCP messages and overwrite the DNS servers with the DNS server configured in this profile. This allows for policy-based DNS application in which unique users/roles should use a different DNS server than others. Select a profile from the menu. Select Disable from the menu if you want to disable the DNS Server profile for the WLAN service. Click  to add a new profile or click
 to edit a profile.
DNS Spoofing Profile When an AP receives a DNS packet, all the fields in the packet are validated. Note: Only A/AAA server DNS query packets are considered. When same domain name is present in both DNS spoofing profile and walled garden table in the WISPr WLAN, then the AP DNS cache is updated with the IP address present in the DNS spoofing profile.If DNS spoofing and URL filtering with safe search is enabled, URL filtering (safe search) takes precedence for the Google, YouTube, and Bing domain names. If safe search is not enabled, DNS spoofing takes the precedence. If safe search is not enabled and URL filtering is enabled also DNS-Spoof takes the precedence.Select a profile from the menu. Select Disable from the menu if you want to disable the DNS Spoofing profile for the WLAN service. Click to add a new profile or click
to edit a profile Precedence Profile Defines the relative policy assignment priority for some specific settings. For example, if a WLAN is configured to use VLAN 10, and an AAA/role policy is configured for VLAN 20, and a device OS policy is configured for VLAN 30, and a user/device connects to the WLAN matching all of these policies, which VLAN should be assigned. The precedence policy determines which setting takes priority. Select the option. Click to add a new profile or click
to edit a profile. CALEA (This feature is supported only for SZ300 controllers.) Intercepts traffic, a requirement enforced on some networks by government agencies. To utilize CALEA, you must support a vSZ-D and configure the CALEA settings in the Services & Profiles > Tunnels & Ports menu. Select the check box. Note: If there are more than 40 DPs been approved, the controller limits the user to use the CALEA feature.Client Flow Data Logging Sends a log message with the source MAC address, destination MAC address, source IP address, destination IP address, source port, destination port, Layer 4 protocol, and AP MAC address of each packet session to the external syslog server. This function is provided by the AP syslog client (not the controller syslog client), which must be enabled at the zone level in order to support this client flow logging. Select the check box to log the client-flow data to the external syslog server. Then enable AP syslog functionality from the Zone settings. Airtime Decongestion Mitigates airtime congestion caused by management frames in high-density deployments. Select the check box. Join RSSI threshold Indicates the signal threshold that could connect to the Wi-Fi. If Airtime Decongestion is enabled, Join RSSI threshold is automatically disabled. Enter the Client RSSI threshold to allow joining. Range: -60 through -90 dBm. Transient Client Management Discourages transient clients from joining the network. Select enable Transient Client Management and set the following parameters: - Join wait time—Enter the wait time before a client can be permitted to join. Range: 1 through 60 secs.
- Join expire time—Enter the time during which a rejoin request is accepted without delay. Range: 1 through 300 secs.
- Join wait threshold—Enter the number of join attempts after which a client is permitted to join even before the join wait time expires.
Optimized Connectivity Experience (OCE) OCE enables probe response suppression and prevents devices with marginal connectivity from joining the network. Optimizes the connectivity experience for OCE-enabled APs and stations. Select Optimized Connectivity Experience (OCE) and set the following parameters: - Broadcast Probe Response Delay: Indicates the time delay to transmit probe response frames in milliseconds.
- RSSI-based Association Rejection Threshold: Indicates the minimum threshold value to connect to the network (in dBm). If the value entered is less than the minimum threshold value, then any RSSI-based association is rejected.
7.0QOS MirroringThis feature allows an AP to use a client's uplink Quality of Service (QoS) classification (Voice, Video, Best Effort or Background) to classify the client device's downlink packets in the mirrored (reverse direction) stream. The AP assigns the downlink packets to the same QoS category as the uplink packets. - Disabled - QoS mirroring is disabled for all the clients.
- Enabled via Protocol - QoS mirroring is enabled only for clients that send Mirrored Stream Classification Service (MSCS) requests. Legacy clients are not supported with QoS preference. This is the default setting.
- Enabled for All - Unilateral mirroring is applied for this option and QoS mirroring is enabled for all the clients.
- Click OK.
 to edit the VSA profile.
For SZ300 and vSZ-H, you can also migrate the WLAN configuration from a regular Domain to a Partner Domain. For more information, see https://support.ruckuswireless.com/answers/000006414.
- Select All: Select all WLANs in the list.
- Deselect All: Clear all WLAN selections from the list.
- Enable: Enable a WLAN from the list.
- Disable: Disable a WLAN from the list.
In the WLAN list, the Status column indicates whether the WLAN configuration is active or inactive. Though a WLAN is disabled by a time schedule, its configuration will remain active.