AP Admin Password and Recovery SSID
5.2.1 Beta Feature Update Topic
This topic
describes the mitigation of security enhancement of the AP admin password management.
Consider the following scenario while generating
the configuration: 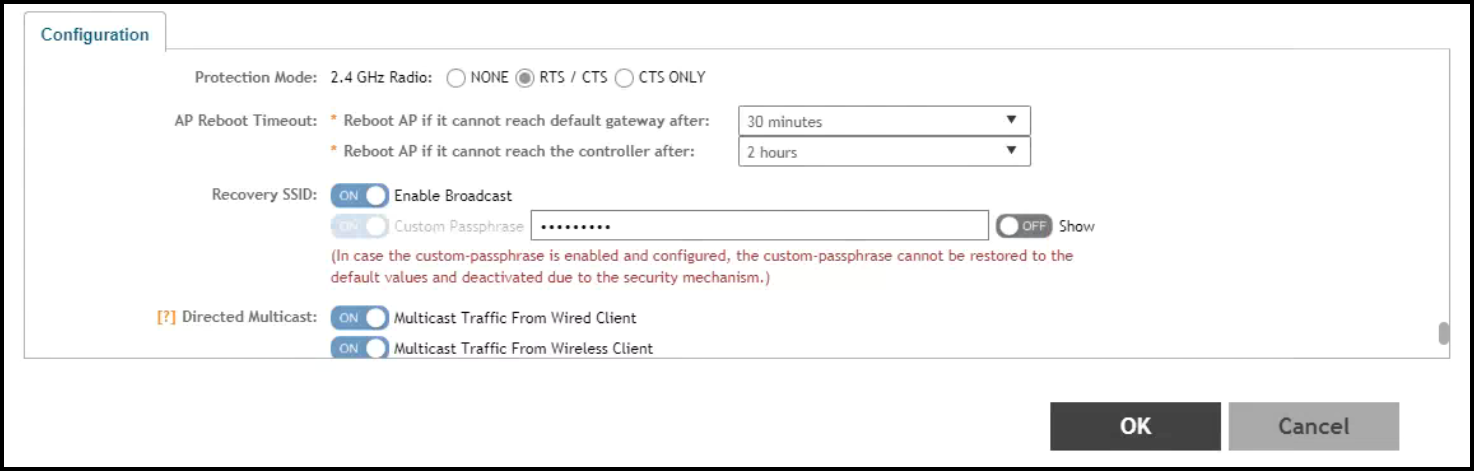
- Initial Installation: AP admin password need to be hashed in SHA-256 algorithm, stored in database and in configuration.
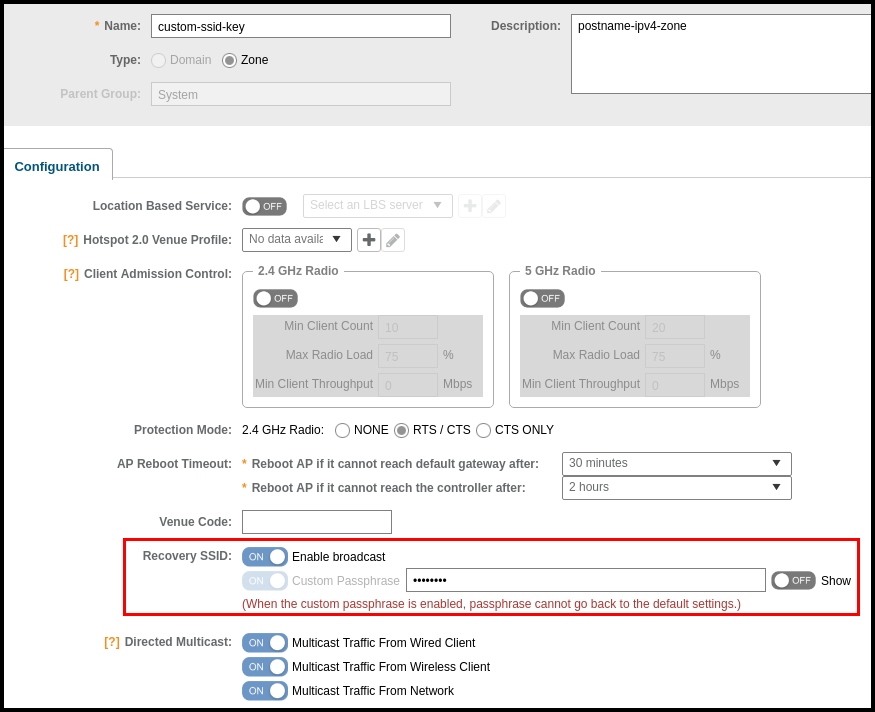
User can specify the Recovery SSID key in the Configuration Tab:
- The default of this Recovery SSID feature is enabled. The default passphrase is AP admin password in clear text format.
- If the user wants to change it, input the passphrase while enabling.
- The validation of passphrase, apply the same rule of WLAN passphrase.
- The passphrase can be clear text stored in the database and delivered to the AP in the GPB configuration by the way of secure channel (SSH channel).
The recovery SSID passphrase(key) will be delivered in GPB configuration as below:
- ccm_zone.proto
- message CcmCommon {
- /** recovery ssid
- */
- optional bool recovery_ssid_enabled = 26
- optional string recovery_ssid_psk_key = 27
- optional int32 server_loss_timeout = 28
When the Custom passphrase is disabled, the Custom passphrase filed is empty.
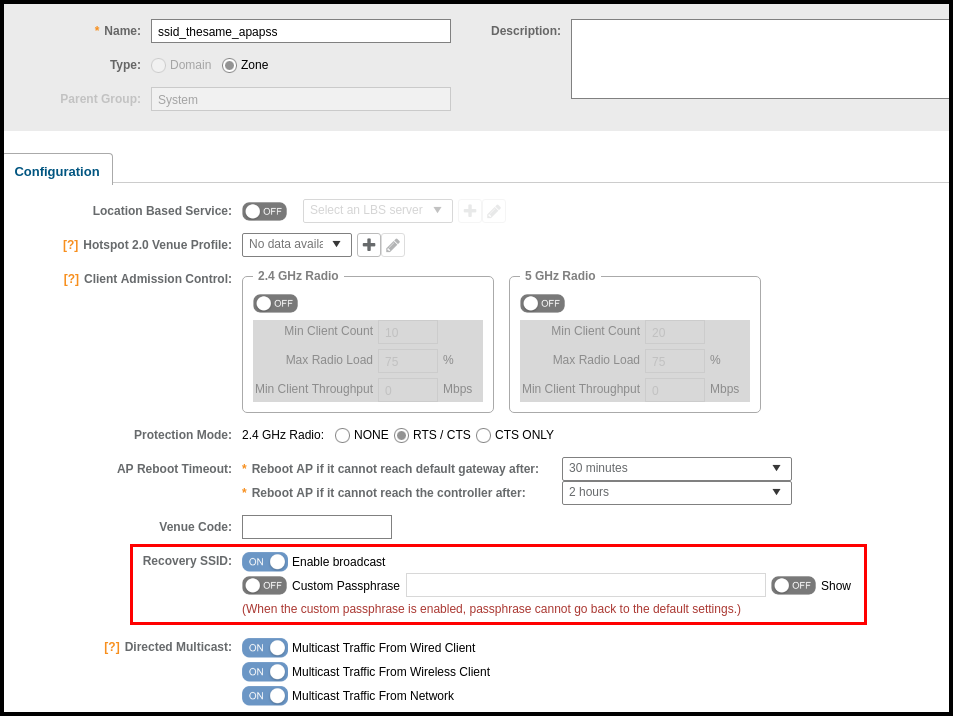
When the Custom passphrase is enabled, the Custom passphrase field is mandatory and should enter a passphrase.