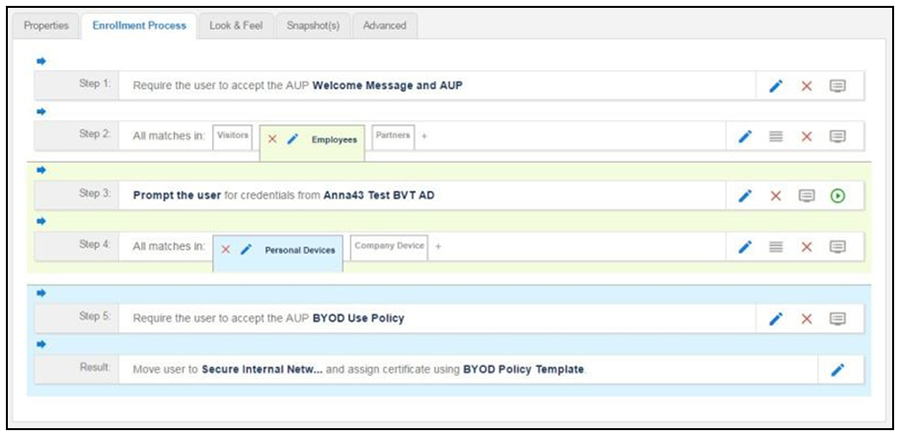
Employee With Personal Device Authenticated to AD Group
This is an example workflow for an employee using a personal device to access the secure network. The employee authenticates to an Active Directory group, and the device type split is managed with a filter, which displays the Personal Device workflow branch only if they are a member of a specified AD group. The user is asked to acknowledge a BYOD use policy before being moved to a secure internal network.