Employee With IT Asset Authenticated to AD Group
This is an example workflow for an employee using an IT-assigned device to access the secure network. The employee is authenticated to an Active Directory group, and the device type split is managed with a filter, which moves the user to the Company Device workflow branch if they are a member of a specified AD group. They are prompted to enter a previously sent/assigned voucher and moved to a secure internal network.
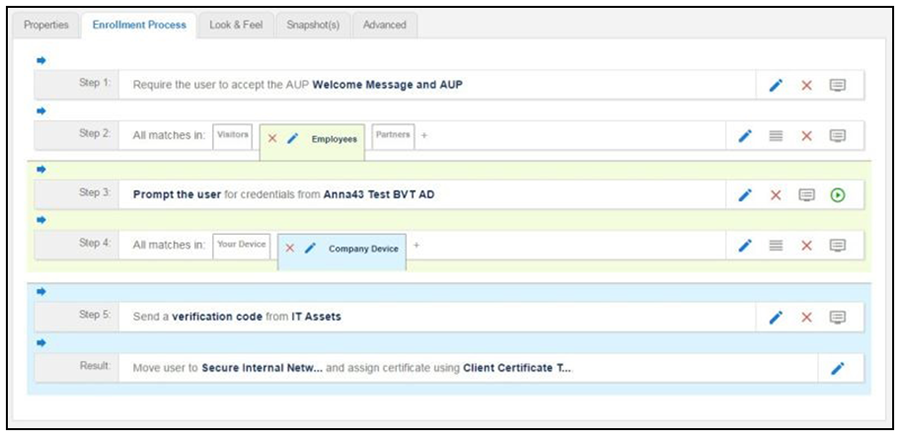
Your workflow does not have to be in the same order as the example. For example, you can move the authentication to LDAP step to immediately after the AUP step and then have the split for different workflow branches be immediately following. If you set up a filter on the LDAP group name, users can be moved to the appropriate workflow branch.