Configuring an IPv6 ACL
Complete the following steps to configure an IPv6 ACL.
- Select . All the configured ACLs are listed in the main pane. You can perform the following actions:
- Add an ACL: Continue to step 2 to add new ACL.
- Edit an ACL: Select
 to display the Edit Access
List dialog box. You can delete the existing rule or add new
rules. Make the necessary changes and select Apply to
apply the changes.
- Delete an ACL: Select
 to display the Delete Access
List dialog box. Select Apply to
delete the ACL.
- Select
 to
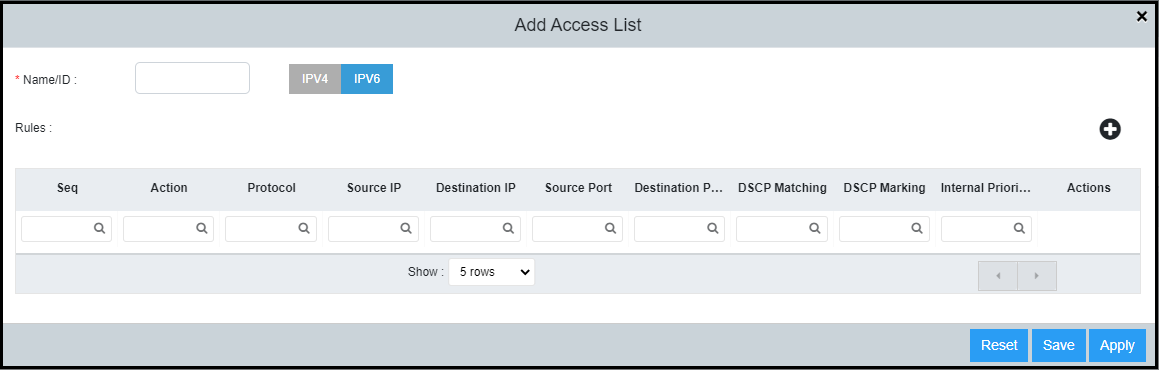
display the Add Access List dialog box.
- Select the IPv6 tab and enter a unique ACL name in the Name/ID field.
- For Rules, select to
add ACL rules with the following parameters:
- Seq: Assign a sequence number to the ACL rule.
- Action: Select permit or deny from the list to filter the traffic according to the rules.
- Protocol: Select the protocol type (IPv6, TCP or UDP) to be specified as a match for filtering.
- Source IP: Enter the source IP address for which you want to filter the subnet.
- Destination IP: Enter the destination IP address for which you want to filter the subnet.
- Source Port: Specify the source port of the specified protocol.
- Destination Port: Specify the destination port of the specified protocol.
- DSCP Matching: Allows filtering by DSCP value.
- DSCP Marking: Assign the DSCP value for the packet.
- Internal Priority: Assign the internal queuing priority (traffic class) for the packet.
- Select Apply to create the IPv6 ACL.