General Options
General Options for Zones, AP Groups, and Individual APs
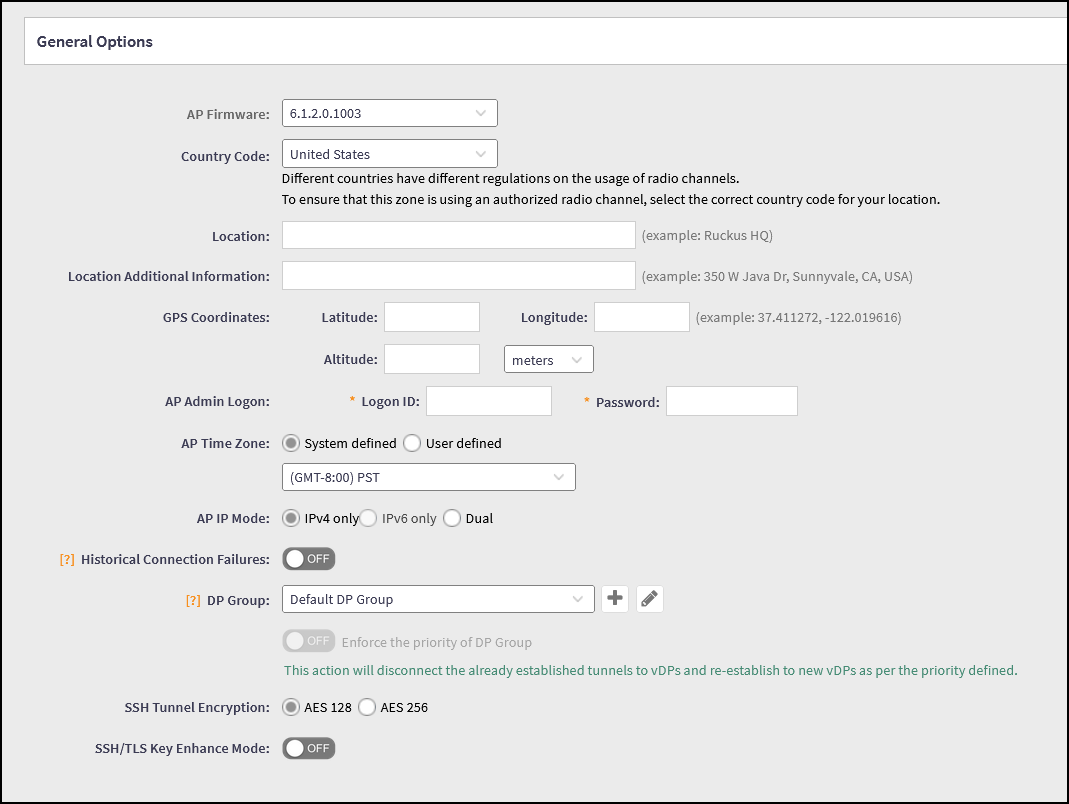
AP Name/Description: Only available at the individual AP level.
AP Firmware: The AP firmware is selected during the initial zone creation. After the zone is created, it can be modified only through the AP firmware upgrade procedures. For more information, refer to AP Firmware Version.
Country Code: Using the correct country code is essential to ensure that APs only utilize authorized radio channels for the region. If you modify this option, the APs in the zone must reboot for the configuration changes to take effect.
Location, Location Additional Information, and GPS Coordinates: The Location field provides a free-form field to specify any generic location if needed. The additional information field can be used to provide additional details about the location. Optionally, you can document the GPS coordinates for the zone, Group, or individual AP.
User Location Information (ULI): In some countries, Wi-Fi service providers are required to support lawful interception, which means incorporating location features into their products. From a solution perspective, this involves including ULI and International Mobile Equipment Identity (IMEI) Information Elements (IEs) in the Packet Data Protocol (PDP) context creation request. Local Area Code (LAC) and Cell Identity (CI) configurations are managed per-AP through the AP Configuration page. During AP-to-AP roaming scenarios, the Update PDP Request should also carry user location information related to the roamed-to AP.
AP Admin Logon: The Logon ID and Password credentials are used to access the command line interface (CLI) of the APs when connecting to them using an SSH client/terminal like PuTTY. If you ever lose this password, you can simply reset it by entering a new password in the Password field. Temporarily overriding this configuration at the individual AP level is useful when access to the CLI of the AP is required but the password is unknown. Modifying these fields does not require an AP reboot or cause service interruptions.
The password must comply with the following requirements:
- Blank Spaces: The password must not contain any blank spaces.
- Character Complexity: The password must be a minimum of 8 characters in length and include at least one lowercase letter, one uppercase letter, one number, and one special character.
- Special Characters Allowed: You can use the following special characters: ~!@#$%^&*()-=_+[]{}|;':",./<>?
AP Time Zone: You can select a system-defined well-known time zone option from the drop-down menu or create a custom time zone profile with a user-defined name, time, and daylight-saving options.
AP IP Mode: Configure the AP IP mode, choosing between IPv4 only, IPv6 only, or Dual. Once the zone has been created, this configuration cannot be modified.
AP IPv4/IPv6 Settings: This option is only available at the individual AP level. Select one of the following options:
- Static: Manually configure an IP address for the access point. IP Address, Network Mask, and Gateway are mandatory fields; Primary DNS and Secondary DNS are optional fields.
- Dynamic/Auto Configuration: Select Dynamic for the AP to use DHCP to obtain an IP address in IPv4 or select Auto Configuration for IPv6.
- Keep the AP’s Settings : Selecting this option honors the current configuration of the access point, whether it has been configured manually or dynamically. This configuration is recommended during maintenance or AP migration to a different controller, as it ensures the APs keep their current configuration.
Historical Connection Failures: Allows the APs in the zone to report client connection failures so that you can view past connection problems from the Troubleshooting menu.
DP Group: Specifies the Data Plane group for the zone.
SSH Tunnel Encryption: Specifies the encryption length utilized for the SSH tunnel in AP-to-controller communications. You can select one of these: AES 128 or AES 256.
- AES 256 offers a higher level of security due to its longer key length.
- On the other hand, AES 128 is faster and more efficient, which might be beneficial if performance and speed are critical for your application.
SSH/TLS Key Enhance Mode: Enable SSH/TLS Key Enhance Mode to configure ECDSA 3K certificates. By default, this option is disabled. This configuration is available only with new installation and upgraded versions of the access points. After enabling the SSH/TLS Key Enhance Mode option, navigate to to map the server's ECDSA 3K certificates.