Configuring the Advanced Security Options for ITSAR Compliance
The ITSAR security enhancements configuration determines how a Zone controls two security functions, restricting AP processing of non‑essential ICMP messages and enabling AP boot‑time integrity and cryptographic self‑tests. These settings allow you to strengthen AP security posture and align with ITSAR compliance requirements.
To enable ITSAR‑aligned ICMP restrictions and AP boot‑time self‑tests for all APs in a Zone, complete the following steps:
- From the main menu, select .
- From the list, select the Zone
for which you want to apply these features and click
 .
- Scroll to Advanced Security
Options and toggle ON the following
options:
- Self Test & Reporting - During boot, APs perform firmware integrity checks and cryptographic Known‑Answer Tests (KATs). They report the results to SmartZone using informational event 99012, which indicates execution status and reason codes.
- Restrict ICMP Processing - APs drop ICMPv4 Timestamp Request and Reply messages along with other non‑essential ICMP types, while continuing to process mandatory ICMPv6 control traffic such as Neighbor Discovery Protocol (NDP) and Multicast Listener Discovery (MLD).
Note: The SNMPv3 agent supports SHA256 or above for authentication and AES128 or above for privacy. By default, SHA256 is used as the authentication protocol for the SNMPv3 agent. To configure SNMPv3 agent, refer to the Advanced Security Options for ITSAR Compliance. - Click OK.
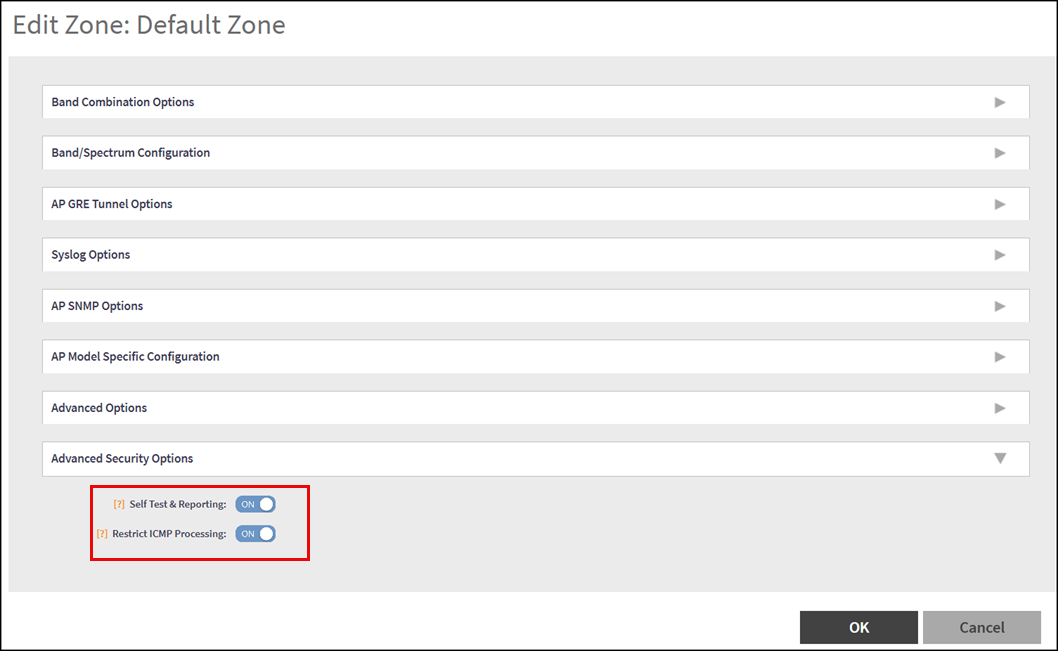
On boot, APs run firmware integrity checks and cryptographic Known‑Answer Tests (KATs), reporting results to SmartZone through Event 99012. APs also drop ICMPv4 Timestamp Request/Reply and other non‑essential ICMP types while preserving required ICMPv6 traffic such as NDP, MLD, and mandatory error messages.