Configuring Port Settings for a Switch
Port settings allow you to configure the behavior of individual ports on a switch,
stack, or switch group. These settings are essential for managing network performance
and
security.
By configuring port settings, you can apply Access Control Lists (ACLs) to invoke Quality of Service (QoS) settings, prioritizing specific types of traffic, such as Voice over IP (VoIP) and VIDEO VLAN traffic.
- Note:
- Port settings for QoS can only be configured for switches that are executing firmware version 08.0.95 and above.
- When SmartZone is configured in 'IPv6 only' mode, it removes support for ACL.
- Port-level DHCP v4/v6 settings and Point-to-Point Protocol over Ethernet Intermediate Agent (PPPoE IA) server port configuration are supported only on the ICX8200 series.
- SmartZone supports configuring PPPoE IA on IPv4 only, dual mode, and IPv6 only mode.
- On the menu, click to display the Switches window.
- On the Switches page, select the switch you want to view.
- Click the Ports tab.
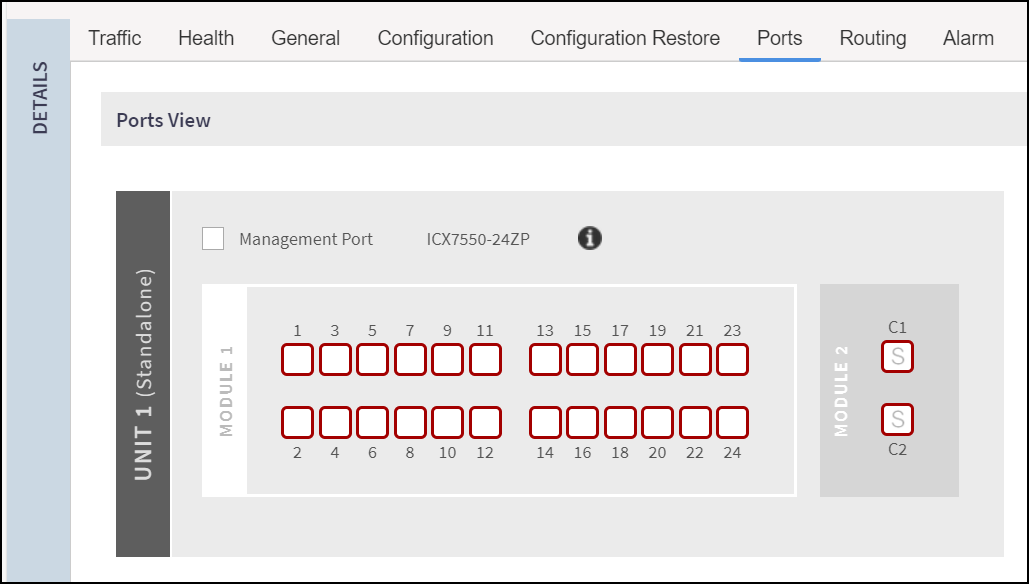
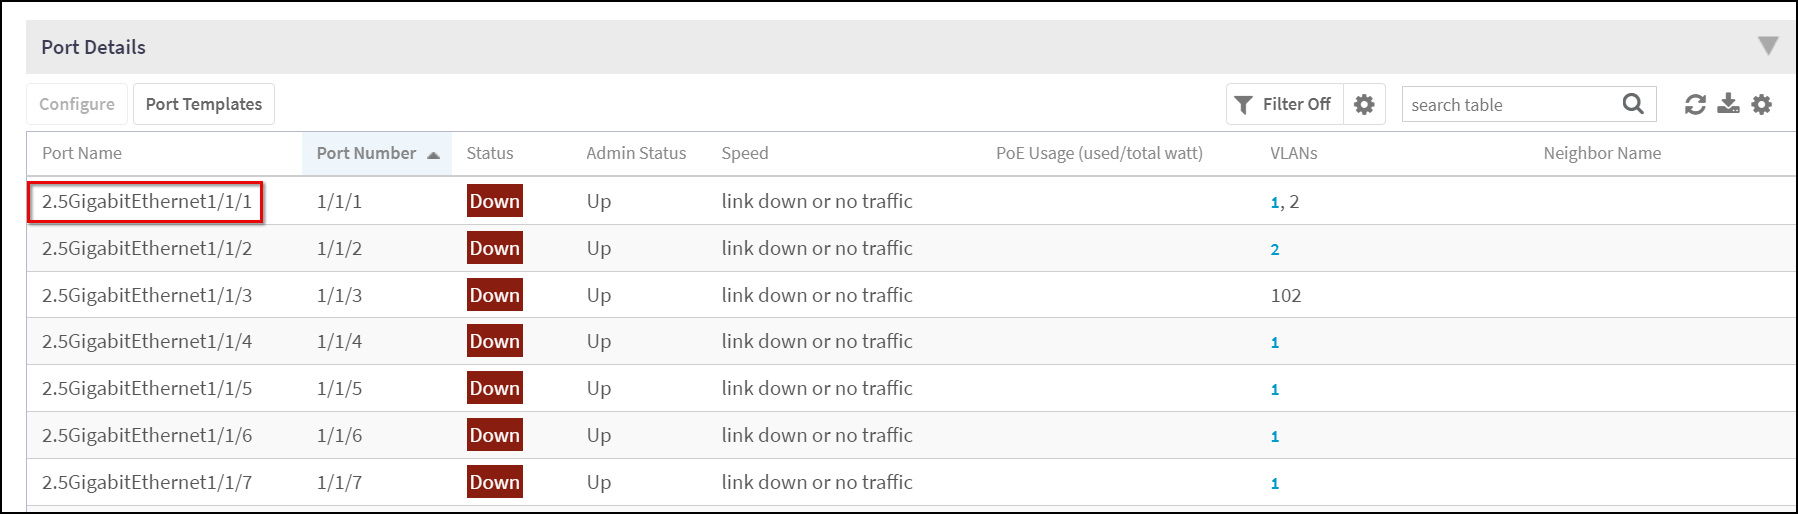
- To configure the Port Settings, either double-click a port in the Ports View section OR double click a port name under the Port Details section.
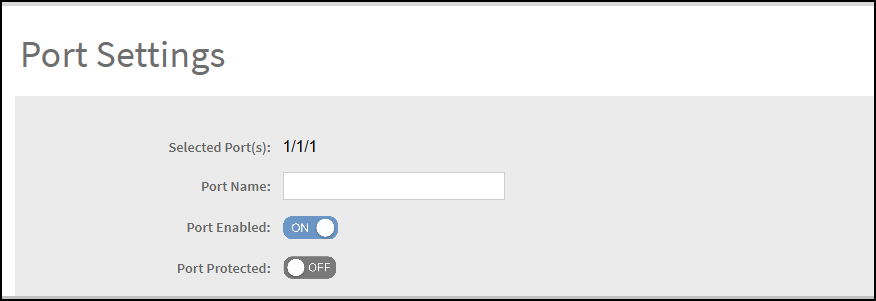
- In the Port
Settings page, complete the following configurations.
- Port Name: Enter the port name.
- Port Enabled: Click to enable the port.
- Port
Protected: Click to enable the protected port.Note: Port Protected field is displayed only for the switches using SmartZone 5.2.1 and above.
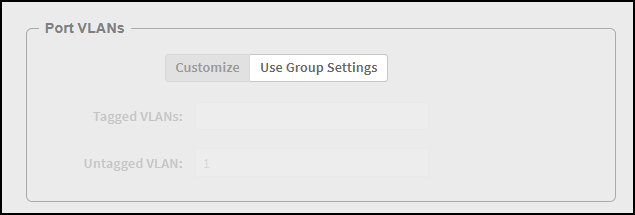
- Port VLANs: If you configure VLAN on both group model configuration and port settings, port level changes takes precedence.
- Customize: Click customize to identify the ports that need to stay customized.
- Use Group Settings: Click the user group settings to rebind the identified ports back to the group level.
- Tagged VLANs: Enter the tagged VLAN ID or VLAN ID range.
- Untagged VLAN: Enter an untagged VLAN ID.
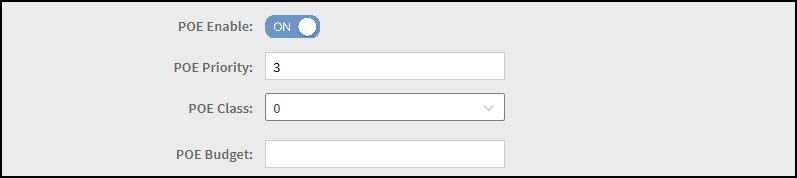
- POE Enable: Click the POE Enable toggle button to enable (ON).
- POE Class: Select the PoE class. You can configure the PoE budget on ports by setting the PoE class to 0 through 4.
- POE Priority: Enter the PoE priority.
- POE Budget: Allows you to manually set the PoE power limit.
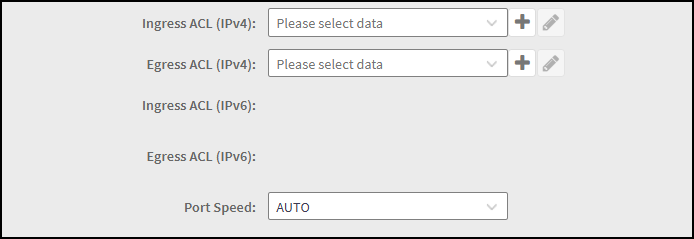
- Ingress ACL: Select the Ingress ACL from the list.
- Egress ACL: Select the Egress ACL from the list.
- Port Speed: Select the required Port Speed from the list.
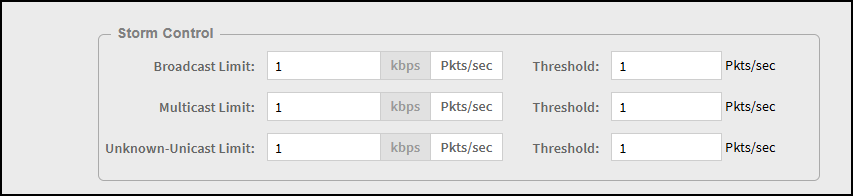
- Broadcast
Limit: Limits the rate of broadcast frames accepted on
the interface to prevent excessive VLAN flooding. Broadcast frames
exceeding the configured limit are dropped at ingress and are not
replicated to other VLAN member ports. Configure the threshold to define
how many dropped broadcast packets must occur before a configured
corrective action (port shutdown) is triggered. Configure the following values:
- Limit: Accepted values range from 1 through 8,388,607 packets per second (pps), or from 1 through 1,000,000 kbps when the port speed is set to Auto or Optic; for fixed port speeds, accepted values are from 1 kbps through the configured port speed.
- Threshold: Accepted values range from 1
through 8,388,607 packets per second (pps) when the limit is
configured in pps, or from 1 through 1,048,576 kbps when the
limit is configured in kbps.
Note: Configure conservative limits on access ports, and use thresholds only to automate mitigation of sustained violations.
- Multicast
Limit: Limits the rate of multicast frames accepted on
the interface to control VLAN replication and bandwidth consumption.
Multicast frames exceeding the configured limit are dropped at ingress
and are not forwarded to other VLAN member ports. Configure the
threshold to define how many dropped multicast packets must occur before
a configured corrective action (port shutdown) is triggered.Configure the following values:
- Limit: Accepted values range from 1 through 8,388,607 packets per second (pps), or from 1 through 1,000,000 kbps when the port speed is set to Auto or Optic; for fixed port speeds, accepted values are from 1 kbps through the configured port speed.
- Threshold: Accepted values range from 1
through 8,388,607 packets per second (pps) when the limit is
configured in pps, or from 1 through 1,048,576 kbps when the
limit is configured in kbps.
Note: Configure conservative limits on access ports, and use thresholds only to automate mitigation of sustained violations.
- Unknown -Unicast
Limit: Limits the rate of unknown unicast frames
accepted on the interface to prevent excessive VLAN flooding during MAC
learning. Unknown unicast frames exceeding the configured limit are
dropped at ingress and are not flooded to other VLAN member ports.
Configure the threshold to define how many dropped unknown-unicast
packets must occur before a configured corrective action (port shutdown)
is triggered.Configure the following:
- Limit: Accepted values range from 1 through 8,388,607 packets per second (pps), or from 1 through 1,000,000 kbps when the port speed is set to Auto or Optic; for fixed port speeds, accepted values are from 1 kbps through the configured port speed.
- Threshold: Accepted values range from 1 through
8,388,607 packets per second (pps) when the limit is configured
in pps, or from 1 through 1,048,576 kbps when the limit is
configured in kbps.
Note: Configure conservative limits on access ports, and use thresholds only to automate mitigation of sustained violations.
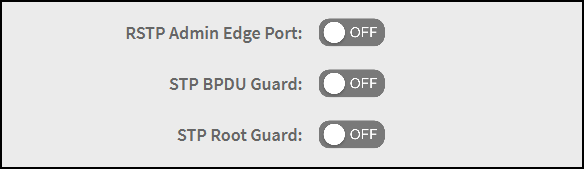
- RSTP Admin Edge Port: Click to enable the RSTP Admin Edge Port.
- STP BPDU Guard: Click the STP BPDU Guard toggle button to enable (ON).
- STP Root Guard: Click the STP Root Guard toggle button to enable (ON).
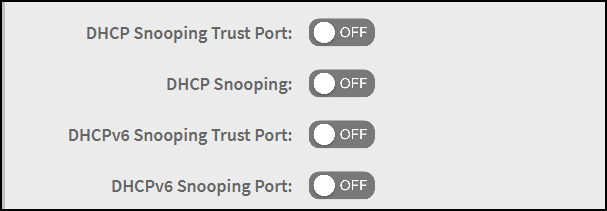
- VLAN DHCP Snooping Trust Port: Click the toggle button to enable (ON) the VLAN DHCP Snooping on the port. The switch port will trust the received DHCP responses as legit and will forward them to the corresponding destination.
- DHCPv6 Snooping Trust Port: Designates the port as trusted for DHCPv6 server traffic. When enabled, the port forwards DHCPv6 messages from legitimate servers and blocks rogue DHCPv6 server responses on untrusted ports.
- DHCP Snooping
Port: Select Enable if
you want the port to participate in DHCP Snooping. The switch port, when
enabled with DHCP snooping, will disregard unauthorized DHCP responses
and maintain a DHCP snooping binding table. This table records DHCP
operations on the port to validate subsequent DHCP messages, ensuring
they come from legitimate sources and enhancing network security. When
enabled, enter a descriptive string (from 1 to 63 characters) in the
Circuit
ID field to identify the port or location, and in the
Remote
ID field to identify the relay agent or forwarding
device.
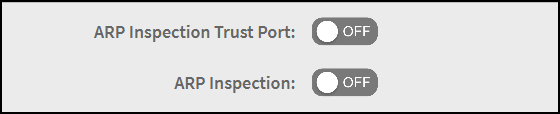
- ARP Inspection Trust Port: Click the toggle button to enable (ON) the ARP Inspection Trust Port. Configure this option on uplink or other trusted ports to allow legitimate ARP traffic while preventing ARP spoofing on untrusted interfaces.
- ARP
Inspection: Click the toggle button to enable (ON) the ARP
Inspection.
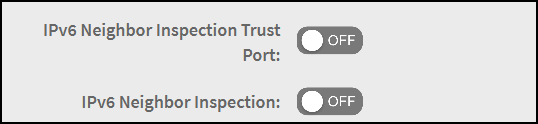
- IPv6 Neighbor Inspection Trust : Click the toggle button to enable (ON) the Neighbor Discover Inspection (IPv6) Trust Port. This trust setting is used on ports that connect to known, trusted devices to ensure the proper forwarding of Neighbor Discovery (ND) messages while still enforcing inspection on untrusted ports.
- Neighbor Discover
Inspection (IPv6): Click the toggle button to enable (ON) the Neighbor
Discover Inspection (IPv6).
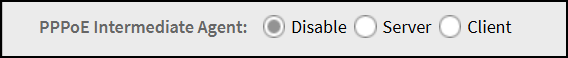
- PPPoE Intermediate
Agent: The Point-to-Point Protocol over Ethernet (PPPoE)
is a network protocol that encapsulates Point-to-Point Protocol (PPP)
frames inside Ethernet frames. When enabled, the PPPoE Intermediate
Agent facilitates the insertion of PPPoE tags and manages PPPoE sessions
between clients and servers. The PPPoE Intermediate Agent setting allows
you to configure the PPPoE port role as either a Server or a Client
interface.
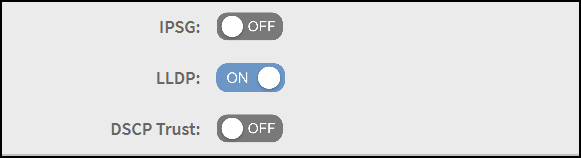
- IPSG: Click IPSG toggle button to enable (ON).
- ILLDP: Click ILLDP toggle button to enable (ON).
- DSCP Trust: Click DSCP toggle button to enable (ON). With this setting, the switch port will honor the DSCP markings of the received traffic and prioritize it accordingly.
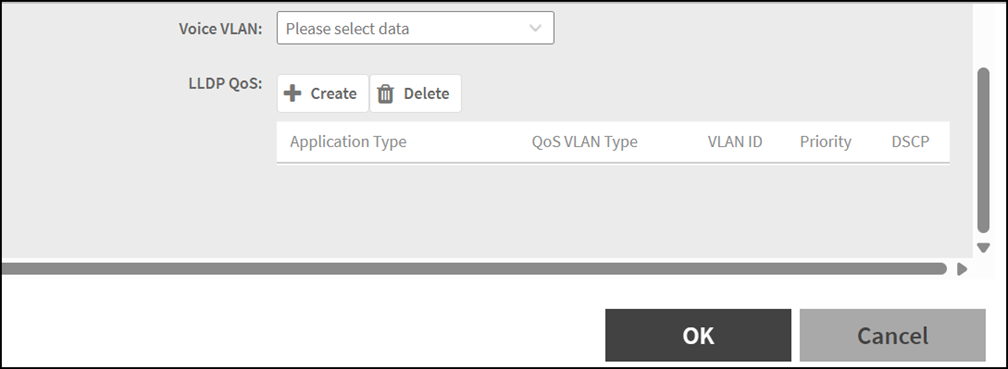
- Voice VLAN: Select the VLAN (tagged or untagged).
- LLDP QoS: Click to enable LLDP-MED settings.
- Application type: Enter one of the application types : Guest_Voice, Guest_Voice_Signaling, Softphone_Voice, Streaming_Video, Video_Conferencing, Video_Signaling, Voice, and Voice_Signaling.
- VLAN type: The VLAN type can be priority-tagged, tagged, or untagged.
- VLAN ID: Enter the VLAN ID of the VLAN type.
- Priority: Enter the priority for the QoS setting.
- DSCP: Enter the DSCP value for the LLDP setting.
- Click OK.