Creating Switch Level Configuration
- On the menu, click to display the Switches window.
- Select an existing switch from the switches list and in the Details area, click the Configuration tab.
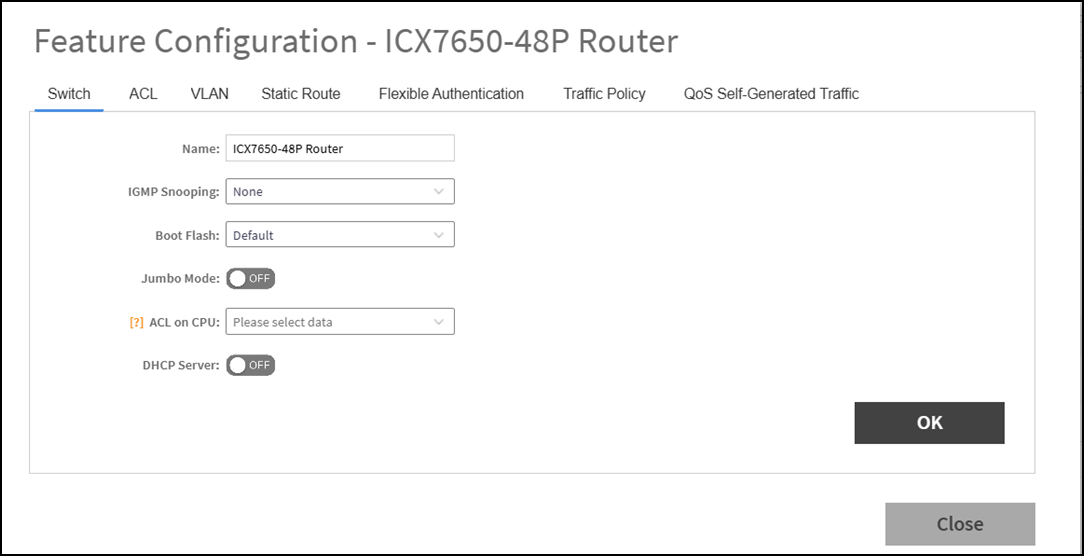
- In the Configuration section, click Configure to display the Feature Configuration dialog box.
- Click the Switch tab, and
configure the following.
- Name: Enter the name of the switch.
- IGMP Snooping: Select the profile from the list.
- Boot Flash: Select the Default, Primary or Secondary option to configure boot preference.
- Jumbo Mode: Enable this option to permit jumbo frames to traverse the switch. Enabling jumbo mode will reboot the switch after the configuration is saved.
- ACL on CPU: From the drop-down list, select an ACL profile with the traffic policy configuration.
- DHCP
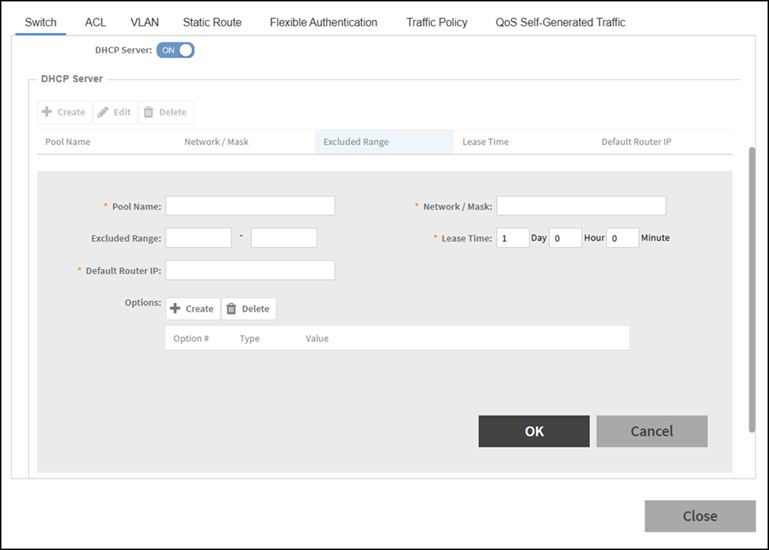
Server: Enable this option and click Create to
configure the following DHCP server settings: Note: You must disable the DHCP client before enabling the DHCP server.
- Pool Name: Enter a name.
- Network/Mask: Enter the network address and network mask.
- Excluded Range: Enter the network range to be excluded.
- Lease Time: Enter the lease time duration.
- Default Router IP: Enter the default router IP address.
- Options: Click Create and enter the option number, select a type, and enter a value for the option.
- Click OK to apply the changes.
- Click Cancel to discard the changes.
- Click OK to apply the changes and save the switch configuration settings.
- Configure the switch ACL settings, refer to Configure the ACL settings in the Model-Based Configurations.
- Configure the switch VLAN settings.Note: You can create a new VLAN and set it as the default VLAN.
- Click the VLAN tab.
- Click the Configure button to display the VLANsettings.
- Complete the following fields:
- VLAN#: Enter a unique number for VLAN.
- VLAN Name: Enter a VLAN name.
- Management VLAN: You can configure the
Management VLAN for the switches or switch groups in the
following ways:
- Enable Management VLAN, and click OK.
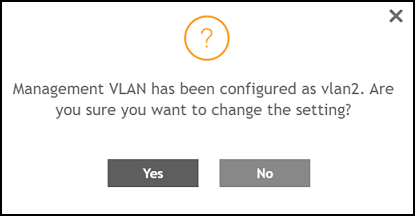
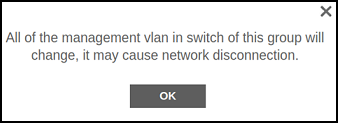
If the VLAN is configured as the default VLAN, enable or disable Management VLAN on the default VLAN, and click OK. A dialogue box is displayed, as shown in the following.
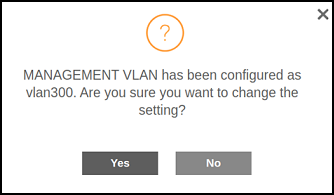
If Management VLAN is enabled on a VLAN and you try to enable it on another VLAN, the controller displays a dialogue box showing the VLAN ID that has been configured as the Management VLAN. If you click Yes, the controller overwrites the settings.
- For a switch group, the controller displays a dialogue box, as shown in the following figure.
- IPv4
DHCP Snooping: Monitors and filters DHCP
traffic on a network switch to prevent unauthorized or
rogue DHCP servers from distributing IP addresses. If
you enable IPv4 DHCP Snooping, you must provide the
trusted port for this option in the DHCP
Snooping Trust Port field.
Attention: To complete this change, the ICX will reboot after the controller syncs the configuration updates.
- ARP
Inspection: Validates ARP packets to
prevent spoofing and MITM attacks by ensuring correct
MAC-to-IP bindings. You must provide the trusted port
for this option in the ARP
Inspection Trust Port field.
Attention: To complete this change, the ICX will reboot after the controller syncs the configuration updates.
- IGMP Snooping: Ensures that multicast traffic is only forwarded to devices that have requested it, thereby preventing unnecessary traffic and conserving bandwidth. Select None, Active, or Passive from the list. Ensures that multicast traffic is only forwarded to devices that have requested it, thereby preventing unnecessary traffic and conserving bandwidth. If you select Active or Passive, you are required to select the Multicast Version as well.
- Spanning Tree: Select None, STP (802.1d), or RSTP (802.1w) from the list. If you select STP or RSTP, you are required to select the Spanning Tree Priority as well. For detailed instructions about configuring Spanning-Tree, refer to the FastIron Layer 2 Guide.
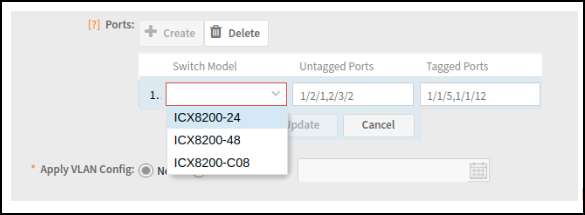
- Ports: Click Create to assign the ports to the switch model. Enter values for Switch Model, Untagged Ports, and Tagged Ports.
- Apply VLAN Config: Select Now or Schedule Later. If you choose to schedule the configuration deployment for later, provide the time and date.
- Click OK to add the newly created VLAN configuration to the VLAN tab.
- Enable Management VLAN, and click OK.
- Configure the switch Static Route settings, refer to Configure the Static Route settings in the Model-Based Configurations.
- Click the Flexible Authentication tab.Configure the following parameters.
- Click the Flexible Authentication toggle button to enable (ON) to configure in the switch the authentication default VLAN and the guest VLAN.
- Auth Default VLAN: Enter a valid VLAN ID. This VLAN is used as the default VLAN for unauthenticated devices connected to a port. Until a device successfully authenticates (via 802.1X, MAC authentication and so on), it will be placed in this VLAN. It ensures that unauthenticated traffic is either isolated or routed appropriately.
- Guest VLAN: Enter a VLAN ID designated for guest VLAN. The wired clients are placed in this VLAN according to the attributes received from the authentication server.
- Click OK to save and apply the configuration.
- Click Close to exit the configuration screen without applying changes.
- Click the Traffic Policy tab. Note: Before applying traffic policy, ensure the following requirements, considerations and limitations are assessed.
- RUCKUS ICX devices must be running FastIron firmware version 10.0.20c or later.
- SmartZone must be running version 7.1.1 or later.
- IPv6-only SmartZone Controllers do not support configuring traffic policy.
- The maximum number of traffic policies for each switch is 1023.
- If a traffic policy is applied to any ACL rule, the Name field cannot be updated.
- The ACL rule cannot be configured with both internalPriority and a traffic policy at the same time.
- When the traffic policy configuration is saved in the controller, it sends the necessary commands to the ICX switch to apply traffic policy parameters to the specified traffic.
You will see three buttons - Create , Configure and Delete - to create, modify and delete the traffic policies, respectively. When a traffic policy is created, modified, or deleted in the controller, the corresponding CLI commands are sent to the target ICX switch for execution.- Click Create to add a new traffic policy.Configure the following parameters.
- Name: Enter a name for the traffic policy.The traffic policy name must not exceed eight characters.
- Type:
Select Fix or Adaptive.
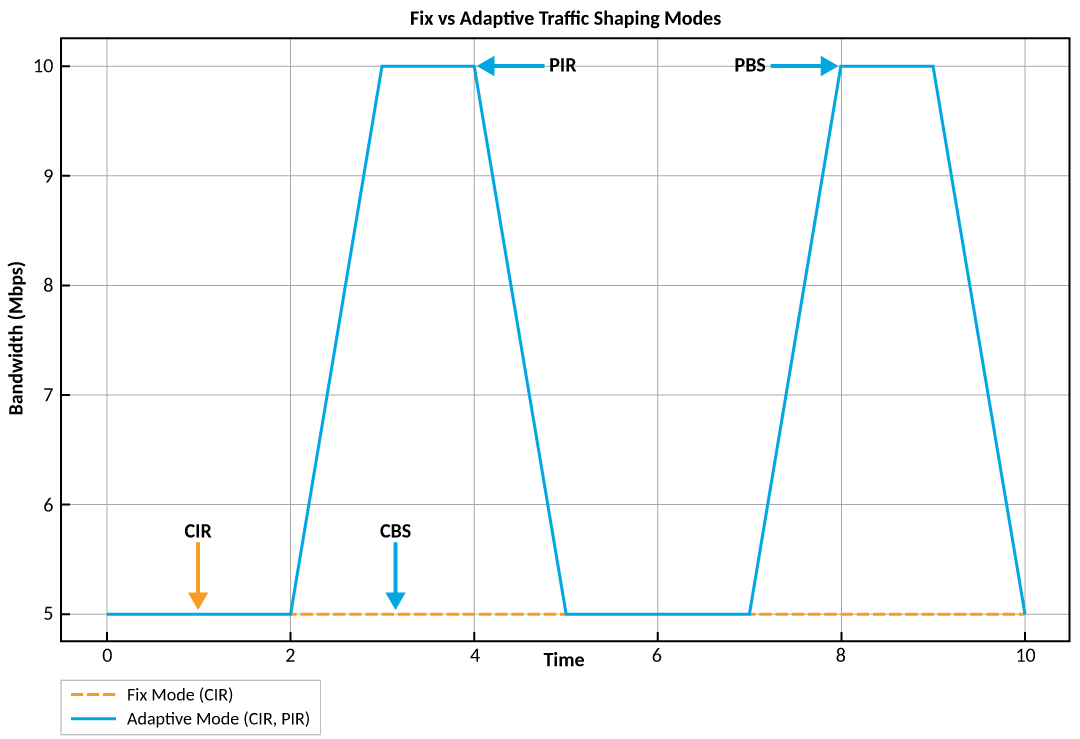
The Fix type is a static traffic shaping option. It enforces a constant, guaranteed bandwidth by allowing you to configure only one parameter. This ensures that traffic is shaped to a consistent rate, regardless of network conditions. This mode is ideal for scenarios where traffic must be tightly controlled and predictable, such as real-time applications like VoIP or video conferencing.
The Adaptive type allows traffic to temporarily exceed the committed rate when bandwidth is available, which is best used when you want to maximize bandwidth utilization while still maintaining control over traffic behavior. It’s particularly useful for applications like file transfers, web browsing and so on.Configure the following parameters for Adaptive type.
- Committed Information Rate (CIR): This is the guaranteed minimum bandwidth that the network will always try to provide to the traffic flow. It's a fixed rate, meaning traffic is shaped to this rate regardless of network conditions. The valid ranges are:
- Committed Burst Size (CBS): The maximum amount of data that can be sent in a burst at the CIR. It allows short bursts above the CIR without being dropped. The valid ranges are:
- Peak Information Rate (PIR): The maximum bandwidth allowed during peak usage. Traffic can temporarily exceed the CIR up to this rate if bandwidth is available. The valid ranges are:
- Peak Information Rate (PIR): The maximum burst size allowed at the PIR. It defines how much data can be sent in a short burst at the peak rate. The valid ranges are:
The following table shows a comparison between the Fix and Adaptive type, best use case scenario according to your network needs,Type Comparison and Recommended Mode
Scenario Recommended Mode Reason Real-time apps (VoIP, video) Fix Ensures consistent delivery with minimal jitter. Web browsing, file transfers Adaptive Allows burst for faster performance when bandwidth is available. Mixed traffic environment Adaptive with tuned CIR/PIR Balances guaranteed service with flexibility. Bandwidth-constrained links Fix Prevents overuse and ensures fairness. To ensure efficient bandwidth utilization and maintain application performance, the following considerations are recommended.
- Set CIR based on minimum required bandwidth for the application.
- Use PIR to allow flexibility — set it higher than CIR if you expect occasional bursts.
- Tune CBS and PBS to control how much burst traffic is allowed — larger values allow more data in short periods but may affect fairness.
- Monitor traffic patterns and adjust values based on real usage to avoid under- or over-provisioning.
- Action: Select the Drop option if you want to drop excess traffic beyond the set limits or select the Permit at Low PRI option to allow excess traffic but marking it as low priority (may be dropped during congestion).
- Click OK to save and apply the traffic policy.
- Click Cancel to exit the traffic policy creation without saving the changes.
- Click Close to exit the Feature Configuration dialog box.
The configurations are updated under Property. If you want to edit the configuration, select it and click Configure to edit the settings.Note: Use the switch-level option to add additional ACLs, VLANs, or static routes other than those already defined at the switch group level. Use the group-level configuration to make changes to existing settings at the group level.