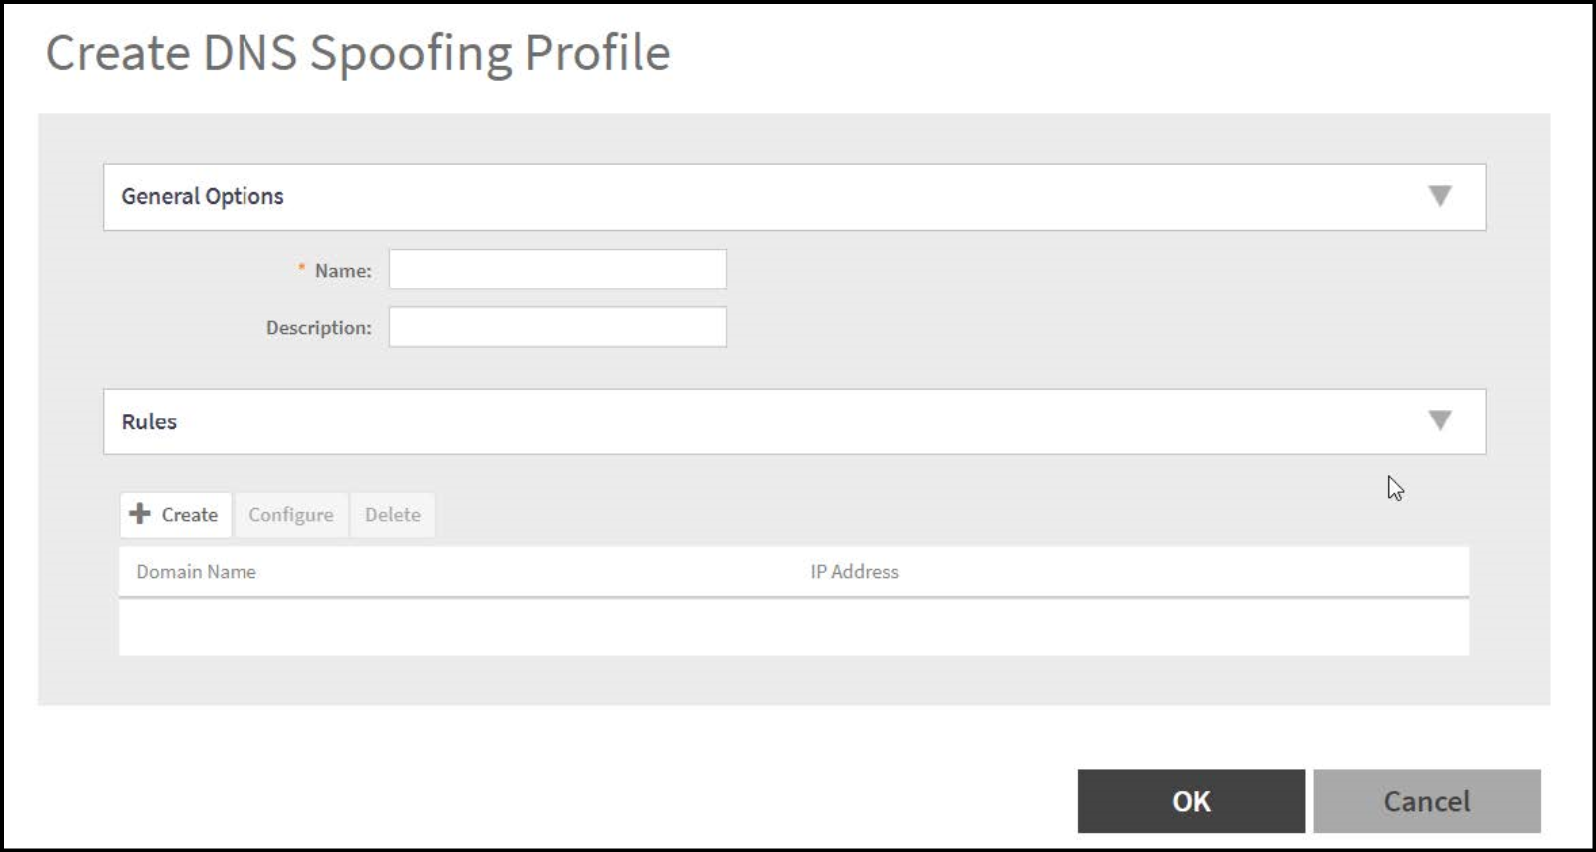
Creating a DNS Spoofing Profile
A DNS spoofing profile allows you to
specify individual Fully Qualified Domain Name (FQDN) entries to bypass DNS resolution
and
provide clients with the result specified in the associated rules. The AP intercepts
DNS
queries for specified URLs and returns a spoofed response containing the IP address
defined
in the DNS spoofing profile.
- Click
- Select a zone to create a DNS spoofing profile and click Create.
- Configure the following:
- General Options
- Rules
- Click Create, and the Create Rules dialog box is displayed.
- Domain Name : Enter the FQDN of an individual host entry.
- IP List: IP Address: Enter the IP Address to resolve the domain name and click Add. If the user sends a request with the domain name configured in the DNS Spoofing profile, then the AP responds with the IP address configured in the DNS Spoofing profile for the requested domain name.
- Click OK to save the rule.
- Click OK to confirm the creation of DNS spoofing profile.