Advanced Options
Advanced Options for Zones, AP Groups, and Individual APs
*This feature is available only after a zone is created.
Restricted AP Access Profile: This option is available only when an existing AP Access Profile is available for the zone. Navigate to to create an AP Access Profile.
BSS Coloring: This feature uses intelligent color codes (or marks) to identify shared frequencies in the spectrum. These color codes are included in the PHY header exchanged between the device and the network. The access points utilize these color codes to determine if simultaneous spectrum usage is allowed. The channel is considered busy and unavailable only when the same color is detected. This feature helps address overlapping Basic Service Set (OBSS) problems, maximizing network performance by decreasing co-channel interference and optimizing spectral efficiency.
Bonjour Fencing: Limits the range of the Bonjour service discovery
within a physical space based on network hop distance. Switch the toggle to
ON and select an existing Fence Policy
from the drop-down menu or create a new policy by clicking the  icon. You
must save the zone before you can create the policy.
- Note:
- Bonjour is Apple's implementation of a zero-configuration networking protocol for Apple devices over IP. It allows OS X and iOS devices to locate other devices such as printers, file servers, and other clients on the same broadcast domain.
- This option is grayed out if a fencing profile is not available for the zone. A Bonjour Fencing profile must be created in the zone for this option to be available.
Bonjour Gateway: Bonjour Gateway policies allow APs to offer Bonjour services across different VLANs by forwarding the mDNS packets sent by the wireless clients. This feature includes a configurable mDNS proxy service accessible through the web interface. Administrators can use this service to specify which types of Bonjour services can be accessed from or to which VLANs.
For the Bonjour Gateway to function, the following network configuration requirements must be met:
- The target networks must be segmented into VLANs.
- VLANs must be mapped to different SSIDs.
- The controller must be connected to a VLAN trunk port.
- Additionally, if the VLANs to be bridged by the gateway are on separate subnets, the network must be configured to route traffic between them.
The following requirements and limitations should be taken into consideration before enabling the Bonjour Gateway feature:
- Bonjour policy deployment to an AP takes effect after the AP joins the controller.
- The switch interfaces connected to these APs must be configured in VLAN-trunk mode. Only by doing so can the designated AP receive all the multicast Bonjour protocol packets from other VLANs.
- The switch interfaces connected to these APs must be configured in VLAN-trunk mode. Only by doing so can the designated AP receive all the multicast Bonjour protocol packets from other VLANs.
- Dynamic VLANs are not supported.
Smart Monitor: TheSmart Monitor feature checks the uplink connectivity of the APs periodically and turns off the WLANs according to the connection status of their gateway. It uses arping as a checking method with the default gateway which is fetched from the routing table automatically. According to the result, Smart Monitor will decide to turn on/off the WLANs.
AP Ping Latency Interval: Enables latency measurement between the AP and the controller every 3 minutes and sends the collected data to RUCKUS SCI, if onboarded. Disable this option if you do not want the AP - to regularly ping the controller or if RUCKUS SCI is not onboarded.
AP Management VLAN: Select between Keep AP’s Settings and VLAN ID to enter a customized VLAN ID. This configuration will change the VLAN that the AP uses for management purposes (including communication to the controller and SSH).
Rogue AP Detection: Rogue (or unauthorized) APs pose problems for a wireless network in terms of airtime contention, as well as security. The controller's rogue AP detection options include identifying the presence of a rogue AP and applying a default rogue classification policy for categorizing it as either a known neighbor AP or as a malicious rogue.
Rogue Classification Policy:
Indicates the parameters used to classify rogue APs. This option is
available after you enable the Rogue AP Detection option. Select or edit an existing policy from the
drop-down menu or create a new one using the icon and
note that policy selection and creation are available only after the initial zone
configuration has been saved.
- Report RSSI
Threshold: Set a received signal strength indicator (RSSI)
threshold above which rogue detection will start to take effect. Rogue APs
detected with below RSSI will not be reported.
Note: If left at the default value of 0, then no rogues will be reported.
- Protect the network from malicious rogue access points: Toggle this to ON to protect the network from malicious rogue APs. Choose from the following a level of aggressiveness:
- Radio Jamming
Detection: If the defined threshold has reached three
consecutive times over a 30-second interval, the AP will categorize it as
jamming and report the activity to the controller. This feature assesses overall
airtime busy percentages to determine when an AP may be experiencing signal
disruption due to jamming. The default jamming threshold of 50% specifies that
if 50% of the AP’s overall airtime is busy, the AP’s radio may be jammed.
Consider that the AP would not take any further actions other than just
notifying what could be seen as an attack. Select a threshold for the AP to flag
an attack or retain the default as 50%.
Note: A jamming attack intentionally disrupts wireless communication by transmitting interfering signals, decreasing the signal-to-noise ratio at the receiver side. Jammers transmit radio signals that override legitimate signals at the receiver.
DoS Protection: A Denial of Service (DoS) attack intentionally disrupts wireless communication by transmitting interfering signals, flooding the target with excessive traffic, and overwhelming its capacity. DoS Protection is disabled by default, but when enabled, the configuration parameters include:
- Block a Client (duration): Specifies the time, in seconds, a client is blocked after repeated authentication failures. (30-600 seconds)
- Repeat Authentication Failures (threshold): Determines how many consecutive authentication failures trigger the block. (2-25 failures)
- Time Window for Failures: Defines the monitoring window, in seconds, within which repeated authentication failures trigger the block. (30-600 seconds)
Load Balancing: Disabled by default, this feature enables the APs to balance the client load based on client count or AP capacity (total throughput). Optionally, select Disabled to disable this feature. The overloaded AP encourages the clients to connect to a neighboring AP by ignoring the association requests.
- Based on Client Count: Distribute the connected clients throughout the available APs in the zone or group to have an even distribution of the client count.
- Based on Capacity:
Distribute the connected clients throughout the available APs in the
zone or group when the APs are reaching the boundaries of the maximum capacity.
Note: The maximum capacity of the APs is determined based on various factors such as bandwidth, data rates, number of streams, and PoE received at the access point.
- Basic: Withholds probe and authentication responses at connection time in heavily loaded band to balance clients to the other band.
- Proactive: Uses the basic functionality and actively rebalances clients via IEEE 802.11v BSS Transition Management (BTM). Essentially, the AP sends a message to the client to roam, and it is left to the client's discretion to make its roaming decision.
- Strict: Uses proactive functionality and forcefully rebalances clients via IEEE 802.11v BTM. Essentially, the AP sends a message to the client to roam. If the client does not roam, the client is forced to disconnect. Additionally, some selected clients are forcefully disconnected directly to force them to roam.
Sticky Client Steering: Enabling this feature allows the APs to identify sticky clients (clients with low SNR) and to encourage these clients to connect to neighbor access points that can offer a better SNR. The APs monitor the received SNR reported by the connected clients and once the SNR drops below the configured threshold value, the AP starts the client steering process by finding a neighboring candidate AP that can provide a better service to the client. Once candidate AP(s) have been identified, the sticky client algorithm will send a BSS Transition Management (BTM) Request frame to the client(s) supporting BTM; depending on the client(s) response, the algorithm will take additional steps in transitioning the client (which may include a disconnect). The algorithm will disconnect the clients that do not support BTM to force scanning and finding the neighboring AP with a better service potential.
- SNR Threshold: The reported client threshold under which the AP triggers the steering algorithm. Permitted values range between 5 and 30 dB, the default is 15 dB. A lower value represents a permissive AP meaning that clients with bad signal will still be connected. A higher value encourages connections with only very good SNR.
- NBRAP Threshold: The difference in percentage of the reported SNR between the current AP and the candidate neighboring APs. The permitted values are 10% - 40%. A lower value encourages quicker roaming by choosing any AP that can offer a slightly better connection. A higher value forces the algorithm to choose only APs that can offer a significant difference in the quality of the connection.
Location Based Service: This RUCKUS proprietary feature refers to the Smart Positioning Technology (SPoT) location service. Thanks to SPoT, enterprises or Managed Service Providers can use SPoT APIs to incorporate location data into their own applications. This service is hosted external to the controller; refer to the SPoT documentation for managing the server portal.
Switch the toggle to ON to enable location-based services. The drop-down menu is displayed, select an existing SPoT server or create a new one. Optionally, edit the selected one.
Hotspot 2.0 Venue Profile: This option is available only after the zone has been saved for the first time. Switch the toggle to ON to enable the feature. A drop-down menu is displayed to select an existing venue profile. Optionally, create a new venue profile or edit the selected one. Refer to the RUCKUS SmartZone Access and Security Services Guide for advanced instructions related to configuring venue profiles for the Hotspot 2.0 WLAN services
Client Admission Control: Client admission control allows APs to adaptively allow or deny the association of clients based on the potential throughput of the currently associated clients. This helps prevent APs from becoming overloaded with clients and improves user experience for wireless users. Use the following options to configure client admission parameters separately on each radio band:
- ON/OFF Toggle: Switch the toggle to ON to enable the feature in the specified band.
- Min Client Count: Client admission control starts when the client count reaches the minimum count.
- Max Radio Load: A client will be rejected if the radio reaches the maximum radio load percentage.
- Min Client
Throughput: A client will be rejected if the estimated average
client throughput falls below the minimum client throughput threshold.
Note: Client admission control is implemented per radio and supported on IEEE 802.11n and 802.11ac APs.
AP Reboot Timeout: Access points will regularly send heartbeat messages to the controller and the default gateway to confirm they are available in the network. You have the option to enable the AP to reboot after a determined amount of time that these heartbeats are not responded. Configure the AP reboot settings as follows:
- Reboot AP if it cannot reach the default gateway (after a selected period of time): Use the drop-down to select the period of time. Values are 0 to 24 hours, in 30-minute increments; 30 minutes is the default. Choose 0 hour (never reboot) to disable this feature.
- Reboot AP if it cannot reach the controller (after a selected period of time): Use the drop-down to select the period of time. Values are 0, 30 minutes, and 2 to 24 hours (in 2-hour increments); 2 hours is the default. Choose 0 hour (never reboot) to disable this feature.
Venue Code: When used in RADIUS, the venue code helps log information about where a client has roamed within the network. RADIUS servers can use the Venue Code to take specific actions based on the client’s location. Enter the required code that matches the accounting policies configured in the RADIUS server.
Recovery SSID: Also known as Island SSID, it is intended to facilitate recovery of the system. Switch the toggle to ON to enable broadcast of the recovery SSID when the AP loses connection to the controller or the gateway. The AP will disable this SSID when an arping response from the gateway and controller is restored.
- Custom Passphrase. By default, the passphrase to connect to this SSID is the AP admin password. Toggle the switch to ON to enter a custom passphrase. After the Custom Passphrase option is enabled and configured, due to the security mechanism, the original default passphrase cannot be restored by toggling OFF the Custom Passphrase option.
- The recovery WLAN uses the IP address 10.154.231.125.
- There is no DHCP service in this WLAN, so the wireless client will need a static IP address in the subnet 10.154.231.0/24.
Refer to the RUCKUS SmartZone Troubleshooting and Diagnostics Guide for additional instructions on how to recover the AP depending on the issue that caused the disconnection.
Directed Multicast: By default, the AP inspects multicast traffic and tracks client IGMP/MLD subscriptions to determine packet handling—converting subscribed multicast data to unicast and dropping unsubscribed packets. Exceptions like Bonjour and uPnP bypass this logic, with conversion is determined by the WLAN’s Directed Threshold. The controller applies this forwarding logic based on whether the traffic originates from wired or wireless clients on the same AP or elsewhere in the network.
Health Check Sites: The AP model M510 periodically checks the connectivity to the specified web servers. When no port is specified, the default port used is 443. This option is disabled by default, but when enabled, five valid web sites are automatically defined (but can be changed).
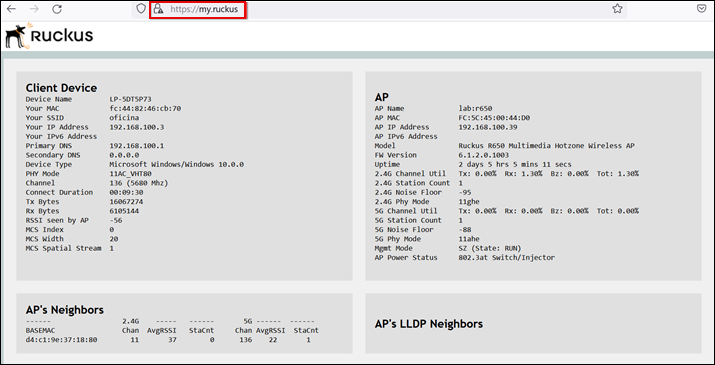
My.Ruckus support for Tunnel-WLAN/VLAN: My.ruckus web diagnosis is a diagnostics tool that allows wireless clients connected to a RUCKUS AP to navigate to the web page https://my.ruckus to receive diagnostic information about the client’s connection. This information is valuable for troubleshooting either for the end user, the network administrator, or the RUCKUS Support team. This feature is enabled by default for Local Break Out (LBO) WLANs if the AP’s management VLAN is in the default VLAN (1). By enabling this toggle, my.ruckus diagnostics will also be enabled for tunneled WLANs and WLANs using other VLANs different from the management VLAN.
Test Speed: Enable this toggle to allow speed tests on a specific AP from the Health tab. Refer to the RUCKUS SmartZone Troubleshooting and Diagnostics Guide for additional instructions on how to run speed tests on your APs.