Creating an Ethernet Port Profile
An Ethernet port profile contains
settings that define how an AP will handle VLAN packets when its port is designated
as a
trunk, access, or general port. By default, three Ethernet port profiles exist:
General
Port, Access Port, and Trunk Port.
- From the main menu go to .
- Select the Ethernet Port tab, and then select the zone for which you want to create the profile.
- Click Create.
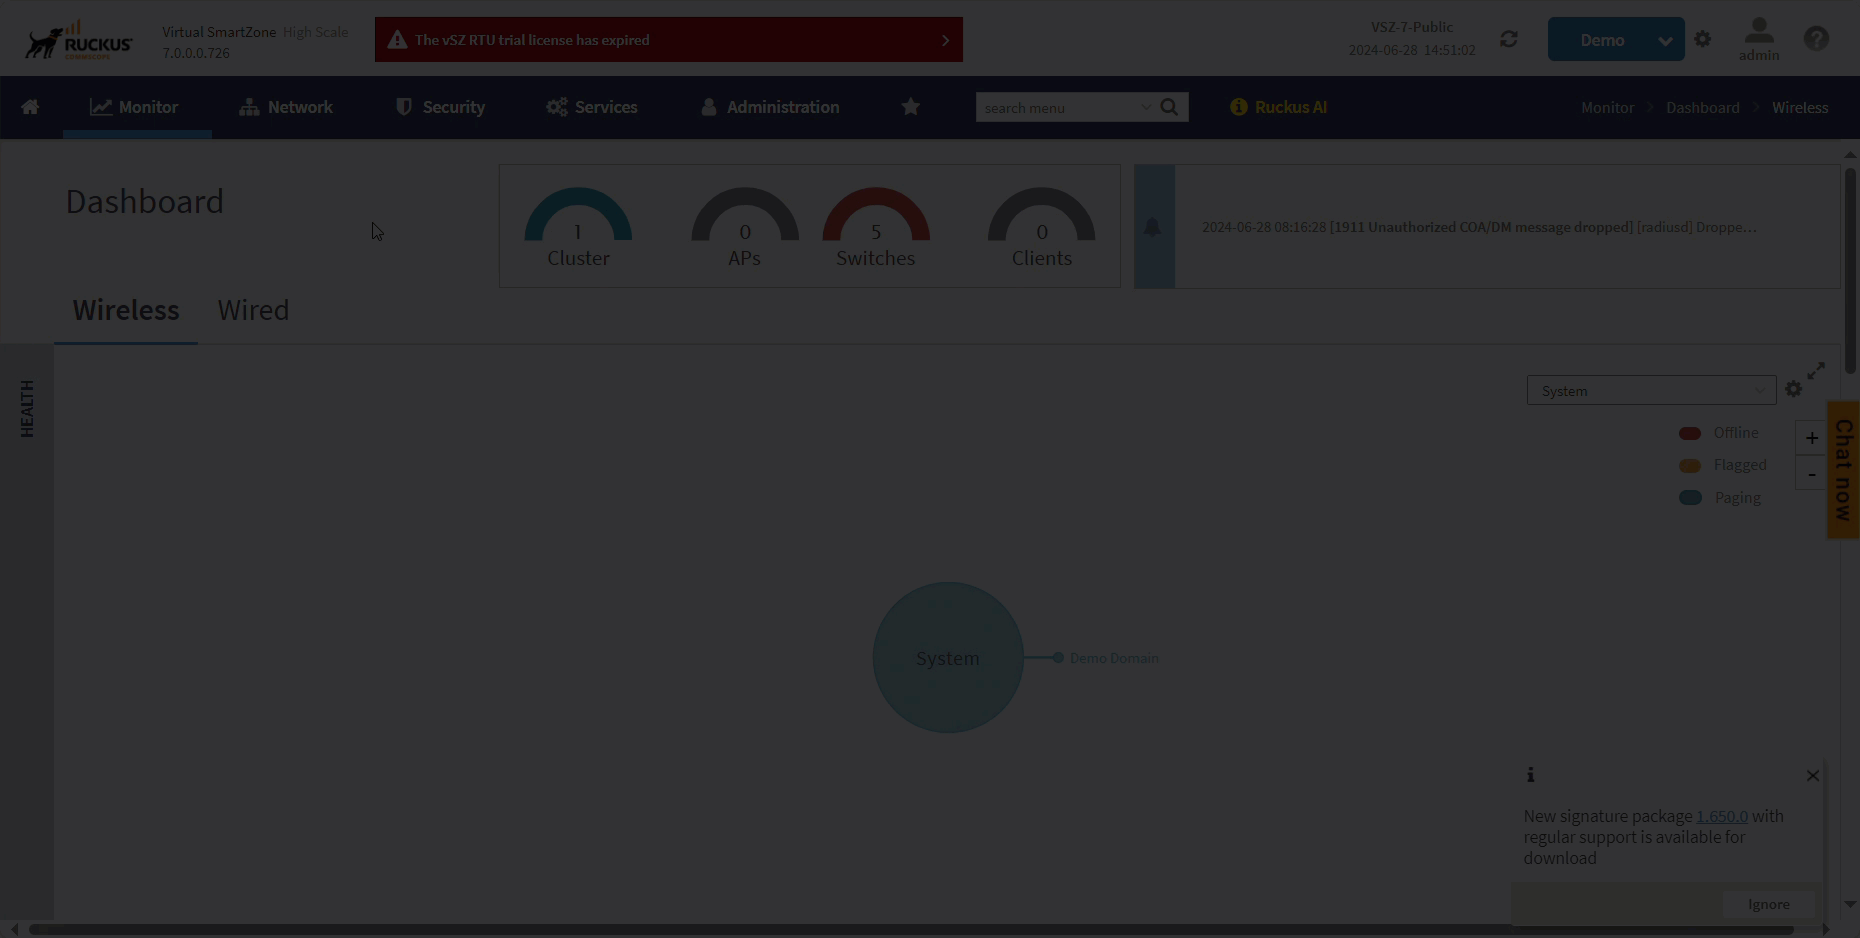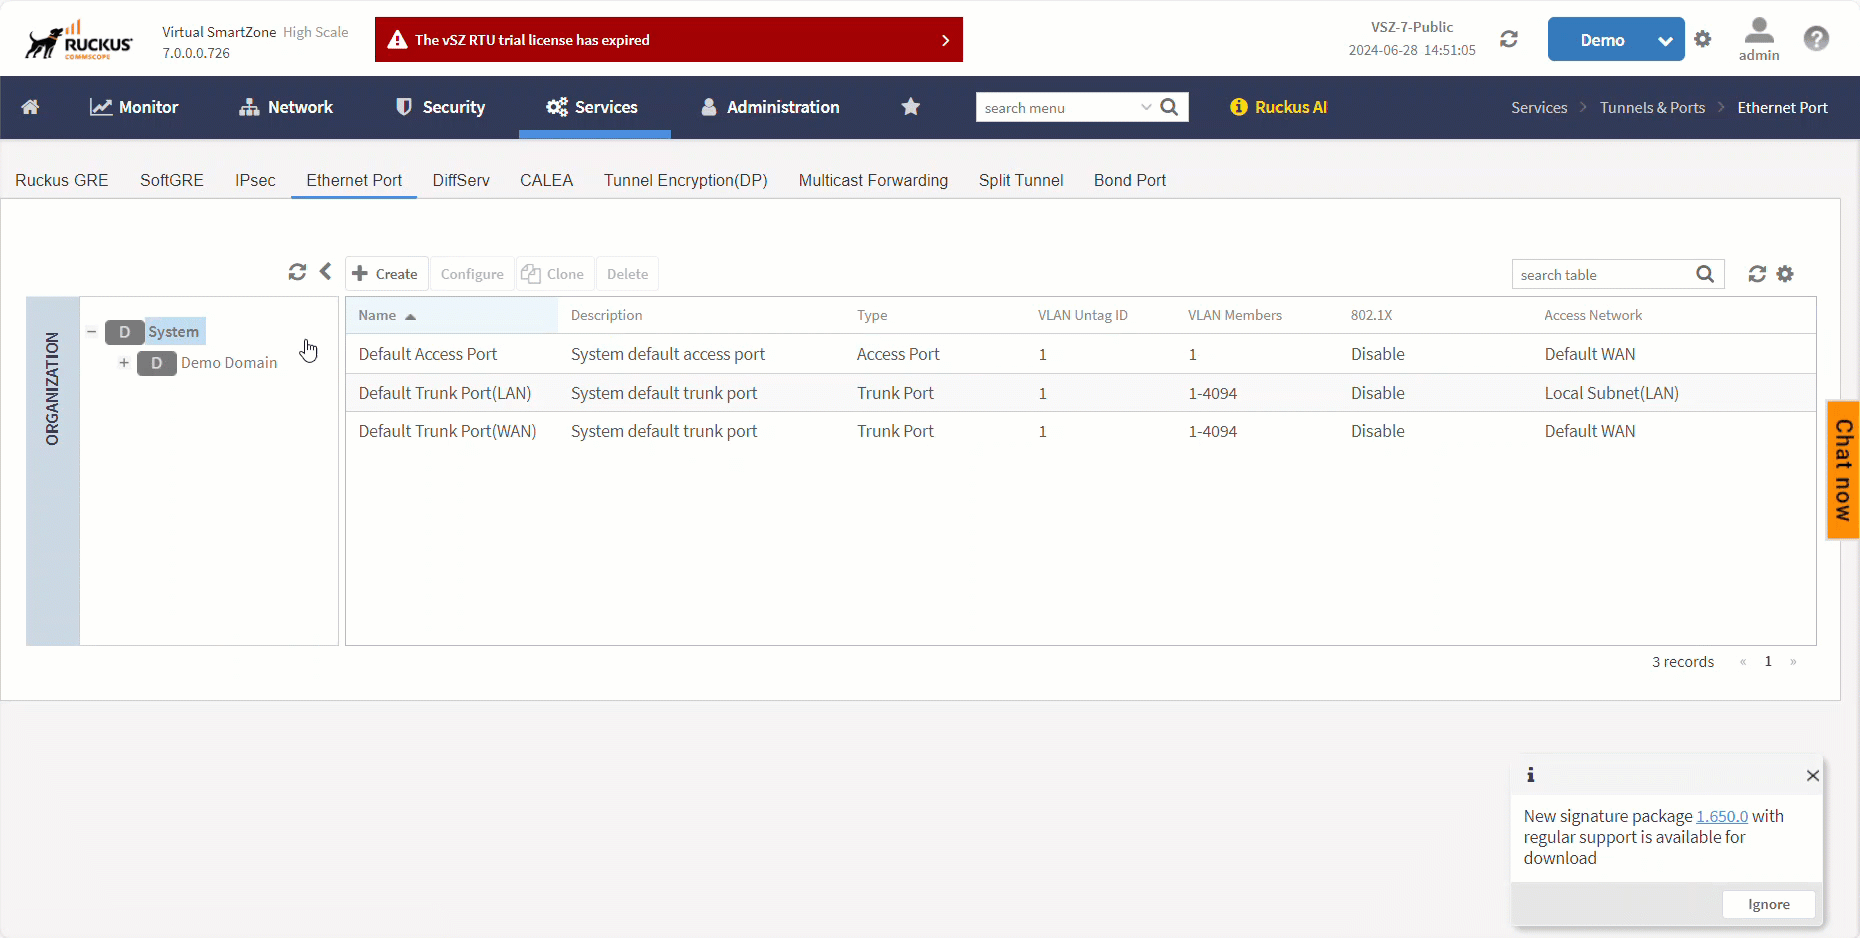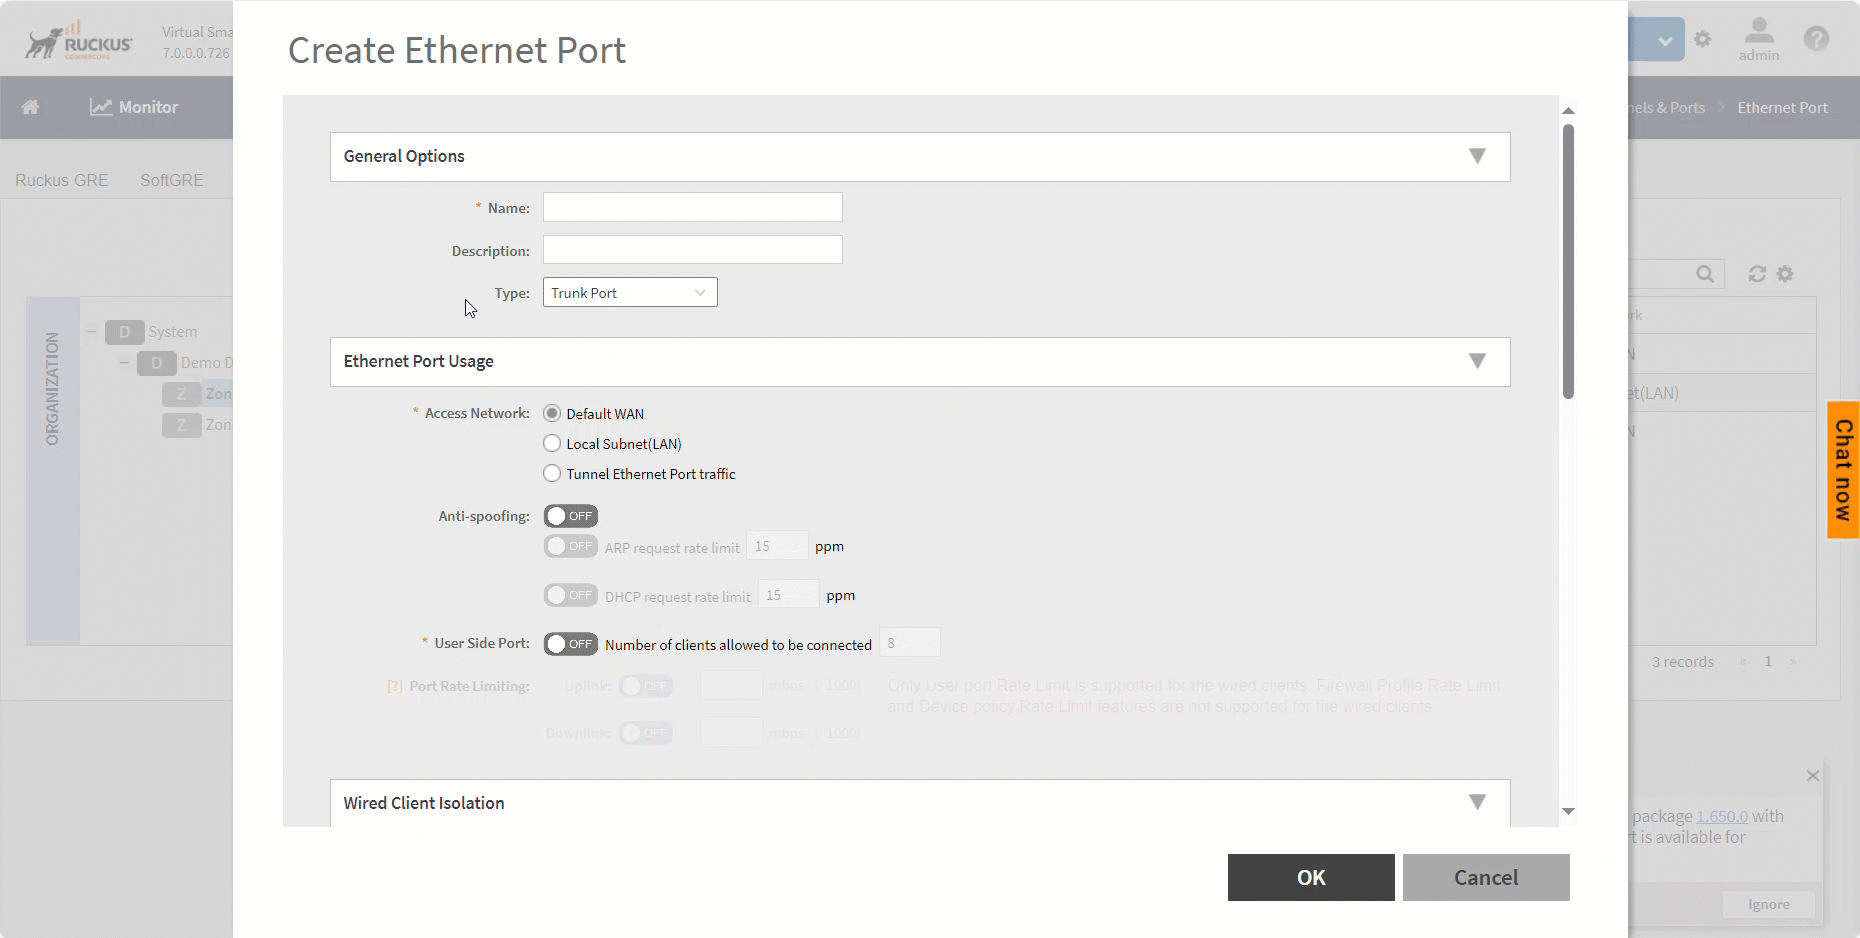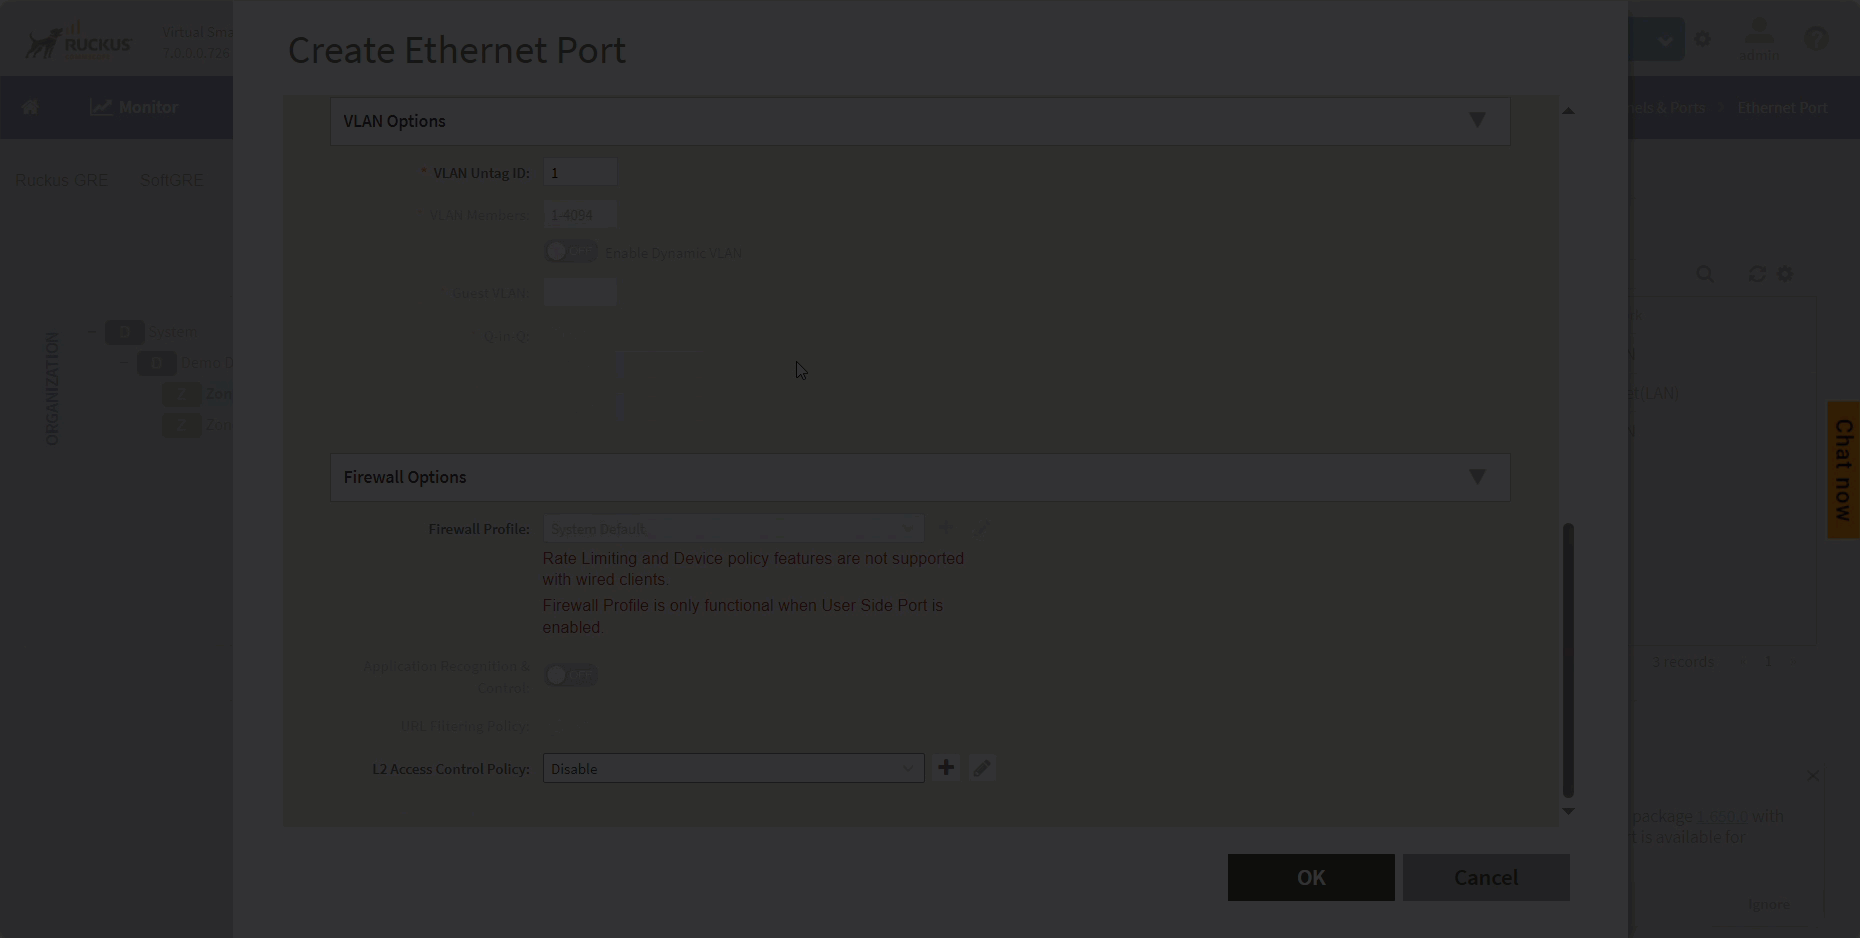
- Configure the following options:
- General Options
- Name: Enter a name for the Ethernet port profile that you are creating.
- Description: Enter a short description about the profile.
- Type: The Ethernet port type defines how the AP will manage VLAN frames. You can set Ethernet ports on an AP to one of the following types: Trunk Port, Access Port, or General Port. For a detailed explanation of these ports, see Designating an Ethernet Port Type.By selecting the appropriate port type, authentication method, and 802.1X role, you can configure the Ethernet ports to be used for the wired client. If you select a non-user port, there is no restriction on the number of clients supported. If the User Side Port is selected, the maximum number of supported clients is 32 and this number is configurable.
- Ethernet Port Usage
- Access Network:
- Anti-spoofing: Prevents attacks on genuine clients
from rogue clients that could lead to service disruption, data
loss, and so on. This is achieved by matching the MAC address or
IP address (IPv4) of the client with the address in the RUCKUS
database. If the addresses do not match, the packet is dropped.
These checks are also performed on ingress data packets to catch
spoofed data packets early.
- ARP request rate limit: The Address Resolution Protocol (ARP) limits the rate of ARP requests from the connected clients to prevent ARP flooding. Enter the number of packets to be reviewed for ARP attacks per minute. In ARP attacks, a rogue client sends messages to a genuine client to establish connection over the network.
- DHCP request rate limit: The DHCP request limits the rate of DHCP requests from the connected clients to prevent DHCP flooding. Enter the number of packets to be reviewed for DHCP pool exhaustion, per minute. When rogue clients send a DHCP request with a spoofed address, an IP address from the DHCP pool is assigned to it. If this happens repeatedly, the IP addresses in the DHCP pool are exhausted, and genuine clients may miss out on obtaining the IP addresses.
Note: When you enable anti-spoofing, an ARP request rate limiter and a DHCP request rate limiter are automatically enabled with default values (in packets per minute) which are applied per client; implying that each client connected to an interface enabled with anti-spoofing is allowed to send a maximum of "X" ARP and DHCP request packets per minute (ppm). The "X" value is configured on the interface to which the client is connected. - User Side Port: User Side Port is by default enabled when 802.1x is enabled.
- Wired Client Isolation
- Client Isolation: Prevents wired clients
from communicating with each other. This option isolates wired
client traffic from all hosts on the same VLAN/subnet. By
default, this option is disabled. Enable the following options
as approriate:
- Isolate unicast packets: Isolates only unicast packets between a wired client enabled with client isolation and other clients of the AP. By default, this option is enabled.
- Isolate multicast/broadcast packets: Isolates only multicast/broadcast packets between a wired client enabled with client isolation and other clients of the AP. By default, this option is disabled.
- Automatic support for VRRP: Isolates packets in Virtual Router Redundancy Protocol (VRRP) deployment. By default, this option is disabled indicating the AP is not in VRRP deployment.
- Client Isolation: Prevents wired clients
from communicating with each other. This option isolates wired
client traffic from all hosts on the same VLAN/subnet. By
default, this option is disabled. Enable the following options
as approriate:
- Authentication Options
- 802.1X: Select to enable 802.1X authentication.
- 802.1X Role: Select the authenticator role from
the menu.
- Supplicant: You can customize the user name and password to authenticate as a supplicant role or use the credentials of the AP MAC address.
- MAC-based Authenticator: Each MAC address host is individually authenticated. Each newly learned MAC address triggers an Extensible Authentication Protocol over LAN (EAPoL) request-identify frame.
- Port-based Authenticator: Only a single MAC address host must be authenticated for all hosts to be granted access to the network.
- Enable client
visibility regardless of 802.1X authentication: If client
visibility is enabled, you can view connected wired client
information. Client visibility is enabled by default if the
802.1x authentication method is selected. For the open
authentication method, you must enable client visibility based
on your requirements.
Note: You can view statistical information about wired clients without enabling 802.1X authentication.
- Supplicant: Select the authentication type
- VLAN Options
- VLAN Untag ID: Enter the ID of the native VLAN (typically 1), which is the VLAN into which untagged ingress packets are placed upon arrival. If your network uses a different VLAN as the native VLAN, configure the VLAN Untag ID of the AP Trunk port with the native VLAN used throughout your network. If Local Subnet option is selected in Ethernet Port Usage, then VLAN ID configured should be the same as one of DHCP NAT VLANs.
- VLAN Members: Enter the VLAN IDs that you want to use to tag WLAN traffic that will use this profile. You can enter a single VLAN ID or a VLAN ID range (or a combination of both). The valid VLAN ID range is from 1 through 4094. If Local Subnet option is selected in Ethernet Port Usage, then only DHCP NAT VLANs are allowed on trunk port.
- Enable Dynamic VLAN:
Select this check box if you want the controller to assign VLAN
IDs on a per-user basis. Before enabling dynamic VLAN, you must
define on the RADIUS server the VLAN IDs that you want to assign
to users.
Note: The Enable Dynamic VLAN option is only available when the Type is set to Access Port and 802.1X authentication is set to MAC-based Authenticator.Note: If you enable client visibility, a maximum of 16 clients can be connected to a port regardless of the 802.1X authentication. The same limitation applies when 802.1X authentication is enabled and client visibility is not enabled.
- Guest VLAN: Select this option if you want to limit the device access to internal network resources only.
- QinQ VLAN: Select the check box and update the ranges:
- Authentication and Accounting
Services
- Authentication Server: Select the check box and a controller from the menu to use the controller as a proxy authentication server.
- Accounting Server: Select the check box and a controller from the menu to use the controller as a proxy accounting server.
- Enable MAC authentication bypass: Select this check box if you want to use the device MAC address as access credentials (user name and password).
- RADIUS Options
- Firewall Options
Note: The User Side Port must be enabled to configure the Firewall Profile, Application Recognition and Control, and URL Filtering Policy.Note: While mapping group attribute values to the user role, avoid special characters or duplicate entries regardless of the order.
- Firewall Profile: Select the firewall profile for wired ports.
- Application Recognition and Control: Enable the option for the wired clients.
- URL Filtering Policy: Enable the option for wired clients.
- L2 Access Control Policy: Select the Layer 2
policy for wired ports. When the User Side Port is not enabled,
a Layer 2 Access Control wired support policy can be mapped
directly to the wired port. If the User Side Port is enabled,
the Layer 2 Access Control wired support policy can be mapped to
the wired port of the firewall profile. Click
 to create a new policy. Refer to
the Creating a
L2 Access Control Service section of the Network
Administrative Guide for more information.
- Click OK.
- General Options
Note: You can edit, copy, or delete the profile by
selecting the options Configure, Clone, or Delete, respectively,
from the Ethernet Port tab.