AP SNMP Options
SNMP options are disabled by default, you can toggle the switch to ON to enable the SNMP protocol in the APs and allow configuration of the SNMP options. You can set customized options on the go or click AP SNMP Agent Profile to select an existing SNMP profile or create a new profile. Any of these types of profiles requires defining an SNMPv2 Agent, an SNMPv3 Agent, or both.
AP SNMP Options for Zones, AP Groups, and Individual APs
| AP Configuration / Configuration Level | Zone | AP Groups | Individual AP | |
|---|---|---|---|---|
| AP SNMP Options | Enable AP SNMP | √ | √ | √ |
| Config Type | √ | √ | √ |
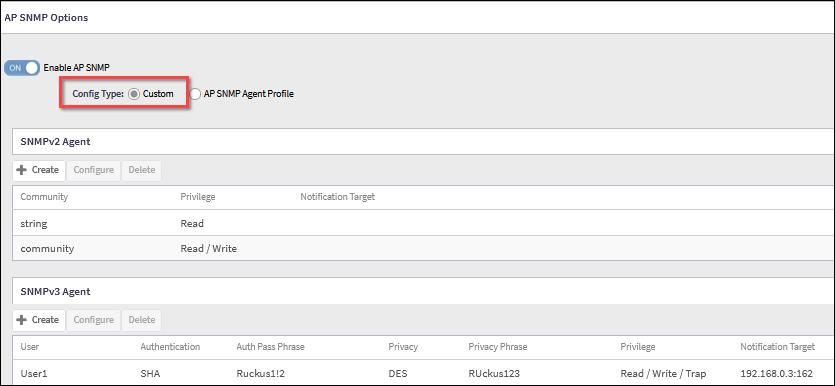
SNMPv2 Agent: Create a community string. The community string is used in SNMPv2 as a password for the SNMP Agent to access information in the AP; it can have read/write or read-only privileges.
Optionally, click the Notification checkbox to enable the AP to send notifications. Type the target IP to define the Agent receiving these notifications. Additionally, define a port number for the SNMP notifications or use the default port number 162. Click Add to add the notification receiver to the list.
Two types of notifications can be sent, Trap and Inform. Both traps and informs are mechanisms used by network devices to send notifications or alerts to an SNMP manager:
- Trap: A trap is an unsolicited message sent by the AP to the SNMP manager to indicate a significant event or condition. Traps are asynchronous and are sent immediately when the event occurs, without waiting for acknowledgment from the SNMP manager. Trap is the default notification type.
- Inform: Unlike traps, informs are acknowledged messages. After sending an inform, the device waits for an acknowledgment (ack) from the SNMP manager. If the SNMP manager receives the inform successfully, it sends an acknowledgment (ack) back to the device, confirming receipt of the notification
SNMPv3 Agent: SNMPv3 is an enhanced version of earlier SNMP versions (SNMPv1 and SNMPv2c) and offers improved security and authentication features. Define the following information for the agent:
- User: A user in SNMPv3 is associated with specific security parameters, including authentication and privacy settings, which are used to control access to SNMP-managed devices.
- Authentication: It ensures the integrity and authenticity of
SNMP messages exchanged between SNMP agents and SNMP managers, involving the use
of cryptographic algorithms to generate a message digest or checksum based on
the contents of the SNMP message and a shared secret.
- SHA - Produces hash values of different lengths. It is considered more secure than MD5 due to its larger hash sizes and resistance to collision attacks. SHA is the default setting.
- MD5 - Produces a fixed-size hash value of 128 bits. It is generally faster than SHA algorithms, but its speed advantage comes at the cost of reduced security.
- Auth Passphrase: Used in the authentication algorithms to ensure the integrity and authenticity of SNMP messages.
- Privacy: Privacy involves the use of encryption algorithms, such as DES (the Data Encryption Standard) or AES (the Advanced Encryption Standard), to encrypt the payload of SNMP messages. This encryption process obscures the contents of the SNMP messages, making them unintelligible to eavesdroppers. By default, Privacy is set to NONE.
- Privilege: Select between Read-Only and Read-Write. Optionally, add a notification mechanism.