Configuring NTP over Management VRF on an NTP Client
To implement NTP over Management VRF, a
Network Time Protocol (NTP) client device must be configured to communicate with
an NTP
server device.
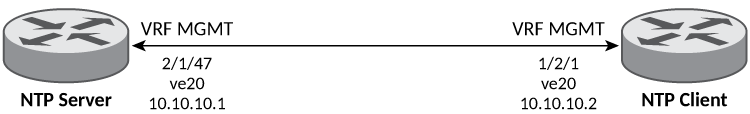
- Enter global configuration mode.
- Configure a port-based VLAN and enter VLAN configuration mode.
- Add an untagged port to the VLAN.
- Create a virtual routing interface.
- Exit to global configuration mode.
- Configure the VRF named management as a global management VRF.
- Enter virtual interface mode for interface ve 20.
- Configure the VRF named mgmt as a forwarding VRF.
- Configure an IP address on the interface.
- Exit to global configuration mode.
- Identify the source interface for the NTP server.
- Enable the Network Time Protocol (NTP) client and server mode.
- Identify the IP address of the VE interface through which the management VRF is running.
The following example configures NTP over Management VRF on an NTP Client including the initial VRF configuration.
configure terminal
 vrf mgmt
  rd 3:3
  address-family ipv4
   ip route 0.0.0.0/0 10.10.10.2
   vlan 20 by port
  untagged ethernet 1/2/1
  interface ve 20
  exit
 management vrf mgmt strict
 interface ve 20
  vrf forwarding mgmt
  ip address 10.10.10.2 255.255.255.0
management source-interface ve 20 protocol ntp
 ntp
  server 10.10.10.1