Import Authorized Public Keys into the ICX Device
SSH clients that support DSA or RSA authentication normally provide a utility to generate a DSA or RSA key pair. The private key is usually stored in a password-protected file on the local host. The public key is stored in another file and is not protected. You must import the client public key for each client into the RUCKUS ICX device.
Note: The keys must be in RFC 4716 format before import.
- Collect one public key of desired types (RSA and DSA) from each client to be granted
access to the
RUCKUS ICX device, and list the keys in one file.
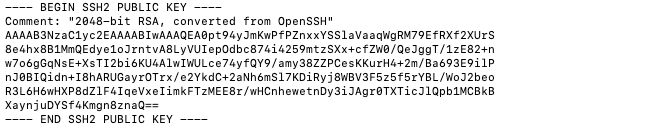
The following example shows a public key file containing one public key.Note: The public key file may contain up to 16 keys.Note: Each key in the public key file must begin and end with the first and last lines shown in the example. If your client does not include these lines in the public key, you must add them manually.
- Place the public key file onto a TFTP server.
The example uses SCP to place the public key file pkeys.txt for user1 on the TFTP server at IP address 10.168.1.234 in file location ssh/pkeys.txt.
- Enter the
ip ssh pub-key-file tftpcommand followed by the IP address of the TFTP server and the public key filename to import the public key file into the active configuration of the RUCKUS ICXdevice from a TFTP server.The following example copies the public key file pkeys.txt to the ICX device from the TFTP server at IP address 10.168.1.234. - (Optional) Enter the
show ip client-pub-keycommand to confirm that the public key file has loaded correctly as shown in the following example.device# show ip client-pub-key ---- BEGIN SSH2 PUBLIC KEY ---- Comment: "2048-bit RSA, converted from OpenSSH" AAAAB3NaC1yc2EAAAABIwAAAQEA0pt94yJmKwPfPZnxxYSS1aVaaqWgRM79EfRXf2XUrs 834hx881MmQedye1oJrntvA8LyVUIepOdbc874i4259mtSXx+cfZW0/QeJggT/1zE82+n w706gGqNsE+XsT12bi6KU4Al2IWULce74yfQY9/amy38ZPCesKKurH4+2m/Ba69391lp nJ0BIQidn+I8hARUGayrOTrx/e2^kdC+2aNh6mS17KDiRyj8WBV3F5z5f5rlYBL/WoJ2beo R3L6H6wHXP8dZ1F4IqeVxeIimkFTzMEE*r/wHCnhewetnDy3iJAgr0TXTicJ1Qpb1MCBkB XaynjuDYSf4Kmgn8znaQ== ---- END SSH2 PUBLIC KEY ----