Enabling URL Filtering on the WLAN
Complete the following steps to create a URL filtering policy.
- From the main menu, go to .
- Select the
Profiles tab, and then click
Create.
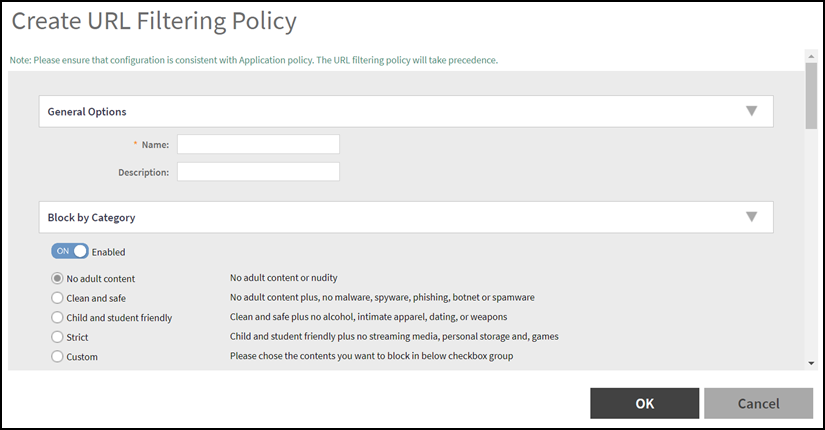
The Create URL Filtering Policy page is displayed.
Configure the following options:
- General Options
Name:: Enter the name of the policy you want to create.
Description: Enter a brief description to identify the policy.
- Blocked Categories: Select one of the categories to block. Selecting the Custom option allows the administrator to customize the list of categories to block for the user. You can also use Select All to choose all of the categories listed, or None to set no filters for the user to access (the user can access any URL in this case because no web page is blocked).
- Block by Threat
Level: Enable this option and set the slider bar to a threat
level. The web reputation score, from 1 through 100, gives the
reputation index or threat level of a URL being browsed by a user. The
reputation score can be used to categorize the threat level of URLs
according to the following levels:
- Trustworthy: The web reputation score is in the range of 81 through 100. These are well known sites with strong security characteristics.
- Low-Risk: The web reputation score is in the range of 61 through 80. These are generally benign sites and rarely exhibit the characteristics that expose the user to security risks.
- Moderate-Risk: The web reputation score is in the range of 41 through 60. These are benign sites but have exhibited some characteristics that suggest a security risk.
- Suspicious: The web reputation score is in the range of 21 through 40. These are suspicious sites.
- High-Risk: The web reputation score is in the range of 1 through 20. These are high risk sites.
-
Blocklist &
Allowlist: If web content categorization, is unable to classify
URLs that the user, organization or institution needs, then Allowlist
and Blocklist profiles can be created by the administrator. The URLs
listed by the administrator under Blocklist are blocked and those listed
under Allowlist are allowed access. The domain names under Blocklist and
Allowlist take precedence over the default allow or deny action of the
URL filter.
The AP matches the URL pattern against all the configured Allowlist and Blocklist profiles through the Extended Global Regular Expressions Print (egrep) program which performs a line-by-line scan of the file and returns lines that contain a pattern matching the given expression. Currently, the exact URL name or a wildcard at the beginning of the URL is used to match the pattern. From R5.2 onwards, the wildcard (*) character is supported in middle and on either start or end, for example, "*.ruckus*.com", www.ruckus*.co*). This only allows a maximum of two wildcards (*).
Administrators can also add specific IP addresses or wildcard domain names under Allowlist and Blocklist.
In Domain Name: Enter the domain name of the web page which you want to deny user access to in the Blocklist tab, and enter the domain name of the web page to which you want to provide user access on the Allowlist tab. You can define up to 16 domains.
Click Add. The domain name or web page is listed in the corresponding tab.
Click Cancel to remove the domain name you have entered in the field.
If you want to delete the domain name from the Blocklist or Allowlist tab, select the URL and click Delete.
- Safe Search:
Administrators can configure the policy to include a safe search option
when users access Google, YouTube, or Bing to search on the internet.
Select the respective enable option for Google, YouTube, and Bing.
Enabling the option will mandate all users using the policy on the
network to use safe search on Google, YouTube, and Bing. By default,
FQDN-based safe search is enabled. This option provides a secure
connection through HTTPS while allowing access to the internet.
6.1.1 updateTo use virtual IP (IPv4 and IPv6) address, select the Virtual IP option and enter the IP address. If safe search is enabled before upgrading to release 6.1, the old configuration or virtual IP-based safe search is retained.
- General Options
- Click
OK.
The URL Filtering Policy form is submitted with the specified configuration settings.
Click Configure to edit the policy. Click Clone to create a duplicate of the policy, or to make modifications to the existing settings of the clone.
Click Delete to delete the policy from the URL Filtering Profile.