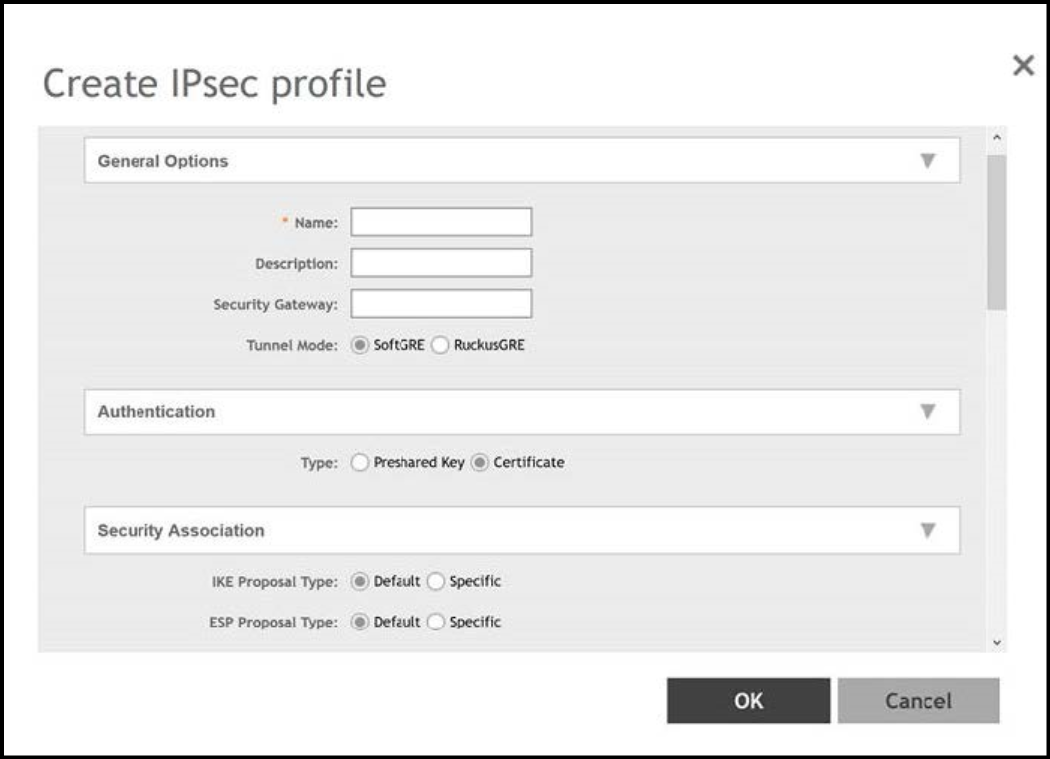
Creating an IPsec Profile
- From the main menu, navigate to .
- Select the IPsec tab, and then select the zone for which you want to create the profile.
- Click Create.
- Under General Options,
configure the following options:
- Name: Enter a name for the profile.
- Description: Enter a description for the profile.
- Security Gateway: Enter the IP address or fully-qualified domain name (FQDN) of the IPsec server. If you use the IP address, the IP address format that you must enter will depend on the IP mode that is configured on the controller.
- Tunnel Mode: Select SoftGRE or RuckusGRE.
- IP Mode: Select IPv4 or IPv6.
- Under Authentication, configure the
Type option.
Select Preshared Key to use PSK for authentication or Certificate to use an X.509 certificate on the certificate authority (CA) or registration authority (RA) server. The controller uses the CMPv2 protocol to obtain the signed certificate from the CA or RA server. If you select Preshared Key, enter the PSK. The PSK must be 8 to 128 ASCII characters in length.
- Under Security Association, configure the following
options:
- IKE Proposal Type: Select Default to use the default
Internet Key Exchange (IKE) security association (SA) proposal type or
select Specific to manually configure the IKE SA proposal. If you
select Specific, you must configure the following settings:
- Encryption Algorithm: Options include 3DES, AES128, AES192, and AES256.
- Integrity Algorithm: Options include MD5, SHA1, AES-XCBC, SHA256, SHA384, and SHA512.
- Pseudo-Random Function: Options include Use integrity ALG, PRF-MD5, PRF-SHA1, PRF-AES-XCBC, PRF-AES-CMAC, PRF-SHA256, and PRF-SHA384.
- DH Group: Options for Diffie-Hellman (DH) groups for IKE include modp768, modp1024, modp1536, modp2048, modp3072, modp4096, modp6144, and modp8192.
- ESP Proposal Type: Select Default to use
the default Encapsulating Security Payload (ESP) SA proposal type or
select Specific to manually configure the ESP proposal. If you
select Specific, you must configure the following settings:
- Encryption Algorithm: Options include 3DES, AES128, AES192, AES256, and NONE.
- Integrity Algorithm: Options include MD5, SHA1, AES-XCBC, SHA256, SHA384, and SHA512.
- DH Group: Options for Diffie-Hellman (DH) groups for ESP include None, modp768, modp1024, modp1536, modp2048, modp3072, modp4096, modp6144, and modp8192.
- IKE Proposal Type: Select Default to use the default
Internet Key Exchange (IKE) security association (SA) proposal type or
select Specific to manually configure the IKE SA proposal. If you
select Specific, you must configure the following settings:
- Under Rekey Options, configure the following
options:
-
Internet Key Exchange: Select a time unit (day, hour, or minute) from the list, and enter a number to set the time interval at which the IKE key renews. Select the Disable check box to disable the IKE rekey.
- Encapsulating Security Payload: Select a time unit (day, hour, or minute) from the list, and enter a number to set the time interval at which the ESP key renews. Select the Disable check box to disable the ESP rekey.
-
- Under Certificate Management Protocol, configure the following options:
- Under Advanced Options, configure the following
options:
- DHCP Option 43 Sub Code for Security Gateway: Set the DHCP Option 43 subcode that will be used to discover the address of the security gateway on the network. The default subcode is 7.
- Retry Limit: Set the number of times that the controller will attempt to discover the address of the security gateway. The default retry count is 5. Accepted values are 0 (disable) through 16.
- Replay Window: Set the ESP replay window (in packets). The default size is 32 packets. Accepted values are 0 (disable) through 32 packets.
- IP Compression: Click Enable to enable IP Payload Compression Protocol (IPComp) compression before encryption. The default value is Disable.
- Force NAT-T: Click Enable to enforce UDP encapsulation of ESP packets. The default value is Disable.
- Dead Peer Detection: By default, the IKE protocol runs a health check with the remote peer to ensure that it is alive. Click Disable to disable the health check.
- NAT-T Keep Alive Interval: Enter a value (in seconds) to set the keepalive interval for NAT traversal. The default keep alive interval is 20 seconds. Accepted values are 1 to 65536. To disable the keep alive interval, click Disable.
- FailOver Options: To configure the failover settings when APs are
unable to connect, configure the following options:
- Retry Period: Set the number of days (minimum 3 days) during which APs will keep attempting to connect. Select the Forever check box to keep trying indefinitely.
- Retry Interval: Set the interval (in minutes) between each retry attempt. The default retry interval is 1 minute. Accepted values are from 1 through 30 minutes.
-
Retry Mode: Click Revertive if you want APs to fall back to the specified primary security gateway. Click Non-revertive if you want APs to maintain connectivity with the security gateway to which they are currently connected.
- Click OK.Note: You can also edit, clone, and delete the profile by selecting the Configure, Clone, and Delete options respectively from the IPsec tab.