Restricted Access
The access point node on the network can be vulnerable to malicious attacks. The AP is a critical node on the network and therefore such an attack can expose the whole network. The Restricted Access profile provides a mechanism to restrict unauthorized access to the AP and allows access only to authorized users, thereby increasing the inherent security of the AP.
The AP currently has the following categories of open ports:
Well known ports on Access Points
| Sl. No. | Port | Use | Protocol |
|---|---|---|---|
| 1 | 80 | HTTP | TCP - IPv4 & IPv6 |
| 2 | 22 | SSH | TCP - IPv4 & IPv6 |
| 3 | 443 | HTTPS | TCP - IPv4 & IPv6 |
| 4 | 161 | SNMP | UDP - IPv4 & IPv6 |
| 5 | 23 | TELNET | TCP - IPv4 & IPv6 |
Overview
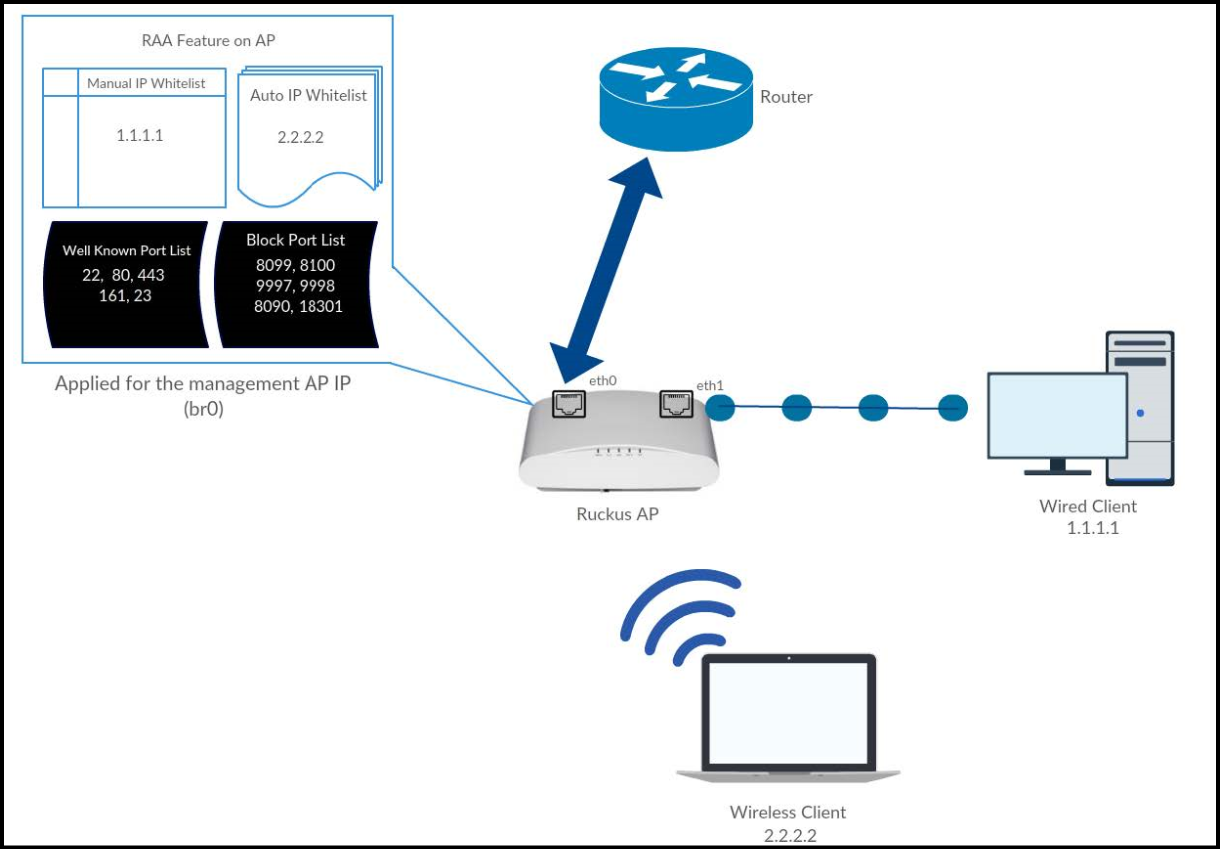
The well known port list includes the ports that are most likely to be exploited, with restricted access enabled, any node on the network trying to access the AP using these ports is blocked. This blocking functionality is configurable from the User Interface (UI) by an administrator. The administrator can perform the following functions:
- The administrator can allow temporary or permanent access to these ports for an IP or a list of IPs (IP and Subnet). These IP(s) when configured are added to the Manual White List (Max 10) and these IP(s) are given unrestricted access to the AP.
- The administrator can add ports or a range of ports to the Port Black List (Max 10) as well. These ports will be inaccessible for any node on the network that is not part of the Manual White List as configured by the administrator.