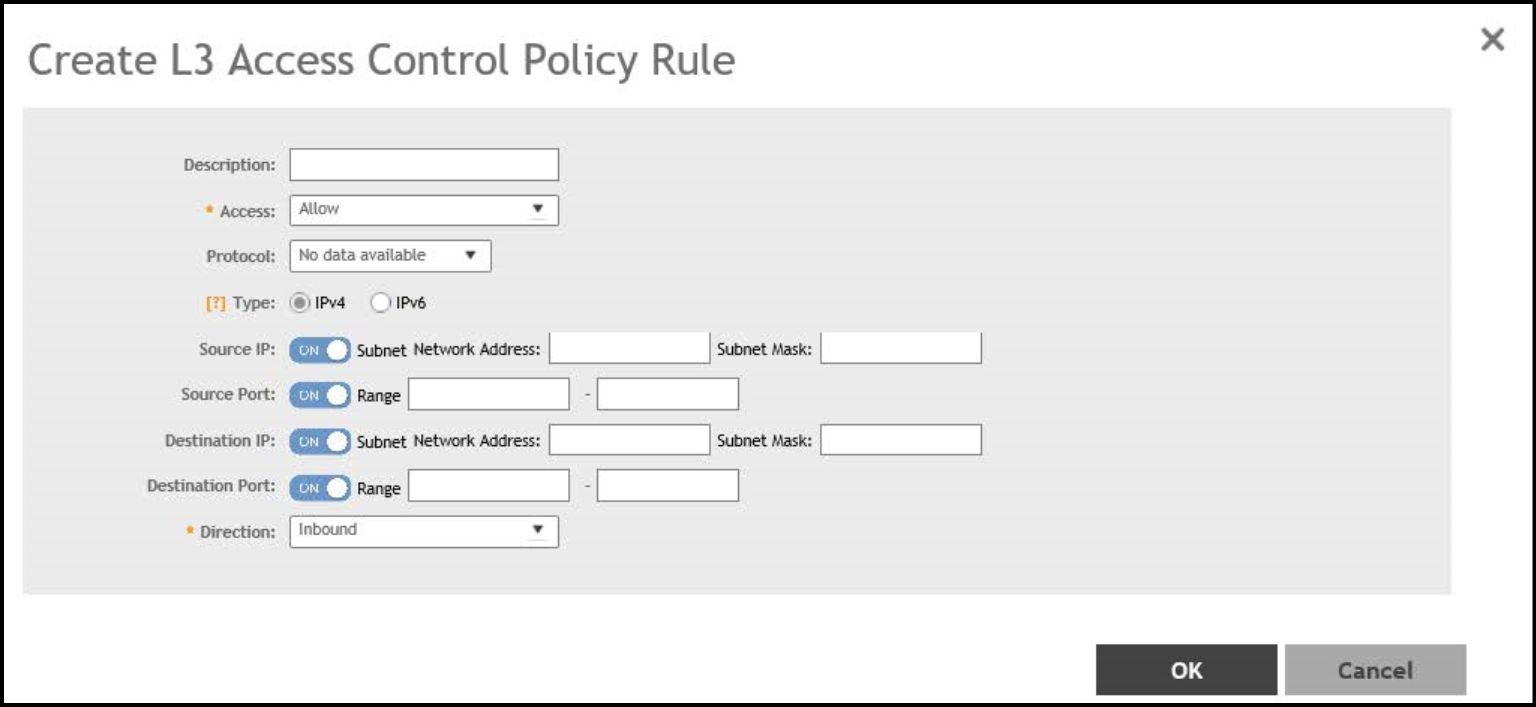
Create an L3 Access Control Policy Rule
An L3 Access Control Policy of multiple traffic control rules, which can be enforced
in any order you prefer.
- To create an L3 access control policy rule:
- From the L3 Access Control Policy page, click Create. The L3 Access Control Policy Rule page is displayed.
- Configure the following:
- Description: Type a short description for the access control policy rule.
- Access:
Select Allow or Block depending on whether you want to set this rule as the
default rule.
Note: All unicast, multicast and broadcast traffic, except the ACL rules will be allowed or dropped depending on the option selected. Add the appropriate rules.
- Protocol: Select the network protocol to which this rule will apply. Supported protocols include TCP, UDP, UDPLITE, ICMP (ICMPv4), ICMPV6, IGMP, ESP, AH, SCTP.
- Type: Choose the IP version, IPv4 or IPv6.
- Source IP: Enable the option and specify the source Subnet Network Address and Subnet Mask for IPv4 option type or enter IPv6 Network address for IPv6 option type.
- Source Port: Enable the option and specify the source port to which this rule will apply. To apply this rule to a port range, type the starting and ending port numbers in the two boxes.
- Destination IP: Enable the option and specify the destination Subnet Network Address and Subnet Mask for IPv4 option type or enter IPv6 Network address for IPv6 option type.
- Destination Port: Enable the option and specify the source port to which this rule will apply. To apply this rule to a port range, type the starting and ending port numbers in the two boxes.
- Direction: Select Inbound, Outbound or Dual indicating the direction of the traffic.
- Click OK to save your changes.