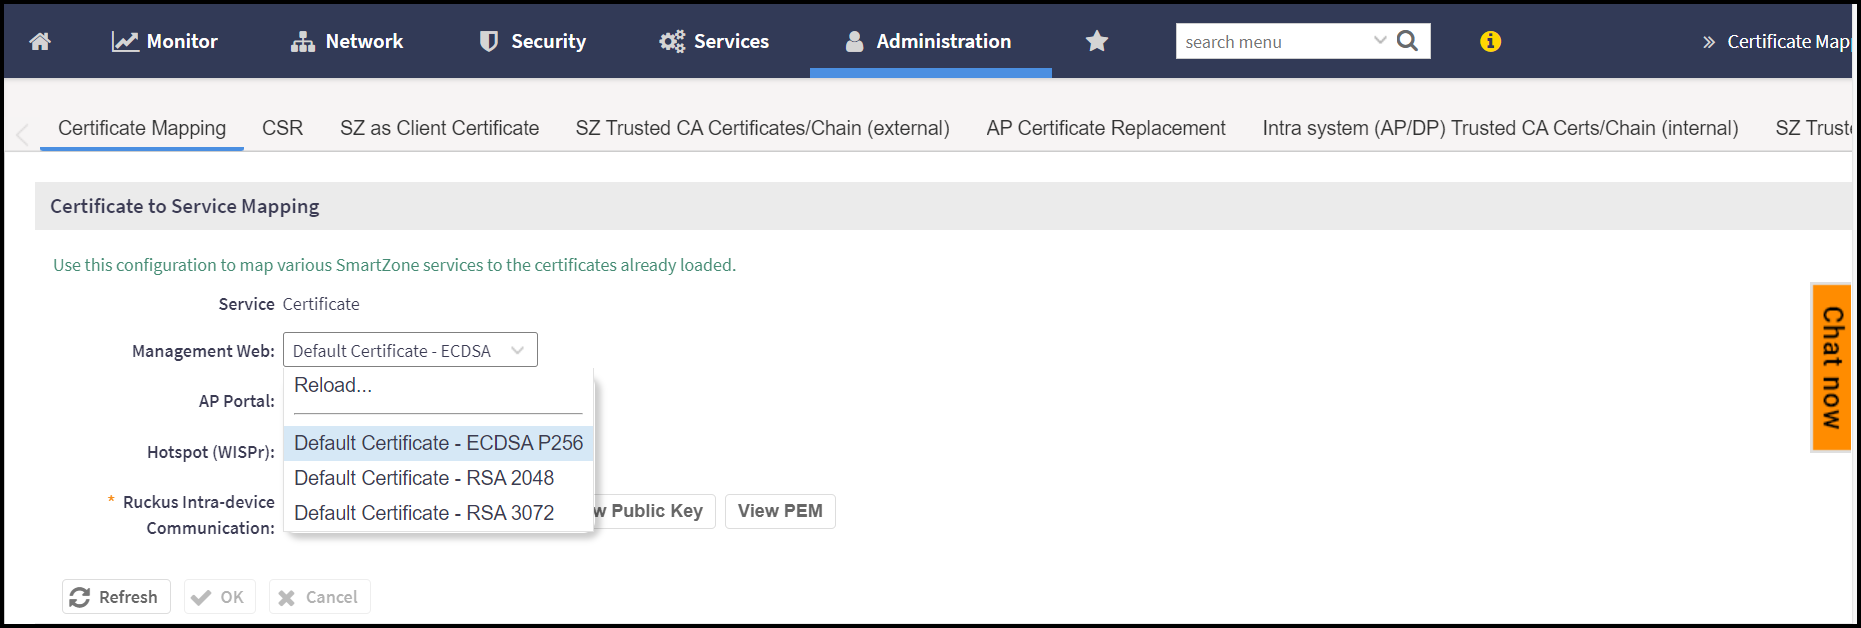
Mapping Server ECDSA Certificates
After enabling the SSH/TLS Key Enhance Mode at
the zone level. You can map the ECDSA certificates to SmartZone (server certificate).
This
mapping ensures that SmartZone (server) is using 2K/3K RSA or ECDSA certificates during
the
TLS handshake.
- Click .
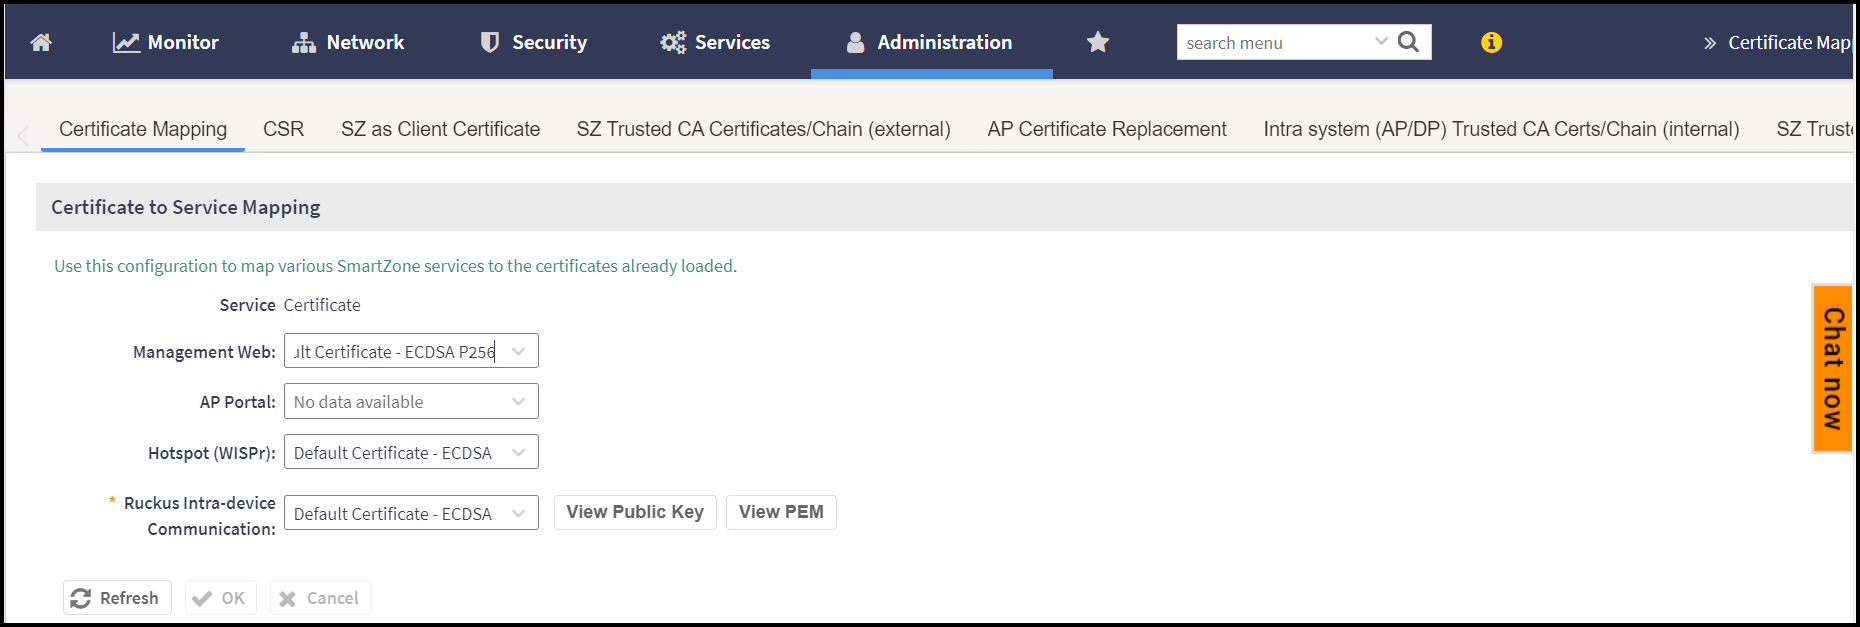
- Management Web: SmartZone uses 2K/3K based certificates to map the services when user access SmartZone user interface via web browser.
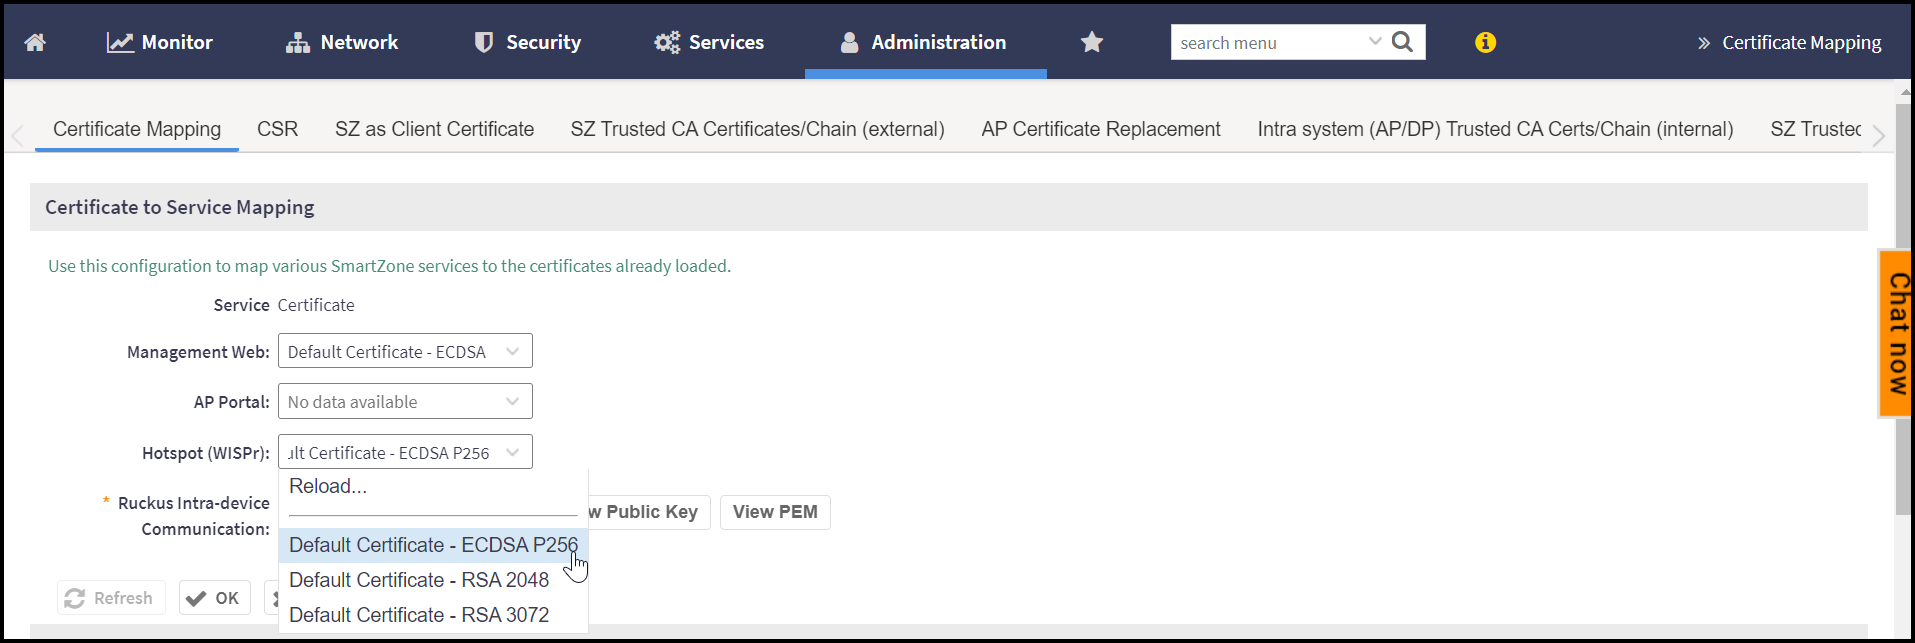
- Hotspot (WISPr): SmartZone re-directs the login portal to connected user (via web browser) for authentication.
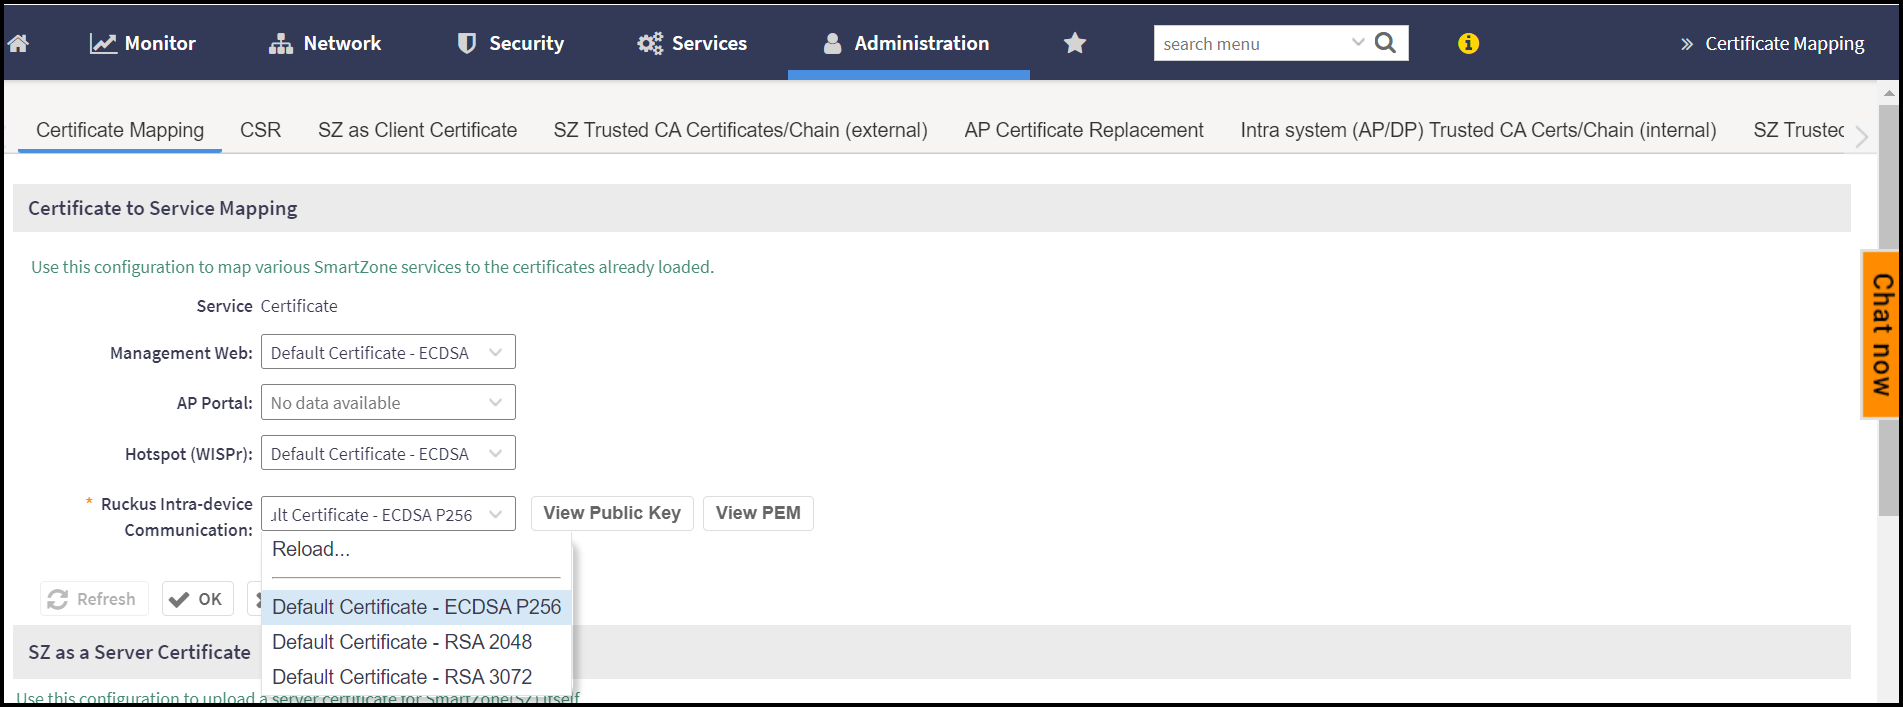
- Ruckus Intra-device Communications: SmartZone uses 2K/3K based certificates to map the services when AP/ICX joins the SSH/TLS Key Enhance Mode enabled zone/switch group.
- You view the new ECDSA certificates in the Certificate to Service Mapping section.
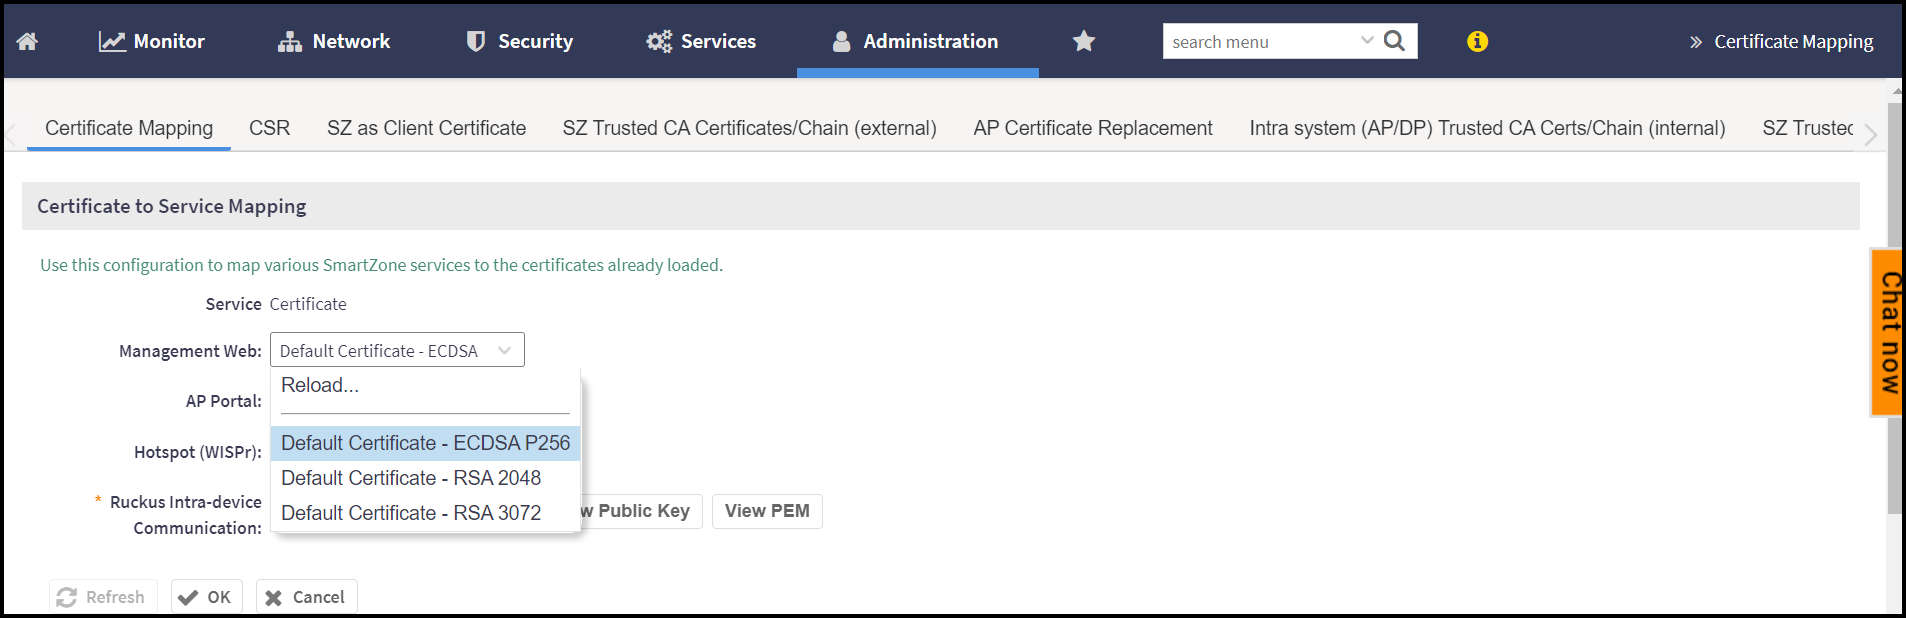
- Click the drop-down menu and
select the pre-loaded certificate to map various SmartZone services.
- ECDSA P256: This supports the signing of data with Elliptic Curve methods. The signing and verification is performed using P256 method. The calculation is hash of the message (h), public key (QA) and private key (dA).
- RSA 2048: This is an asymmetric encryption. Each side has a public and private key. The default 2K certificate is renamed as RSA 2048.
- RSA 3072: This is again an asymmetric encryption. RSA can work with keys of different keys of length.
- Select the certificates and click OK and the settings are mapped to various SmartZone services.