Creating Account Security
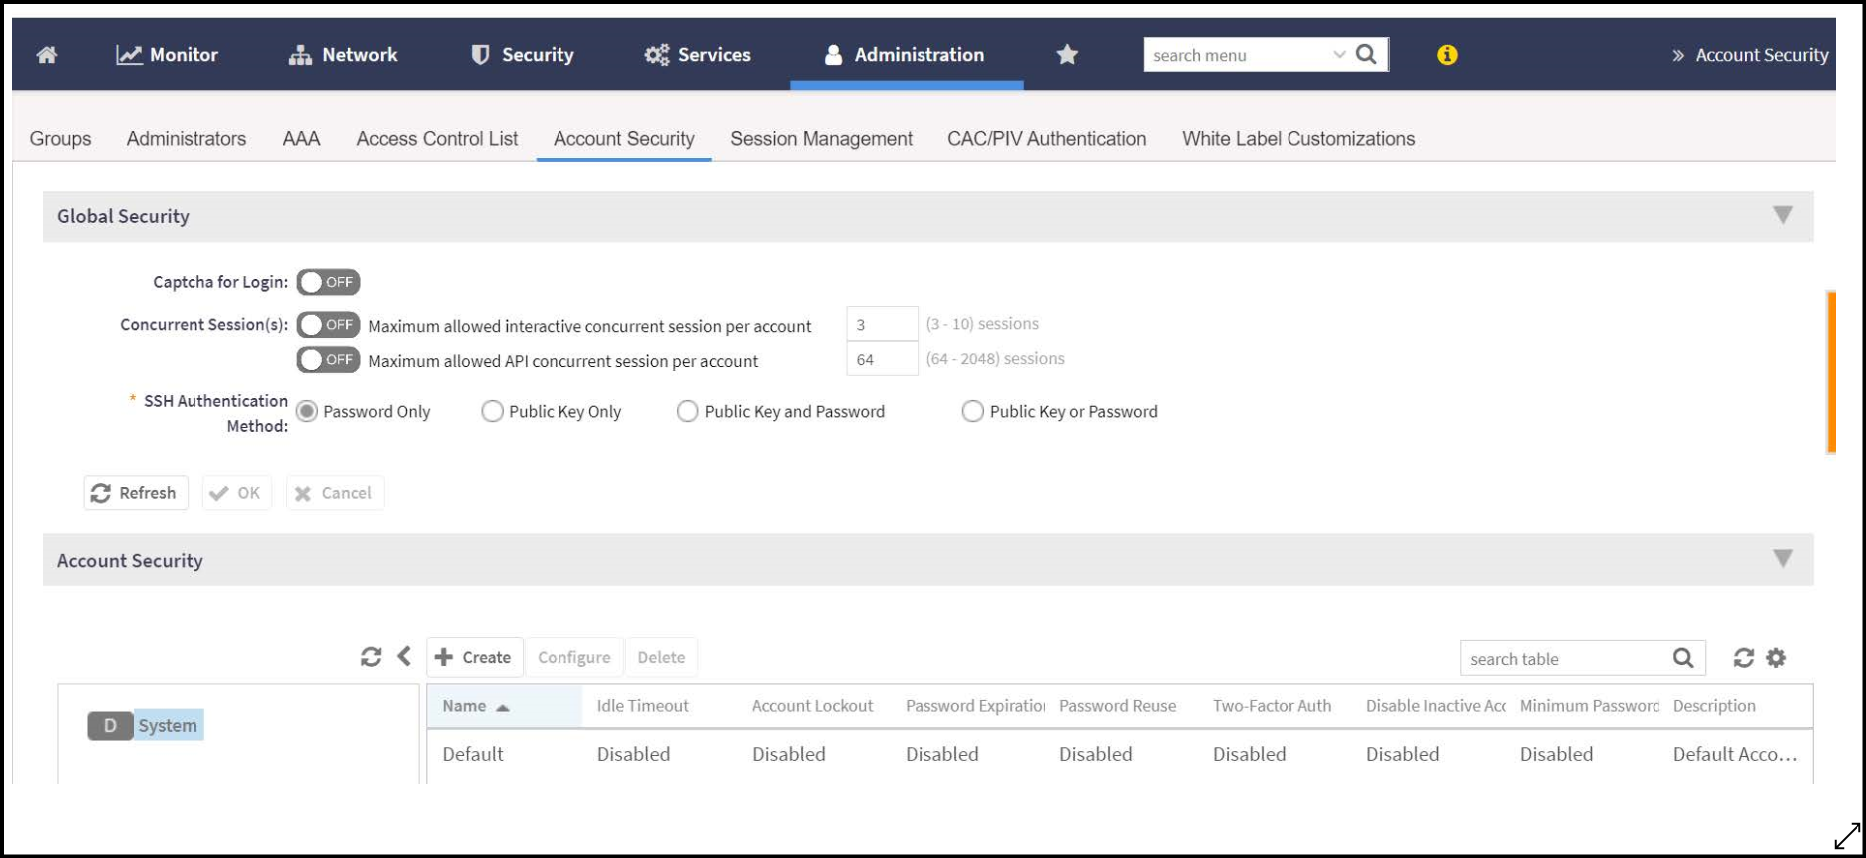
- Go to .
- Select the Account Security tab.
- From Global Security, configure the following:
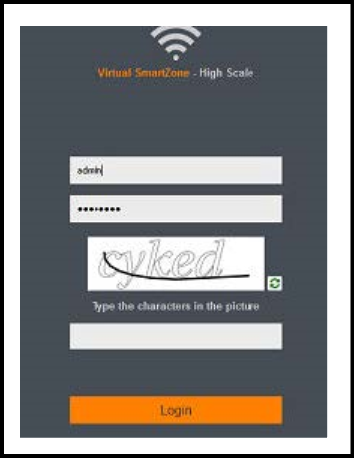
- Captcha for Login: select the option to enable Captcha for log in. The captcha feature provides additional security to ensure a human is signing into the account, and not a robot. If this feature is enabled; when you log into the web interface, the captcha characters are displayed in the login page as shown in the following example. Type the characters as shown in the captcha picture and log in. The characters in the captcha image are case sensitive and can be refreshed if not clear.
- Concurrent sessions: Click the required options and enter the number of sessions allowed:
- Click OK.
- From Account Security, click Create.
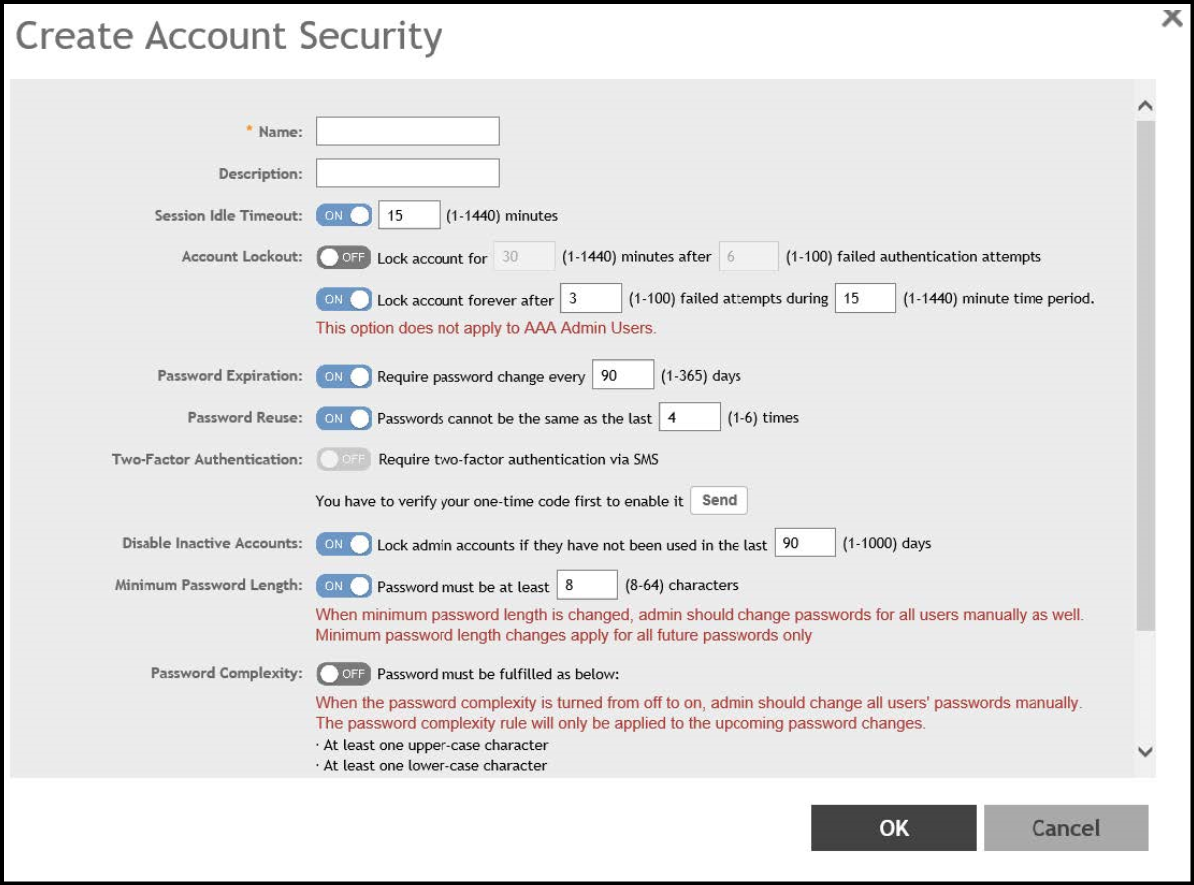
- Configure the following:
- Name: Type the name of the security profile that you want to create.
- Description: Provide a short description for the profile.
-
5.0 UpdateSession Idle Timeout: Click the button and enter the timeout duration in minutes.
- Account Lockout: You can configure the security profile to lock the account based
on the duration of the session or number of failed attempts to access the account.
Provide the values as necessary. Enable and configure one of the following:
5.1.2 update - reused across platforms
- Enter the account lockout time and number of failed authentication attempts.
- Enter the number of failed attempts after which the account is locked and the corresponding time period. After three unsuccessful login attempts in a time interval of 15 minutes, the account is locked and must be released by an Administrator.
- Password Expiration: Click the button and type the
number of days for which the account's password will be valid. After the
configured number of days, the password will expire and render the
account inaccessible. You must change the password before the expiration
day to have continued access to the account. By default, the password is
valid for a period of 90 days. It can be configured for validity from a
minimum of 1 day, to a maximum of 365 days.
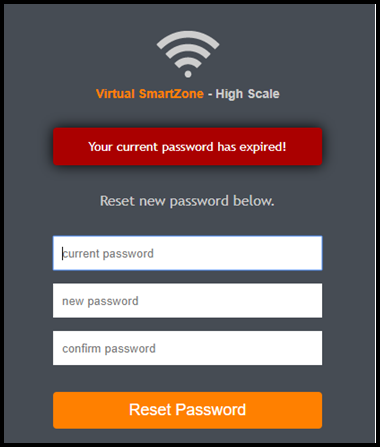
If your password has expired, you are prompted to change or reset your password as soon as you log in. Reset the password as shown in the figure.
- Password Reuse: Prevents the reuse of passwords. Click the button to enable this option. By default, the value is 4 (last 4 passwords cannot be reused).
-
5.0 UpdateDisable Inactive Accounts: Locks the admin user IDs that are inactive for the specified period of time. Click the button and specify the number of days.
-
5.1.2 UpdateMinimum Password Length: Indicates the minimum number of characters required for a password. If there is a change in the number of characters, the Admin must manually change the passwords for all users. Enter the minimum number of characters required for a password.
- Password Complexity: Ensures that the password applies the following rules: Select the appropriate options.
- Minimum Password Lifetime: Ensures that the password is not changed twice within a period of 24 hours. Select the option.
- Click OK to submit the security profile/form.
With new enhancements to account security, SmartZone has a complete feature set to make PCI compliance very simple and straightforward. In addition to local PCI enforcement settings, SmartZone also integrates with SCI for reporting and analytics. SCI version 5.0 and later supports a PCI compliance report, which is based on the relevant PCI-related configuration settings throughout SmartZone. To facilitate the SmartCell Insight PCI report, the SmartZone is capable of sending the following information to SCI:
- Configuration messages as separated GPB messages
- WLAN configuration
- Default configuration changes
- Controller information that identifies the controller model
- Encryption details of communication, for example: CLI, SSH, telnet, Web, API
- Inactive user IDs and session timeout
- Authentication mechanism enforced on user IDs
- Enforcement of password
- Supported mechanism on SZ that can be provided to SCI
- User IDs that are locked after failed attempts
- Authentication credentials that are unreadable and encrypted during transmission
- Enforcement of password standards
- Disallowing duplicate password feature is enabled
- If rogue AP detection is enabled on each AP
To learn more about SCI and the PCI compliance report it provides, check the product page (https://www.ruckuswireless.com/products/smart-wireless-services/analytics) and documentation on the RUCKUS support page (https://support.ruckuswireless.com).