Configuring SZ Admin AAA Servers
To add and manage AAA servers that the controller can use to authenticate users, complete the following steps.
- Select .
- From AP AAA Servers, click Create.
- Enter the AAA server name.
- For Type, select the type of AAA server to authenticate users:
-
5.1 Update - reused across platformsFor Realm, enter the realm or service.Multiple realms or services are supported. Separate multiple realms or services with a comma.Note: Because the user login format (User Account + @ + Realm) includes a special character, the at symbol (@), the user account must not include the at symbol (@) separately on the AAA server.
- Enable
Default Role Mapping.
You can select auto-mapping for the system to automatically map between the AAA and SZ accounts.
If Default Role Mapping is disabled, the AAA administrator must be mapped to a local SZ Admin user with matching AAA attributes for the RADIUS, TACACS+, Active Directory, or LDAP servers.
5.1.1 update - reused across platforms- On a RADIUS server, the user data can use the VSA Ruckus-WSG-User attribute with a value depending on the SZ users or permissions you want the RADIUS user to map.
- On a TACACS+ server, the user data can use the user-name attribute with the user1, user2, or user3 value depending on the SZ users or permissions you want the TACACS+ user to map.
- On an Active Directory or LDAP
server, the user data can belong to the group cn=Ruckus-WSG-User-SZAdminName (for example, cn=Ruckus-WSG-User-User1, depending on the SZ users or
permissions you want the Active Directory or LDAP user to map.
5.2 Update on the Active Directory bullet above.
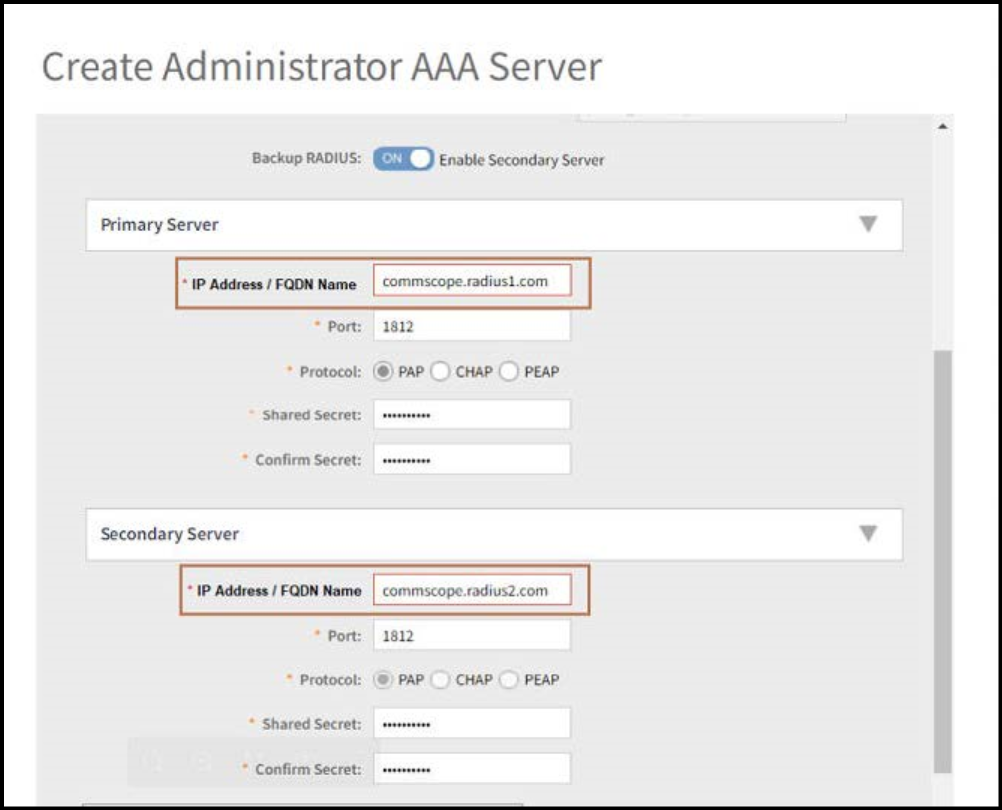
- For Backup RADIUS, select Enable Secondary Server if a secondary RADIUS server exists on the network. Refer to step 9 for configuration settings.
- Under
Primary Server, configure the settings of the primary AAA server.
- IP Address or FQDN
: Enter the IP address or Fully Qualified Domain Name (FQDN)
of the AAA server.
Note: The FQDN option can be configured only for the RADIUS server.
- Port: Enter the UDP port that the RADIUS server is using. The default port is 1812.
- Protocol:
Select the PAP or CHAP or
PEAP protocol.
Note: For the PEAP and PAP protocols, you must configure the Trusted CA certificate to support PEAP and EAP connection.
- Shared Secret: Enter the shared secret.
- Confirm Secret: Re-enter the shared secret to confirm.
- Windows Domain name: Enter the domain name for the Windows server.
- Base Domain Name: Enter the name of the base domain.
- Admin Domain Name: Enter the domain name for the administrator.
- Admin Password: Enter the administrator password.
- Confirm New Password: Re-enter the password to confirm.
- Key Attribute: Enter the key attribute, such as UID.
- Search Filter: Enter a filter by which you want to search, such as objectClass=*.
For Active Directory, configure the settings for the Proxy Agent.
- IP Address or FQDN
: Enter the IP address or Fully Qualified Domain Name (FQDN)
of the AAA server.
- Under
Secondary Server, configure the settings of the secondary RADIUS server.
- IP Address: Enter the IP address of the AAA server.
- IP Address or
FQDN: Enter the IP address or Fully Qualified Domain
Name (FQDN) of the AAA server.
Note: The FQDN option can be configured only for the RADIUS and Secondary server.
- Port: Enter the UDP port that the RADIUS server is using. The default port is 1812.
- Protocol:
Select the PAP or CHAP or
PEAP protocol.
Note: For the PEAP and PAP protocols, you must configure the Trusted CA certificate to support PEAP and EAP connection respectively.
- Shared Secret: Enter the shared secret.
- Confirm Secret: Re-enter the shared secret to confirm.
-
5.1.1 update - reused across platformsUnder Failover Policy at NAS, configure the settings of the secondary RADIUS server.
- Request Timeout: Enter the timeout period in seconds. After the timeout period, an expected RADIUS response message is considered to have failed.
- Max Number of Retries: Enter the number of failed connection attempts. After the maximum number of attempts, the controller tries to connect to the backup RADIUS server.
-
5.1.2 update - reused across platformsReconnect Primary: Enter the time in minutes, after that the controller connects to the primary server.
- Click OK.