AP Validate SmartZone Controller
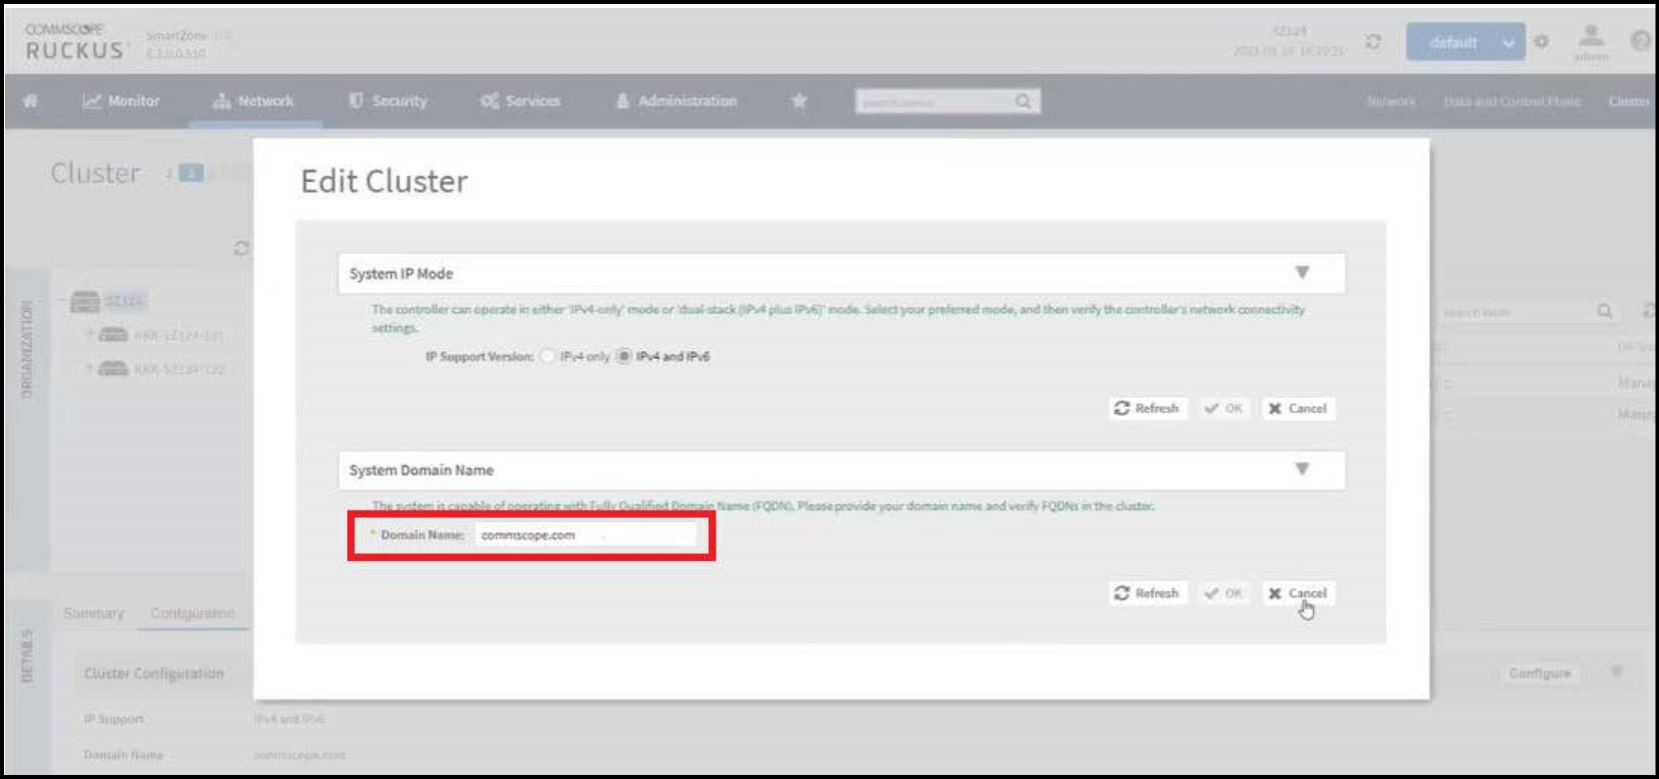
Smart Zone can edit the Domain name after the installation
Smart Zone can show the Infra (Communicator) certificate's pem data.
When Server validation is enabled, SZ will push the configurations to AP.
Follow the below steps for the validation of server certificates:
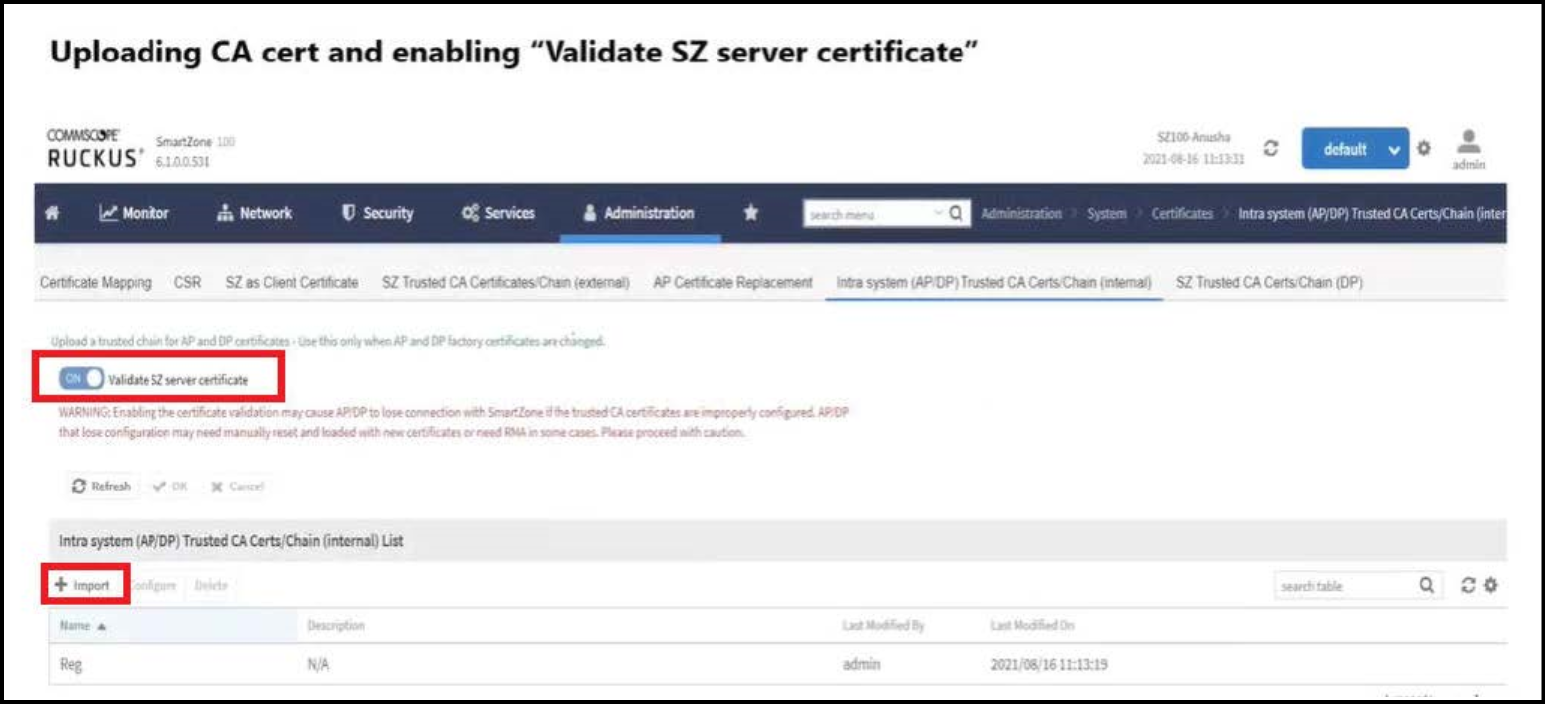
- Go to Administration> Intra System (AP/DP) Trusted Certs/Chain (Internal).
- Click "Import" to add valid trusted CA certificate/chain as per the figure above.
- Enable the "Validate Server certificate".
- The configuration will be pushed to SCG managed AP's.
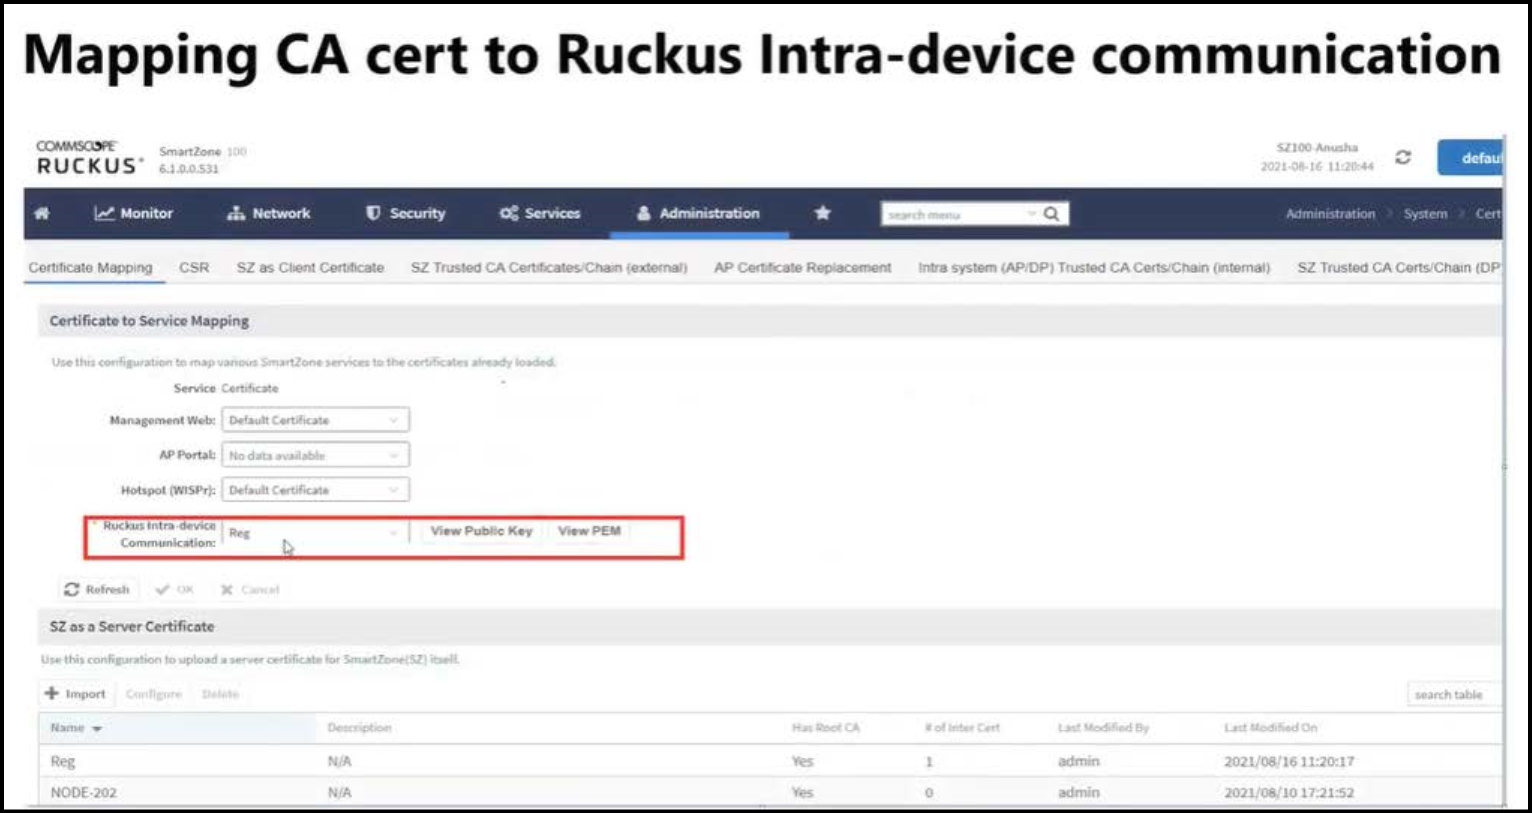
- Upload the certificate in the Administration>Certificate Mapping> SZ as a Certificate.
- Map Server certificate to Ruckus Intra-Device Communication also change the below heading from Mapping CA Cert to Mapping Server Certificate.
- The certificate will be validated when AP connects to SCG.
- Configuration Method:
Part 1:Using Public Key
The certificate mapping is done in Administration>System>Certificates> Certificate Mapping.
-
Copy the public key from the above marked "View Public key", Enter the Public key in AP CLI using command “ set scg pubkey <publickey> “.
-
Enable the server cert validation in AP using command “set scg server-validate enable”.
- If public key matches The AP will be listed in staging
zone.
Success message : ssl_cert_verify_callback:294 SSL Verification OK.
-
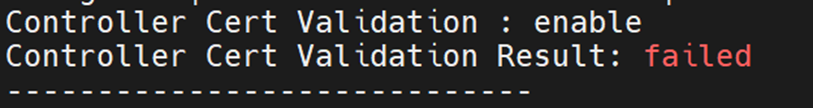
If public key is not matching error message,
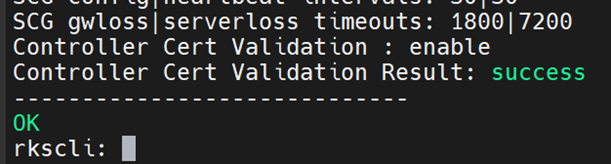
In Ap CLI execute command “get scg “.
SSL certificate verification failed.
ERROR: check_http_status:542 Curl error: Peer certificate cannot be authenticated with given CA certificates.".
Part 2: Using CA Cert
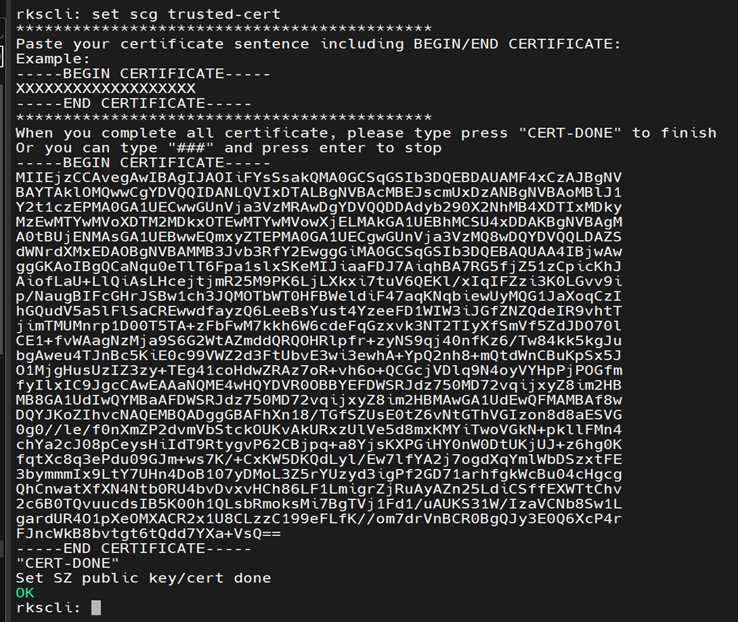
-
In AP CLI configure ca cert using command “set scg trusted-cert “.
-
Enable the server cert validation in AP using command “set scg server-validate enable”.
-
If CA certificate is validated the AP will be listed in staging zone.
-
- Domain name configuration:
For release 6.1fresh installation of domain name is mandatory to support AP/DP validate the controller feature. FQDN (Fully Qualified Domain Name) consists of domain nameand the host name. The below table is an example of cluster deployment based on thedomain name in a cluster deployment.
Cluster Deployment
Cluster Domain Name Node# Host Name FQDN ruckus.com Master Master master.ruckus.com Slave1 Slave1 slave1.ruckus.com Slave2 Slave2 slave2.ruckus.com Slave3 Slave3 slave3.ruckus.com Domain name can be modified after installation by navigating to .