Working with SmartZone
Configuring the Authentication Services and Creating a WLAN
Configure an authentication server in the controller to be used as a RADIUS server within the IEEE 802.1X WLAN settings. Wireless clients attempting to connect to the WLAN will be prompted for username and password credentials that will be checked against the Active Directory (AD) by the Network Policy Server (NPS).
Complete the following steps in your SmartZone controller UI to configure a WLAN with IEEE 802.1X authentication that uses an NPS as the RADIUS server:
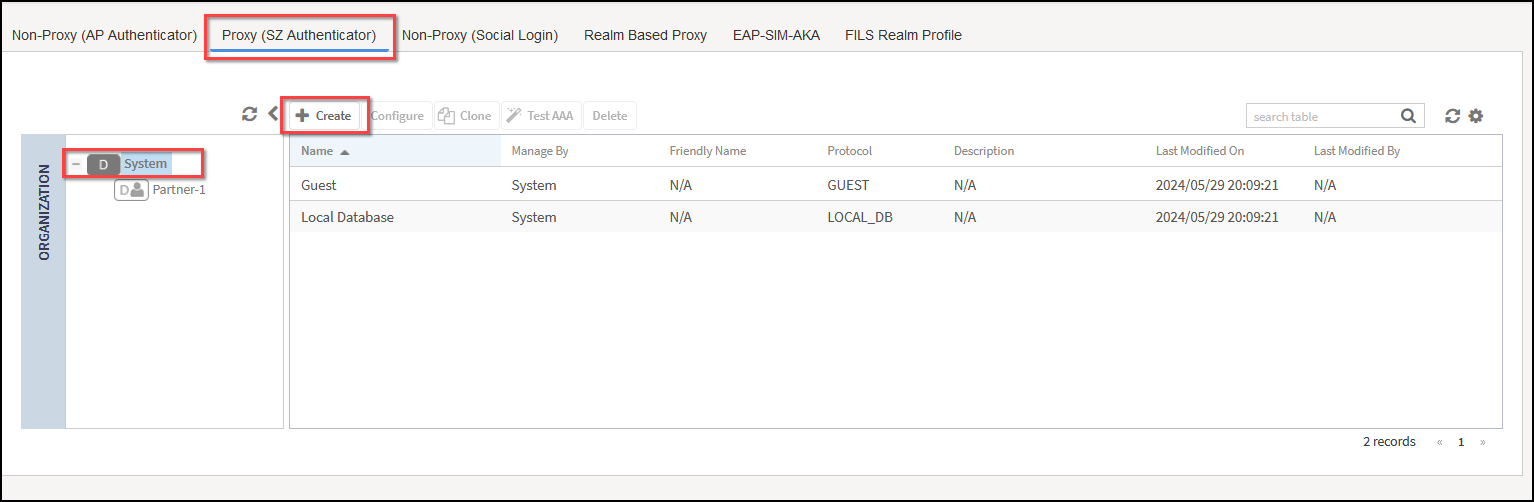
- Create the proxy
authentication server.
- Navigate to .
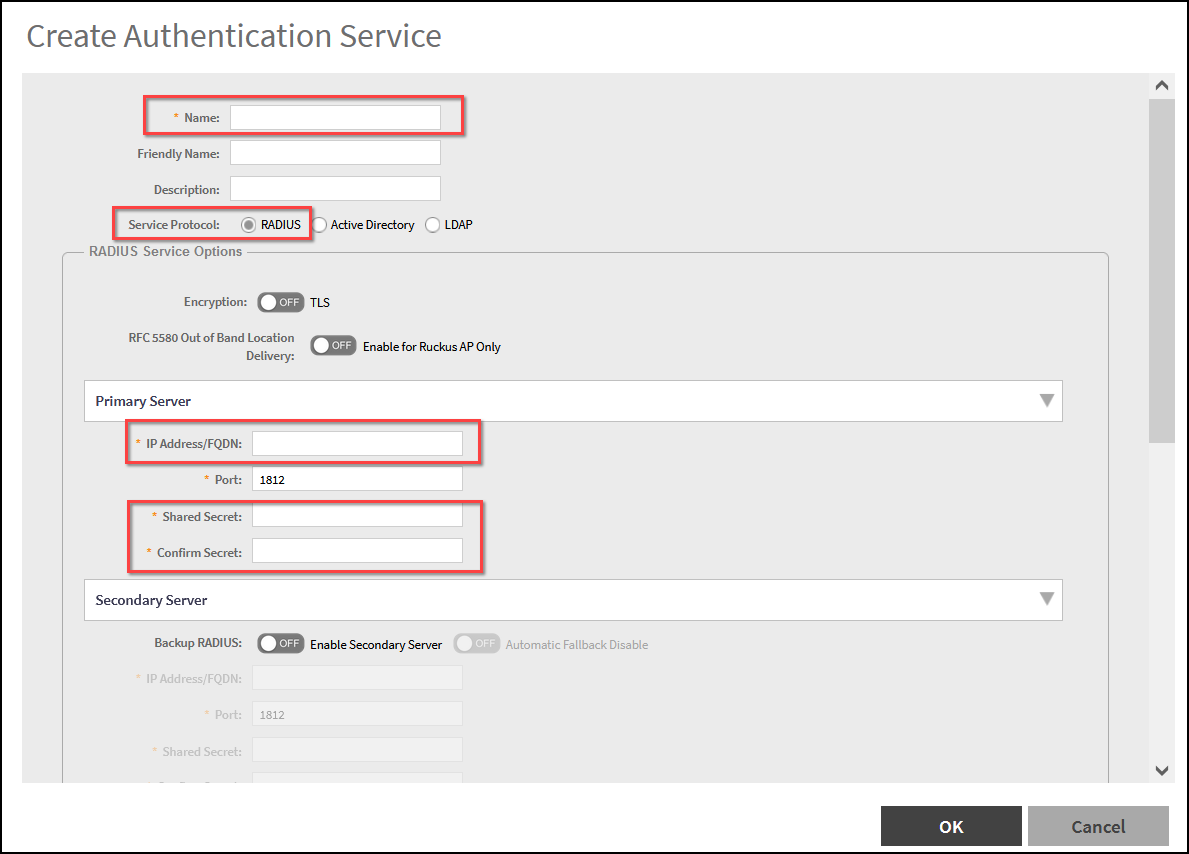
- Click Create to create a new authentication service.
- Type a name.
- For Service Protocol select RADIUS.
- Type the IP address of the NPS.
- Type the shared secret that you entered when you configured the RADIUS client on your NPS (as descibed in Configuring the NPS for IEEE 802.1X Wireless Connections .
- Keep default
selections for the remaining options and click OK.The authentication service is created.
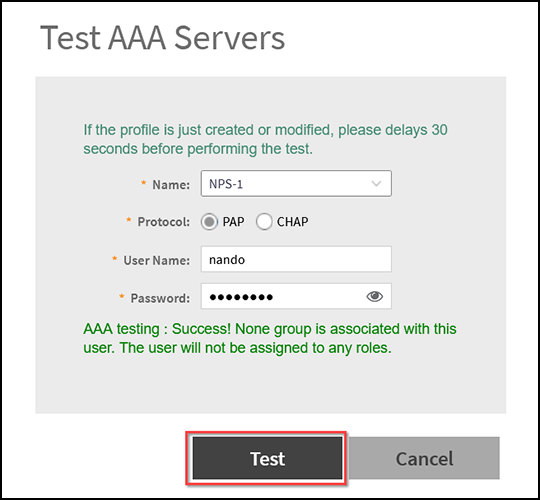
- Test the authentication
service. Use the AAA test option to verify that the controller can contact
the NPS and the authentication settings match the network policies. Select
from the list the authentication service you created and click Test
AAA.Configure the following parameters.
- In the Name field, keep the default selection.
- For Protocol, select PAP.
- For User Name, type the logon name as configured in AD.
- For Password, type the password configured in AD for this user.
- Click Test.
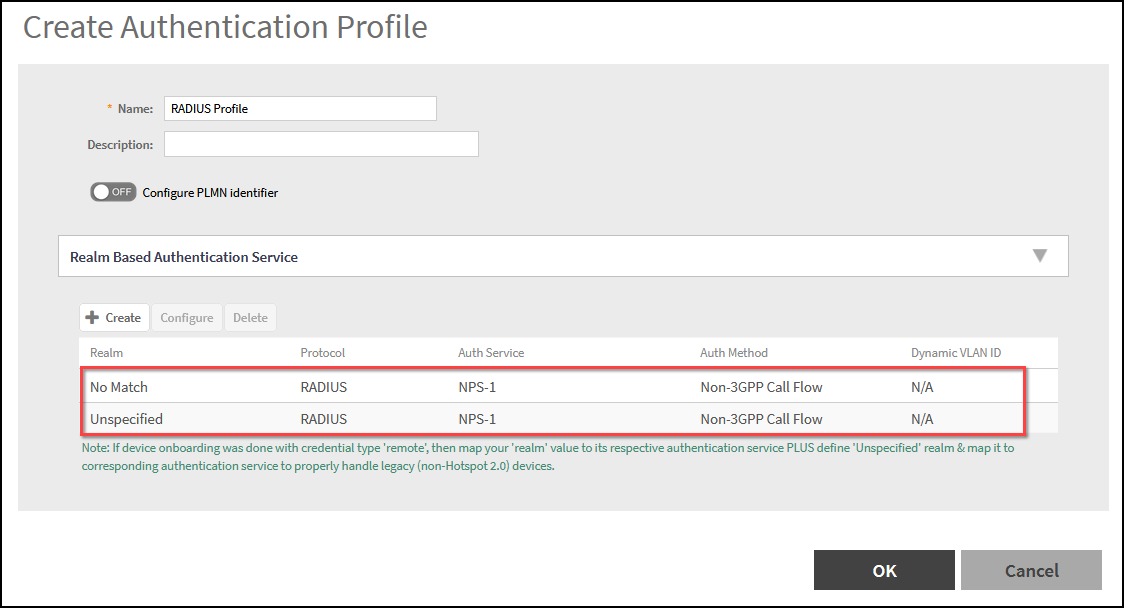
- Create a realm-based proxy authentication profile. Navigate to and click Create.
- Double-click the No Match row to edit it using the following settings:
- Double-click the Unspecified row to edit it using the following settings:
- Click
OK.The realm-based proxy authentication profile is created.
- Configure a WLAN for 802.1X
authentication. Navigate to . Select the zone where you want to create the WLAN. Click
Create.
- Type a name and, optionally, a description.
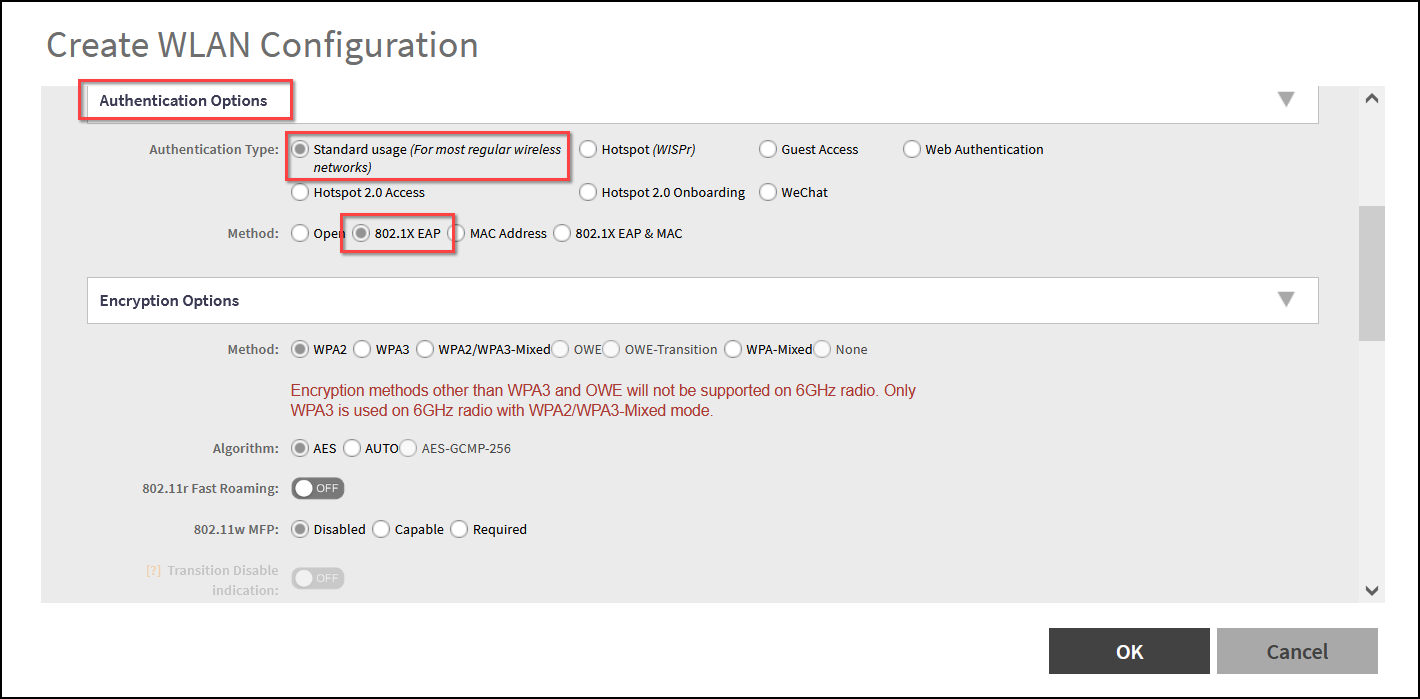
- For Authentication Type, select Standard usage (For most regular wireless networks).
- For Method, select 802.1X EAP.
- Scroll down to Authentication & Accounting Service.
- Toggle the Use the controller as proxy option to enable.
- Select from the list the realm-based proxy authentication profile created in step 3.
- Click OK.
Testing the Configuration
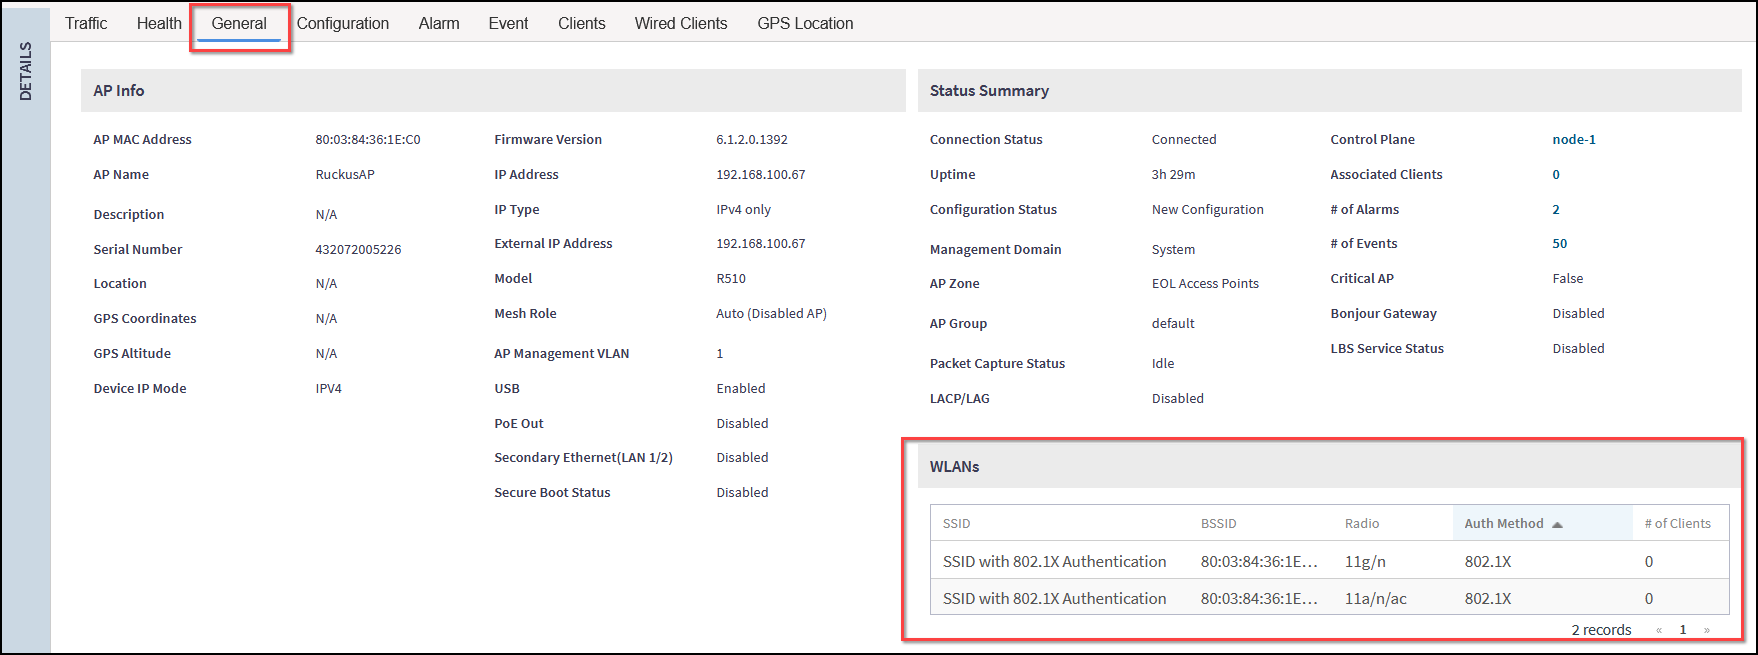
- Verify from SmartZone that AP is broadcasting the SSID. Navigate to , locate and select the AP, then select the General tab. Scroll down to the WLANs section. The WLAN you created must be listed.
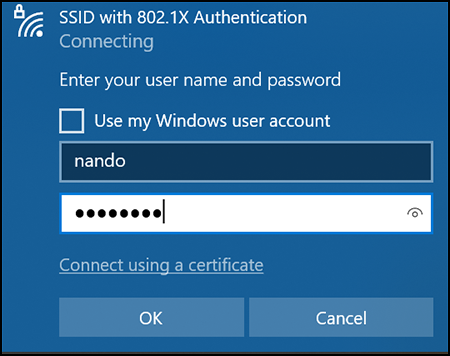
- Connect the testing client
to the SSID. Enter the credentials configured in AD when prompted for
username and password. Click OK. The
wireless client will connect to the SSID. Use the CMD command
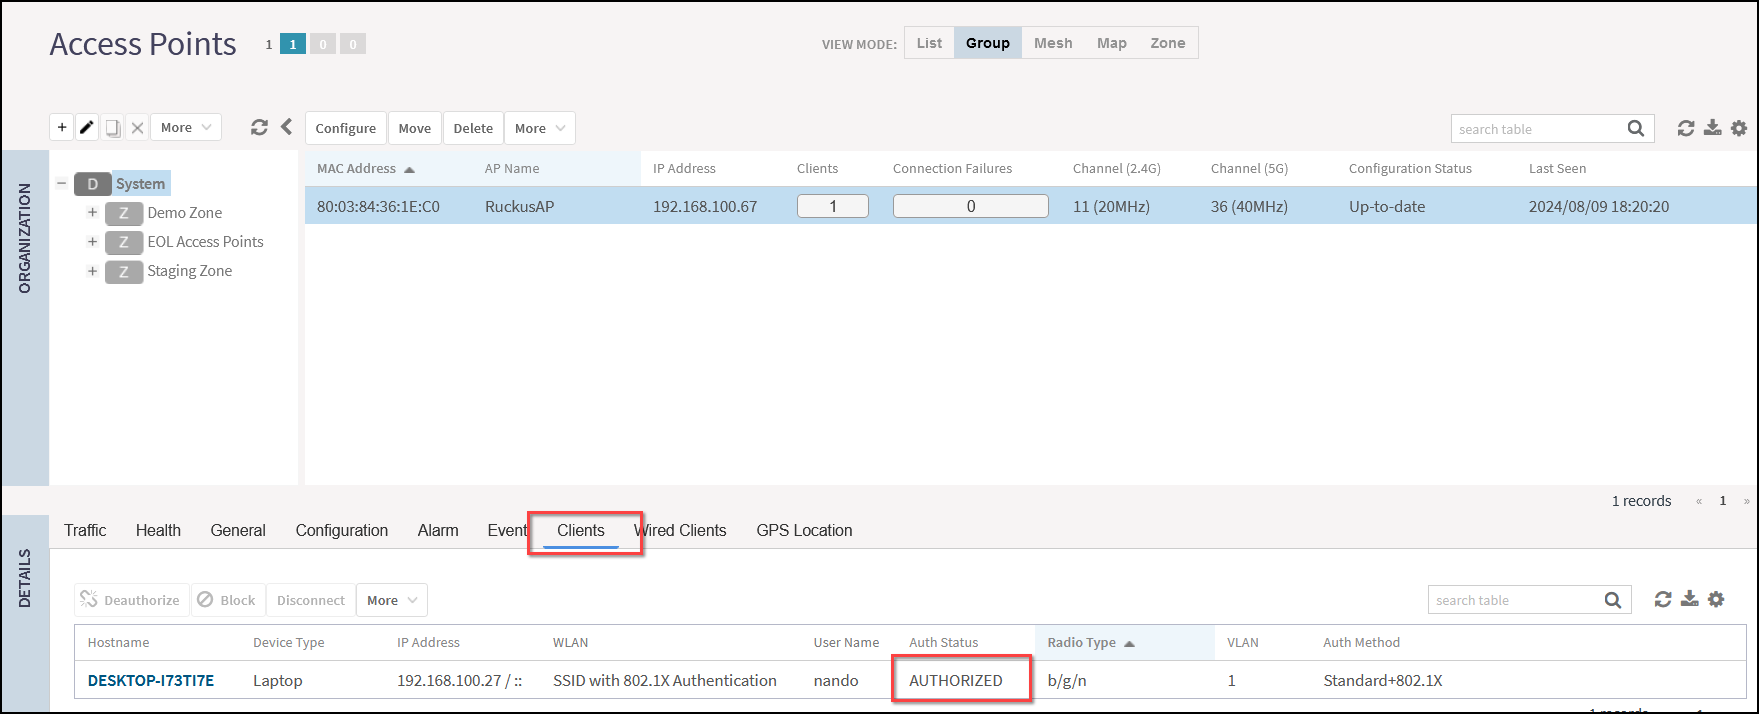
ipconfigto make sure the testing client got an IP address. - Verify from SmartZone that the client shows authorization status shows as AUTHORIZED. Navigate to , locate and select the AP and select the Clients tab. Locate the testing client. The authorization status should be listed.
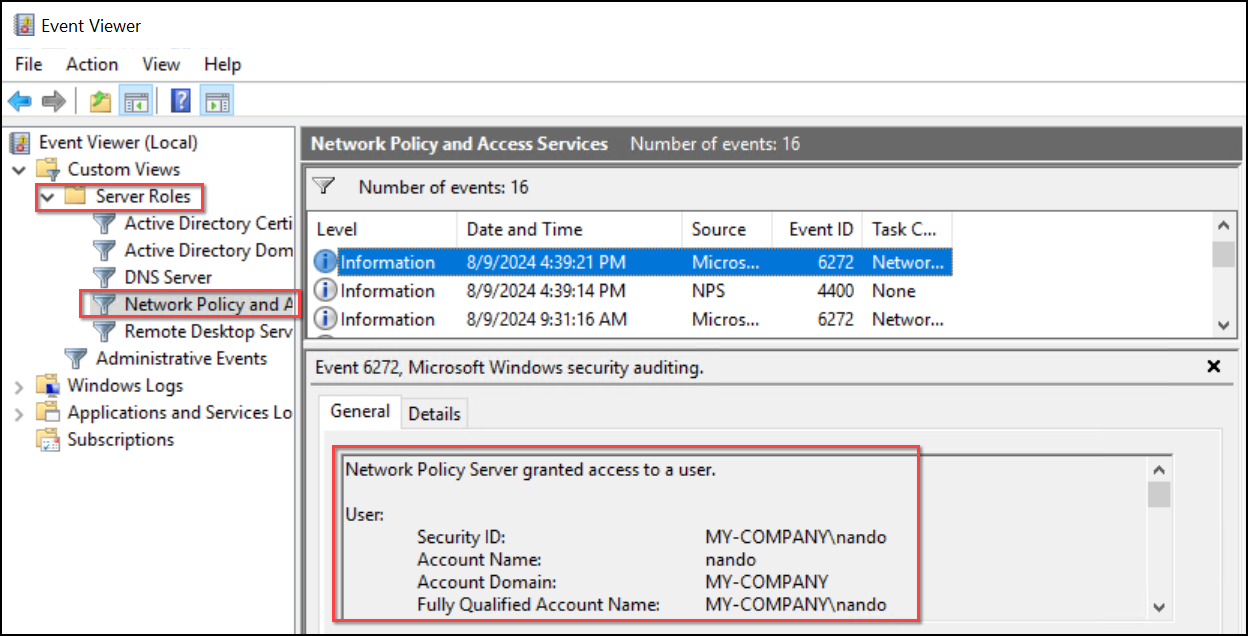
- Review the event logs in the NPS. In the Server Manager UI, click Tools in the upper-right corner and then select Event Viewer. In the Event Viewer, expand . Select the newest log to review the latest authentication details (which should correspond to the access authentication for your testing client).