Active Directory Configurations
Deploying AD Domain System and Creating AD Users and Groups
Deploy and configure the Active Directory Domain System (AD DS) feature in the same Windows Server to integrate AD services with the NPS. This way, you can grant or deny access to the network based on users and User Groups.
Complete the following steps to deploy the AD services in the Windows server.
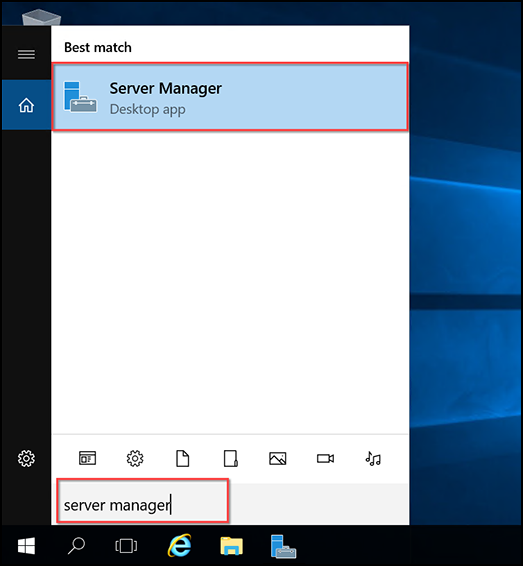
- Open the Server
Manager.Note: Type “server manager” in the search bar in the Windows Server to quickly find the Server Manager application.
- Add the AD DS role in the
Server Manager. In the Server Manager Dashboard, click Add roles
and features.
- In Before You Begin, click Next >.
- For the Installation Type, select Role-based or feature-based installation. Click Next >.
- For the Server Installation, keep the default selection, and click Next >.
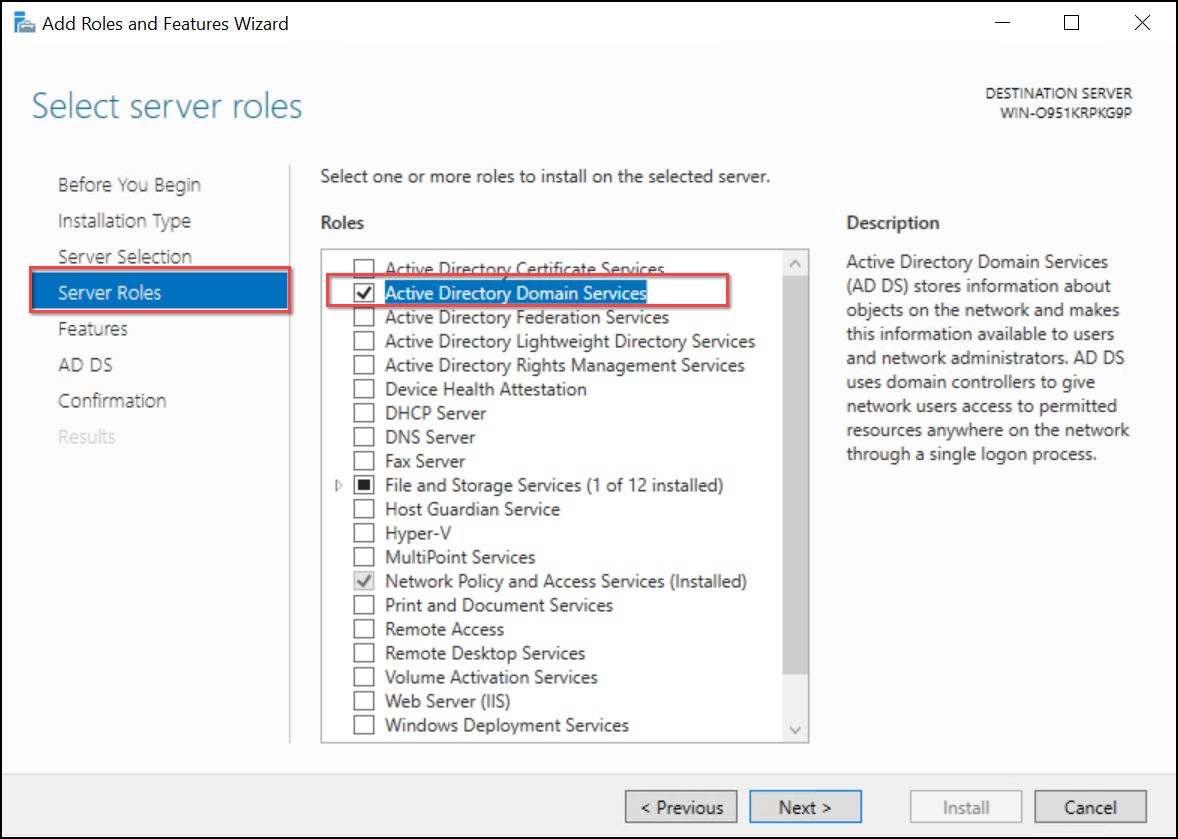
- For the Server Roles, select Active Directory Domain Services. Click Next >.
- In Features, keep the default selection, and click
Next
>.Note: The necessary features (directly related to the Server Roles you selected) are automatically selected and no additional features are required.
- In AD DS, click Next >.
- In Confirmation, click Install.
- Perform the AD DS
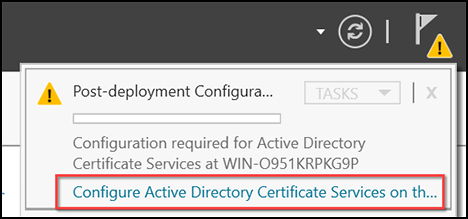
post-deployment configuration. Click the flag icon with the warning sign in
the upper-right corner in the Server Manager Dashboard to display the list
of pending tasks and click Promote this server to a
domain controller.
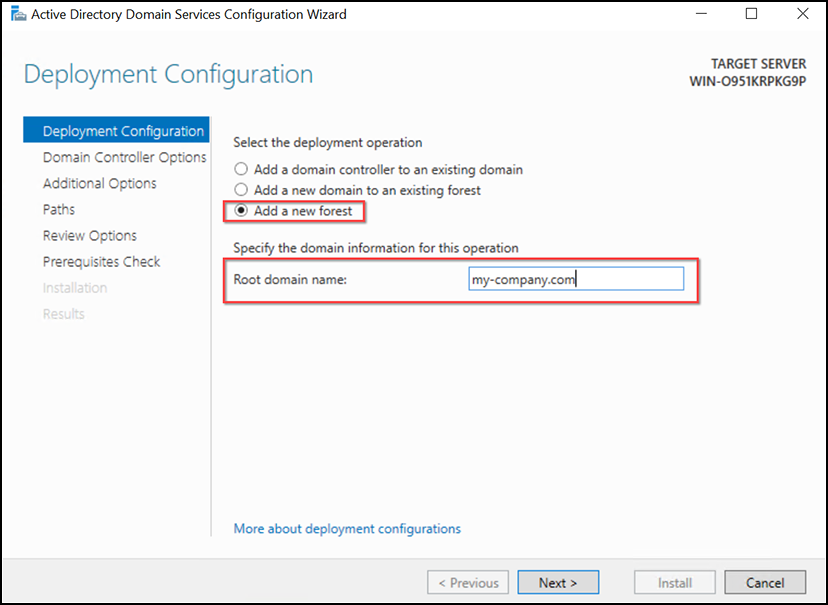
- In the Deployment Configuration tab, select Add a new forest and type the Root domain name you would like to assign to this new domain. Alternatively, you can select the option Add new domain to an existing forest, in case a forest already exists. Click Next>.
- In Domain Controller Options, type a password for Directory Services Restore Mode (DSRM). Click Next >.
- In the following tabs, keep the default selection, and click Next > until you get to the Prerequisites Check tab.
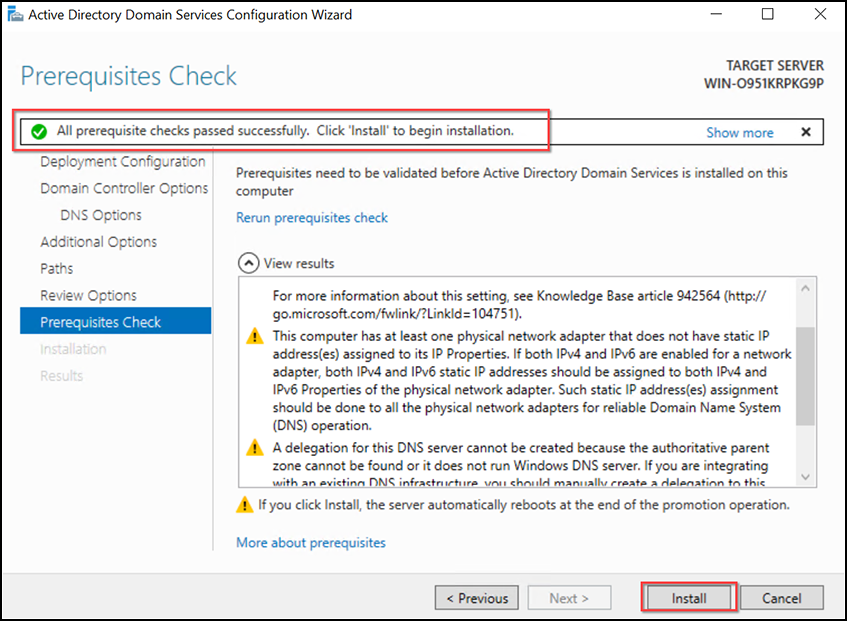
- In the Prerequisites
Check tab, ensure all prerequisite checks pass
successfully, then click Install to begin the installation.Note: If any of the prerequisite checks do not pass, address each issue by following the instructions provided in the configuration wizard.
- Log in using the newly configured domain credentials with the format Domain-Name\UserName.
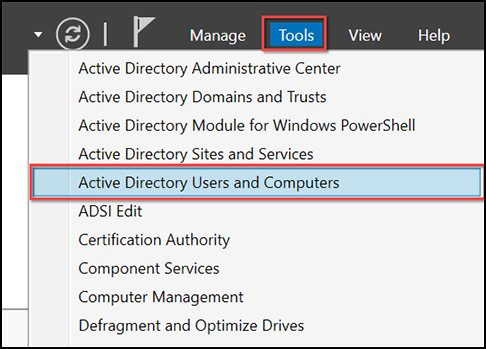
- Open Active Directory Users and Computers. Open the Server Manager and click .
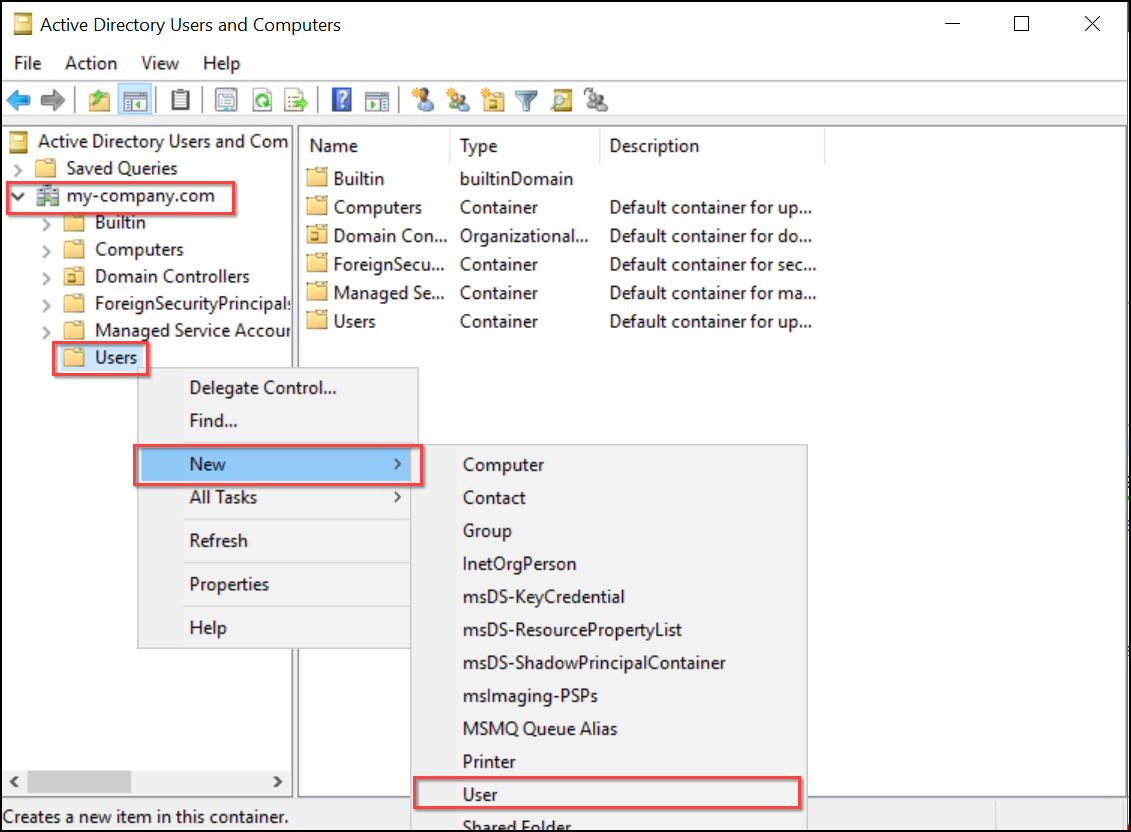
- Create a user. Expand the
domain name folder in the hierarchy, right-click the Users folder,
and select .
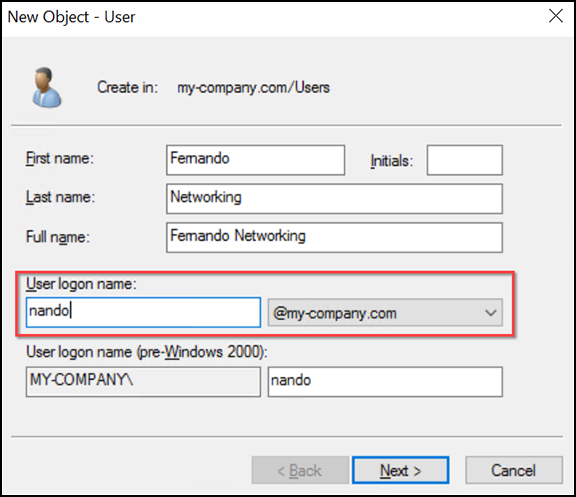
- Type the new user's first name, last name, and user logon name information in the corresponding fields. Click Next >.
- Type the password for this user and enable/disable the available password preferences according to your needs. Click Next >.
- Confirm the details
in the final step and click Finish.The user is created.
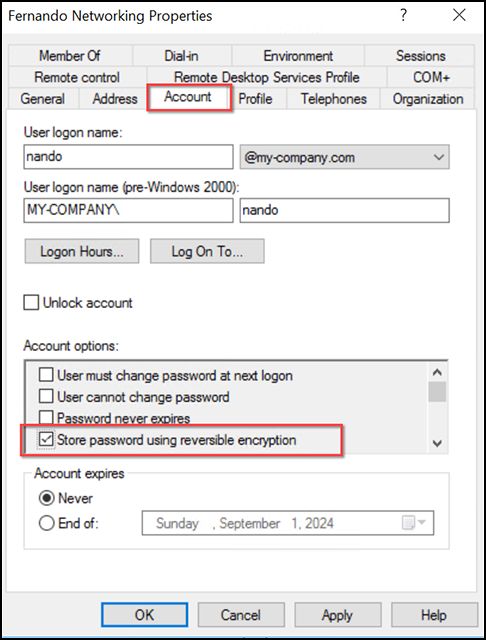
- Double-click the user you have just created to open the properties window of the user.
- In the Account tab, select Store password using reversible encryption and click OK.
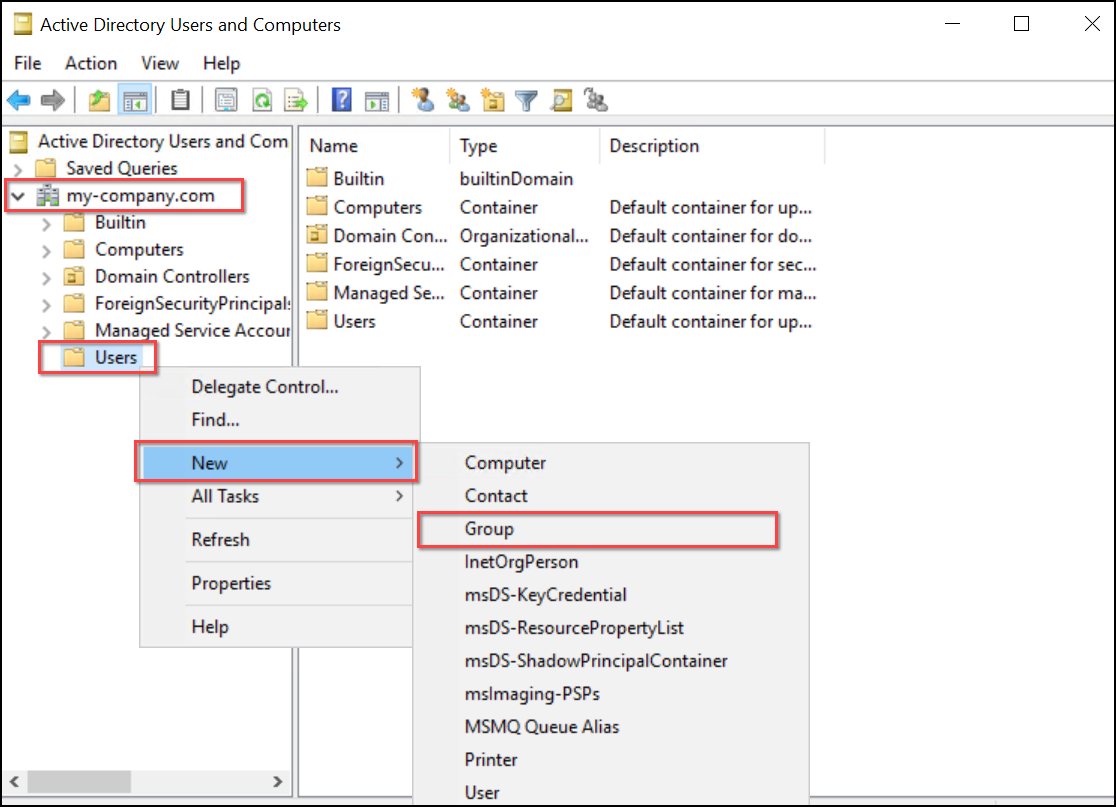
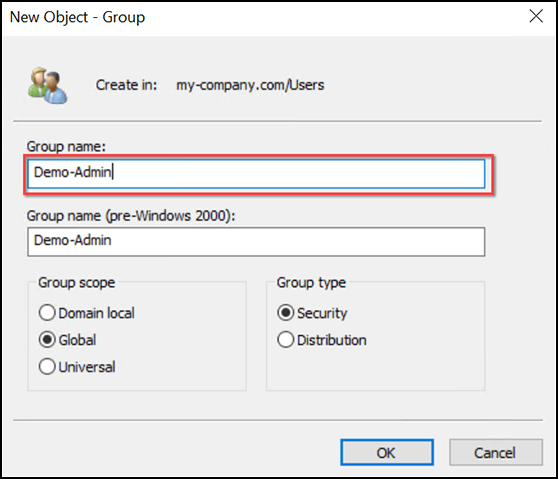
- Create a user group. Expand the domain name folder in the tree hierarchy, right-click the Users folder, and select .
- Add users to the User Group.
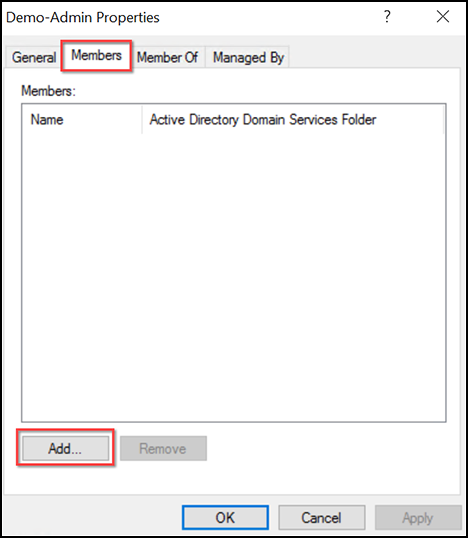
Double-click the User Group you have just created and navigate to the
Members tab.
- In the Members tab, click Add….
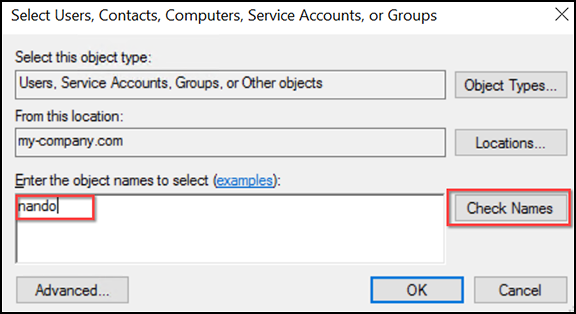
- Type the logon name
of the user in the Enter the object
names to select field. Click the Check
Names option to validate the object information.
Click OK.
The user is added to the members list of the group.
Note: When using the Check Names option, if the logon name you entered is correct, the object name information will auto complete, otherwise, a notification window will inform you that the object was not found. To ensure the user exists, you may alternatively add the user to a group by navigating to the user's Properties folder, click the Member Of tab, click Add..., and enter the desired Group name
- Click Apply and OK.
Deploying the AD Certification Authority
The IEEE 802.1X authentication protocol requires encrypted end-to-end communication. This is achieved through SSL certificates exchanged between the NPS server and the authenticator. Deploy an AD Certification Authority (AD CA) for the NPS to automatically get an SSL certificate assigned for the RADIUS services.
Complete the following steps to deploy the AD CA:
- Add the AD DS role in the
Server Manager. In the Server Manager Dashboard, click Add roles
and features.
- In Before You Begin, click Next >.
- For the Installation Type, select Role-based or feature-based installation. Click Next >.
- For the Server Installation, keep the default selection and click Next >.
- For the Server Roles, select Active Directory Certificate Services. Click Next >.
- In Features, keep the default selection and click Next >.
- In AD CS, click Next >.
- In Role Services, select Certification Authority, and click Next >.
- In Confirmation, click Install.The AD CS installation is completed. You can close the installation window.
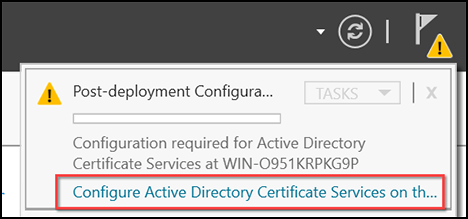
- Perform the AD CS
post-deployment configuration. Click the flag icon with the warning sign in
the upper-right corner in the Server Manager Dashboard to display the list
of pending tasks and click Configure Active
Directory Certificate Services on the destination
server.
- In Credentials, keep the default selection (which is the same as the credentials for the AD DS). Click Next >.
- In Role Services, select Certification Authority. Click Next >.
- In Setup Type, select Standalone CA. Click Next >.
- In CA Type, select Root CA. Click Next >.
- In Private Key, select Create a new private key. Click Next >.
- In Cryptography, select 2048 for the key length and SHA256 for the hash algorithm. Click Next >.
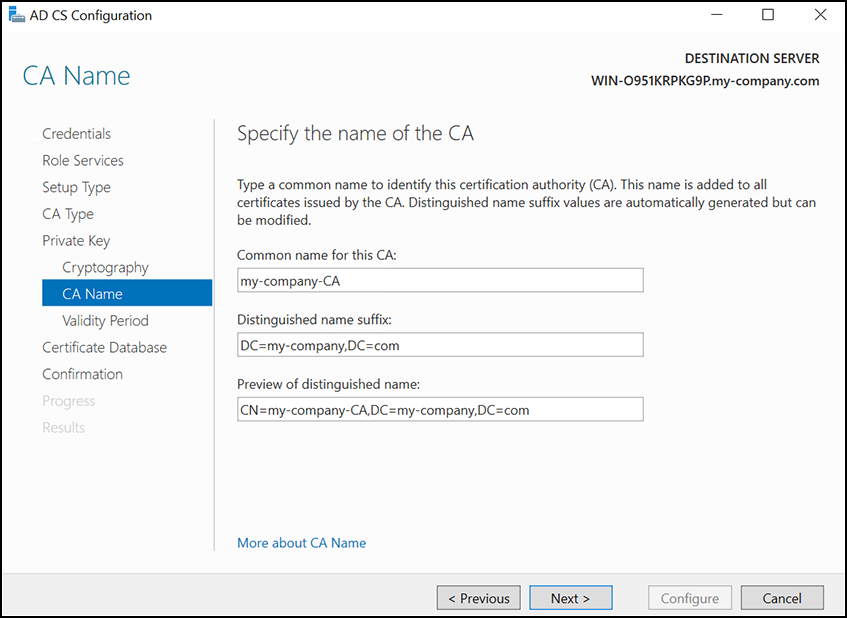
- In CA Name type the Common name for this CA, and keep the other fields with the default details. Click Next >.
- In Validity Period, select the validity period of your preference. Click Next >.
- In Certificate Database, keep the default selection. Click Next >.
- In Confirmation, click Configure. When the "Configuration succeeded" status appears, click Close to to close the wizard.