Configuring the NPS for IEEE 802.1X Wireless Connections
Complete the following steps to configure your Network Policy Server (NPS) with a set of default RADIUS policies to authenticate wireless clients based on AD groups membership that can be modified later:
- Configure RADIUS services for
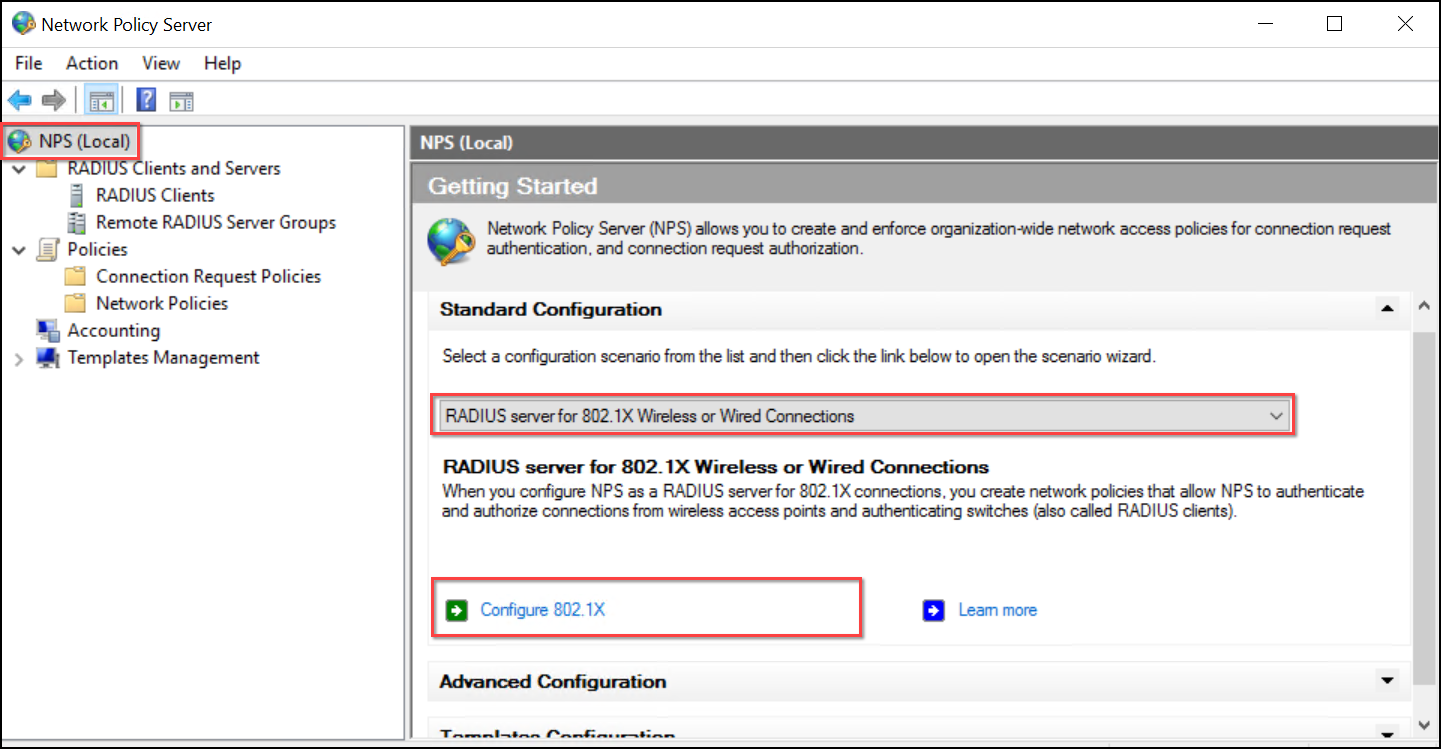
IEEE 802.1X for wireless connections. In the NPS console, in the left navigation
pane, click NPS
(Local). On the right pane, select RADIUS server for 802.1X
Wireless or Wired Connections and click Configure 802.1X
to configure 802.1X authentication settings.Attention: The Network Policy (NP) configured in this task uses AD User Groups as a condition. Make sure you have an existing AD User Group before starting your NP configuration. For instructions to create AD User Groups and users, refer to Active Directory Configurations.
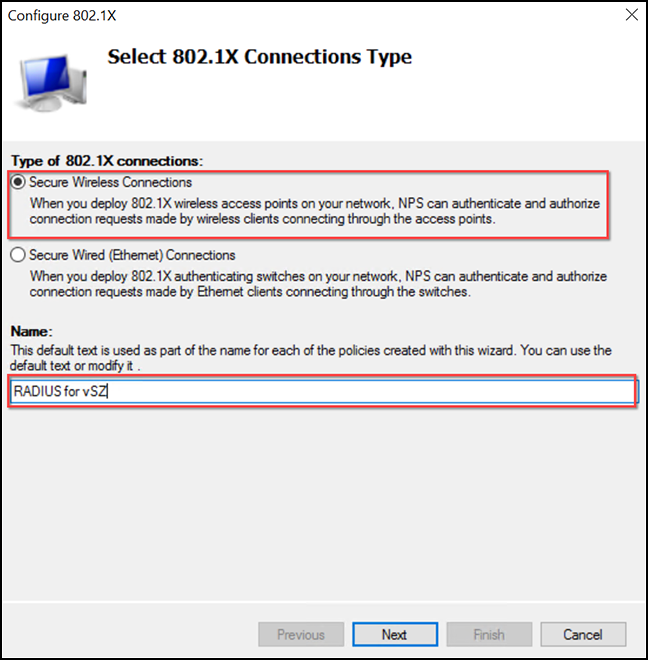
- In Select 802.1X Connections
Type, choose the connection type as Secure Wireless
Connections and type the name of the policy. Click Next.Note: By default, a Connection Request Policy (CRP) and a Network Policy (NP) will be created with the same name provided in this wizard.
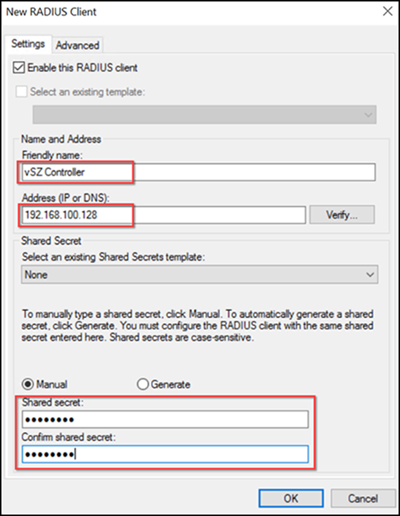
- In Specify 802.1X
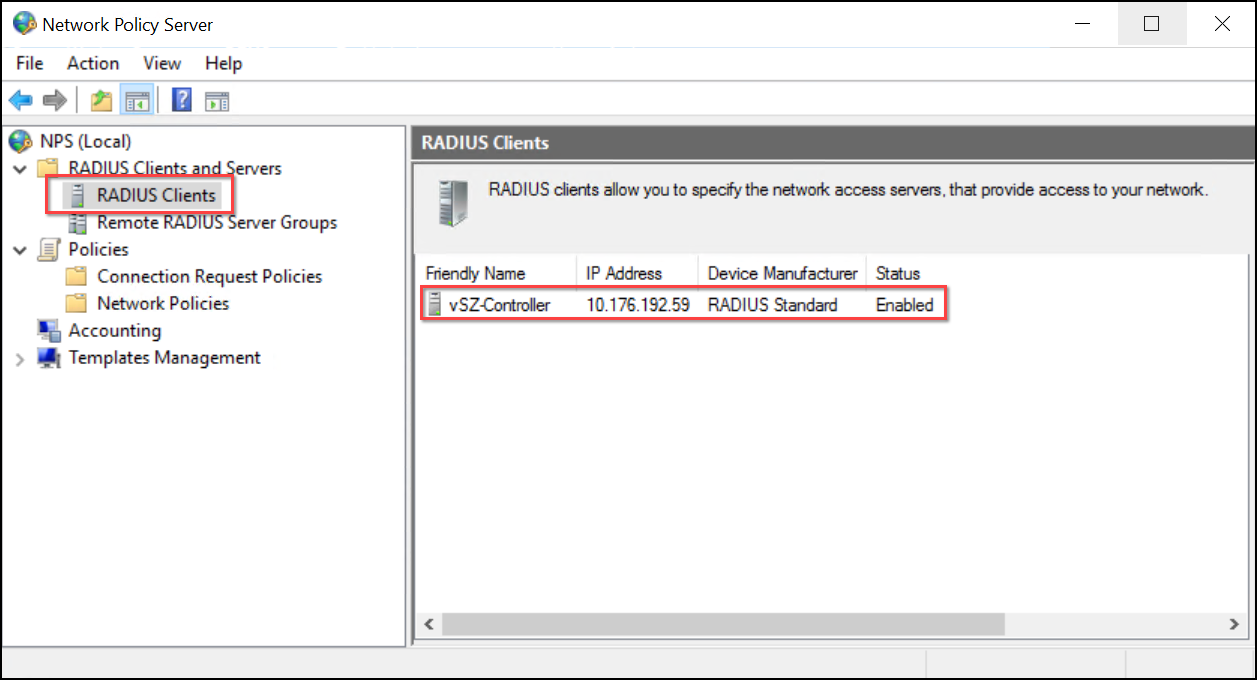
Switches, create a RADIUS Client.Note: The term RADIUS Client corresponds to the authenticator device; it could be the controller in proxy authentication mode, or it can be every access point in the network (in the case of non-proxy authentication).
- In Configure an Authentication Method select Microsoft Protected EAP (PEAP) from the list. Click Next.
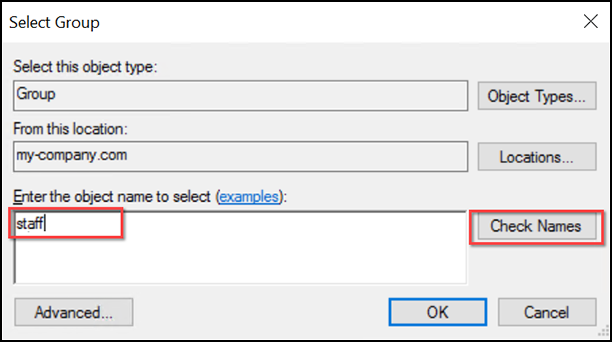
- In Specify User Groups click Add… to add an existing Active Directory (AD) group as a condition.
- In Configure Traffic Controls keep the default settings, and click Next.
- Review the configuration summary
and click Finish.You have successfully configured the NPS for 802.1X wireless connections and it is ready to authenticate any connection requests coming from the controller.
Modifying the Network Policy Conditions
The default NP created (as per the Configuring the NPS for 802.1X Wireless Connections ) has a condition to only grant access to users that belong to the specified user groups. Complete the following steps to modify that condition:
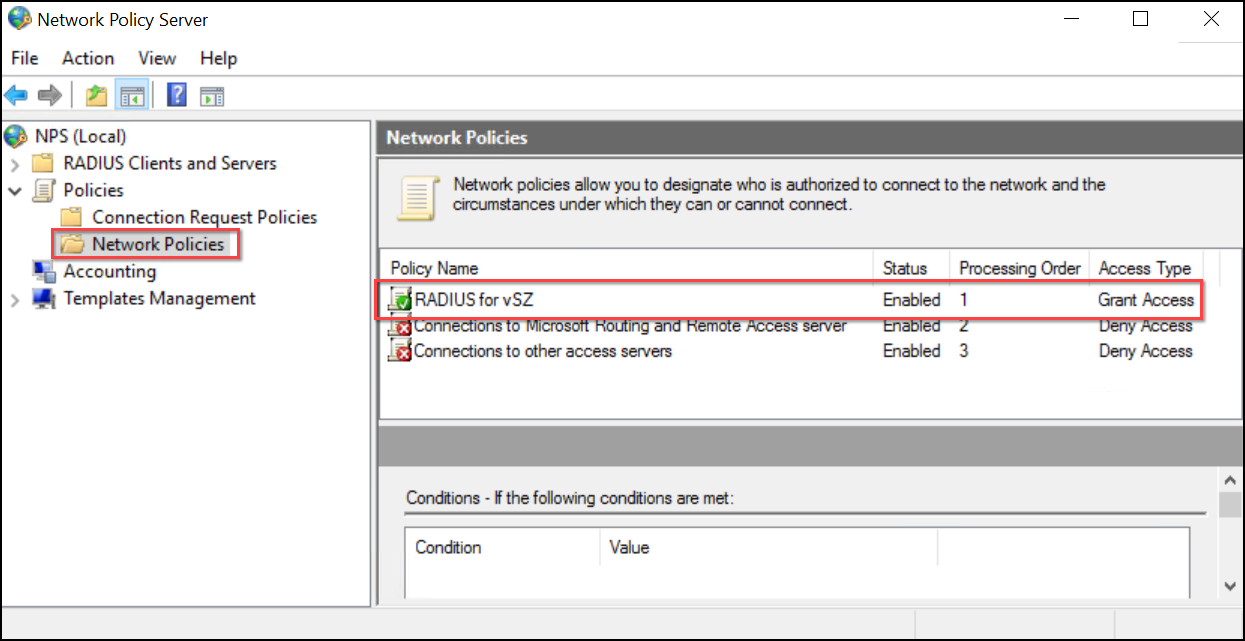
- Open the NP properties. In the left navigation pane of the NPS console, expand the NPS (Local) folder, locate and click the Network Policies folder. On the right pane, locate the network policy you created and double-click it to access its properties.
- In the Conditions tab, select the existing User Groups condition, and click Edit … . The User Groups window is displayed for you to add new groups to this condition or remove the existing ones.
- Optionally, in the
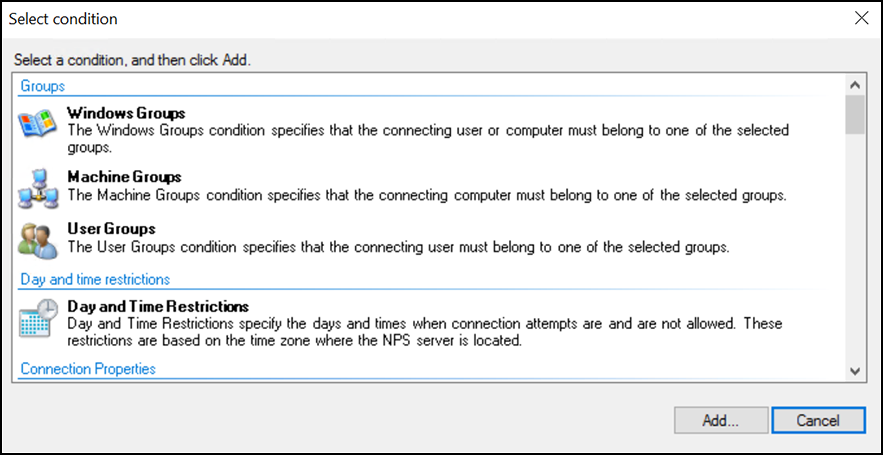
Conditions tab, click Add … to create a new
condition. The Select condition window is displayed for you to choose an
additional condition for the NP.You have successfully modified the NP conditions.
NPS Certificate for EAP Services
Extensible Authentication Protocol (EAP) is a secure connection protocol that requires a Secure Sockets Layer (SSL) certificate to ensure the security of communications. Complete the following steps to corroborate whether there is an existing and valid SSL certificate for the Network Policy:
- Open the NP properties. In the left navigation pane of the NPS console, expand the NPS (Local) folder, locate and click the Network Policies folder. On the right pane, locate the network policy you created and double-click it to access its properties.
- In the Constraints
tab, select Authentication Methods, then select Microsoft: Protected EAP
(PEAP) in the list and click Edit ...
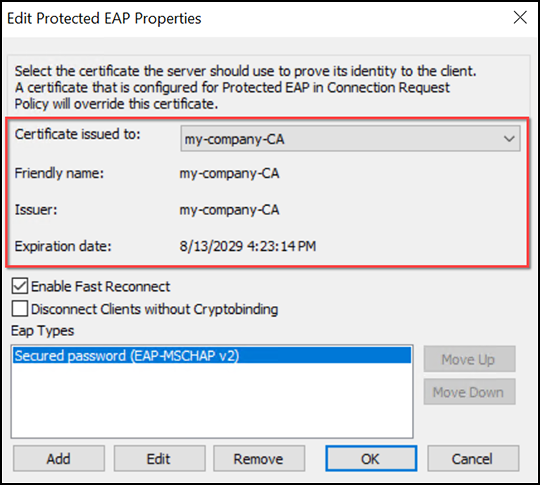
.The Edit Protected EAP Properties window opens for you to corroborate the certificate is valid. If the certificate is not present, a warning will pop up as A certificate could not be found that can be used with this Extensible Authentication Protocol. In case the certificate is not found, refer to Deploying the AD Certification Authority section in the topic Active Directory Configurations for instructions on how to assign a certificate to this NPS.
The SmartZone AAA Test Tool
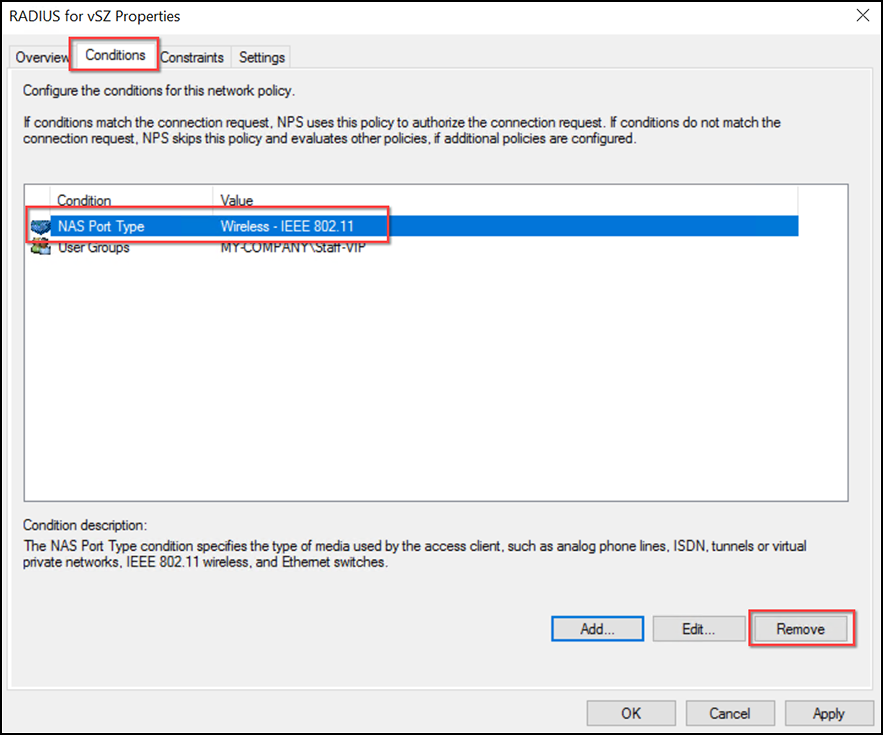
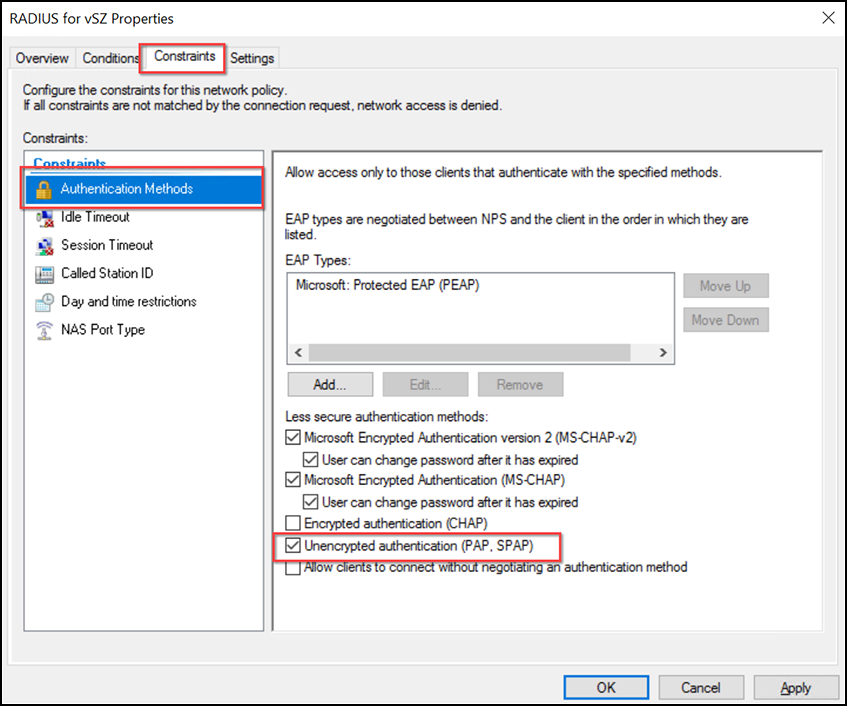
The controller AAA test tool is a handy troubleshooting tool to verify the NPS communication with SmartZone, but it relies on the Password Authentication Protocol (PAP), which is an unsecure authentication method. When using the SmartZone AAA test tool, ensure that PAP is enabled in the NP constraints. Additionally, because the controller creates a virtual authentication port for the AAA test, you need to remove the NAS Port Type Wireless - IEEE 802.11 condition from the NP conditions to allow the AAA test tool to function correctly.
Complete the following steps to prepare the existing Network Policy for a AAA test from the controller.
- Open the NP properties. In
the left navigation pane of the NPS console, expand the NPS (Local) folder,
locate and click the Network Policies folder. On the right pane, locate the network
policy you created and double-click it to access its properties.The NP Properties window is displayed.
- In the Conditions tab, select the NAS Port Type condition and click Remove.
- In the Constraints tab, select Authentication Methods, then enable the Unencrypted authentication (PAP, SPAP) option.
- Click OK to apply the changes.
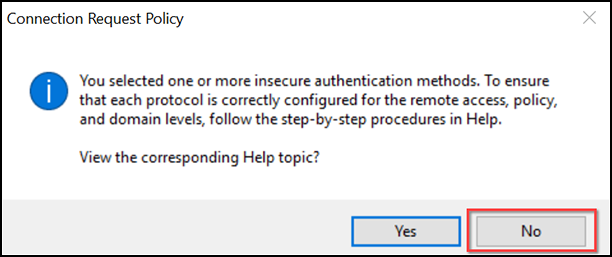
A confirmation pop-up will warn you from enabling this unsecure authentication method. Click No to ignore the suggestion and keep with the intended configuration for the test.
- Perform the testing from the
SmartZone GUI, then revert and manually return these changes when done.
Note: To learn the steps to configure and test the RADIUS AAA server in controller, refer to the section Configuring the Authentication Services and Creating a WLAN in the topic Working with SmartZone.
Attention: Return to the secure authentication methods after your testing is completed.