Managing AP Certificates
AP certificates are valid for a period of time and have to be replaced when they expire.
3.6 Update
Note: Although AP Certificate Expire Check is enabled by default, when an AP with an expired
certificate joins the controller, this check automatically gets disabled. To restore
security:
You must get AP certificate replacement before your AP certificate expires. The system generates an apCertificateExpireSystem alarm and event when an AP certificate expires.
For AP Certificate replacement, perform the following:
- Click . This displays the AP Certificate Replacementpage.
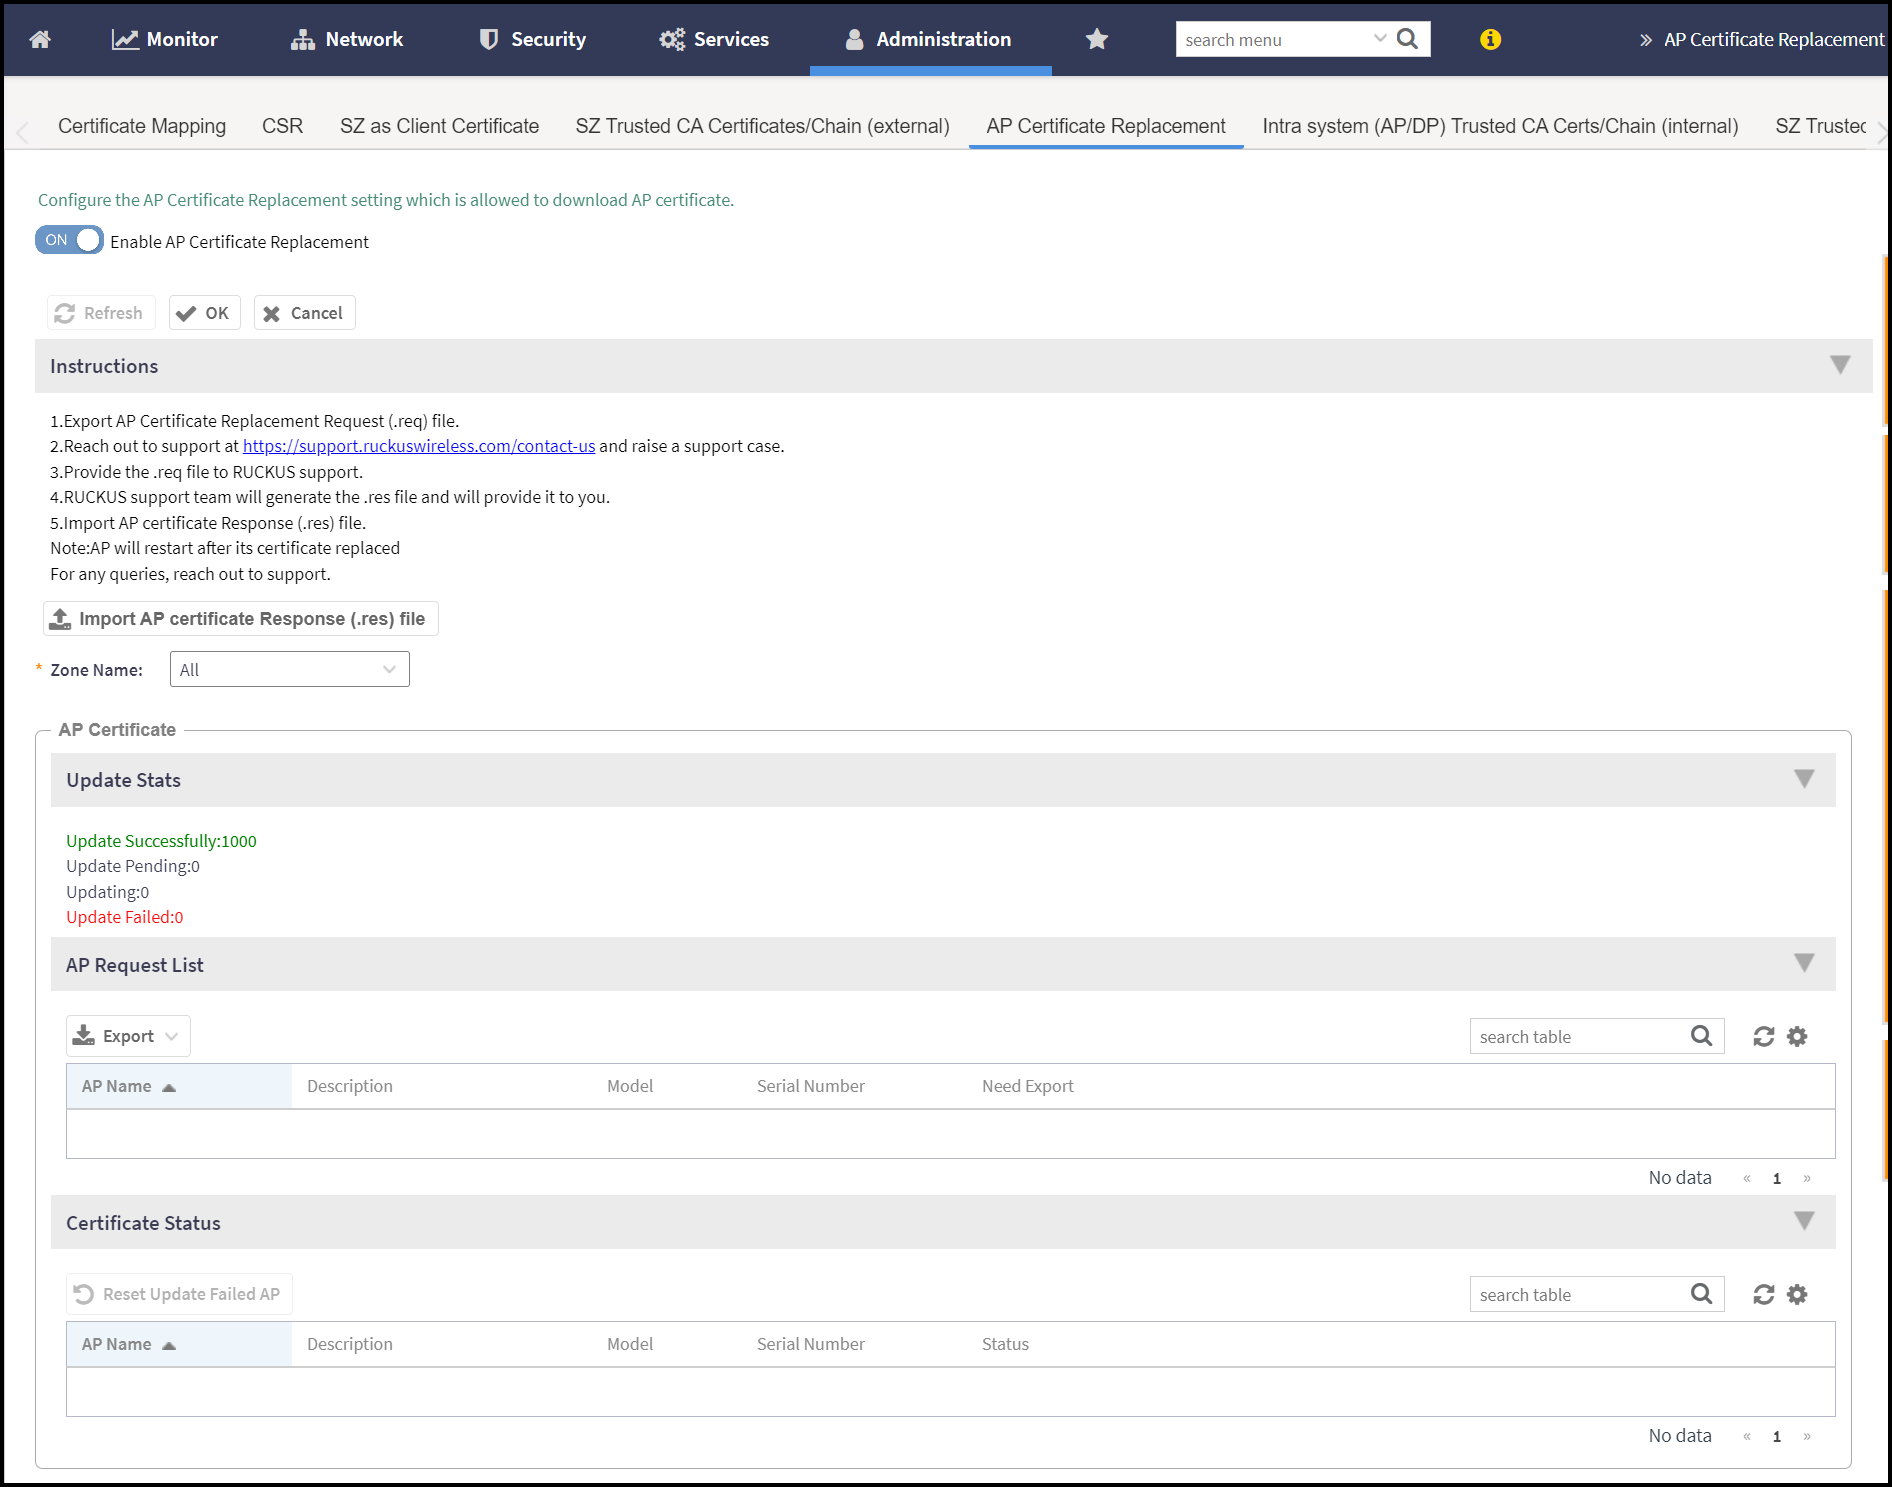
- By default, the Enable AP Certificate Replacement is disabled. Click the Enable AP Certificate Replacement button to enable the AP certificate replacement and follow the instructions on the screen.
- From the AP Certificate Replacement page of the application, click Import AP certificate Response (.res) file. The Import AP certificate for replacement form appears.
- Click Browse and select the file.
- Click OK.
Note: All APs included in the imported response (.res) file reboot after their certificate is refreshed.
- Select the Zone Name from the drop-down list.
AP Certificate
In the AP Certificate section, the following details are displayed.
- Update Stats: Displays the status of the AP certificate.
- AP Request List: Displays the list of requested APs.
- Certificate Status:
Displays the certificate status.If the status is:
- Updating: Controller is in the process of updating the certificate.
- Update Failed:
Controller failed to update the certificate.
Note: The AP reports to the controller at 15-minute intervals. As a result, it may take up to 15 minutes for the AP to update its certificate status on the web interface.
After all the APs are updated with the new certificates, manually enable the
ap-cert-expired-checkCLI command in the config mode to restore security and reject APs that try to connect with expired certificate