Configuring a Rogue Classification Policy
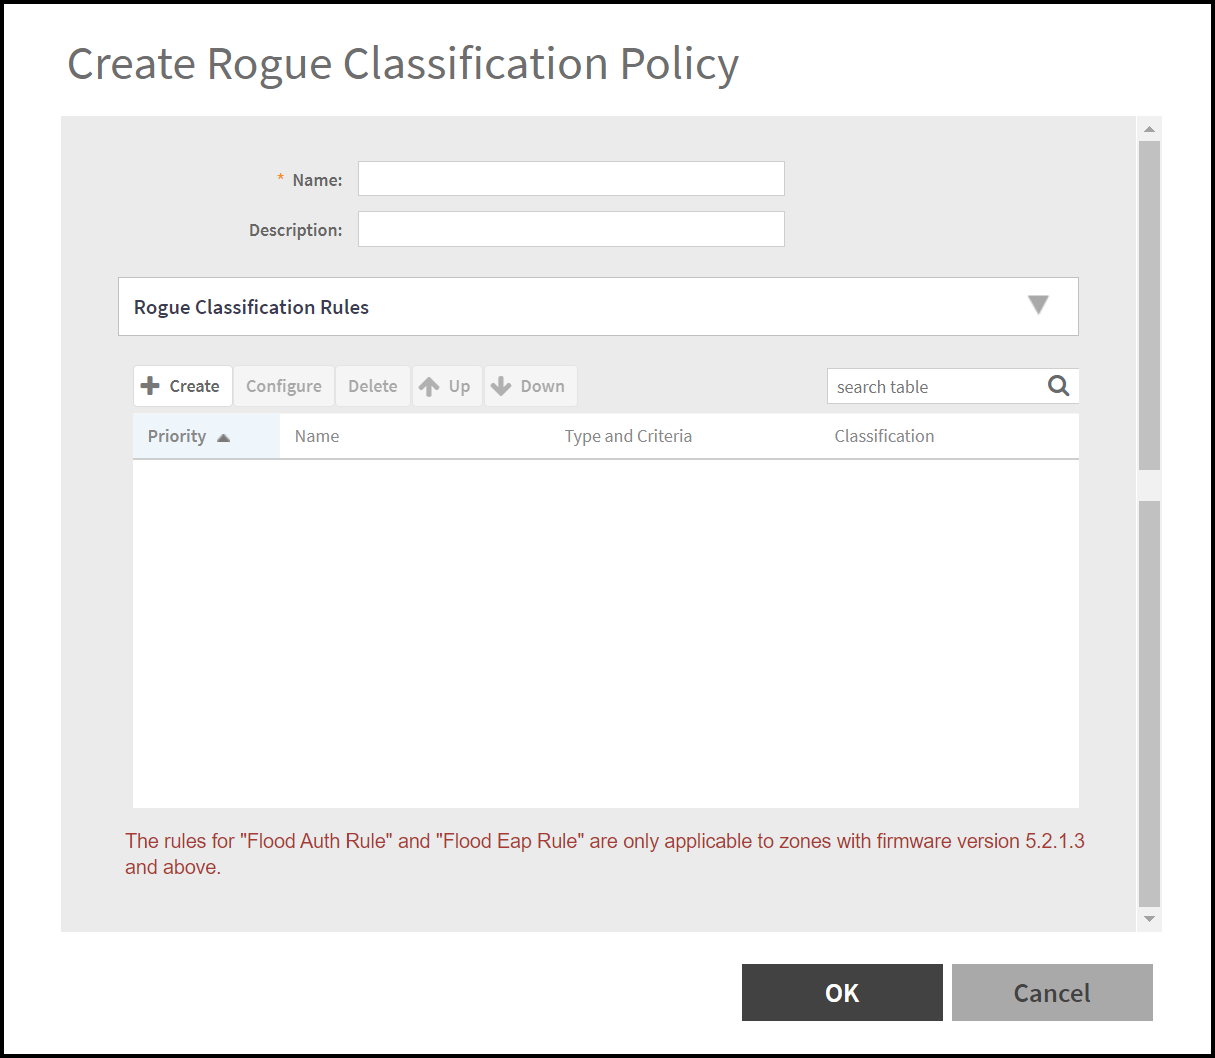
A user can create a rogue classification
policy with rules at the zone and monitoring-group level. This allows automatic
classification when specific rogue detection criteria is met.
- Click .
- Select the zone from the system tree and click Create.
- Enter the following:
- Rogue Classification Rules
- Click OK to create Rogue Classification Policy.
Note: Click
Configure or
Delete to edit or delete a rogue classification policy respectively. To prioritize a classification
rule, select the rule from the list and click
Up or
Down to position the rule.
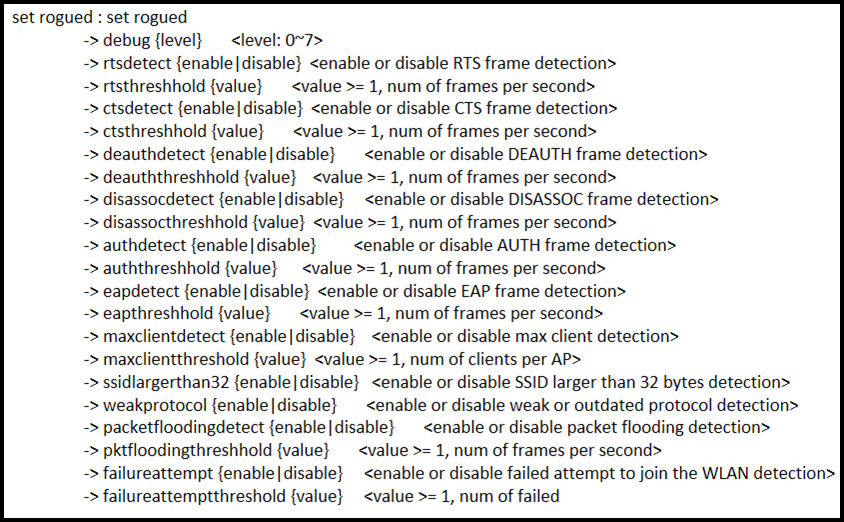
Note: The user can use command line interface in SZ
to disable or change threshold packets per seconds for CTS abuse, RTS abuse, Deauth
flood, disassociation flood and other detection types.
- To change the threshold detection follow the command: remote ap-cli <ap-mac> "set rogued <attack-type> <number pf packets>". Example: remote ap-cli 8c:fe:74:1c:d6:b8 "set rogued rtsthreshhold 10"
- To enable / disable flood detection follow the command : remote ap-cli <ap-mac> "set rogued <attack-type> enable/disable". Example: remote ap-cli 8c:fe:74:1c:d6:b8 "set rogued rtsdetect enable"