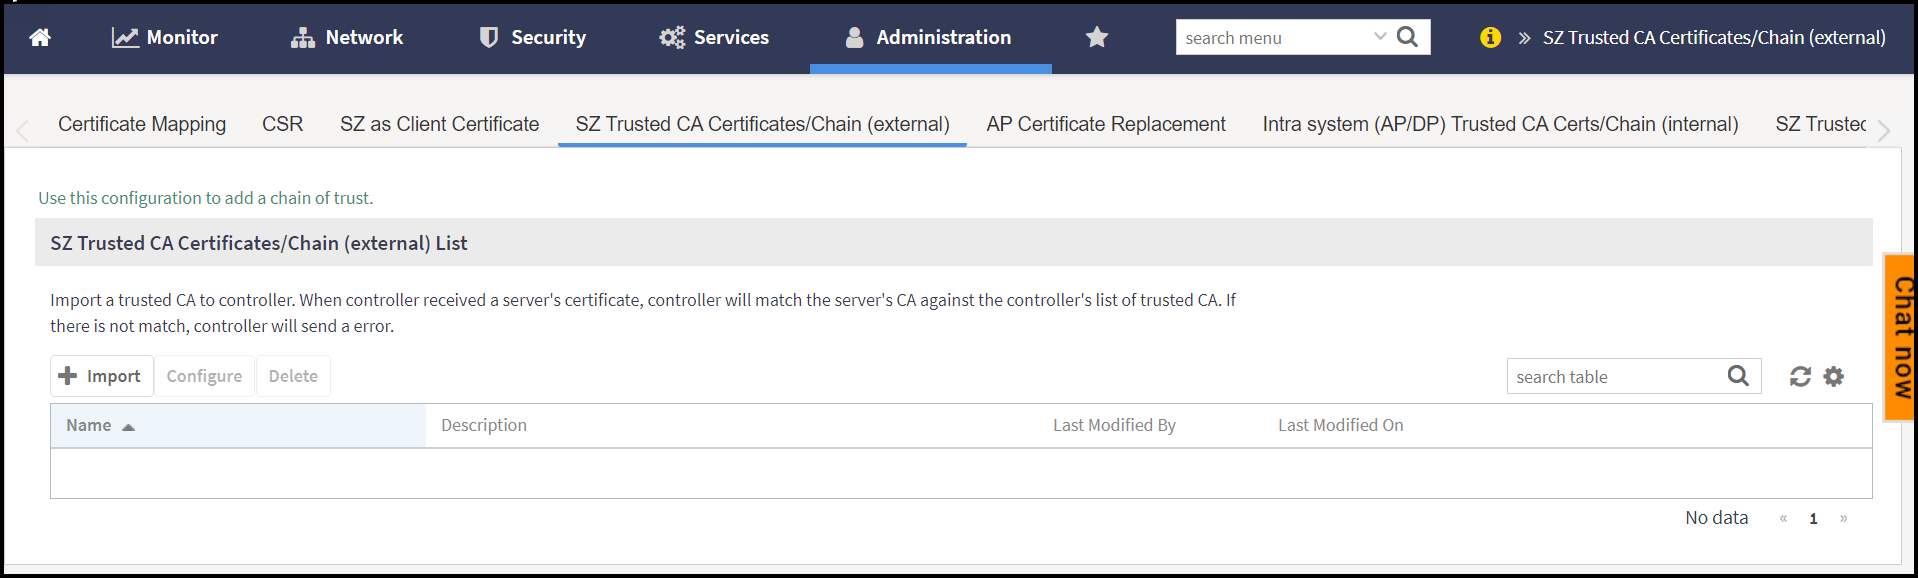
Importing SmartZone (SZ) Trusted CA Certificates/Chains
When a controller receives a server's
certificate, it matches the server's CA against the list of trusted CAs it has.
If there is
no match, the controller sends an error.
To import a CA certificate, perform the following:
- Click and select SZ Trusted CA Certificates/Chain (external). This displays SZ Trusted CA Certificates/Chain (external) page.
- Click Import. This displays the Import CA Certs (Chain) window.
- Enter the following details:
- Name: Type a name ot identify the CA Certificate.
- Description: Enter a short description for the CA Certificate.
- Intermediate CA Certificates: Click Browse and select the file from your local system. If you need to upload multiple intermediate CA certificates to establish a chain of trust to the signed certificate, you can select up to four certificates.
- Root CA Certificate: Click Browse and select the file from your local system.
- Click OK to add the newly imported certifcate.
- Click OK.
Note: You can also edit or delete a CA certificate by selecting the options Configure or
Delete respectively.
Note:
SCG-96911, SCG-97846 updates, Second line as a part of 5.1.2.3 update
The controller does not support the CA certificate with p7b (windows format), only
CRT or PEM format is supported. If the Certificates signed by CA chain has more than
5 chain length then you can upload only the Root CA of the certificate.