ARP Termination
Feature Overview
ARP Termination is used on network edge devices for several important reasons:
- Traffic Reduction: Intercepting ARP requests and responding on behalf of known destinations significantly reduces ARP broadcast traffic across the network.
- Improved Scalability: Limiting ARP broadcasts enhances scalability in large network deployments, particularly in data center environments with numerous endpoints.
- Performance Enhancement: Reducing unnecessary ARP traffic leads to improved overall network performance and reduced latency.
- Efficient Address Resolution: The RUCKUS Edge device maintains a table mapping IP addresses to MAC addresses, allowing for quicker and more efficient address resolution without flooding the network with ARP requests.
- Security Enhancement: Limiting the scope of ARP broadcasts improves network security by making it more difficult for potential attackers to gather information about the network topology.
- Bandwidth Conservation: Reducing the flooding of ARP messages in the network helps conserve core bandwidth.
The data plane component of the RUCKUS Edge device handles ARP requests. Typically, without the ARP Termination feature, when it receives an ARP request for a remote IP address, it forwards the request by flooding it across the Layer 2 (L2) network. This flooding causes a broadcast storm, affecting all APs in the L2 domain. The APs react to these broadcast packets by reducing their transmission rate on the wireless network. This leads to a decrease in network bandwidth available for regular data traffic.
A detailed explanation of the key components and processes follows:
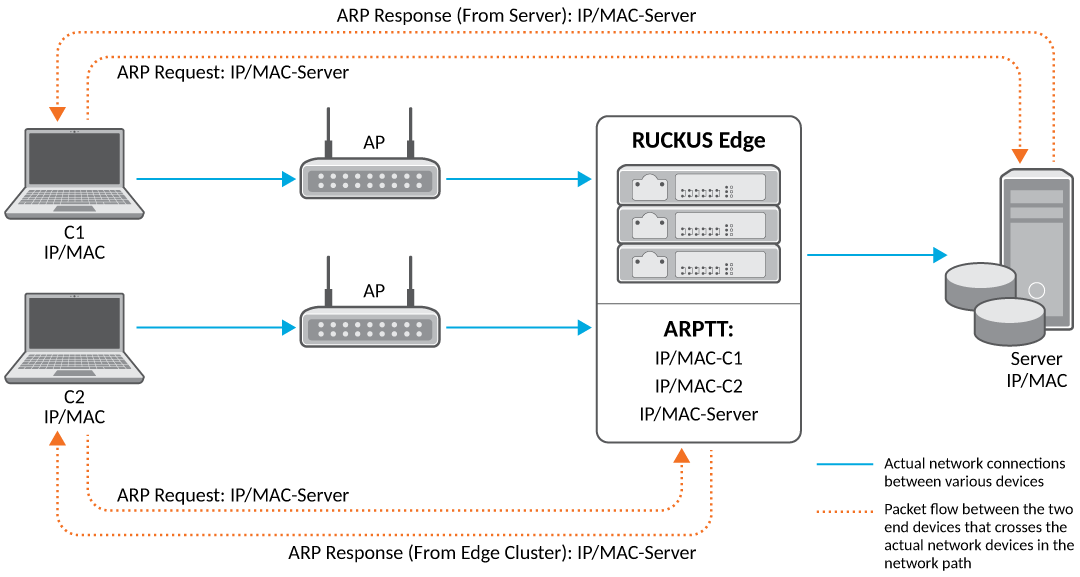
- When the RUCKUS Edge device receives an ARP Request, C2, it terminates the request and replies with an ARP Response on behalf of the IP owner (the target of the ARP Request).
- ARP Termination keeps track of the IP address and MAC address bindings of the IP owners. It builds an IP and MAC binding table, also known as the ARP Termination Table (ARPTT), by monitoring ARP Request and ARP Response packets.
- ARP Termination maintains these IP/MAC bindings in separate hash tables for each Bridge Domain (BD), corresponding to each Virtual Network Identifier (VNI). These tables are used to process ARP Request packets in the L2 forwarding path.
- Processing ARP Requests:
- If the IP/MAC entry for the ARP Request target is found in the table, an ARP Response is sent to the ARP Request sender through the input interface.
- If the entry is not found, the ARP Request packet is flooded normally, following the standard L2 broadcast forwarding path.
- When the ARP Termination table reaches the maximum capacity of 50,000 entries, no new ARP entries can be added until some of the existing entries expire.
Requirements
Ensure that the firmware version is at least 2.3.0.1181 to support this feature.
Limitations
The total number of IP to MAC bindings cannot exceed 50,000 entries in each of the IPv4 and IPv6 tables. The ARP request packet will flood the network in the same manner as standard Layer 2 broadcast forwarding. When the ARP Termination table reaches the maximum capacity of 50,000 entries, no new ARP entries can be added until some of the existing entries expire.
Considerations
The ARP termination feature is enabled by default, with the ARP Termination Aging Timer set to a default value of 600 seconds.
Best Practices
Implementing ARP termination in RUCKUS Edge can enhance network performance and security. Here are some good practices to consider:
- Enable ARP Inspection: Configure ARP inspection on the relevant VLANs to ensure that only valid ARP requests and responses are allowed. This helps prevent ARP spoofing attacks.
- Use Static ARP Entries: Where possible, use static ARP entries for critical devices. This can prevent unauthorized devices from communicating on the network.
- Segment the Network: Properly segment the network using VLANs to limit the broadcast domains and reduce unnecessary ARP traffic.
- Implement IP Source Guard: Use IP Source Guard to bind IP addresses to specific MAC addresses and switch ports. This ensures that only legitimate devices can communicate on the network.
- Monitor and Log ARP Traffic: Regularly monitor and log ARP traffic to detect and respond to any suspicious activity promptly.
Prerequisites
This feature has no prerequisites to feature enablement or usage.