Changing the Controller IP Address
Update the controller node IP address
using either the single-interface or three-interface configuration. Ensure uninterrupted
connectivity for APs, ICX switches, and Data Plane nodes. This procedure covers both
web UI
and CLI methods, and includes the required updates to dependent systems.
Attention: Changing the IP address configuration of a controller node requires the controller
services to restart.
Consider the following prerequisites before changing the
controller IP address:- Approve a maintenance window for this activity.
- Collect a backup of the controller.
- Ensure console or out-of-band access to the controller node is available.
- Prepare to update DHCP, DNS, routing, and firewall rules.
- Confirm the new address is reachable from all AP and switch VLANs.
- Confirm VLAN tagging on the access switch ports to the controller (for both physical and virtual appliances) allows the required VLANs as untagged.
- For virtual appliances (vSZ), ensure the hypervisor configuration (vSwitch or NIC settings) also passes the same VLAN tags to the controller VM.
- (Optional) If you are changing
the control interface IP address, use the Switch over cluster
option to retarget APs and switches before changing IP.Note: Retargeting APs and switches before changing the control IP address minimizes downtime and ensures devices reconnect to the new address immediately after the change.
- To retarget APs, in the web UI, select .
- Select the APs or Zone and click .
- Enter the destination controller Control IP/FQDN and confirm.
- To retarget switches, in the web UI, select .
- Select the switch or switch group and click .
- Enter the destination controller Control IP/FQDN and confirm.
The APs or switches receive the new IP configuration and attempt to connect immediately. If the controller does not answer after 900 seconds, the AP or switch will fallback to the previously configured IP address. - Choose from one of the following
procedures to change the IP address on a single-interface or a three-interface
controller.
- Single-interface
controller: Perform sub-steps a through e if using the web UI; perform
sub-step f if using the CLI.
- In the controller web UI, select .
- Select the node and click Configure.
- Set the Management/AP Tunnel interface to Static or DHCP as planned.
- Enter the Primary DNS Server and Secondary DNS Server and if required, enter the Control NAT IP.
- Click OK to
save the changes.
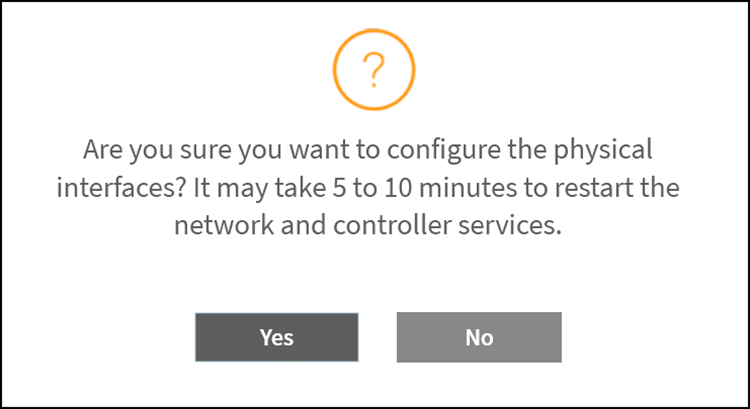
A confirmation message pops-up alerting you that services will be restarted and requiring you choose whether to proceed. Click Yes to continue.
Alternatively, from the controller CLI, in the config mode enter the commandinterface mgmt-or-ap-tunnel, followed by the commandip addressnew_ip subnet_mask gateway_ip. Type yes at the confirmation prompt and conclude with theendcommand to return to the privilege EXEC mode.node-1# config node-1(config)# interface mgmt-or-ap-tunnel node-1(config-if)# ip address 192.168.110.79 255.255.255.0 192.168.110.1 This requires restarting all vSZ services. Do you want to continue (or input 'no' to cancel)? [yes/no] yes The control plane configuration has been updated successfully. The service will restart momentarily. To avoid service disruptions, please avoid any cluster operations (add node, remove node, backup, restore, upgrade) for the next 10 minutes. node-1(config-if)# end node-1#
- Three-interface
controller: Perform sub-steps a through d if using the web UI; perform
sub-step f if using the CLI.
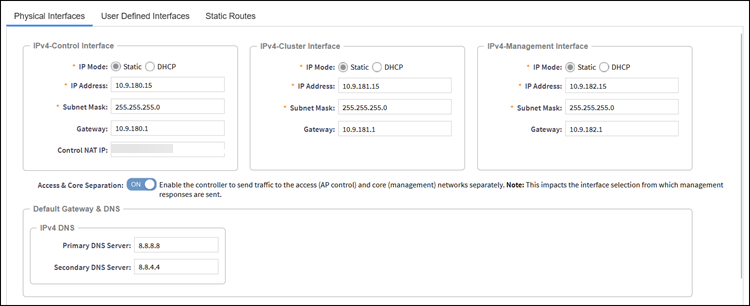
- In the controller web UI, select .
- Select the node and click Configure.
- Update the Control, Cluster, and Management interfaces to DHCP or Static as well as the DNS and control NAT information as needed.
- Click OK to
save the changes.
A confirmation message pops-up alerting you that services will be restarted and requiring you choose whether to proceed. Click Yes to continue.
- Alternatively, from
the controller CLI, in the config mode enter the command
interfacefollowed by the keywords cluster, control, or management. Within the interface configuration mode, enter the commandip addressnew_ip subnet_mask gateway_ip.The CLI prompts you with a confirmation message warning you about the required services restart. Enter yes.
node-1# config
node-1(config)# interface cluster
node-1(config-if)# ip address 10.0.0.1 255.255.255.248 10.0.0.6
This requires restarting all vSZ services. Do you want to continue (or input 'no' to cancel)? [yes/no] yes
The control plane configuration has been updated successfully. The service will restart momentarily. To avoid service disruptions, please avoid any cluster operations (add node, remove node, backup, restore, upgrade) for the next 10 minutes.
- Single-interface
controller: Perform sub-steps a through e if using the web UI; perform
sub-step f if using the CLI.
- Complete these updates
immediately after the controller IP address change to ensure all devices and
integrations use the new address:
- DHCP option 43: Update to advertise the new controller Control IP or FQDN.
- DNS records: Update host records; lower TTLs if rapid propagation is needed.
- ICX registrar settings: Update manager active-list and manager backup-list to the new address or FQDN.
- Routing, ACLs, Firewall rules, NAT: Update all relevant policies and static routes.
- External tools: Update RADIUS/AAA, syslog, SNMP managers, monitoring, and automation systems.