Wireless Client Isolation
This means that a wireless client cannot send or receive packets from another wireless client, ensuring that each client can only communicate with backend servers over the backbone network via the current AP. This feature is crucial for enhancing network security and performance by isolating client traffic. Additionally, ARP requests are dropped if the target IP is not in the whitelist, if the sender IP or MAC is in the whitelist (to protect against ARP spoofing), or if the target IP is broadcast. IP packets are dropped if the source IP is in the whitelist to protect against IP spoofing. The AP drops DHCP OFFER and ACK messages, as well as DNS responses.
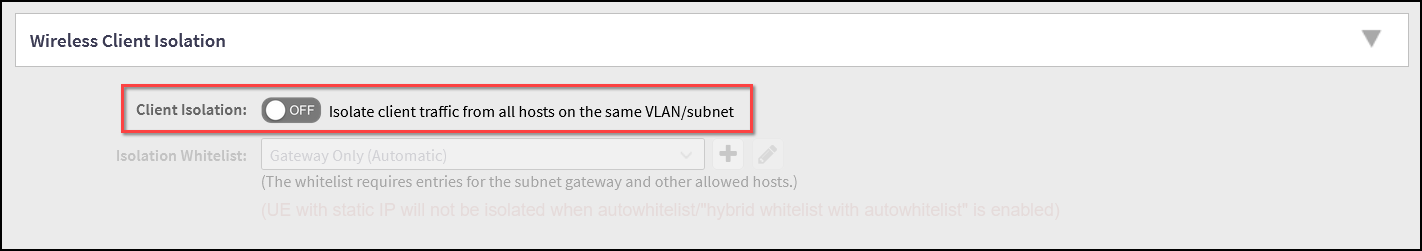
Switch ON the toggle with the legend Isolate client traffic from all hosts on the same VLAN/subnet to make visible the traffic isolation options, and enable at least one of the following:
- Isolate unicast packets: Enable this option to isolate unicast packets between a client isolation-enabled client and other clients connected to the same AP. Unicast packets are those sent from one specific client to another.
- Isolate multicast/broadcast packets: Enable this option to isolate multicast and broadcast packets between a client isolation-enabled client and other clients connected to the same AP. Multicast packets are sent to multiple clients, while broadcast packets are sent to all clients in the network.
- Automatic support for VRRP/HSRP: Enable this option to ensure proper client isolation in environments where VRRP or HSRP is deployed. This option provides automatic support for Virtual Router Redundancy Protocol (VRRP) and Hot Standby Router Protocol (HSRP), which are used for router redundancy.
Optionally, select an Isolation Whitelist from the drop-down list. By default, Auto Whitelist is enabled for the default gateway of the network only. If required, click + to create a new list, the Create Client Isolation Whitelist window opens.
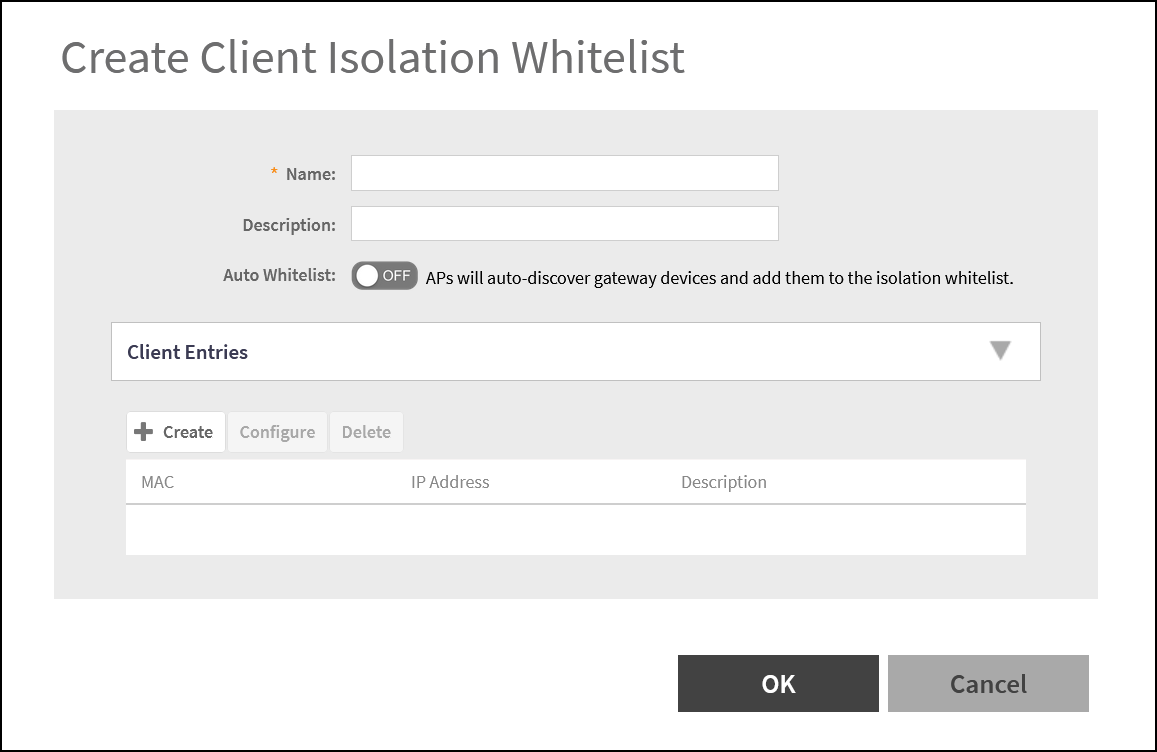
Refer to the following guidelines for implementing wireless client isolation. -
- When using Auto Whitelist or Hybrid Whitelist with Auto Whitelist, enable the Force DHCP option to ensure clients acquire IP addresses via DHCP, as static IPs are not supported.
- On network switches or routers, disable Proxy ARP to prevent ARP responses from non-CI clients from reaching CI clients.
- For VRRP deployments, add the physical and virtual MAC addresses of VRRP routers to the manual Whitelist to ensure proper isolation.
- Be aware of multicast traffic handling, especially in VRRP deployments, and configure the Whitelist accordingly to avoid dropping necessary packets.
- For IPv6 networks, ensure the on-link flag in the prefix information option is enabled to maintain proper client isolation.
Refer to the following limitations and exceptions for implementing wireless client isolation. -