Configuring URL Redirection
URL Redirection uses ACLs set up in the
controller to apply dynamic URL Redirection policies based on RADIUS attributes received
during user authentication.
- Create an L3 Access Control
Policy to manage blocked and permitted URLs, as well as the
redirection behavior depending on the Default Access setting:
- Navigate to and click Create.
- Select the Default Access
settings as follows:
- Allow: When the Default Access action is set to Allow, the user is not redirected after successful authentication but is redirected only when trying to access blocked sites.
- Block: When the Default Access action is set to Block, the user is redirected after successful authentication and also when trying to access blocked sites.
- Click Create to create ACL policy rules. For URL Redirection, you must create an Allow rule for the redirection site followed by Deny rule for the sites you want to block for a User Role. Click OK the save the policy rule. You may create as many policy rules as necessary.
- Click OK to
save the L3 Access Control Policy.
Note: If you are using Fully Qualified Domain Names (FQDN) in the URL sent from AAA, make sure that a Domain Name Server (DNS) Server Profile is available for the WLAN. For more information about configuring a DNS Server Profile in the WLAN, refer to Advanced Options.
- Create a Firewall Profile that contains the L3 Access Control Policy that you created in step 1.
- Create a User Role and map
to it the Firewall Profile you created in step 2.
- Navigate to and click Create.
- In Firewall Profile, from the drop-down menu, select the Firewall Profile you created in step 2.
- Click OK to save the User Role.
- Create additional User
Role entries as needed to meet network requirements and link each User
Role with unique Firewall Profiles to ensure varied access levels.
Note: For additional details about configuring the remaining Firewall Profile options, refer to User Roles.
- Edit the Proxy Authentication
Service to add the User Role Mapping policies corresponding to URL Redirection.
- Navigate to .
- Select the Authentication Service to which you want to add the Role Mapping for URL Redirection and click Configure. Optionally, you can create a new proxy authentication service by clicking Create. Refer to Creating Proxy Authentication AAA Servers.
- In the Edit Authentication Service page, scroll to the User Role Mapping section and click Create.
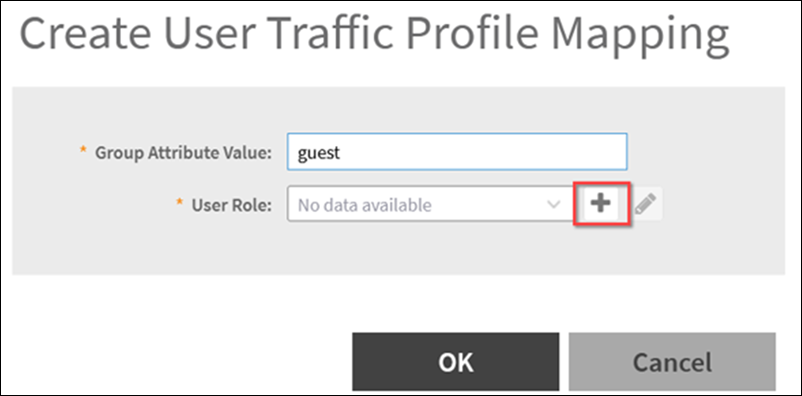
- In the Create User Traffic
Profile Mapping window, type the Group Attribute
Value (GAV). For example, guest.
- Note:
- You can grant full access to a client by assigning a GAV value, such as guest, to the system's default User Role through the Firewall Profile.
- The GAV value should match the Filter-ID attribute value received from the authentication server. This value will determine the User Role to be mapped to the user that is connecting to the network.
- In User Role, from the drop-down menu, select the User Role that you created in step 3.
- Click OK to save the User Traffic Profile Mapping.
- Create additional User Traffic Profile Mapping entries with different User Roles to grant varied access levels within the same WLAN.
- Click Apply to save the Authentication Service configuration.
- Configure the WLAN as
follows:
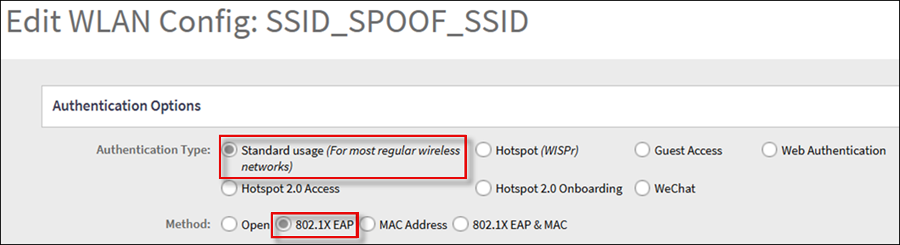
Note: Make sure the WLAN to which you are adding URL Redirection is already configured as a Standard usage authentication type with 802.1X EAP or MAC Address as the authentication method.
- Navigate to and select the domain or zone where the WLAN is located.
- Select and existing WLAN in the list and click Configure; the Edit WLAN Configuration window appears. Optionally, create a new WLAN. For more information about creating new WLANs, refer to Creating a WLAN Configuration
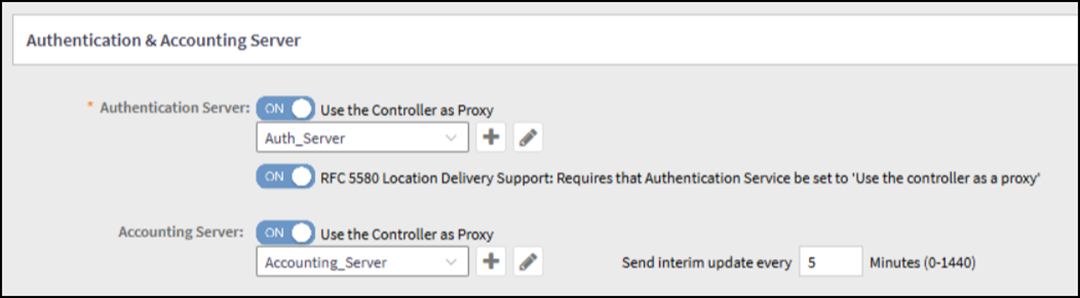
- Scroll to the Authentication & Accounting Server section and configure the following settings:
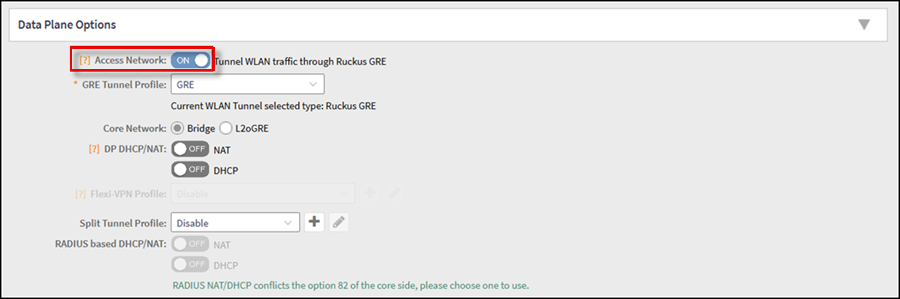
- Scroll to the Data Plane Options section and configure the following settings:
- Click OK to save the WLAN configuration.
You have successfully configured L3 ACL policies to manage URL redirection for your WLAN.