Troubleshooting with AP Packet Captures
- Client Connection Failures - One of the most common issues is client connectivity failure. If a client cannot obtain an IP address, check the capture for DHCP Discover and Offer packets, followed by DHCP Request and Acknowledgment. If the DHCP Offer or Acknowledgment is missing, the problem may be related to DHCP relay configuration, VLAN tagging, or server availability.
- Authentication Issues - Authentication problems are another frequent concern. In these cases, look for Extensible Authentication Protocol over LAN (EAPOL) packets and RADIUS Access-Request or Access-Reject messages. If the EAPOL handshake is incomplete or the RADIUS server rejects the request, verify the client credentials, RADIUS server configuration, and shared secrets.
- Roaming - Roaming delays can also be identified through packet captures. When a client moves between APs, you should see 802.11 Reassociation Request and Response frames, followed by DHCP or ARP traffic. If there is a long delay between reassociation and the start of data traffic, the issue may be related to AP handoff settings, client driver behavior, or fast roaming configuration.
- Interference - High retry rates or packet loss often indicate interference, excessive airtime usage, or physical issues such as a damaged Ethernet cable. In the capture, look for repeated 802.11 retransmissions, duplicate TCP acknowledgments, or TCP retransmissions. These patterns suggest that frames are being lost or corrupted.
To investigate further, use the following commands on the AP to check interference levels and radio statistics:
get wlanlist– Lists WLANs and their status.get airtime– Displays airtime usage per radio.get rssi– Shows received signal strength for connected clients.get txrx stats– Provides transmit and receive statistics, including retries and errors.
By combining packet analysis with AP-level diagnostics, you can pinpoint the source of performance issues and take corrective action.
Using Wireshark for Packet Analysis
Analyzing the contents of network packets is a powerful method for understanding network behavior and troubleshooting issues. Wireshark is a practical and widely used tool for this purpose. Once you have captured network traffic, open the capture file in Wireshark and apply the following tips and techniques to maximize the effectiveness of your analysis.
- Filtering the captured packets to display only wireless packets. Type wlan in the filter bar at the top of the Wireshark interface. This will limit the view of your packet capture to only packets that include the IEEE 802.11 wireless protocol.
- Analyzing Wireless Frame
Metadata. Wireshark provides detailed metadata about each captured
wireless frame through two key sections: the Radiotap Header and the
802.11 Radio
Information. These sections offer insight into how the frame was
transmitted over the air, including physical layer characteristics and signal
quality indicators.
In these sections, you can typically find information such as:
- Channel number and frequency
- PHY type
- Bandwidth
- Modulation and Coding Scheme (MCS) index
- Data rate
- Short Guard Interval (GI) status
- Space-Time Block Coding (STBC) streams
- Signal strength and noise level
- Signal-to-noise ratio (SNR)
- Timestamps and frame duration
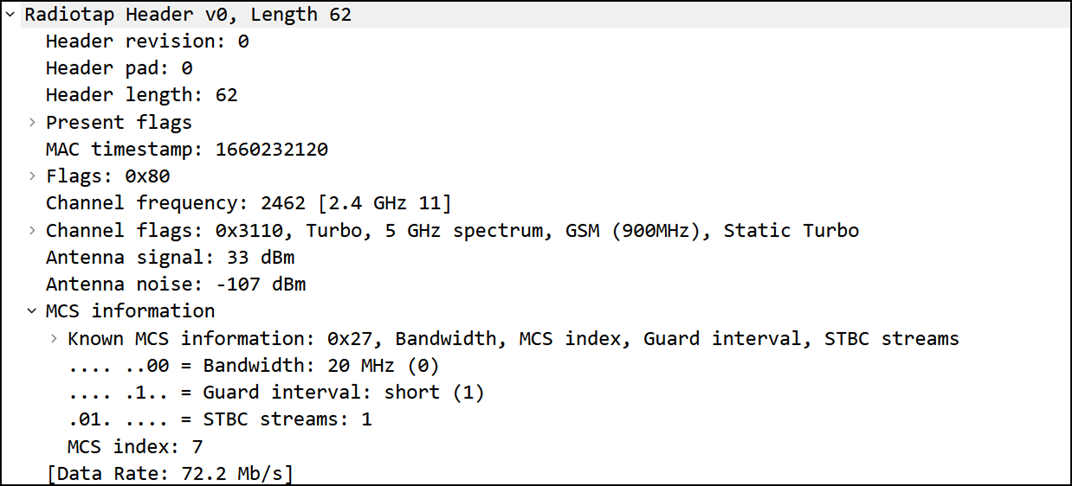
In The Radiotap Header, consider the following items:
- The MAC timestamp provides additional timing information that can be useful for correlating events or analyzing frame timing behavior.
- The Channel frequency indicates that the wireless frame was transmitted on the 2.4 GHz radio, using channel 11, at 2462 MHz.
- The antenna's signal strength is reported as 33 dBm, while the noise level is -107 dBm, resulting in a signal-to-noise ratio (SNR) of 140 dB. This exceptionally high SNR suggests a very clean wireless environment with minimal interference. In typical deployments, an SNR above 30 dB is considered excellent. Values significantly lower than that may indicate interference, distance from the access point, or physical obstructions.
- The bandwidth is set to 20 MHz, and the short guard interval is enabled, which allows for slightly faster transmission times.
- The presence of one STBC stream implies that the device may be using spatial diversity to improve reliability, which is common in environments with multipath propagation.
- The MCS index is 7, corresponding to a data rate of 72.2 Mbps, indicating that the connection is operating under favorable conditions.
By interpreting these values together, you can assess the overall health of the wireless link and identify potential issues such as poor signal quality, suboptimal channel selection, or client-side limitations.
- Understanding IEEE 802.11 QoS
Data Frames. The IEEE
802.11 QoS Data is a type of data field used in wireless networks that
support Quality of Service (QoS). When QoS is enabled in the network, the IP
data containing the transmitted information is contained in this section, for
example the web information in a web packet or the voice information in a voice
packet.
In this section of the packet, you can typically find:
- Frame type and subtype
- MAC addresses for source, destination, transmitter, and receiver
- BSS ID identifying the basic service set
- QoS Control field, which may indicate traffic priority
- Sequence and fragment numbers
- Encryption flags
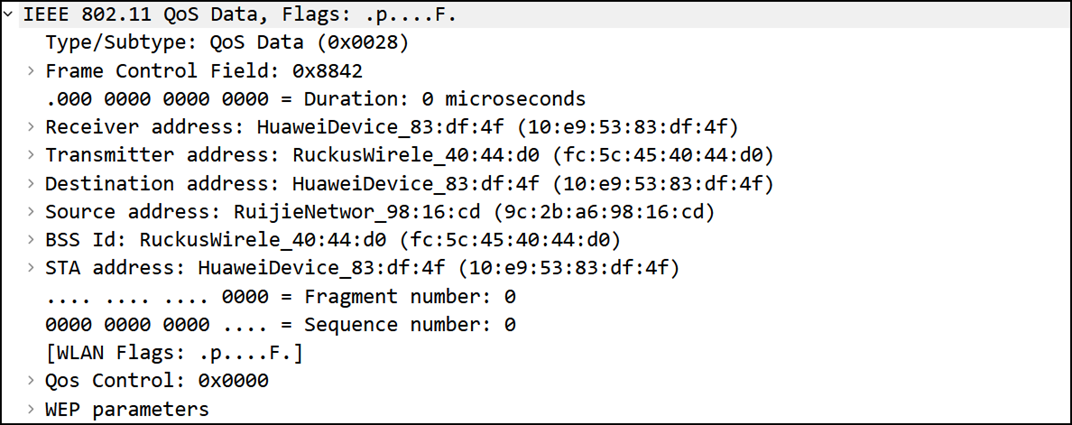
In QoS Data, consider the following items:
- The frame is
identified as a QoS Data frame (
Type/Subtype:
                              0x0028
), indicating that it supports traffic prioritization. - The receiver is a
Huawei device (
10:e9:53:83:df:4f). - The transmitter
is a RUCKUS access point (
fc:5c:45:40:44:d0). - The source
address differs from the transmitter, suggesting that the
frame may have been relayed or originated from a different device on
the network (
9c:2b:a6:98:16:cd). - The sequence and fragment numbers are both 0, meaning this is likely the first and only fragment of this frame.
- The WLAN flags
show
.p....F., which may indicate power management and frame type characteristics. - The QoS Control
field is set to
0x0000, which typically indicates best-effort traffic — meaning no special priority is applied. If this value were different (for example, indicating voice or video access categories), it would suggest that the frame is part of a latency-sensitive stream.
While this guide has focused on analyzing data frames and physical layer metadata, Wireshark also allows you to inspect other important 802.11 frame types such as beacons, probe requests/responses, and block acknowledgments. These frames are especially useful for tasks like infrastructure discovery, client roaming analysis, and performance tuning. For example, beacon frames reveal access point capabilities and timing information, probe frames help track client scanning behavior, and block ACKs provide insight into transmission efficiency and retransmissions. Although not covered in detail here, these frame types can offer valuable context when troubleshooting complex wireless environments.
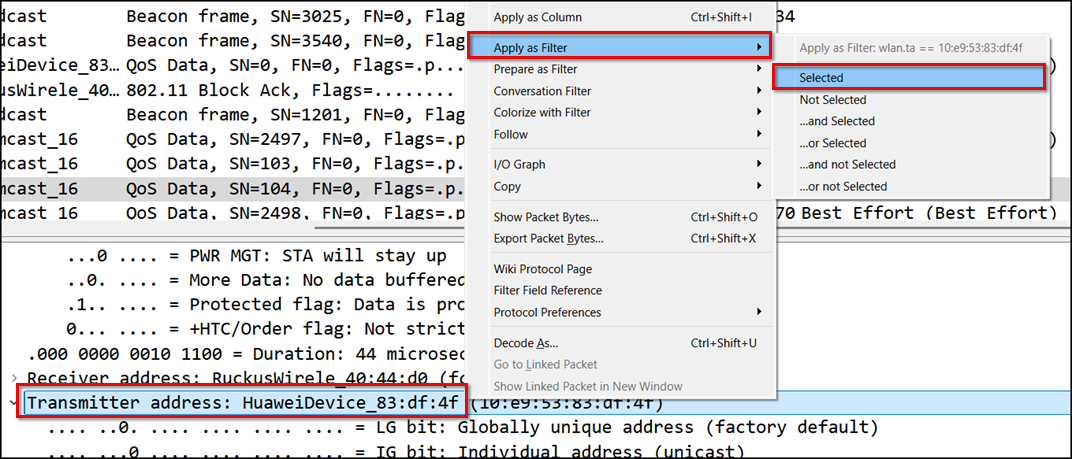
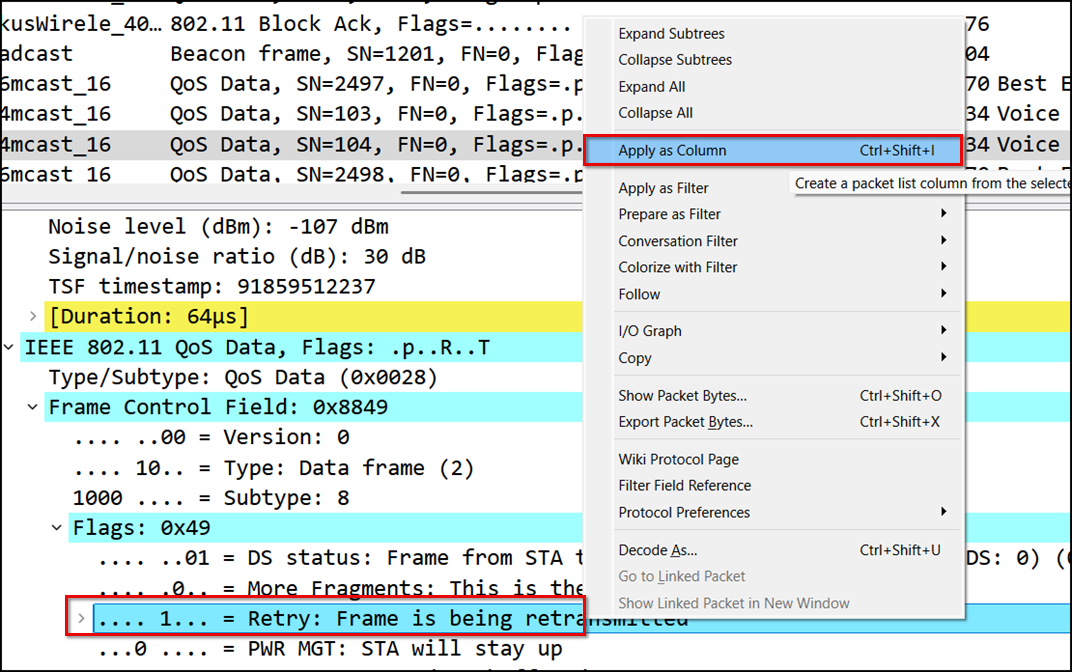
- Setting fields as filters or
columns. Wireshark allows you to interact directly with individual
fields in a captured frame. This is especially useful when for deeper analysis,
you want to filter or sort information based on specific values but you don't
know the filter syntax.
To do this:
- Right-click on the field of interest in the Packet Details pane.
- Choose one of the
following options:
- Apply as Filter, to instantly filter the packet list using the value of the selected field.
- Apply as Column, to add the selected field as a new column in the packet list view.
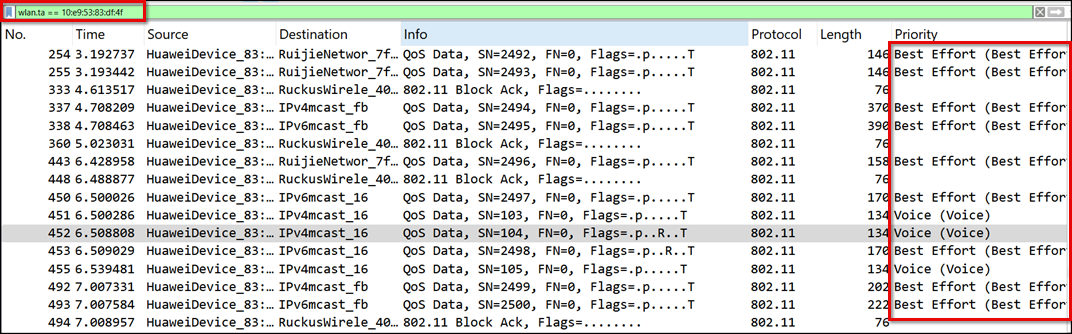
This feature is particularly useful when tracking values like: