Configuration Example for an IPsec Tunnel Using Default Settings (Site-to-Site VPN)
An IPsec tunnel is configured by binding an IPsec profile to the virtual tunnel interface
(VTI) at each end of the IPsec tunnel. When the default settings for the IPsec profile
are used, minimal configuration is needed to establish the tunnel.
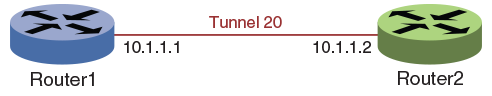
In the following example, Router1 and Router2 are the devices at each end of the tunnel.
On each device, an IPsec profile (profA) is created and bound to the VTI by using
the
tunnel protection ipsec profile command.
Router1
Router1(config)# ipsec profile profA
Router1(config-ipsec-profile-profA)# exit

Router1(config)# Interface tunnel 20
Router1(config-tnif-20)# tunnel mode ipsec ipv4
Router1(config-tnif-20)# tunnel protection ipsec profile profA
Router1(config-tnif-20)# tunnel source 10.1.1.1
Router1(config-tnif-20)# tunnel destination 10.1.1.2
Router1(config-tnif-20)# ip address 10.0.0.1 255.255.255.0
Router1(config-tnif-20)# exit
Router2
Router2(config)# ipsec profile profA
Router2(config-ipsec-profile-profA)# exit

Router2(config)# Interface tunnel 20
Router2(config-tnif-20)# tunnel mode ipsec ipv4
Router2(config-tnif-20)# tunnel protection ipsec profile profA
Router2(config-tnif-20)# tunnel source 10.1.1.2
Router2(config-tnif-20)# tunnel destination 10.1.1.1
Router2(config-tnif-20)# ip address 10.0.0.2 255.255.255.0
Router2(config-tnif-20)# exit