WLAN Encryption Options
The encryption methods utilize encryption algorithms to create a secure key. This key is used in the encryption process to encode the data.
None
Choosing None for the encryption method in a WLAN means your network will transmit data in plain text, making it vulnerable to interception and unauthorized access. This lack of encryption allows anyone within range to connect to your network and monitor your activities, posing significant security and privacy risks.
WPA2
Choosing WPA2 for the encryption method in a WLAN ensures that your network is protected by a robust encryption protocol. WPA2 uses the Advanced Encryption Standard (AES) to secure data, making it highly resistant to interception and unauthorized access. This encryption method helps maintain the privacy and integrity of your data, ensuring that only authorized devices can connect and communicate securely on your network.
Select WPA2 and configure the following settings:
Algorithm - Specifies the cipher is used to encrypt data. Choose one of the following:
- AES - Is a highly secure encryption algorithm used to protect data. It provides strong security by encrypting data in blocks of 128 bits, making it very difficult for unauthorized users to decrypt the information.
- AUTO - This setting allows the network to automatically select the best encryption algorithm available. Typically, it will default to AES if all devices on the network support it, ensuring optimal security and compatibility.
Passphrase - A password used to generate the encryption key. This supports 8 to 70 characters and does not have any requirement for password complexity.
802.11r Fast Roaming - This feature allows seamless transition between access points (supported by Wi-Fi 5 and Wi-Fi 6 APs). It works by pre-authenticating devices with multiple access points, reducing the time needed to switch connections and ensuring uninterrupted connectivity. Switch the toggle to ON and enter a Mobility Domain ID. The Mobility Domain ID is used by IEEE 802.11r to define a scope of the network in which a Fast Roaming is supported. Master keys are shared within the Mobility Domain, allowing clients to take advantage of fast roaming.
802.11w MFP - Management Frame Protection, which secures management frames from unauthorized alterations is supported by Wi-Fi 4 (IEEE 802.11n) and later standards. It works by encrypting management frames, ensuring that only authenticated devices can interpret and act on these frames. Select one of the following options:
- Disable: This option turns off MFP. Management frames will not be protected, making the network more vulnerable to certain types of attacks.
- Capable: This option enables MFP but does not enforce it. Wireless clients that support MFP will use it, while those that do not support it can still connect to the network without using MFP.
- Required: This option mandates the use of MFP. Only wireless clients that support MFP can connect to the network, ensuring that all management frames are protected.
- Disable
- Internal
- External
Note: DPSK options are only available to Open Standard usage WLANs with WPA-Mixed or WPA2 as the encryption method.
Reserve SSID - Toggle the switch to ON to reserve this SSID. When an SSID is reserved, the WLAN will be broadcast only if the AP loses connectivity to the controller or Data Plane. It activates 3 minutes after the heartbeat loss is detected.
WPA3
Selecting WPA3 for the encryption method in a WLAN provides the highest level of security currently available. WPA3 uses more advanced encryption algorithms and includes features like individualized data encryption, which ensures that even if someone intercepts your data, it remains unreadable. This method enhances protection against brute-force attacks and improves overall network security, making it ideal for safeguarding sensitive information.
Select WPA3, and configure the following settings:
Algorithm - Specifies the cipher used to encrypt data. The following algorithm is pre-selected and cannot be changed:
- AES - Advanced Encryption Standard (AES) is a highly secure encryption algorithm used to protect data. It provides strong security by encrypting data in blocks of 128 bits, making it very difficult for unauthorized users to decrypt the information.
SAE Passphrase - Simultaneous Authentication of Equals (SAE) is a key exchange protocol that provides robust protection against offline dictionary attacks by using a secure, mutual authentication process. The passphrase is used to generate cryptographic keys that encrypt the data transmitted over the network, ensuring that only authorized devices can access and communicate securely.
802.11r Fast Roaming - This feature allows seamless transition between access points. access points (supported by Wi-Fi 5 and Wi-Fi 6 APs). It works by pre-authenticating devices with multiple access points, reducing the time needed to switch connections and ensuring uninterrupted connectivity. Switch the toggle to ON and enter a Mobility Domain ID. The Mobility Domain ID is used by IEEE 802.11r to define a scope of the network in which a Fast Roaming is supported. Master keys are shared within the Mobility Domain, allowing clients to take advantage of fast roaming.
802.11w MFP - Management Frame Protection, which secures management frames from unauthorized alterations is supported by Wi-Fi 4 (IEEE 802.11n) and later standards. It works by encrypting management frames, ensuring that only authenticated devices can interpret and act on these frames. The following option is preselected and cannot be changed:
- Required: This option mandates the use of MFP. Only wireless clients that support MFP can connect to the network, ensuring that all management frames are protected.
Reserve SSID - Toggle the switch to ON to reserve this SSID. When an SSID is reserved, the WLAN will be broadcast only if the AP loses connectivity to the controller or Data Plane. It activates 3 minutes after the heartbeat loss is detected.
Transition Disable Indication - When this option is enabled, the AP will instruct the wireless client to disable certain transition modes for future connections to the AP's network. This information is included in the Transition Disable Key Data Element (KDE). The client should disable all transition algorithms requested if it supports the most secure algorithms. Additionally, the client must disable WEP and TKIP encryption methods and disallow associations without Protected Management Frames (PMF).
WPA R3 Support
WPA3 R3 is the latest iteration of the Wi-Fi Protected Access (WPA) protocol, designed to enhance wireless security. It introduces advanced features such as SAE Hash to Element (H2E) for improved password protection and robust management frame protection. These enhancements aim to provide stronger security for modern wireless networks.
WPA2/WPA3-Mixed
Choosing WPA2/WPA3-Mixed for the encryption method in a WLAN provides compatibility and security by supporting both WPA2 and WPA3 devices. This mode allows older devices to connect using WPA2 while newer devices benefit from the enhanced security features of WPA3. It ensures a smooth transition to WPA3, maintaining robust encryption and protecting your network from unauthorized access.
Select WPA2/WPA3-Mixed, and define the following settings:
Algorithm - Determines the specific cipher used to encrypt data. Choose one of the following:
- AES - Advanced Encryption Standard (AES) is a highly secure encryption algorithm used to protect data. It provides strong security by encrypting data in blocks of 128 bits, making it very difficult for unauthorized users to decrypt the information.
Passphrase - A password used to generate the encryption key. It supports from 8 to 70 characters and does not have any requirement for password complexity.
SAE Passphrase - Simultaneous Authentication of Equals (SAE) is a key exchange protocol that provides robust protection against offline dictionary attacks by using a secure, mutual authentication process. The passphrase is used to generate cryptographic keys that encrypt the data transmitted over the network, ensuring that only authorized devices can access and communicate securely.
802.11r Fast Roaming - A feature that allows seamless transition between access points. supported by Wi-Fi 5 and Wi-Fi 6 APs. It works by pre-authenticating devices with multiple access points, reducing the time needed to switch connections and ensuring uninterrupted connectivity. Switch the toggle to ON and enter a Mobility Domain ID. The Mobility Domain ID is used by 802.11r to define a scope of the network in which a Fast Roaming is supported. Master keys are shared within the Mobility Domain, allowing clients to support fast roaming.
802.11w MFP - Management Frame Protection, which secures management frames from unauthorized alterations, supported by Wi-Fi 4 (802.11n) and later standards. It works by encrypting management frames, ensuring that only authenticated devices can interpret and act on these frames. Select between one of the following options:
- Capable: This option enables MFP but does not enforce it. Wireless clients that support MFP will use it, while those that do not support it can still connect to the network without using MFP.
- Required: This option mandates the use of MFP. Only wireless clients that support MFP can connect to the network, ensuring that all management frames are protected.
Reserve SSID - Toggle the switch to ON to reserve this SSID. When an SSID is reserved, the WLAN will be broadcast only if the AP loses connectivity to the controller or Data Plane. It activates 3 minutes after the heartbeat loss is detected.
Transition Disable Indication - When this option is enabled, the AP will instruct the wireless client to disable certain transition modes for future connections to the AP's network. This information is included in the Transition Disable Key Data Element (KDE). The client should disable all transition algorithms requested if it supports the most secure algorithms. Additionally, the client must disable WEP and TKIP encryption methods and disallow associations without Protected Management Frames (PMF).
OWE
Choosing Opportunistic Wireless Encryption (OWE) for the encryption method in a WLAN provides a balance between security and ease of use. OWE automatically encrypts data between the client and the access point without requiring a pre-shared key, enhancing security for open networks. This method ensures that data is protected from eavesdropping, even on networks that do not require a password for access.
Select OWE, and define the following settings:
Algorithm - Defines the specific cipher used to encrypt data. Choose one of the following:
- AES - Advanced Encryption Standard (AES) is a highly secure encryption algorithm used to protect data. It provides strong security by encrypting data in blocks of 128 bits, making it very difficult for unauthorized users to decrypt the information.
802.11w MFP - Management Frame Protection, which secures management frames from unauthorized alterations, supported by Wi-Fi 4 (802.11n) and later standards. It works by encrypting management frames, ensuring that only authenticated devices can interpret and act on these frames. Select between one of the following options:
- Required: This option mandates the use of MFP. Only wireless clients that support MFP can connect to the network, ensuring that all management frames are protected.
Transition Disable Indication - When this option is enabled, the AP will instruct the wireless clients to disable certain transition modes for future connections to the AP. This information is included in the Transition Disable Key Data Element (KDE). The client should disable all transition algorithms requested if it supports the most secure algorithms. Additionally, the client must disable WEP and TKIP encryption methods and disallow associations without MFP.
OWE-Transition
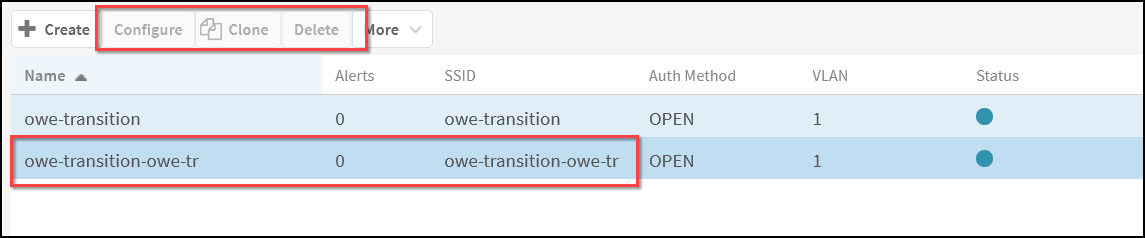
Select OWE-Transition for the encryption method in a WLAN provides a seamless upgrade path from open networks to encrypted ones. This mode supports OWE and adds a traditional open network, allowing devices to connect securely without requiring a pre-shared key. If OWE-Transition is selected, two SSIDs are broadcasted:
- One for OWE-capable clients (unencrypted)
- One for OWE WLAN with an SSID and name set to OWE-Transition's SSID plus "-owe-tr" (encrypted)
WPA-Mixed
Choosing WPA-Mixed for the encryption method in a WLAN provides flexibility by supporting both WPA and WPA2 devices. This mode allows older devices to connect using WPA while newer devices can use the more secure WPA2. It ensures broad compatibility across different devices while maintaining a reasonable level of network security.
Select WPA-Mixed, and define the following settings:
Algorithm - Defines the specific cipher used to encrypt data. Choose one of the following:
- AES - Advanced Encryption Standard (AES) is a highly secure encryption algorithm used to protect data. It provides strong security by encrypting data in blocks of 128 bits, making it very difficult for unauthorized users to decrypt the information.
- AUTO - This setting allows the network to automatically select the best encryption algorithm available. Typically, it will default to AES if all devices on the network support it, ensuring optimal security and compatibility.
Passphrase - A password used to generate the encryption key. It supports from 8 to 70 characters and does not have any requirement for password complexity.
802.11r Fast Roaming - A feature that allows seamless transition between access points. supported by Wi-Fi 5 and Wi-Fi 6 APs. It works by pre-authenticating devices with multiple access points, reducing the time needed to switch connections and ensuring uninterrupted connectivity. Switch the toggle to ON and enter a Mobility Domain ID. The Mobility Domain ID is used by 802.11r to define a scope of the network in which a Fast Roaming is supported. Master keys are shared within the Mobility Domain, allowing clients to support fast roaming.
Dynamic PSK - Choose Disable, Internal, or External radio button.
Reserve SSID - Toggle the switch to ON to reserve this SSID. When an SSID is reserved, the WLAN will be broadcast only if the AP loses connectivity to the controller or Data Plane. It activates 3 minutes after the heartbeat loss is detected.
WEP-64 (40 bits)
Choosing WEP-64 (40 bits) for the encryption method in a WLAN provides a basic level of security by using a 40-bit key for encryption. However, WEP-64 is considered outdated and highly vulnerable to attacks due to its short key length and weaknesses in its encryption algorithm.
WEP-128 (104 bits)
Choosing WEP-128 (104 bits) for the encryption method in a WLAN provides a slightly stronger level of security compared to WEP-64 by using a 104-bit key for encryption. However, like WEP-64, WEP-128 is also considered outdated and vulnerable to attacks due to inherent weaknesses in its encryption algorithm.