Configuring a Rogue Classification Policy
A rogue classification policy can be
created with rules defined at the zone and monitoring group levels, enabling automatic
classification when specified rogue detection criteria are met.
- From the main menu, navigate to .
- Select the zone from the system tree and click Create.
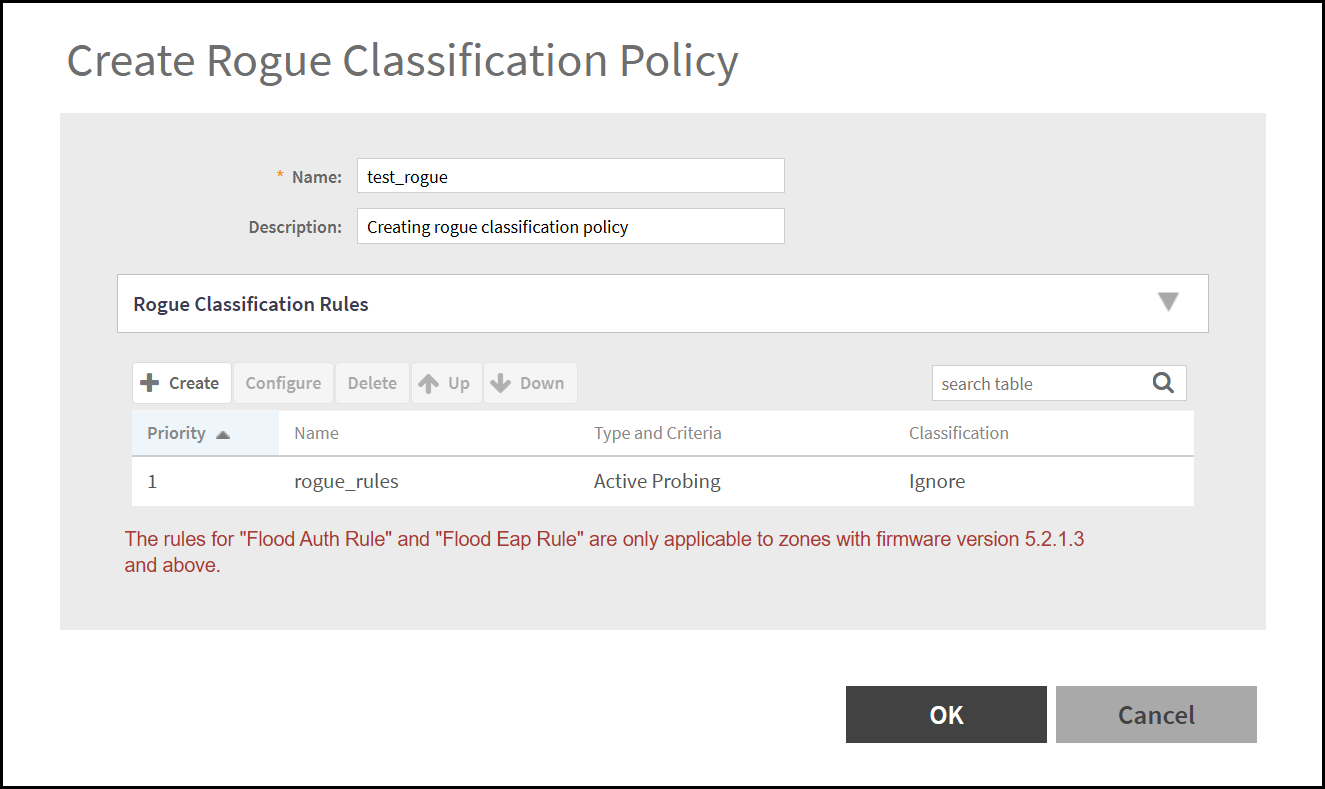
- In the Create Rogue
Classification Policy window, enter the following:
- Name - Enter a unique name to identify the rogue classification policy.
- Description - Enter a brief description to provide additional context for the rogue classification policy.
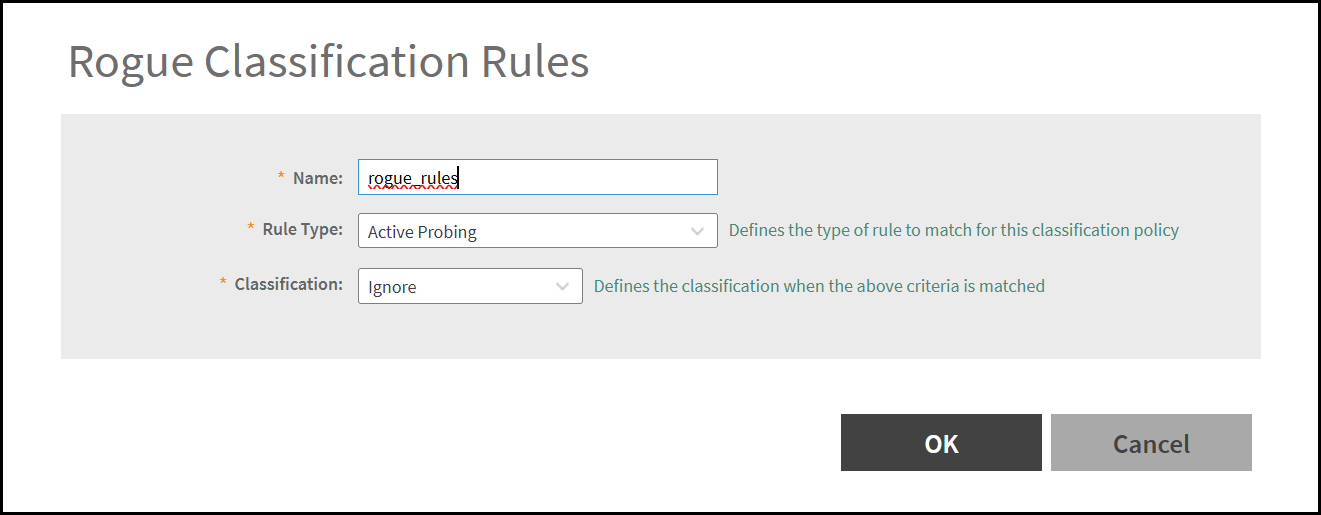
- Rogue Classification Rules - Defines the criteria used to automatically classify detected wireless devices as rogue, friendly, or neighboring. These rules can be applied at the zone or monitoring group level and are based on parameters such as SSID match, MAC address, signal strength, VLAN mismatch, and network connectivity behavior.
- Click OK to create
Rogue Classification Policy.Note: Click Configure or Delete to edit or delete a rogue classification policy. To prioritize a classification rule, select the rule from the list and click Up or Down to position the rule.Note: The user can use command line interface in SZ to disable or change threshold packets per seconds for CTS abuse, RTS abuse, Deauth flood, disassociation flood and other detection types.
- To change the threshold detection follow the command: remote ap-cli <ap-mac> "set rogued <attack-type> <number pf packets>". Example: remote ap-cli 8c:fe:74:1c:d6:b8 "set rogued rtsthreshhold 10"
- To enable / disable flood detection follow the command : remote ap-cli <ap-mac> "set rogued <attack-type> enable/disable". Example: remote ap-cli 8c:fe:74:1c:d6:b8 "set rogued rtsdetect enable"
There are 37 rule types available for creating a rogue classification policy through the SmartZone web interface. However, only 30 of these rule types can be configured through the command-line interface (CLI). Use the following CLI commands to configure the available rule types.
Usage: set rogued
		 -> debug {level} 	<level: 0~7>
		 -> rtsdetect {enable|disable} 	<enable or disable RTS frame detection>
		 -> rtsthreshhold {value} 	<value >= 1, num of frames per second>
		 -> ctsdetect {enable|disable} 	<enable or disable CTS frame detection>
		 -> ctsthreshhold {value} 	<value >= 1, num of frames per second>
		 -> deauthdetect {enable|disable} 	<enable or disable DEAUTH frame detection>
		 -> deauththreshhold {value} 	<value >= 1, num of frames per second>
		 -> disassocdetect {enable|disable} 	<enable or disable DISASSOC frame detection>
		 -> disassocthreshhold {value} 	<value >= 1, num of frames per second>
		 -> authdetect {enable|disable} 	<enable or disable AUTH frame detection>
		 -> auththreshhold {value} 	<value >= 1, num of frames per second>
		 -> eapdetect {enable|disable} 	<enable or disable EAP frame detection>
		 -> eapthreshhold {value} 	<value >= 1, num of frames per second>
		 -> maxclientdetect {enable|disable} 	<enable or disable max client detection>
		 -> maxclientthreshold {value} 	<value >= 1, num of clients per AP>
		 -> ssidlargerthan32 {enable|disable} 	<enable or disable SSID larger than 32 bytes detection>
		 -> weakprotocol {enable|disable} 	<enable or disable weak or outdated protocol detection>
		 -> packetfloodingdetect {enable|disable} 	<enable or disable packet flooding detection>
		 -> pktfloodingthreshhold {value} 	<value >= 1, num of frames per second>
		 -> failureattempt {enable|disable} 	<enable or disable failed attempt to join the WLAN detection>
		 -> failureattemptthreshold {value} 	<value between 3 and 20, num of failed attempts to join the WLAN detection>
		 -> failureattempttimeperiod {value} 	<value between 300 and 900, time period for failed attempts to join WLAN detection>
		 -> signaturedetect {enable|disable} 	<enable or disable signature based detection>
		 -> unauth-p2p {enable|disable} 	<enable or disable unauthorized p2p network detection>
		 -> activeprobing {enable|disable} 	<enable or disable active probing>
		 -> data_unencrypted {enable|disable} 	<enable or disable data unencrypted>
		 -> excessive_transmit_power {enable|disable} 	<enable or disable excessive transmit power>
		 -> whndetect {enable|disable} 	<enable or disable windows hosted network detection>
		 -> icsdetect {enable|disable} 	<enable or disable ICS Connection detection>
		 -> adhocdetect {enable|disable} 	<enable or disable adhoc connection detection>
Note: The preferred method for creating a rogue classification policy is through the SmartZone web interface.