WLAN Data Plane Options
The DP manages the data between wireless clients and the network and applies security policies such as encryption and access control. The APs form an encryption tunnel to the Data Plane and all traffic transmitted from the AP to the Data Plane and back is encrypted.
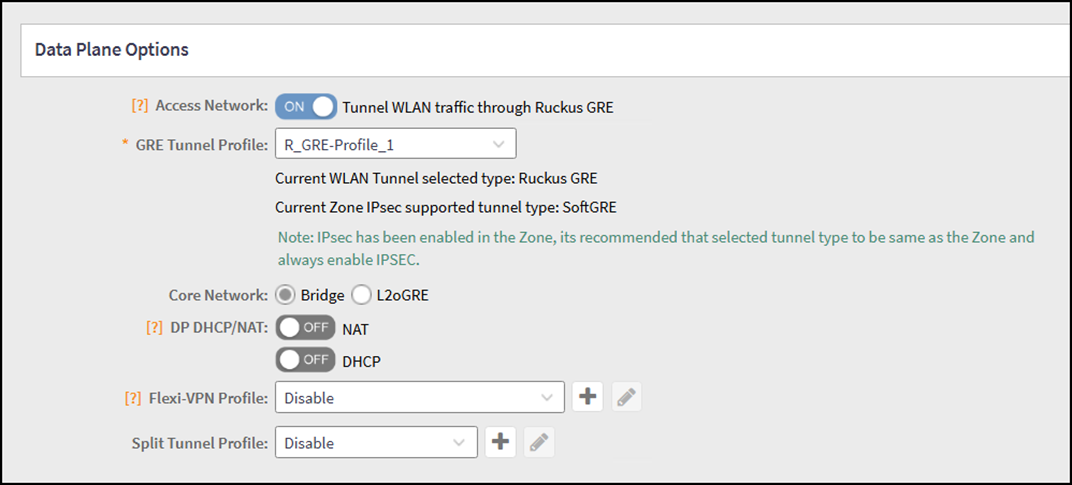
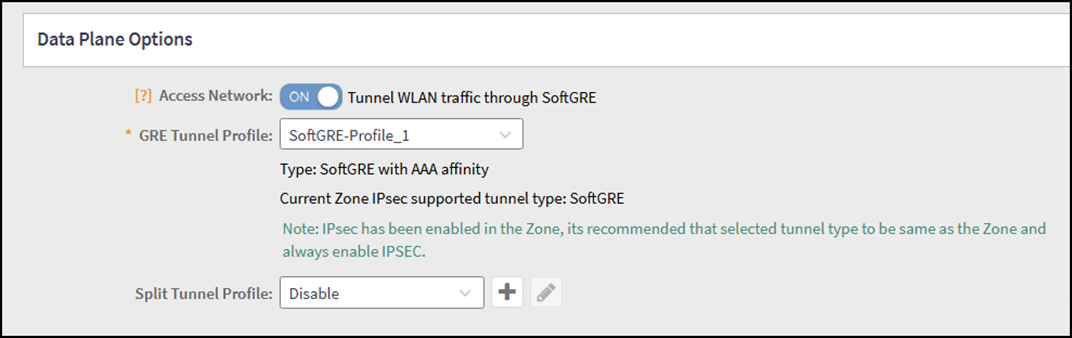
Access Network: Toggle ON Tunnel WLAN traffic through Ruckus GRE to convert this WLAN into a tunneled WLAN. With this setting, the AP tunnels all client traffic (access network) in this WLAN from the AP to the Data Plane. Configure the required parameters as follows:
- GRE Tunnel Profile:
Keep the Default Tunnel Profile or select an existing profile from the list.
Note: Only profiles added to the Zone configuration appear in the list. For instructions on the AP GRE tunnel options at the Zone level, refer to the RUCKUS SmartZone (LT-GA) Access Points and Switch Management Guide.
The options available after selecting the tunnel profile vary depending on the tunnel type selected (RUCKUS GRE or SoftGRE). The UI displays the current WLAN tunnel type selected and the current Zone IPsec supported tunnel type according to the GRE profile configuration selected.
Data Plane options available for RUCKUS GRE tunnel type:
- Core
Network: This field defines what happens to client
traffic after it leaves the Data Plane on its path to the destination
network (core network). Choose between Bridge (the DP
bridges the de-capsulated traffic directly onto the local VLAN or
network segment) and L2oGRE (the DP re-encapsulates the traffic using Layer 2 over
GRE and sends it to a specified GRE endpoint, extending the Layer 2
domain over an IP network).
Note: The L2oGRE option is typically used for remote bridging, and DHCP/NAT services are often provided at the GRE gateway. When selecting this option, you must configure a corresponding Forwarding Profile to specify the GRE endpoint and DHCP/NAT parameters. Refer to Forwarding Profile.
- DP DHCP/NAT: Enable the toggles for Dynamic Host Configuration Protocol (DHCP) and Network Address Translation (NAT) separately depending on your requirement to have the Data Plane providing these services to the tunneled WLAN. RUCKUS recommends that you enable DHCP and NAT together to ensure correct IP addressing for the clients.
- Flexi-VPN Profile: Select a Flexi-VPN profile to configure VPN settings for the tunneled WLAN. This profile defines the VPN parameters and ensures secure communication over the network.
- Split Tunnel Profile: Choose a Split Tunnel Profile to determine how traffic is routed. Split tunneling allows you to direct some traffic through the VPN while other traffic accesses the internet directly. This profile helps optimize network performance and security.
Data Plane options available for SoftGRE tunnel type:
- Core
Network: This field defines what happens to client
traffic after it leaves the Data Plane on its path to the destination
network (core network). Choose between Bridge (the DP
bridges the de-capsulated traffic directly onto the local VLAN or
network segment) and L2oGRE (the DP re-encapsulates the traffic using Layer 2 over
GRE and sends it to a specified GRE endpoint, extending the Layer 2
domain over an IP network).
Forwarding Profile
A forwarding profile defines how client traffic is handled after it leaves the Data Plane. When you select a forwarding profile, you specify the destination and processing for tunneled traffic, such as the DHCP relay actions or the GRE endpoint for L2oGRE encapsulation. Select the appropriate forwarding profile from the drop-down menu. The available options depend on your selection in the Core Network field within the Data Plane Options section:
- If the Core Network
is set to Bridge, the default selection in the drop-down menu is
Factory
Default. Optionally, click
 to create a custom DHCP relay forwarding profile.
- If the Core Network is set
to L2oGRE, select an existing forwarding profile or click
to create a new one.
The system displays this section only if the Access Network toggle button is set to ON in the Data Plane Options section of the Edit or Create WLAN Configuration page.