Site-to-Site VPN: Configuration for an IPv6 Over IPv6 IPsec Tunnel Using Nondefault Settings
An IPsec tunnel is configured by binding an IPsec profile to the virtual tunnel interface
(VTI) at each end of the IPsec tunnel. With nondefault settings for the IPsec tunnel,
the user-defined IKEv2 proposal, IKEv2 policy, IKEv2 auth-proposal, IKEv2 profile,
IPsec proposal, and IPsec profile must be created at the two endpoints. The IKEv2
proposal is tied to the IKEv2 policy, the IKEv2 auth-proposal is tied to the IKEv2
profile, and the IKEv2 profile and IPsec proposal are tied to the IPsec profile.
In the following example, Router1 and Router2 are the devices at each end of the tunnel.
On each device, a nondefault IPsec profile (profA) is created and bound to the VTI
by using the tunnel protection ipsec profile command.
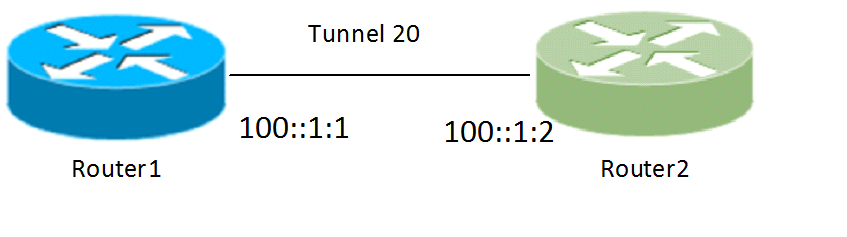
Note: Tunnel endpoints may be multiple hops away and the base path reachable over any interior gateway protocols such as static routing, RIP, OSPF, BGP, and so on.
Configurations
Router1(config)# ikev2 auth-proposal auth_propA
Router1(config-ike-auth-proposal-auth_propA)# pre-shared-key test123
Router1(config-ike-auth-proposal-auth_propA)# exit

Router1(config)# ikev2 proposal propA
Router1(config-ike-proposal-propA)# dhgroup 19
Router1(config-ike-proposal-propA)# no dhgroup 20
Router1(config-ike-proposal-propA)# prf sha256
Router1(config-ike-proposal-propA)# no prf sha384
Router1(config-ike-proposal-propA)# encryption aes-cbc-128
Router1(config-ike-proposal-propA)# no encryption aes-cbc-256
Router1(config-ike-proposal-propA)# integrity sha256
Router1(config-ike-proposal-propA)# no integrity sha384
Router1(config-ike-proposal-propA)# exit

Router1(config)# ikev2 profile profA
Router1(config-ike-profile-profA)# authentication auth_propA
Router1(config-ike-profile-profA)# local-identifier address 1001::1:1
Router1(config-ike-profile-profA)# remote-identifier address 1002::1:1
Router1(config-ike-profile-profA)# match-identity local address 1001::1:1
Router1(config-ike-profile-profA)# match-identity remote address 1002::1:1
Router1(config-ike-profile-profA)# exit

Router1(config)# ikev2 policy polA
Router1(config-ike-policy-polA)# proposal propA
Router1(config-ike-policy-polA)# match address-local 100::1:1/64
Router1(config-ike-policy-polA)# exit

Router1(config)# ipsec proposal propA
Router1(config-ipsec-proposal-propA)# encryption-algorithm aes-gcm-128
Router1(config-ipsec-proposal-propA)# no encryption-algorithm aes-gcm-256
Router1(config-ipsec-proposal-propA)# exit

Router1(config)# ipsec profile profA
Router1(config-ipsec-profile-profA)# proposal propA
Router1(config-ipsec-profile-profA)# ike-profile profA
Router1(config-ipsec-profile-profA)# exit

Router1(config)# interface tunnel 20
Router1(config-tnif-20)# tunnel mode ipsec ipv6
Router1(config-tnif-20)# tunnel protection ipsec profile profA
Router1(config-tnif-20)# tunnel source 100::1:1
Router1(config-tnif-20)# tunnel destination 100::1:2
Router1(config-tnif-20)# ip address 1000::1/64
Router1(config-tnif-20)# exit
Router2(config)# ikev2 auth-proposal auth_propA
Router2(config-ike-auth-proposal-auth_propA)# pre-shared-key test123
Router2(config-ike-auth-proposal-auth_propA)# exit

Router2(config)# ikev2 proposal propA
Router2(config-ike-proposal-propA)# dhgroup 19
Router2(config-ike-proposal-propA)# no dhgroup 20
Router2(config-ike-proposal-propA)# prf sha256
Router2(config-ike-proposal-propA)# no prf sha384
Router2(config-ike-proposal-propA)# encryption aes-cbc-128
Router2(config-ike-proposal-propA)# no encryption aes-cbc-256
Router2(config-ike-proposal-propA)# integrity sha256
Router2(config-ike-proposal-propA)# no integrity sha384
Router2(config-ike-proposal-propA)# exit

Router2(config)# ikev2 profile profA
Router2(config-ike-profile-profA)# authentication auth_propA
Router2(config-ike-profile-profA)# local-identifier address 1002::1:1
Router2(config-ike-profile-profA)# remote-identifier address 1001::1:1
Router2(config-ike-profile-profA)# match-identity local address 1002::1:1
Router2(config-ike-profile-profA)# match-identity remote address 1001::1:1
Router2(config-ike-profile-profA)# exit

Router2(config)# ikev2 policy polA
Router2(config-ike-policy-polA)# proposal propA
Router2(config-ike-policy-polA)# match address-local 10.1.1.2 255.255.255.255
Router2(config-ike-policy-polA)# exit

Router2(config)# ipsec proposal propA
Router2(config-ipsec-proposal-propA)# encryption-algorithm aes-gcm-128
Router2(config-ipsec-proposal-propA)# no encryption-algorithm aes-gcm-256
Router2(config-ipsec-proposal-propA)# exit

Router2(config)# ipsec profile profA
Router2(config-ipsec-profile-profA)# proposal propA
Router2(config-ipsec-profile-profA)# ike-profile profA
Router2(config-ipsec-profile-profA)# exit

Router2(config)# interface tunnel 20
Router2(config-tnif-20)# tunnel mode ipsec ipv4
Router2(config-tnif-20)# tunnel protection ipsec profile profA
Router2(config-tnif-20)# tunnel source 10.1.1.2
Router2(config-tnif-20)# tunnel destination 10.1.1.1
Router2(config-tnif-20)# ip address 10.0.0.2 255.255.255.0
Router2(config-tnif-20)# exit