Creating Switch Model-Based Configurations
You can create and edit ACL, Layer 2, and Layer 3 configuration settings for a family of switches. You can also create or update the ACL to configure QoS profiles that prioritize VOIP and VIDEO VLAN traffic.
- On the menu, click to display the Switches window.
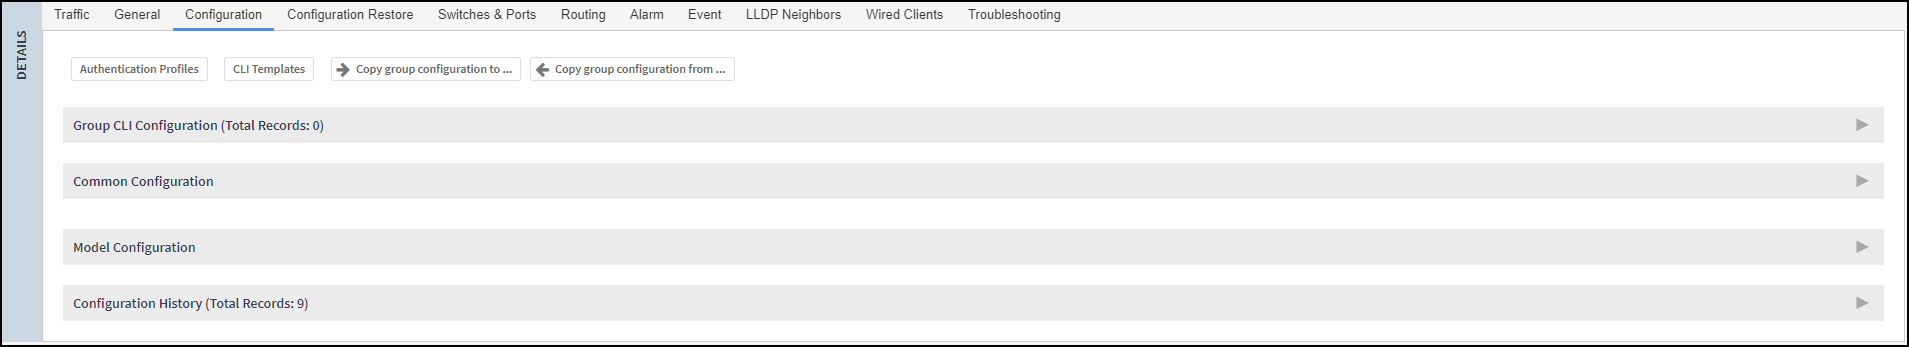
- Select or Switch Group and click the Configuration tab.
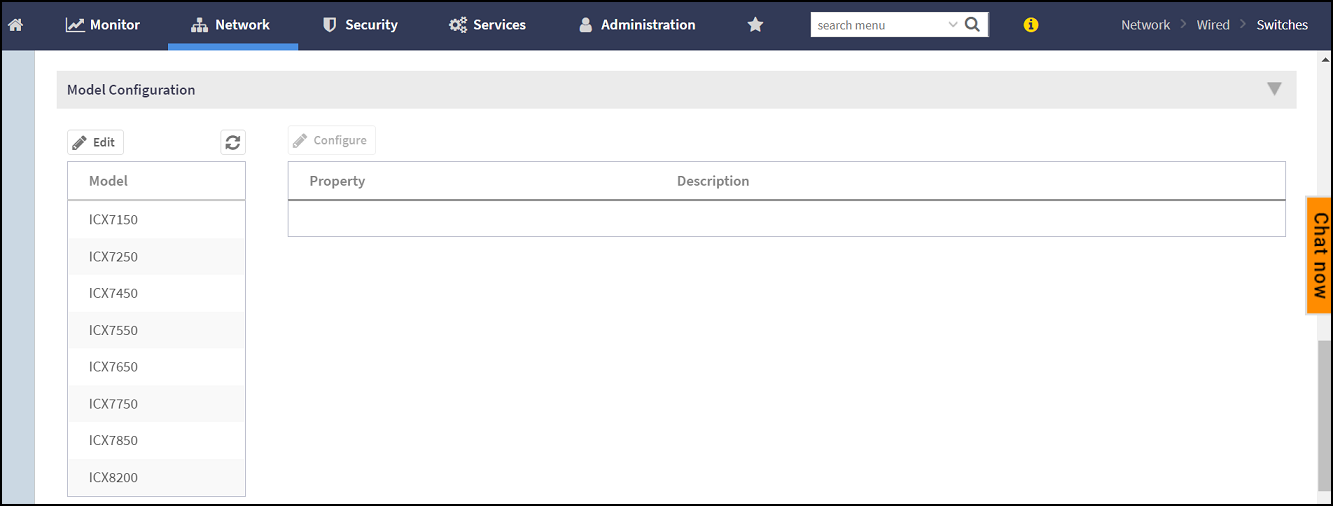
- In the Model Configuration, select the Switch Model from
the drop down list and click Configure to display the
Feature Configuration dialog box.Note: The Feature Configuration page displays details about the ACL, VLAN, and static route. You can create, edit, and delete these configurations as necessary.
- Configure the
ACL settings.
- Click the ACL tab.
- Click Create display the ACL fields.
- Complete the
following fields:
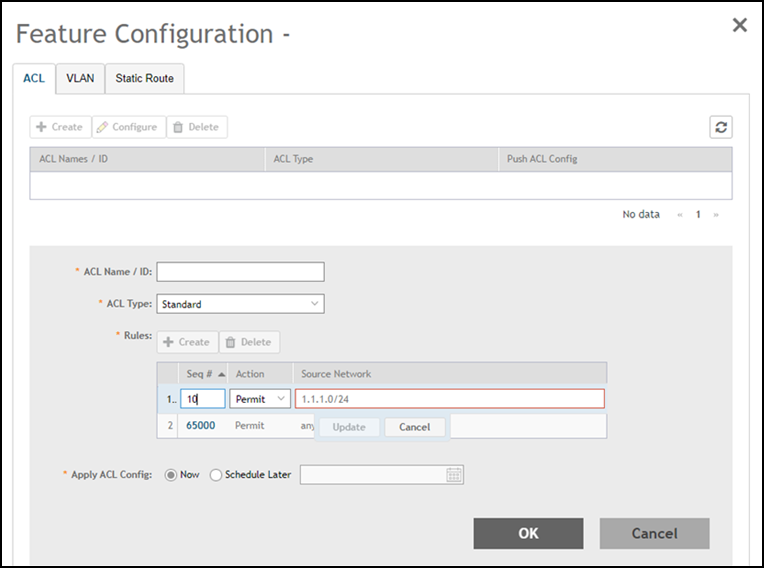
- ACL Name/ID: Enter the name of the access control list or provide the list identifier.
- ACL Type: Select Standard or Extended from the drop down list.
- Rules: Click Create to create an ACL rule.
- Complete the following fields to configure the
following ACL rule for the Standard ACL type:
You must provide the list sequence (Seq#), Action (Permit or Deny) and Source Network information to create the rule.
Note: Controller supports the "equal to" operator only. - Complete the following fields to configure the
following ACL rule for the Extended ACL type:
- Seq#: Enter the sequence.
- Action: Select Permit or Deny.
- Source Network: Enter the source network.
- Destination Network: Enter the destination network.
- Source Port: By default port 22 is selected.
- Destination Port: By default port 22 is selected.
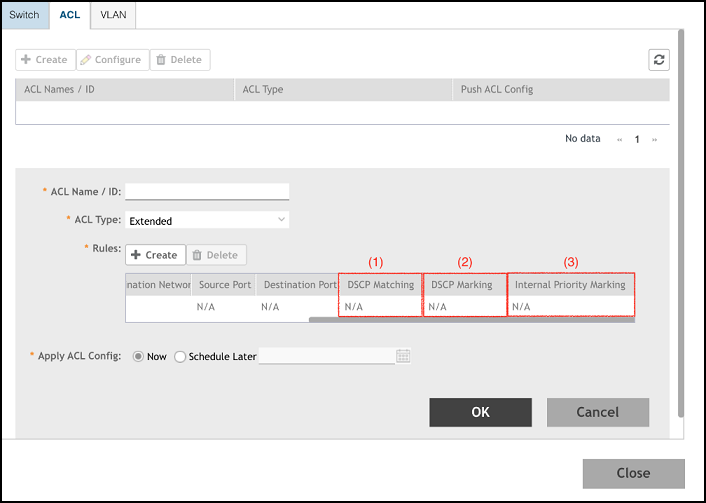
- DSCP Matching: Enter the DSCP matching.
- DSCP Marking: Enter the DSCP marking.
- Internal Priority Marking: Enter the internal priority marking.
- Complete the following fields to configure the
following ACL rule for the Standard ACL type:
- Apply ACL Config: Select Now or Schedule Later. If you choose to schedule the configuration deployment for later, provide the time and date.
- Click OK to add the newly created ACL configuration to the ACL page. You can edit the configuration by selecting Configure.
- Configure the
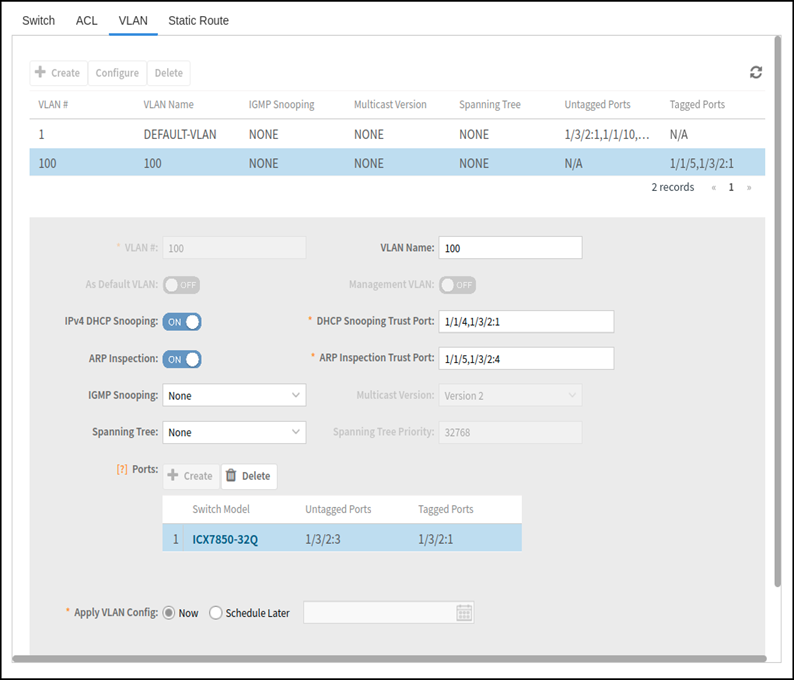
VLAN settings.
- Complete the
following VLAN fields:
- VLAN #: Enter the number of the VLAN.
- VLAN Name: Enter the name of the Layer 2 VLAN.
- As Default VLAN: If you enable the As Default VLAN the VLAN Name is changed to DEFAULT-VLAN and the Management settings correspond to the previous VLAN settings.
- Management VLAN: By enabling this, you can configure Management VLAN for the switches or switch groups.
-
7.0 Beta FeatureIPv4 DHCP Snooping: Enable or disable IPv4 DHCP Snooping. Enabling this option allows the controller to send the ACL-per-port-per-VLAN message to the switch to reboot it. If you enable IPv4 DHCP Snooping, you must provide the breakout port for this option in the DHCP Snooping Trust Port field.
-
7.0 Beta FeatureAPR Inspection: Enable or disable ARP Inspection. Enabling this option allows the controller to send the ACL-per-port-per-VLAN message to the switch to reboot it. If you enable IPv4 DHCP Snooping, you must provide the breakout port for this option in the ARP Inspection Trust Port field.
- IGMP Snooping: Select None, Active, or Passive from the list. The Internet Group Management Protocol (IGMP) allows the switch to track the communication between hosts and routers based on which the switch maintains a map of which links need which IP multicast streams. If you select Active or Passive, you are required to select the Multicast Version as well.
- Spanning Tree: Select None, STP (802.1d), or RSTP (802.1w) from the list. Both Spanning Tree Protocol (STP) and Rapid Spanning Tree Protocol (RSTP) prevent creation of bridge loops when you have redundant paths in your network, and the broadcast radiation that results from them. If you select STP 802.1d or RSTP 802.1w, you are required to select the Spanning Tree Priority as well.
- Ports: Click Create and complete the following
fields:
Note: Different set of ports can be entered for each switch model.
- Apply VLAN Config: Select Now or Schedule Later. If you choose to schedule the configuration deployment for later, provide the time and date.
- Click OK to add the newly created VLAN configuration to the VLAN page.
Note: You can also edit and delete the VLAN configuration by selecting the options Configure and Delete respectively, from the VLAN tab.Note: Beginning with the 7.0 release, when you modify the VLAN # and VLAN Name , the ICX System log displays the SZ Administrator name associated with this configuration activity. In the earlier releases, the ICX System log showed a generic message indicating that the network controller made the change.
- Complete the
following VLAN fields:
- Configure the
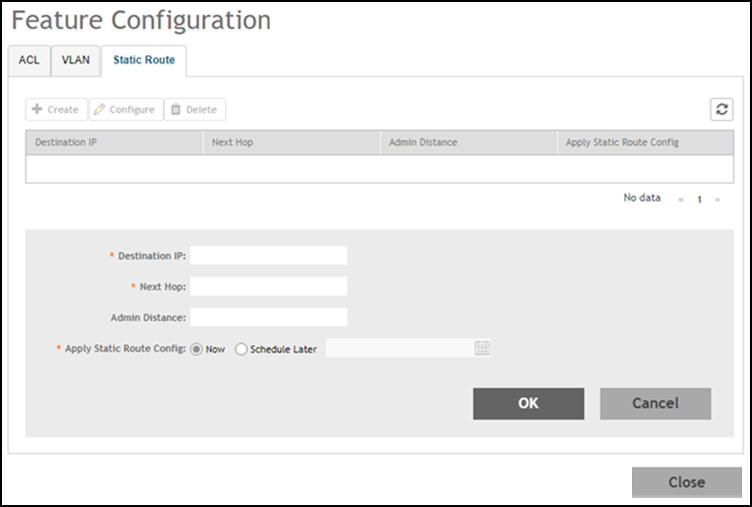
Static Route settings.
- Click the Static Route tab.
- Click Create to display the Static Route fields.
- Complete the
following Static Route fields:
- Destination IP: Enter the destination IP address.
- Next Hop: Enter the next-hop IP address. Multicast and broadcast IP addresses are not allowed.
- Admin Distance: Enter a value from 1 through 255.
- Apply Static Route Config: Select Now or Schedule Later. If you choose to schedule the configuration deployment for later, provide the time and date.
- Click OK to add the newly created static route configuration to the Static Route page.
- Click Close.
The IP address is added to the Model Configuration page under Property. If you want to edit the configuration, select it and click Edit to edit the settings.Note: Any changes made to the group level configuration including common configuration and switch model-based configuration will be applied to all the switches belonging to the group.Configuration defined at group level can be chosen to be applied instantaneously by selecting the Now option or schedule for a later time using Schedule later option. The scheduling option is only applicable if you are trying to make changes to existing switches in the group. For any new switches that are joining the group, this configuration gets applied instantaneously.
- Configure the
ACL settings.