Creating a Hotspot (WISPr) Portal

To create a hotspot service, you must define the required basic settings.
SZ supports only one grace period, session timeout, UTP, VLAN and all UE session related configuration. These configurations for the first WLAN do not work when the UE joins the second WLAN. The configuration works only when the UE roams within the cluster node. The configurations do not work when the client roams from one zone to another zone or from one cluster to another cluster.

Before creating a hotspot, you need to create a user defined interface.

  1. Select Services > Hotspots & Portals > Hotspot (WISPr). The Hotspot (WISPr) page is displayed.

    Hotspot (WISPr)

  2. In the Organization tab, select a Zone from the system tree and click Create.
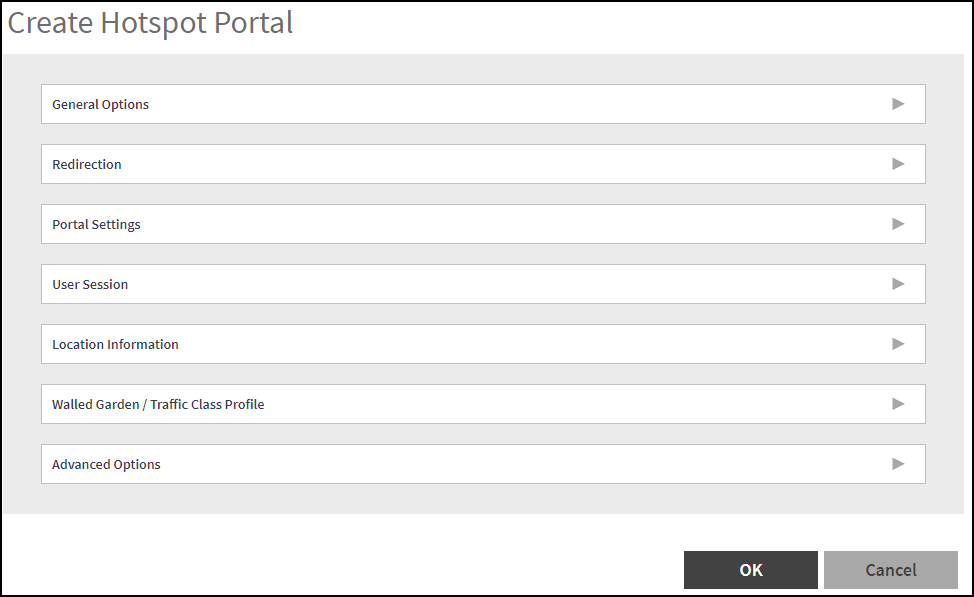
  3. Click Create. The Create Hotspot Portal dialog box is displayed.

    Creating a Hotspot (WISPr) Portal

  4. Complete the following fields:
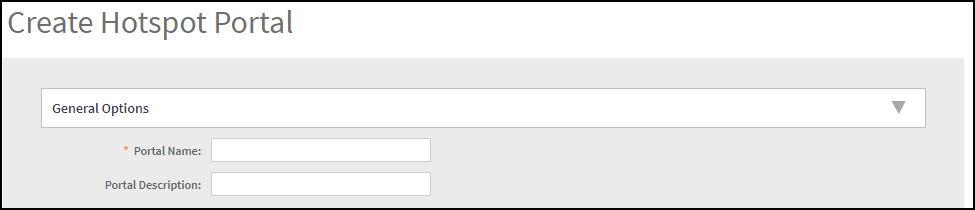
    1. General Options

      Create Hotspot Portal - General Options

      • Portal Name: Type a name for the hotspot portal that you are creating.
      • Portal Description: Type a short description of the hotspot portal.
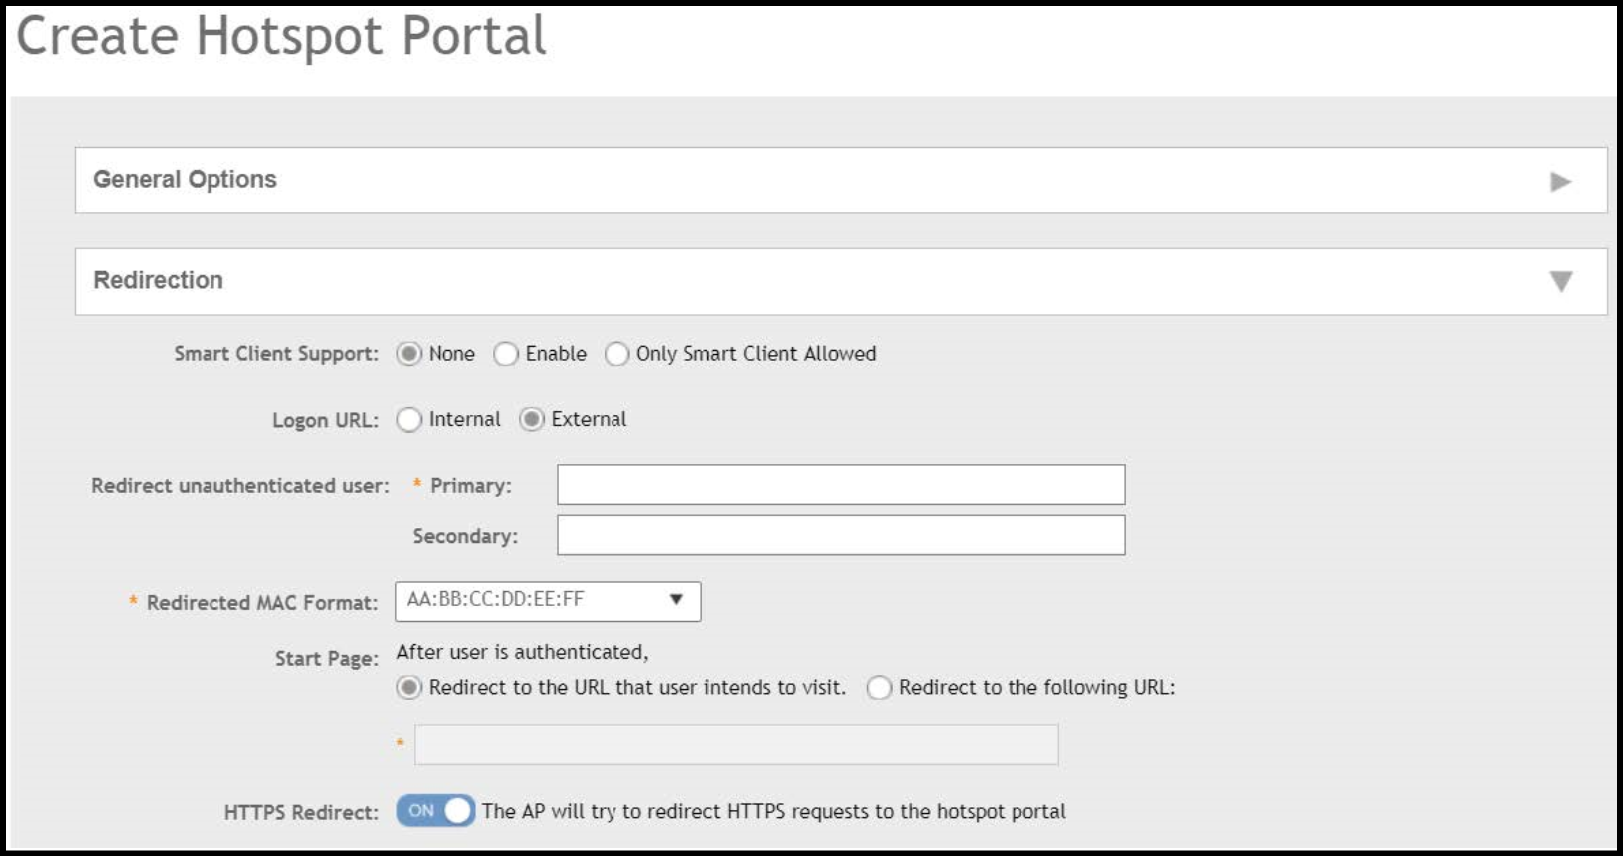
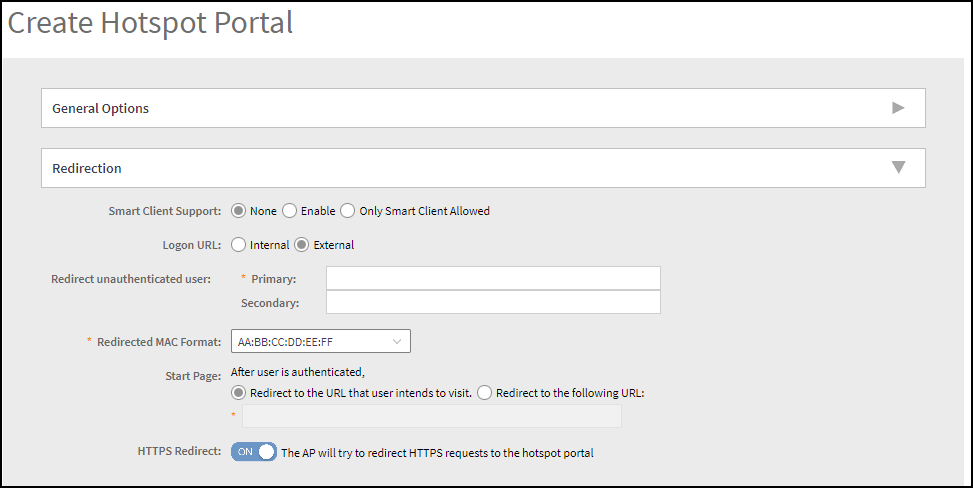
    2. Redirection

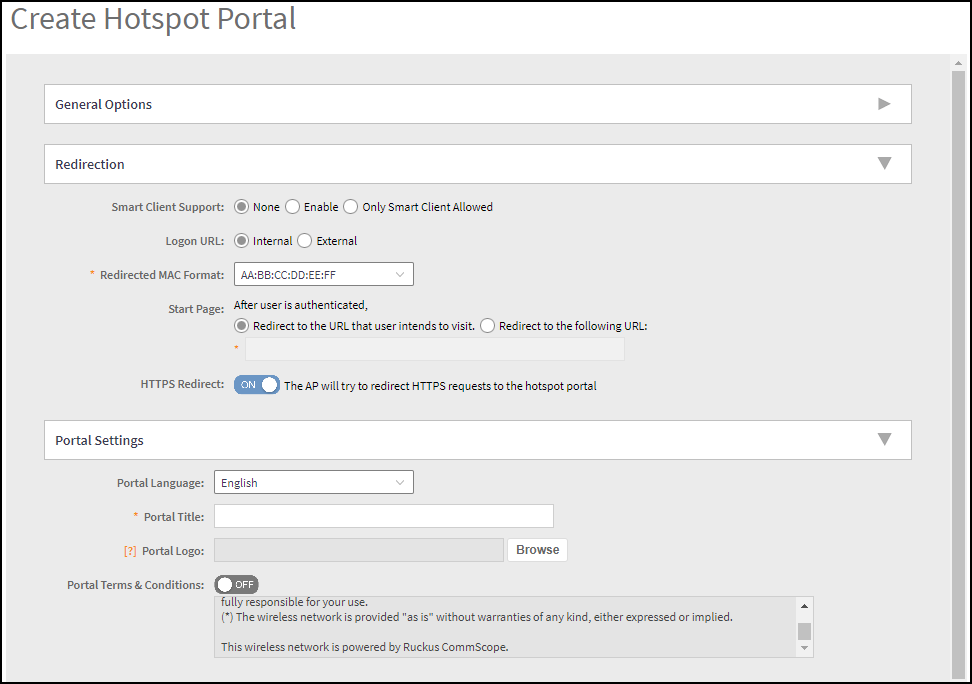
      Create Hotspot Portal

      • Smart Client Support: Select one of the following options:
        • None: Disables Smart Client Support on the hotspot service.
        • Enable: Enables Smart Client Support.
        • Only Smart Client Allowed: Allows only Smart Clients to connect to the hotspot service.
      • Logon URL: Select one of the following options:
        • Internal: Indicates the internal URL of the subscriber portal (where hotspot users can log in to the service). If you select Internal, you have to manually configure the following Portal Settings.

          Create Hotspot Portal: Logon URL-Internal

          • Portal Language: Select the required language from the drop down list.
          • Portal Title: Enter the portal title.
          • Portal Logo: Click Browse to upload the portal logo.
          • Portal Terms & Conditions: Switch ON to accept the portal terms and conditions.
        • External: Indicates the external URL of the subscriber portal.

          Selecting External provides an option to reroute an unauthorized user to a primary location. You can set the primary location in Redirect unauthenticated user. If an unauthorized user is rerouted, the AP redirects the UE to a backup portal.

          The AP subscriber portal supports ZD-style API to login and logout. A customer can use AP IP address to submit the login or logout request.

      • Redirect unauthenticated user: APs can perform WISPr redirection. Native WISPr support is available on SZ-managed APs even if access to SZ is not available. It supports external portal redirection with survivability when APs cannot reach the centralized SZ. It also supports backup portal redirection if primary portal is down. The WISPr authentication load can be distributed to AP or use an AP as a WISPr authentication backup.

        WISPr redirection and survivability is supported only on Ruckus 11AC Wave 1 and later APs. Only ZD-style external WISPr is supported. No NBI is supported for backup.

        Note: The AP uses the secondary portal when the AP cannot access the primary portal.

        • Primary: Redirects an unauthenticated user to a specified URL for authentication.
        • Secondary: Redirects an unauthenticated user to the backup external portal if the primary URL is down. The AP periodically accesses the primary portal URL to detect and check the availability of the primary URL.
      • Redirected MAC Format: Enter the format of the redirection MAC address.
      • Start Page: Select one of the following options:
        • Redirect to the URL that the user intends to visit: Redirects users to the page that they want to visit.
        • Redirect to the following URL: Sets a different page where users will be redirected (for example, your company website). Enter a domain name or an IP address to be redirected.
      • HTTPS Redirect: Switch ON HTTPS Redirect, if you want the AP to redirect HTTPS requests to the hotspot portal. HTTPS requests are dropped if this option is disabled.
    3. User Session

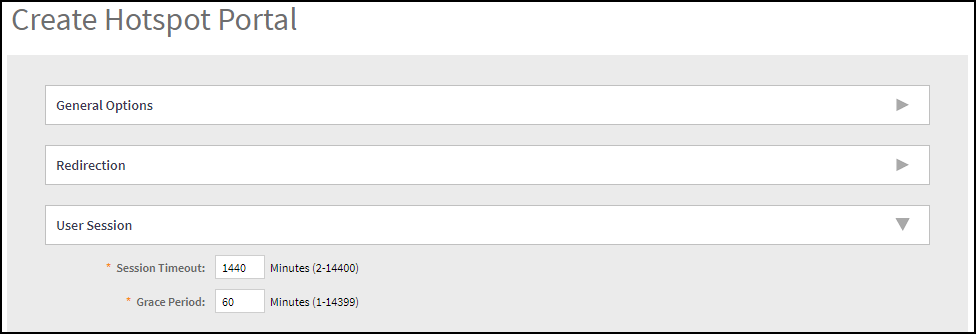
      Create Hotspot Portal - User Session

      • Session Timeout: Sets a time limit (in minutes) after which users will be disconnected from the hotspot service and required to log in again.
      • Grace Period: Sets the time period (in minutes) during which disconnected users are allowed access to the hotspot service without logging in again.
    4. Location Information

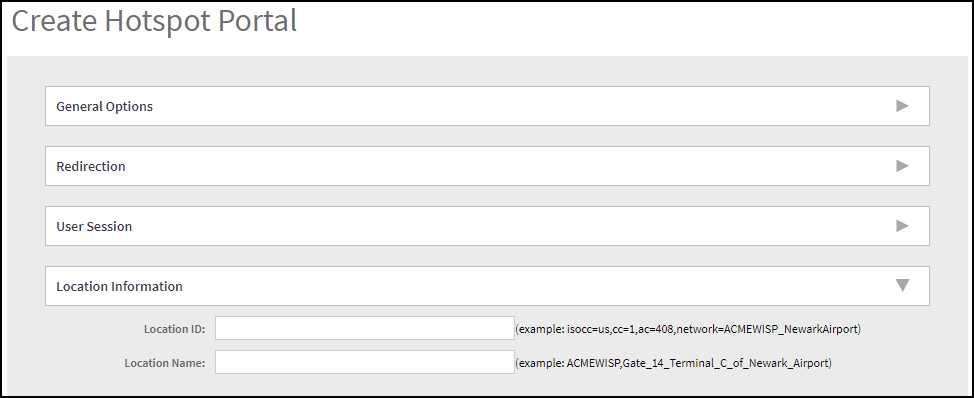
      Create Hotspot Portal - Location Information

      • Location ID: enter the ISO and ITU country and area code that the AP includes in accounting and authentication requests. The code includes the following requirements:
        • isocc (ISO-country-code): The ISO country code that the AP includes in RADIUS authentication and accounting requests.
        • cc (country-code): The ITU country code that the AP includes in RADIUS authentication and accounting requests.
        • ac (area-code): The ITU area code that the AP includes in RADIUS authentication and accounting requests.
        • network: Name of the network.

        The following example illustrates a proper location ID entry: isocc=us, cc=1, ac=408, network=Ruckus

      • Location Name: Enter the name of the location of the hotspot service.
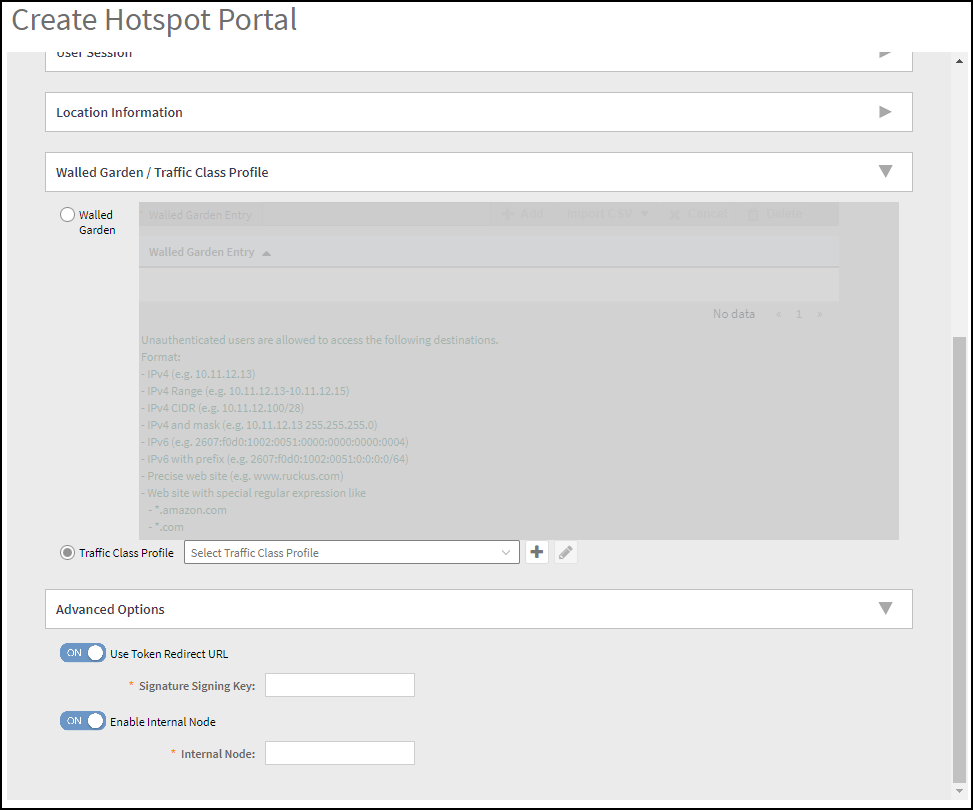
    5. Walled Garden/Traffic Class Profile

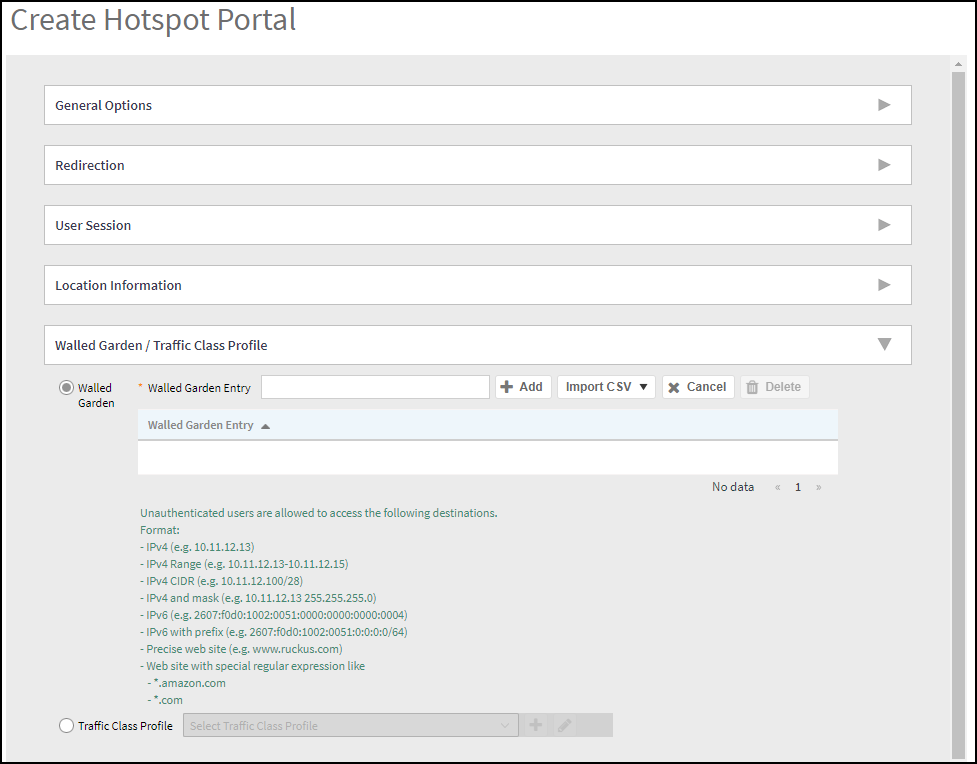
      Create Hotspot Portal - Walled Garden/Traffic Class Profile

      • Walled Garden
        • Walled Garden Entry Add: Enter an IP address or a domain name and click Add to add a Walled Garden Entry.
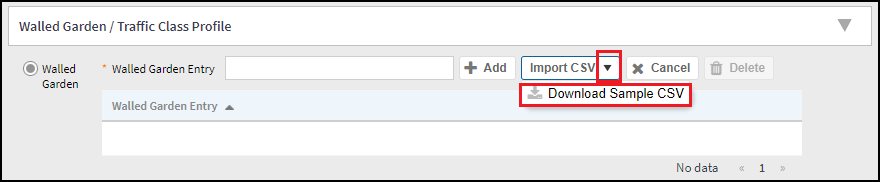
        • Walled Garden Entry Import:

          Walled Garden Entry - Import

          • Click drop-down arrow corresponding to the Import CSV and select Download Sample CSV and download the sample file.
          • Add the user information in the download sample CSV excel file.
          • Click Import CSV and import the sample CSV excel file.
      • Traffic Class Profile: Select a traffic class profile from the drop down list or click the icon to create a traffic class profile. Refer to Creating a Traffic Class Profile in the RUCKUS SmartZone Security Guide for more information.
    6. Advanced Options
      Note: This option is available only if the Traffic Class Profile option is enabled.

      Create Hotspot Portal - Advanced Options

      • Use Token Redirect URL: Switch ON Use Token Redirect URL and enter a signature signing key.
      • Enable Internal Node: Switch ON Enable Internal Node and enter the internal node.

      Note: If an Internal node is enabled, then only one IP is used and the IP domain name and IP ranges are not supported.

  5. Click OK.
Note: If Traffic Class Profile or Use Token Redirect URL is enabled, Smart Client Support is set to None.
Note: You can also edit, clone, and delete a Hotspot (WISPr) portal by selecting the options Configure, Clone, and Delete respectively, from the Hotspot (WISPr) window.