Creating Non-Proxy Authentication AAA Server
A non-proxy AAA server is used when APs
connect to the external AAA server directly.
- Go to .
- Select a Zone from the system tree and click Create.
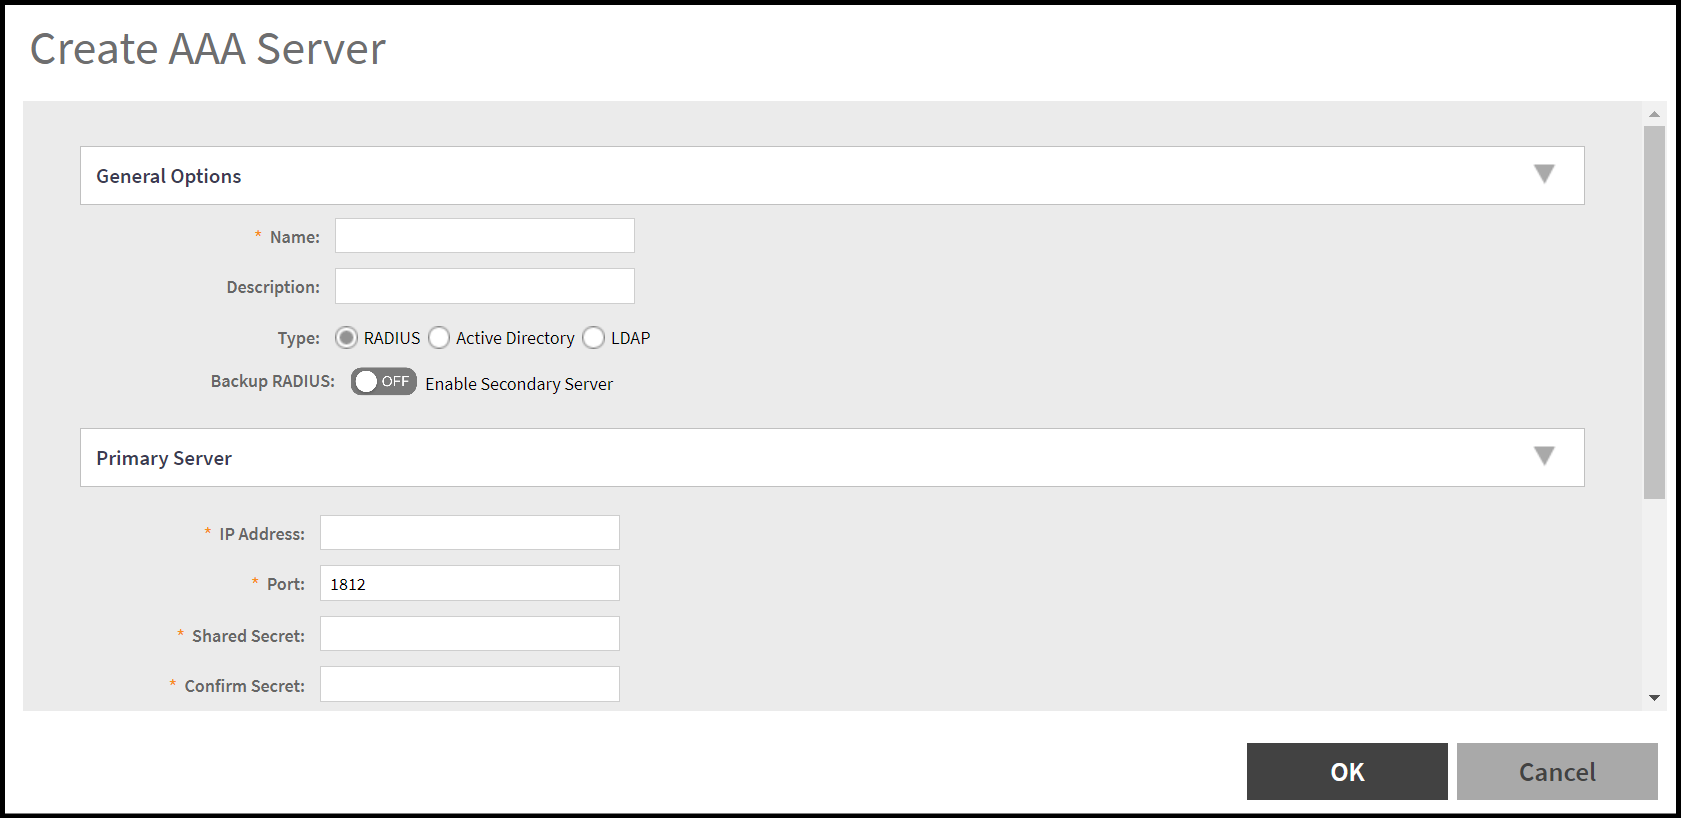
- Configure the following options:
- General Options
- Name: Name the AAA server that you are creating.
- Description: Short description of the AAA server.
- Type: Select the type of AAA server that you are creating. Options include RADIUS, Active Directory and LDAP.
- Backup RADIUS : If secondary RADIUS server exists on the network then only toggle the button to ON to enable the Secondary Server option.
- Primary Server
- If you select the type as RADIUS, configure the following options:
- IP Address: The IP address of the AAA server. Both IPv4 and IPv6 addressing formats are supported.
- Port: The port number of the AAA server. The default RADIUS server port number is 1812.
- Shared Secret: The AAA shared secret.
- Confirm Secret: Re-enter the shared secret to confirm.
If you have enabled the secondary server for Backup RADIUS, you must provide similar information as in the primary server.
- If you select the type as Active
Directory, configure the following options:
- IP Address: Enter the IPv4 address of the Active Directory server.
- Port: Enter the port number of the Active Directory server. The default port number (389) must not be changed unless you have configured the Active Directory server to use a different port.
- Windows Domain Name: Enter the Windows domain name assigned to the Active Directory server (for example, domain.ruckuswireless.com).
- If you select the type as LDAP, configure the following options:
- IP Address: Enter the IPv4 address of the LDAP server.
- Port: Enter the port number of the LDAP server. The default port number is 389.
- Base Domain Name: Enter the base domain name in LDAP format for all user accounts (for example, dc=ldap,dc=com).
- Admin Domain Name: Enter the administrator domain name in LDAP format (for example, cn=Admin;dc=Your Domain,dc=com).
- Admin Password: Enter the administrator password for the LDAP server.
- Confirm Password: Re-enter the administrator password to confirm.
- Key Attribute: Enter a key attribute to denote users (for example, default: uid)
- Search Filter: Enter a search filter (for example, objectClass=Person).
- If you select the type as RADIUS, configure the following options:
- General Options
- Under User Role
Mapping, Note: While mapping group attribute value to a user role, avoid special characters, wild-card entries, or duplicate entries regardless of the order. Only the first-matched entry will be mapped to the user role.
- Click + Create. The Create User traffic Profile Mapping dialog box is displayed
- In the Group Attribute Value field, enter the value to be sent from AAA as part of an Access-Accept.
- Click OK
- Select a user role from the User Role list or click + to create a user role. For more information, refer to User Roles in User Management Guide.
- Click OK.
Note: You can also edit, clone and delete
an AAA server by selecting the options Configure, Clone, and Delete, respectively,
from the Non-Proxy (AP
Authenticator) tab.