Application Logs
The following table lists the controller applications that are running.
System Applications for SmartZone and Virtual SmartZone
| Application | Description |
|---|---|
| API | The application program interface (API) provides an interface for customers to configure and monitor the system, allowing external applications or users to send commands, retrieve data, and automate tasks without needing direct access to the system. |
| CaptivePortal | CaptivePortal performs portal redirect for clients and manages the walled garden and blacklist. It intercepts client requests and redirects them to a login or authentication page before granting broader internet access. |
| Cassandra | The controller database server that stores most of the run-time information and statistical data. |
| Ccmd | Central Command Daemon responsible for orchestrating control plane operations across the controller cluster. In logs, it typically records cluster coordination activities, configuration propagation, and failover handling. |
| CcmSync | Synchronization service for configuration and state data across cluster nodes, ensuring consistency in distributed deployments. Logs often reflect sync status, version mismatches, and replication consistency checks. |
| Collectd | System statistics collection daemon that gathers performance metrics (CPU, memory, disk, and so on.) for monitoring and analytics. It logs periodic metric snapshots, plugin activity, and any data collection errors. |
| Communicator | Communicates with access points and retrieves statuses, statistics, and configuration updates. |
| Configurer | Performs configuration synchronization and cluster operations (for example, join, remove, upgrade, backup, and restore). |
| Core | Foundational service layer that handles base controller functions, including service registration, inter-process communication, and lifecycle management. Logs show service lifecycle events such as startup, shutdown, and registration. |
| DeviceManager | Manages lifecycle and configuration of connected devices (APs, switches), including provisioning, firmware updates, and policy enforcement. Logs typically include onboarding events, configuration pushes, and device status changes. |
| Diagnostics | An interface that can be used to upload scripts (.ksp files) for troubleshooting or applying software patches. This interface displays the diagnostic scripts and system patch scripts that are uploaded to a node. |
| ElasticSearch | ElasticSearch is a scalable real-time search engine used in the controller, enabling fast and efficient indexing, querying, and analysis of large volumes of data. Integrated into the system, it allows for real-time monitoring, logging, and searching across various datasets. |
| EventReader | Receives event messages from access points and saves the information to the database. |
| GuestPassAuthenticator | Handles guest access workflows such as authenticating guest users, managing guest pass issuance, and integrating with captive portal systems. Logs capture guest login attempts, pass generation, and authentication outcomes. |
| LogMgr | Organizes the application logs into a common format, segregates them, and copies them into the respective application log files. |
| MdProxy | MdProxy on the AP and controller connect to AP-MD and controller-MD, respectively. MdProxy on the controller receives messages and retrieves the message header. It also forwards the response to controller-MD. This message is sent to MdProxy on the AP through AP-MD. MdProxy on the AP removes the MSL header and responds to the connection on which the request was received. |
| MemCached | The controller memory cache that stores client authentication information for fast authentication or roaming. |
| MemProxy | Replicates MemCached entries to other cluster nodes. |
| Mosquitto | A lightweight method used to carry out messaging between Location-Based Services (LBS) and APs. |
| MrProxy | Proxy service for management requests that routes or translates application programming interface (API) calls between internal modules or external clients. Logs often show request routing, proxy errors, and timeout events. |
| MsgDist | The message distributor (MD) maintains a list of communication points for both local applications and remote MDs to perform local and remote routing. |
| NginX | A web server that is used as a reserve proxy server or an HTTP cache. |
| Northbound | The interface between a service provider (SP) and Authentication, Authorization, Accounting (AAA) servers, facilitating UE authentication and approval or denial of UEs to APs. |
| Observer | Monitoring and telemetry service that tracks system health, logs events, and may feed data into analytics platforms. Logs include health check results, alert triggers, and telemetry export statuses. |
| RabbitMQ | Message broker that facilitates asynchronous communication between microservices. Logs detail queue operations, message delivery status, and broker health metrics. |
| RadiusProxy | Sets the RADIUS dispatch rules and synchronizes configuration to each cluster node |
| Redis | In-memory data store used for caching, session management, and fast access to frequently used data. Logs show cache hits and misses, eviction events, and connection diagnostics. |
| ScgUniversalExporter | Exports metrics and logs to external systems (for example, Prometheus, Grafana) for observability and monitoring. Logs typically include export success/failure, endpoint reachability, and data formatting issues. |
| Scheduler | Performs task scheduling and aggregates statistical data. |
| SessMgr | Session Manager that tracks client sessions, including authentication state, roaming, and policy enforcement. Logs reflect session creation, updates, disconnects, and policy enforcement actions. |
| SNMP | Provides a framework for the monitoring devices on a network. The SNMP manager is used to control and monitor the activities of network hosts using SNMP. As an agent that responds to queries from the SNMP Manager, SNMP Traps with relevant details are sent to the SNMP Manager when configured. |
| SubscriberManagement | Maintains local user credentials for WISPr authentication. |
| SubscriberPortal | Internal portal page for Hotspot (WISPr). |
| Switchm | Switch Manager that oversees ICX switch discovery, configuration, firmware management, and telemetry. Logs capture switch onboarding, configuration deployment, and telemetry data collection. |
| System | Collects and sends log information from all processes. |
| Web | Runs the controller management web server. |
Application logs store different types of information:
- Event Details: Specific events such as user logins, device connections, and configuration changes.
- Error Messages: Errors and warnings encountered by applications, aiding in diagnostics.
- Performance Metrics: Data on network and controller performance, including CPU and memory usage.
- Security Alerts: Potential security threats, such as unauthorized access attempts.
You can adjust application logs to record up to the specified levels: Error, Warning, Info, Debug. The Debug level, which consumes significant memory, should only be used when requested by RUCKUS Support during specific troubleshooting periods.
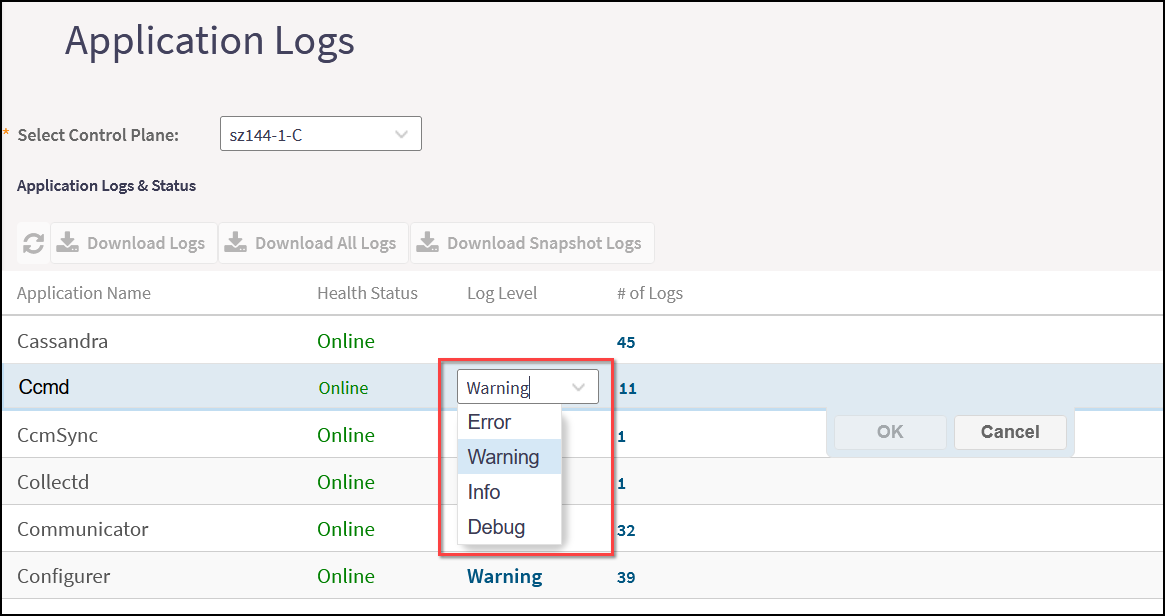
Application logs are essential for troubleshooting within the SmartZone environment. They provide a detailed record of system activities, offering critical insights into network health and performance.
Reviewing the application logs allows RUCKUS Support to pinpoint root causes. For example, connectivity issues may be traced to logs from DeviceManager, revealing offline or misconfigured access points. High CPU or memory usage indicated in logs from Core suggests the need for optimization.
Security alerts in logs help detect and respond to threats. Multiple failed login attempts in CaptivePortal logs may indicate a brute-force attack, prompting immediate actions like blocking the offending IPs to secure the network.