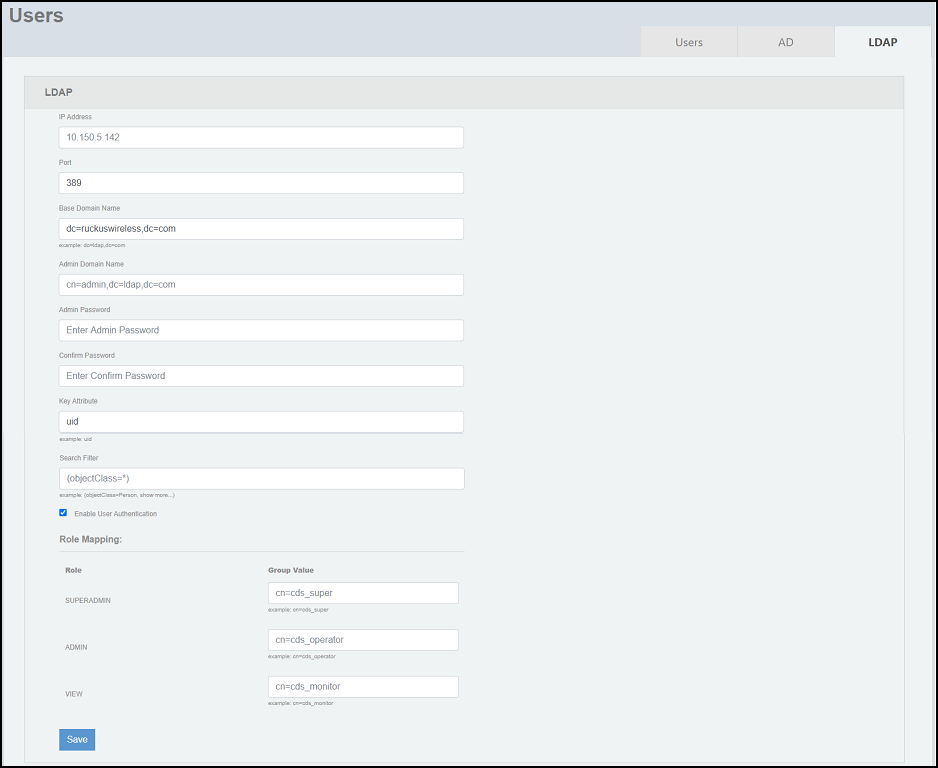
Configuring LDAP Settings
To enable user authentication through
LDAP, create LDAP settings by completing the following steps.
- On the menu, go to
Admin >
Users.
The Users window is displayed.
- In the Users window, select the LDAP tab.
- Click Create LDAP Settings.
- Complete the following fields to configure LDAP server credentials.
- IP Address: Enter the IPv4 address of the LDAP server.
- Port: Enter the port number of the LDAP server. Default is 389.
- Base Domain Name: Enter the base DN in LDAP format for all user accounts.
- Admin Domain Name: Enter the admin DN in LDAP format.
- Admin Password: Enter the administrator password for the LDAP server.
- Confirm Password: Retype the administrator password to confirm.
- Key Attribute: Enter a key attribute to denote users (for example, default: uid)
- Search Filter: Enter a search filter
- Enable User Authentication: If selected, the user will be authenticated and can login through LDAP.
- Role Mapping: Based on the LDAP group ID for the users, the user roles can be mapped in the RUCKUS Network Director to integrate with LDAP. This establishes the mapping between the user attributes and the user roles, to authenticate the user and apply the role policy. For example, the following role attributes can be mapped.
- Click Save to save the LDAP server settings in RUCKUS Network Director.