Using SSOCircle as the SAML Identity Provider
You can use SSOCircle as the public SAML IdP with a tested Cloudpath configuration.
SSOCircle provides a ready-to-use Identity Provider that uses several strong 2-factor authentication methods.
Basic Tasks for Using SSOCircle
Configure SAML using SSOCircle as the IdP by performing the following tasks sequentially:
Adding a SAML Step To Your Workflow
A SAML authentication server may be added to the workflow in place of a traditional
Active Directory or LDAP server for authenticating users.
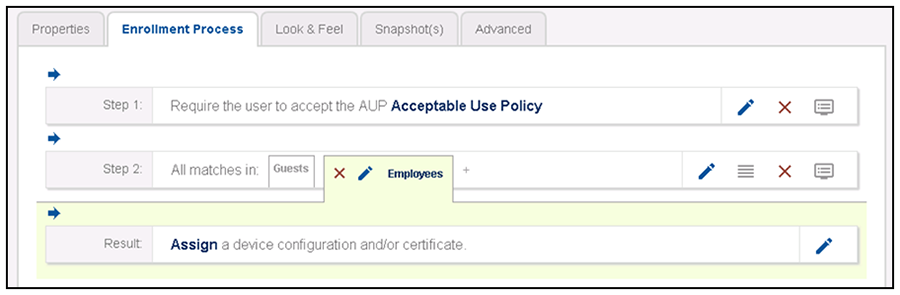
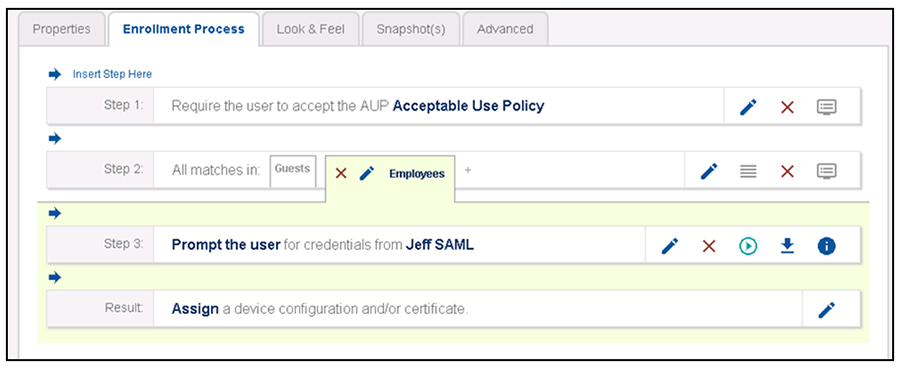
Determine in which branch and in which step to add a SAML authentication server plug-in to the workflow. For example, in the default workflow, you might create a split for Guests and Employees, and you could then use a SAML authentication server instead of the Active Directory authentication server, as shown below.
- Log in to the Cloudpath user interface.
- Go to Configuration > Workflows.
- Click on a workflow (or create a new one) for which you want to configure SAML as the authentication server.
- Highlight the tab in the workflow where you want to add the SAML authentication-server step. In this example below, it is the Employees tab.
- With the Employees branch of the workflow highlighted, click the blue arrow to insert a step below the Guests/Employees split.
Adding the SSOCircle SAML Authentication Server to the Workflow
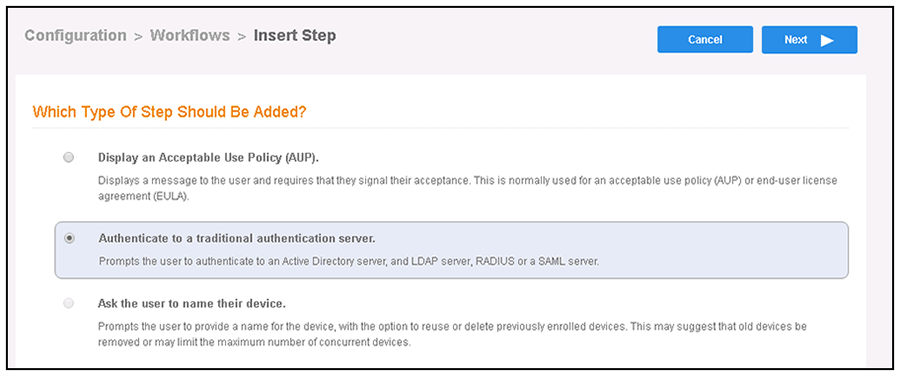
- Once you click the arrow to insert the SAML step, you receive the following prompt:
"Which Type Of Step Should Be Added?"
- Select the button to authenticate to a traditional authentication server, as shown in the following screen:
- Click Next.
- If you have already defined an authentication server, you will get a prompt asking whether you want to reuse an existing authentication server or define a new authentication server. Choose the radio button to define a new authentication server, then click Next.
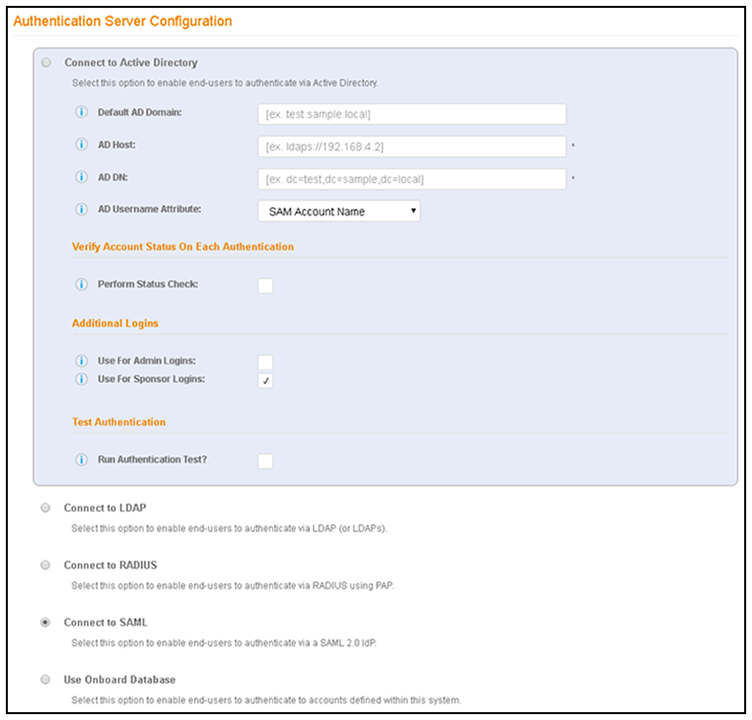
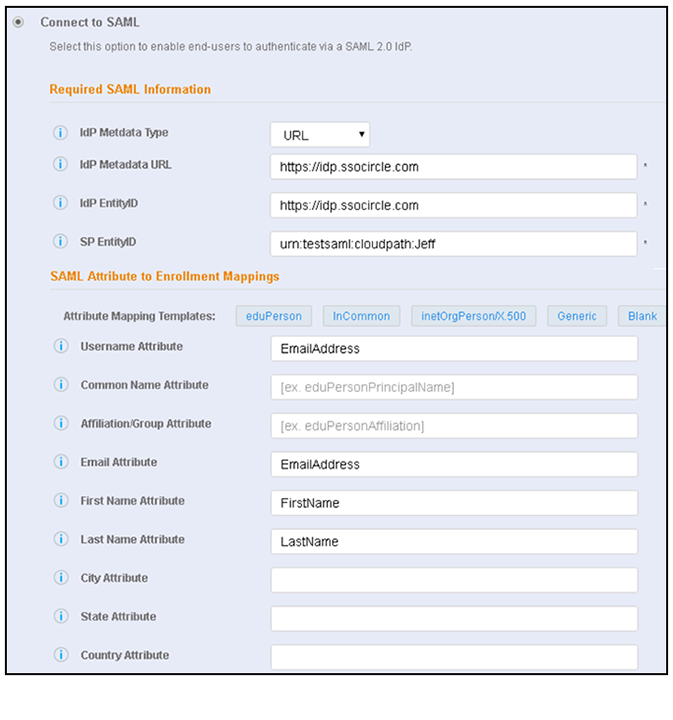
- On the Authentication Server Configuration screen, select the Connect to SAML radio button:
- Complete the configuration as shown in the example below:
Note: You can click the "i" icons next to the field names to obtain the information required for each field.
- Required SAML Configuration section:
- SAML Attribute to Enrollment Mappings - Required fields:
- Username Attribute: Must be EmailAddress
- Email Attribute: Must be EmailAddress
- First Name Attribute: Must be FirstName
- Last Name Attribute: Must be LastName
Note: You can use defaults for the remaining fields. - SAML Options (not shown in the screen shot above): Use all default settings.
- Click Next.
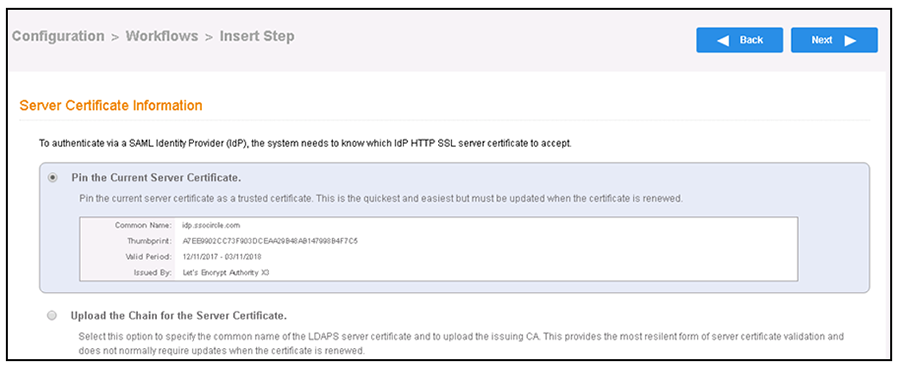
- You can leave the Pin the Current Server Certificate radio button selected, or you can select the other radio button and upload the CA certificate for the SAML server (if you have that certificate). Whichever method you choose, click Next when you are done.
Downloading the SAML Metadata for SSOCircle

Configuring Your Account on SSOCircle
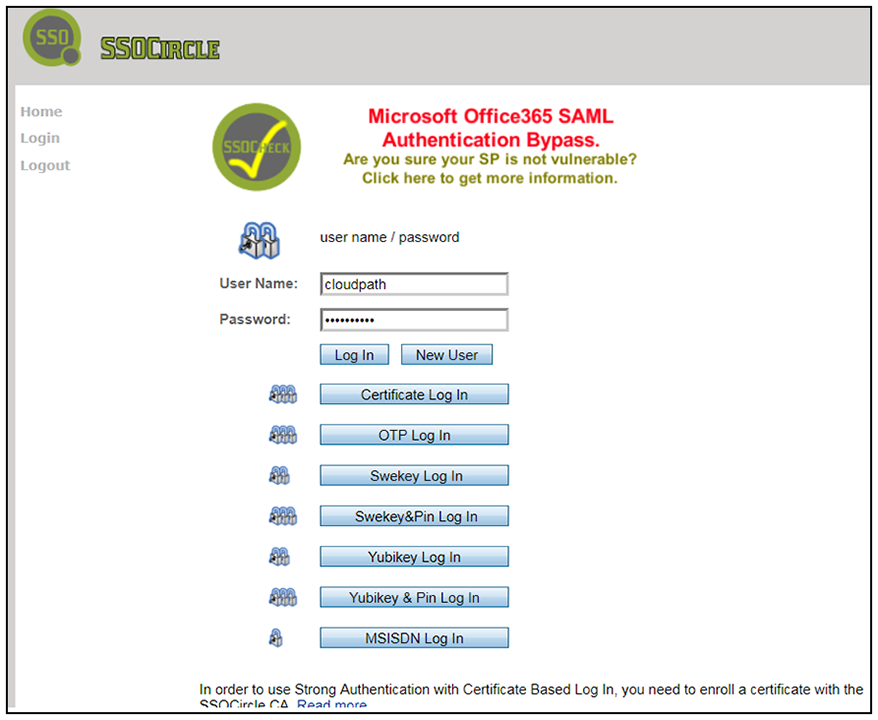
- In a browser, go to the following URL: https://idp.ssocircle.com/sso/UI/Login
- Click Log In.
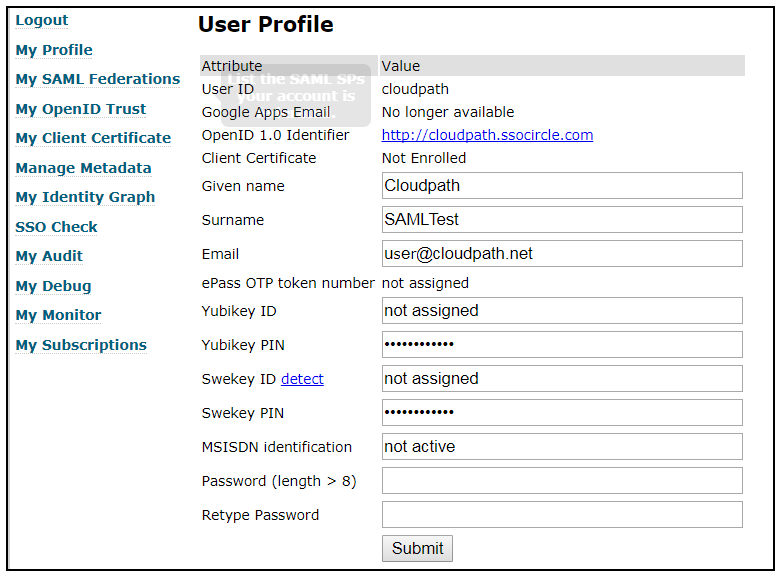
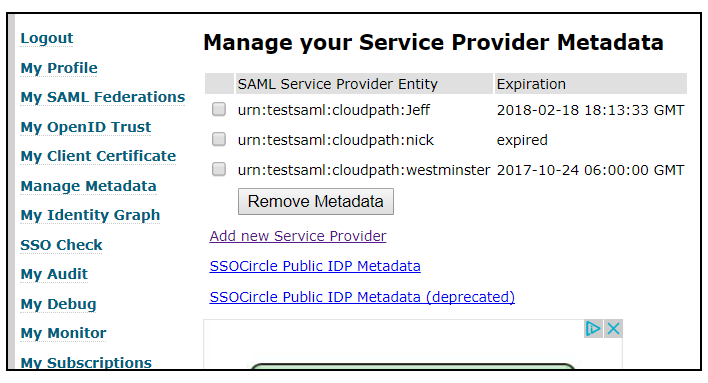
- Click Manage Metadata on the left side of the screen.
- Click the Add new Service Provider link.
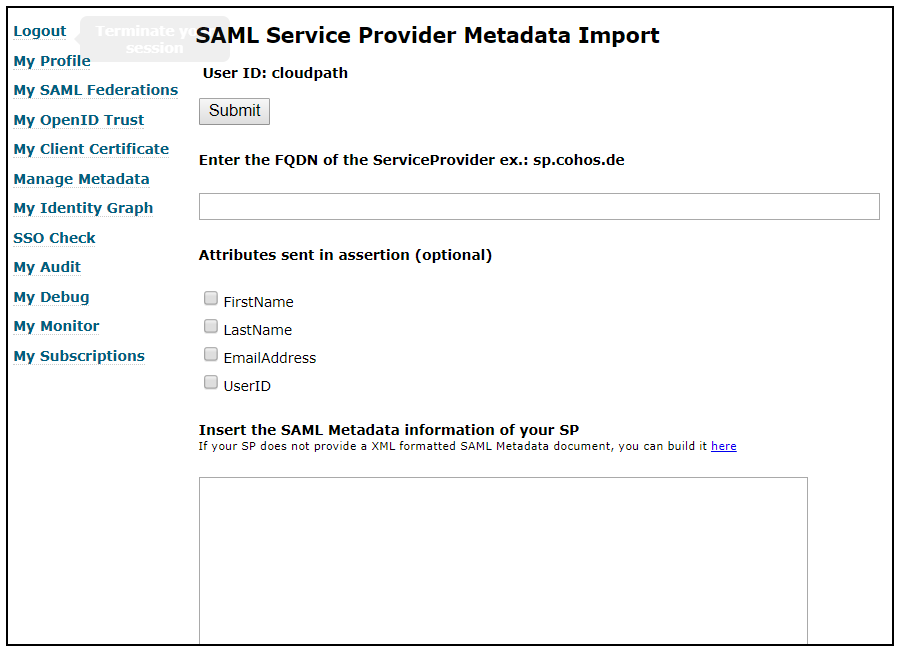
- On the
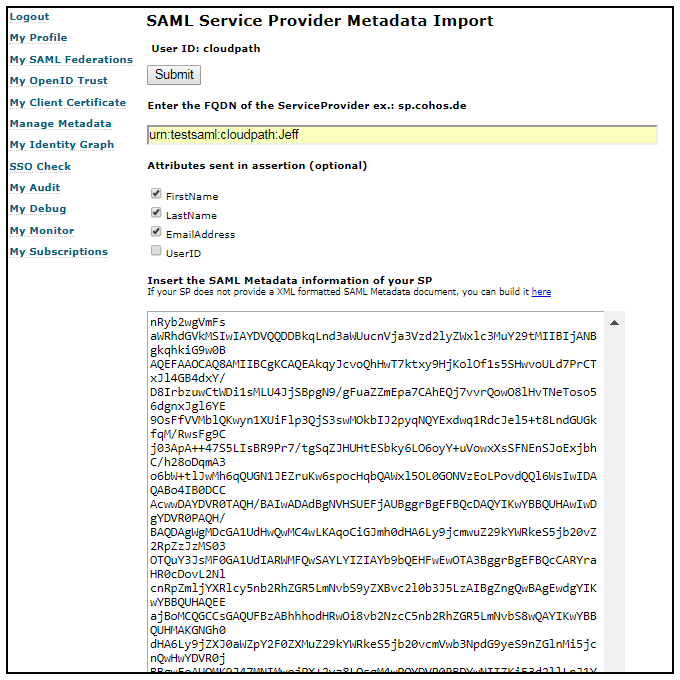
SAML Service Provider Metadata Import screen, do the following:
- For the FQDN, enter the SP Entity ID exactly as you entered it in your Cloudpath system: urn:testsaml:cloudpath:<your first name>. See SAML Configuration Fields for SSOCircle.
- In the Attributes section, check FirstName, LastName, and EmailAddress.
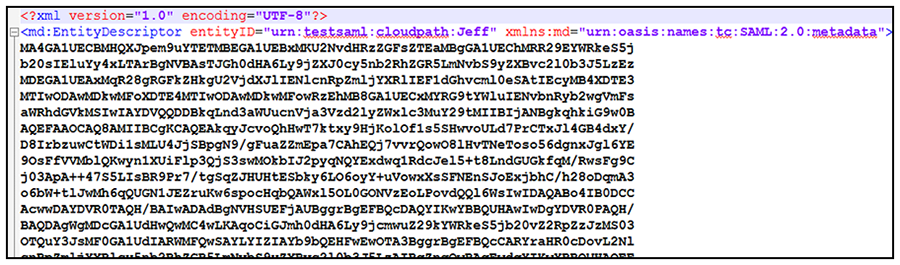
- In the Insert the SAML Metadata information of your SP section, copy and paste the entire contents of the metadata file that you downloaded earlier into the box provided. (Make sure there is no white space before the pasted contents.)
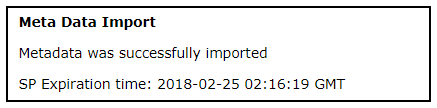
- Click Submit.
- Click Logout.
Publishing the Workflow for SAML SSOCircle
- Return to the workflow on your Cloudpath system by navigating to the Configuration > Workflows screen.
- Complete the workflow by adding a device configuration. Refer to Adding a Device Configuration to Your Workflow.
- Publish the workflow by clicking the Publish icon to the left of the workflow name.
Testing the User Experience for SAML SSOCircle
- Test the enrollment process by clicking on the enrollment portal URL for the workflow at the top of the Configuration > Workflows screen.
- When are you presented with the with the Welcome screen, click Start.
- When you are presented with various branches of your workflow, navigate down a branch
that uses the SAML authentication server you just configured.
You are directed to the SSOCircle login page.
- Log in with the your credentials.
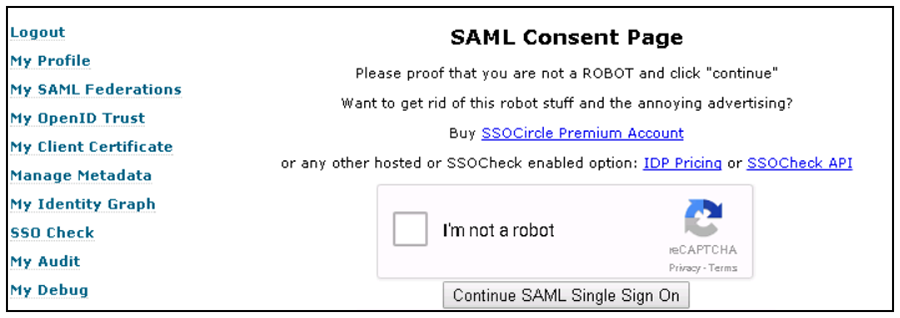
- Check the "I'm not a robot" box, and follow the on-screen instructions.
- When a green check mark appears next to the "I'm not a robot" box, click Continue SAML Single Sign On.
- If the SAML authentication is successful, you are returned to the Cloudpath system, where you can continue with the enrollment.